R2C-CVE-2025-55182-66478

Exploit tool targeting CVE-2025-55182-66478 for vulnerability exploitation and penetration testing. Automates payload delivery and post-exploitation…

Exploit tool targeting CVE-2025-55182-66478 for vulnerability exploitation and penetration testing. Automates payload delivery and post-exploitation…

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

Configurable, Community driven, HTTP C2 Profile

Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…

UDRL for CS

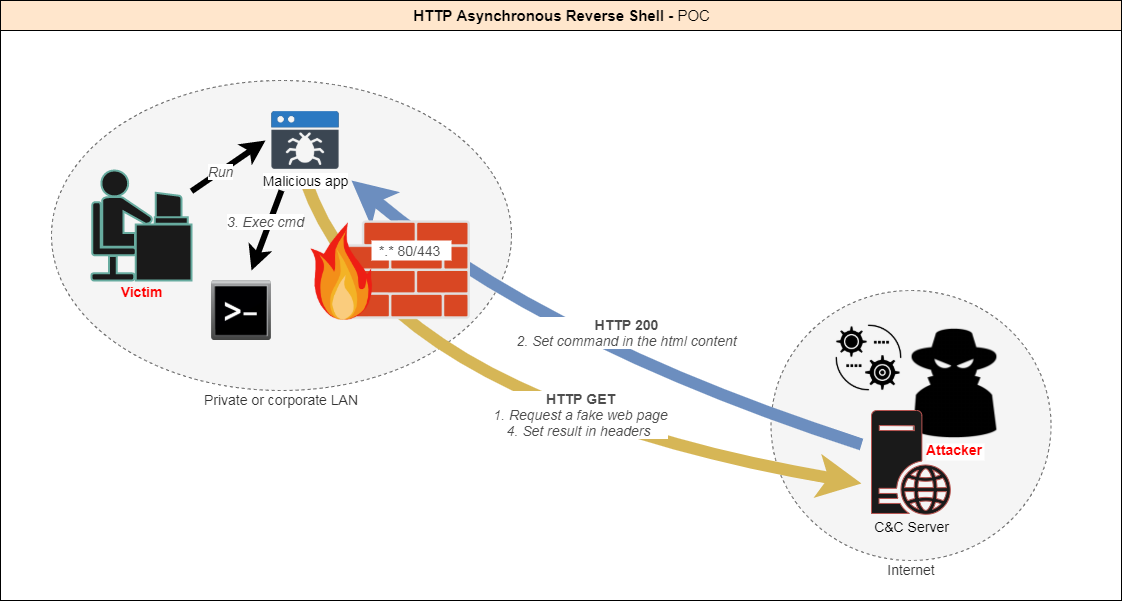
[POC] Asynchronous reverse shell using the HTTP protocol.

Beacon Object File Loader

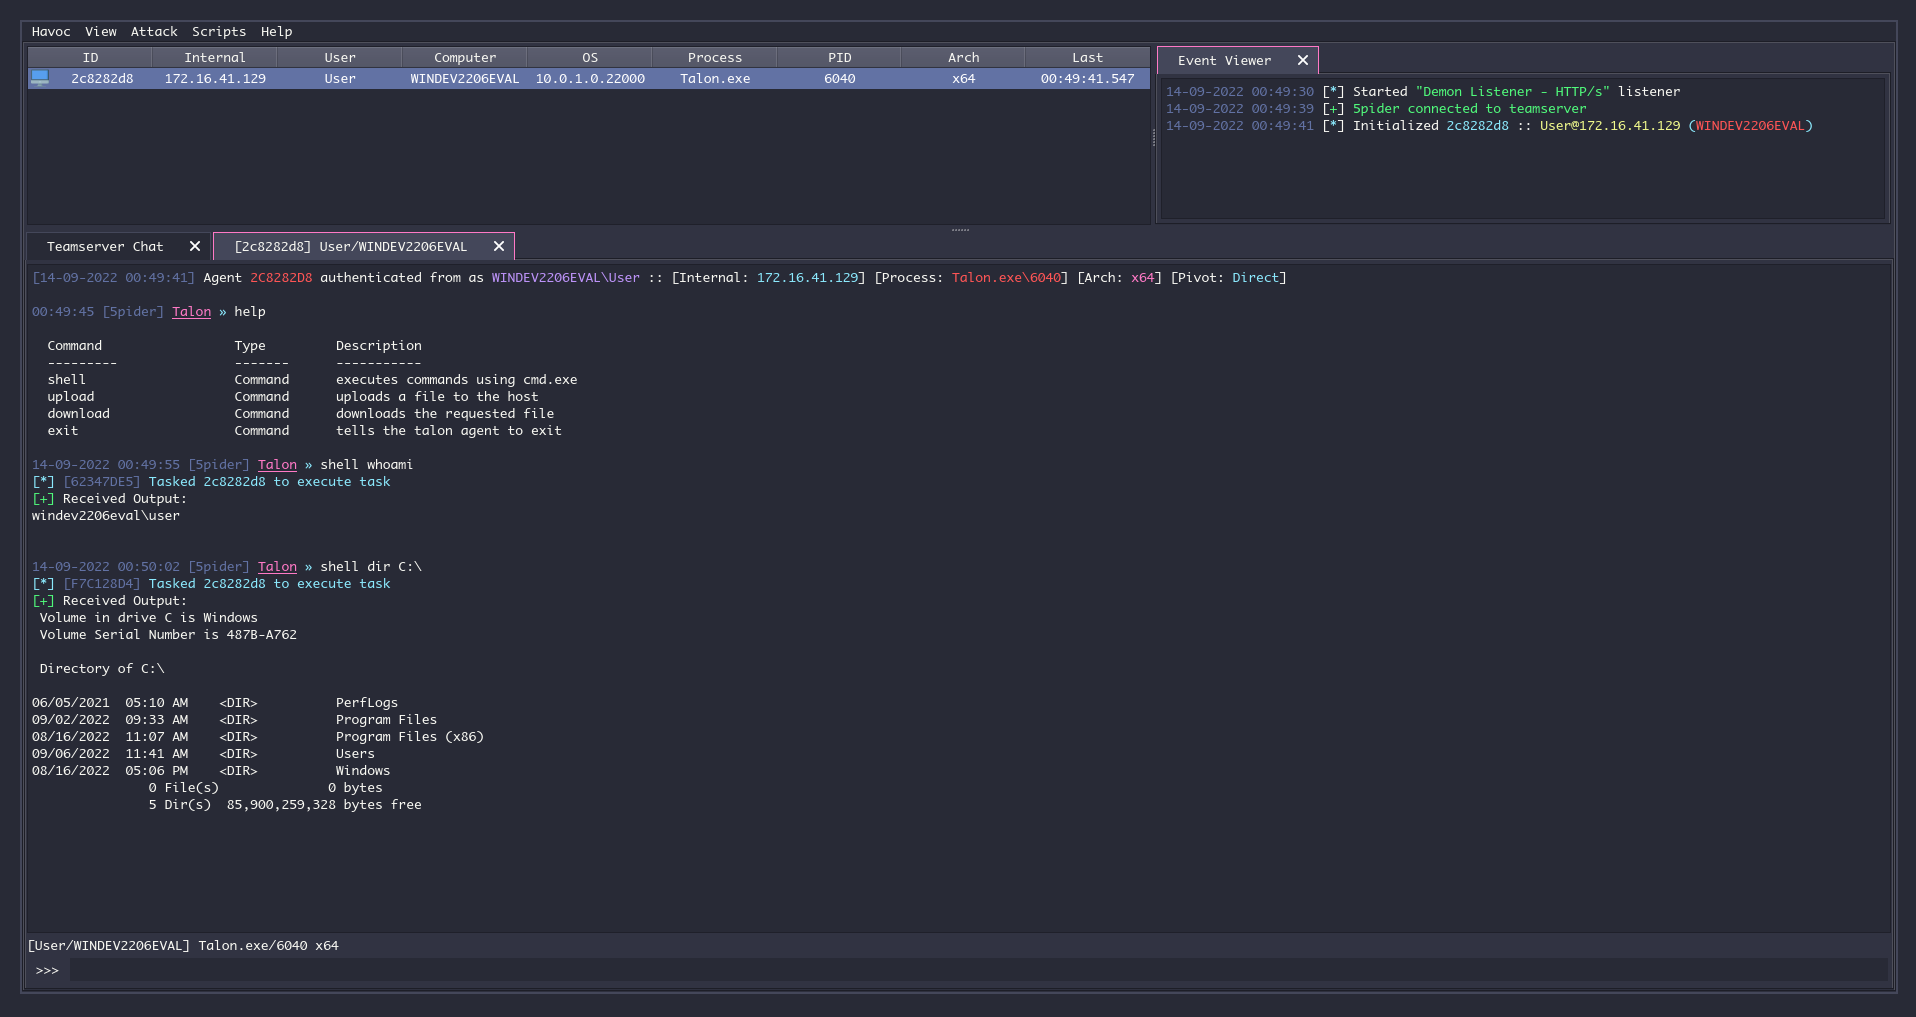
(Demo) 3rd party agent for Havoc

Perl/Python modules for interfacing with Metasploit MSGRPC

Python / C# Unmanaged PowerShell based RAT

A C2 project that controls a self-propagating MS17-010 worm.

DNS covert channel implant for Red Teams.

A Python agent targeting Linux for Mythic C2

.NET/PowerShell/VBA Offensive Security Obfuscator

Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…