
CVE-2024-6366
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
code-analysisexploit-frameworkspayload-development+3
abdurahmon3236/cve-2024-6366Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 0xhuesca/cve-2019-18655
CVE-2019-18655 metasploit module. SEH based buffer overflow in file sharing wizard app v.1.5.0.
 zeroethical/cve-2022-28108
Metasploit module exploiting CVE-2022-28108 in Selenium Grid for remote code execution, with content-type evasion and post-exploitation capabilities.
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
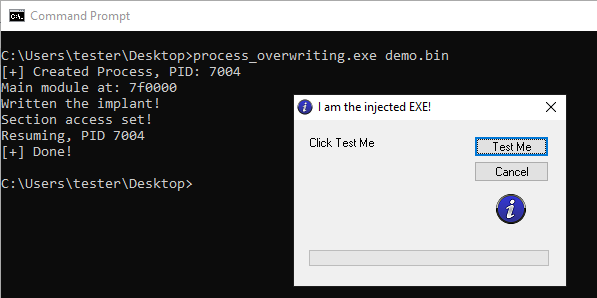 hasherezade/process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 bkup/slackshell
PowerShell to Slack C2
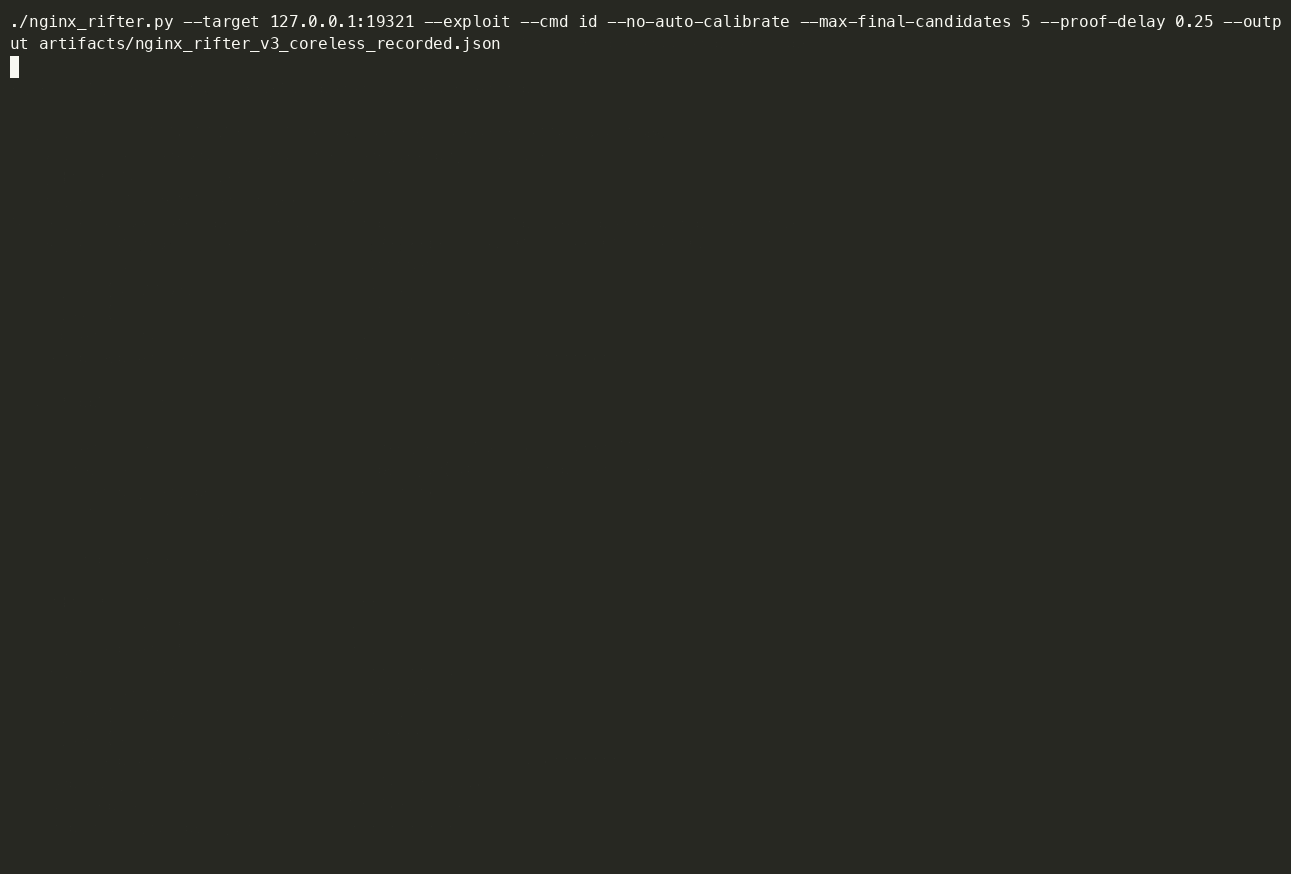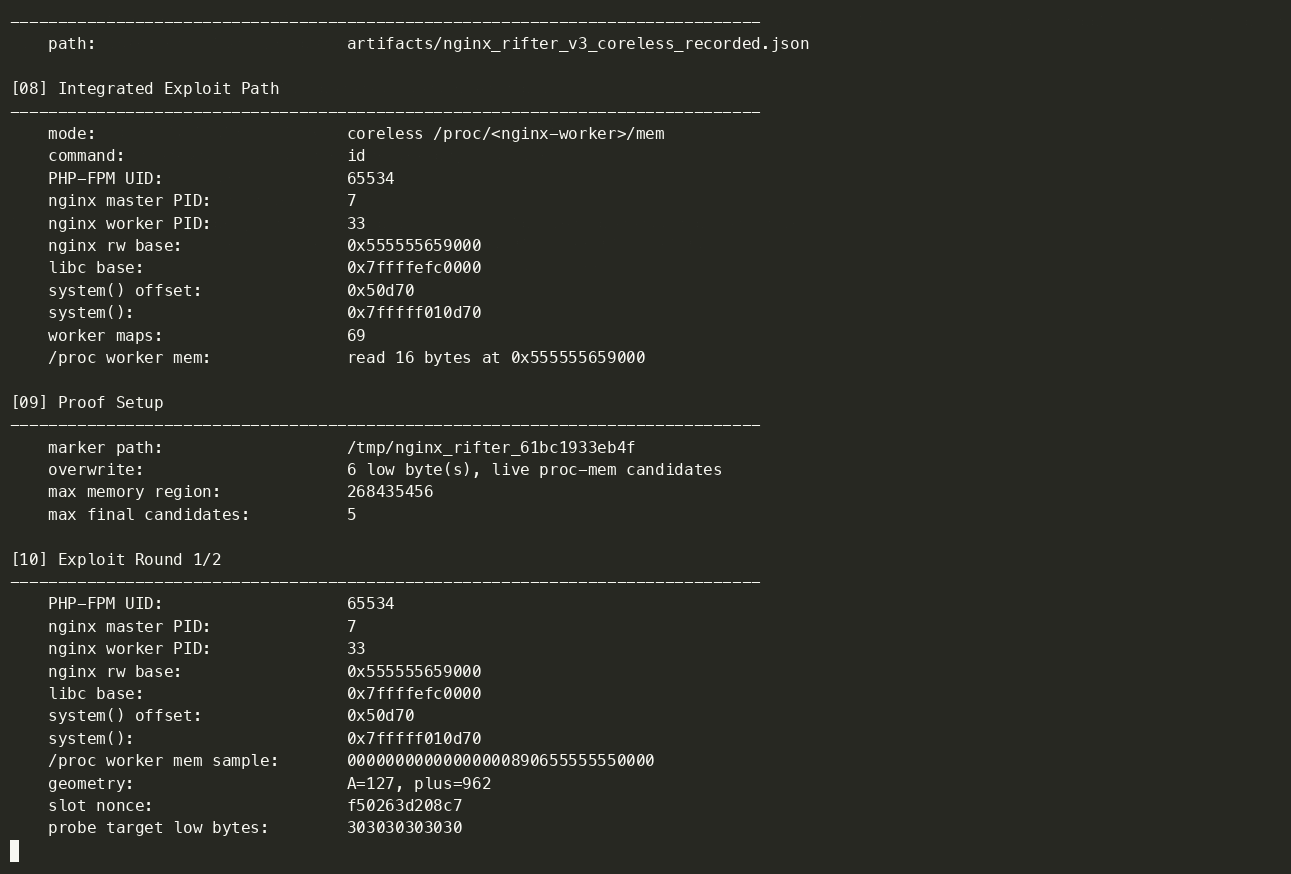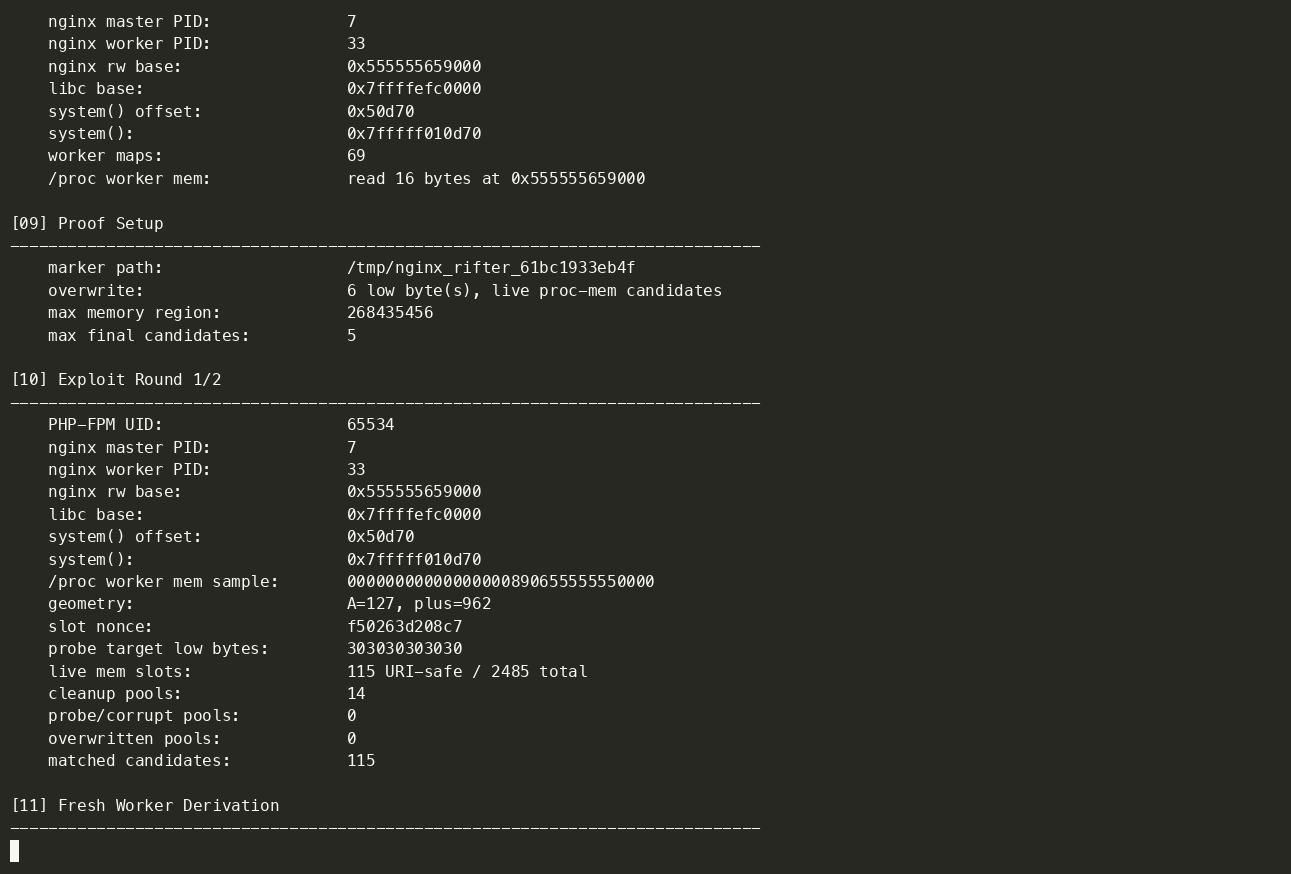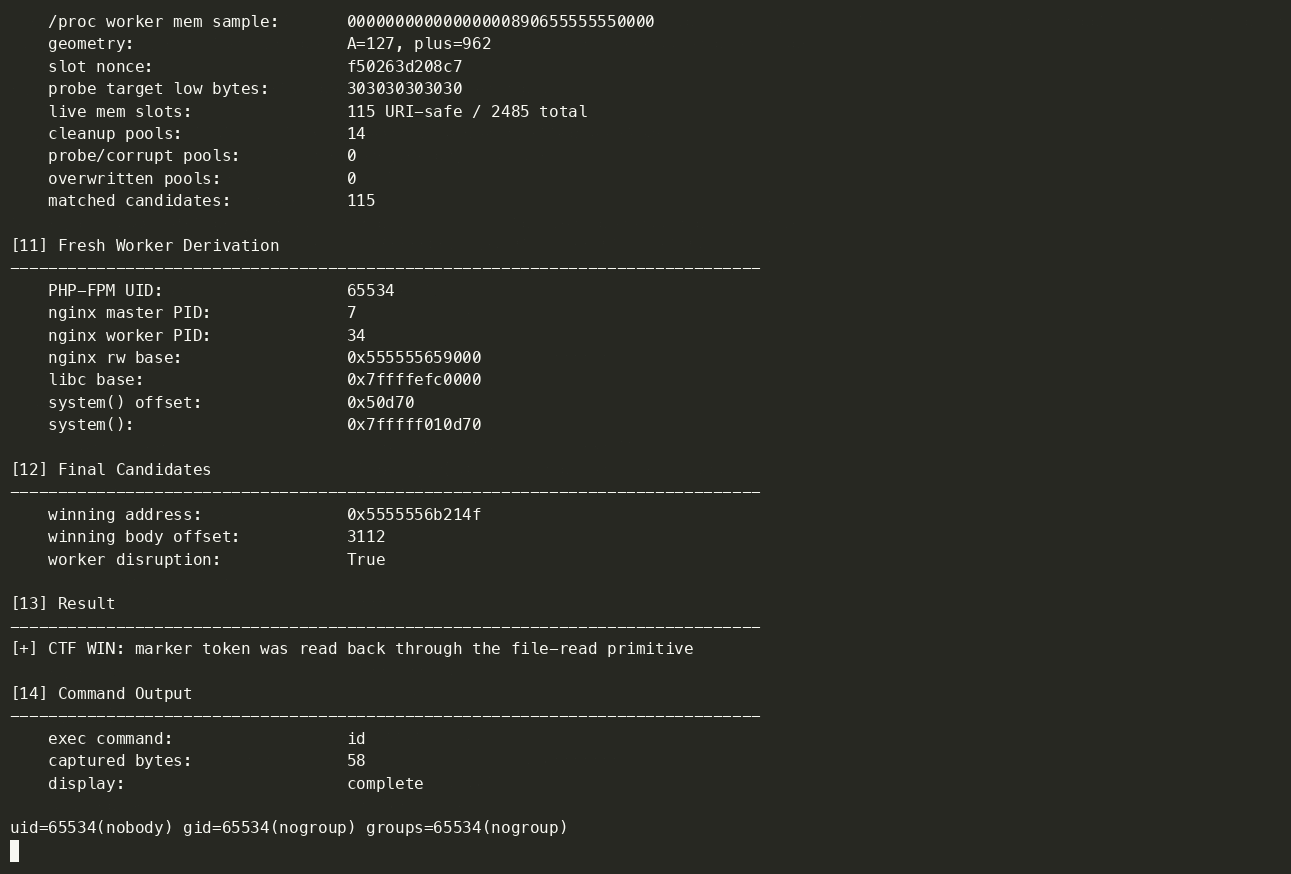 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 0dayninja/cve-2021-24155.rb
WordPress Backup Guard Authenticated Remote Code Execution Exploit
 skynoxk/cve-2025-48703
Remote Code execution in CentOS web panel
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 x1o3/cve-2025-50286
Metasploit exploit for the CVE-2025-50286.
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 ready2disclose/cve-2022-31491
CVE-2022-31491
 kov404/cve-2025-52385
Studio 3T v.2025.1.0