

Invisi-Shell
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
defensive-toolsexploitationids-ips-evasion+9
1.3k
omerya/invisi-shellHide your Powershell script in plain sight. Bypass all Powershell security features
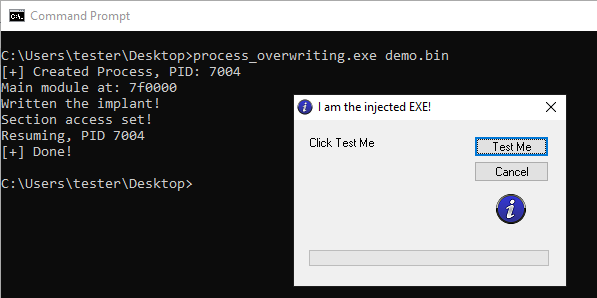 hasherezade/process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 bkup/slackshell
PowerShell to Slack C2
 lazorfuzz/python-hacklib
hacklib - pentesting, port scanning, and logging in anywhere with Python
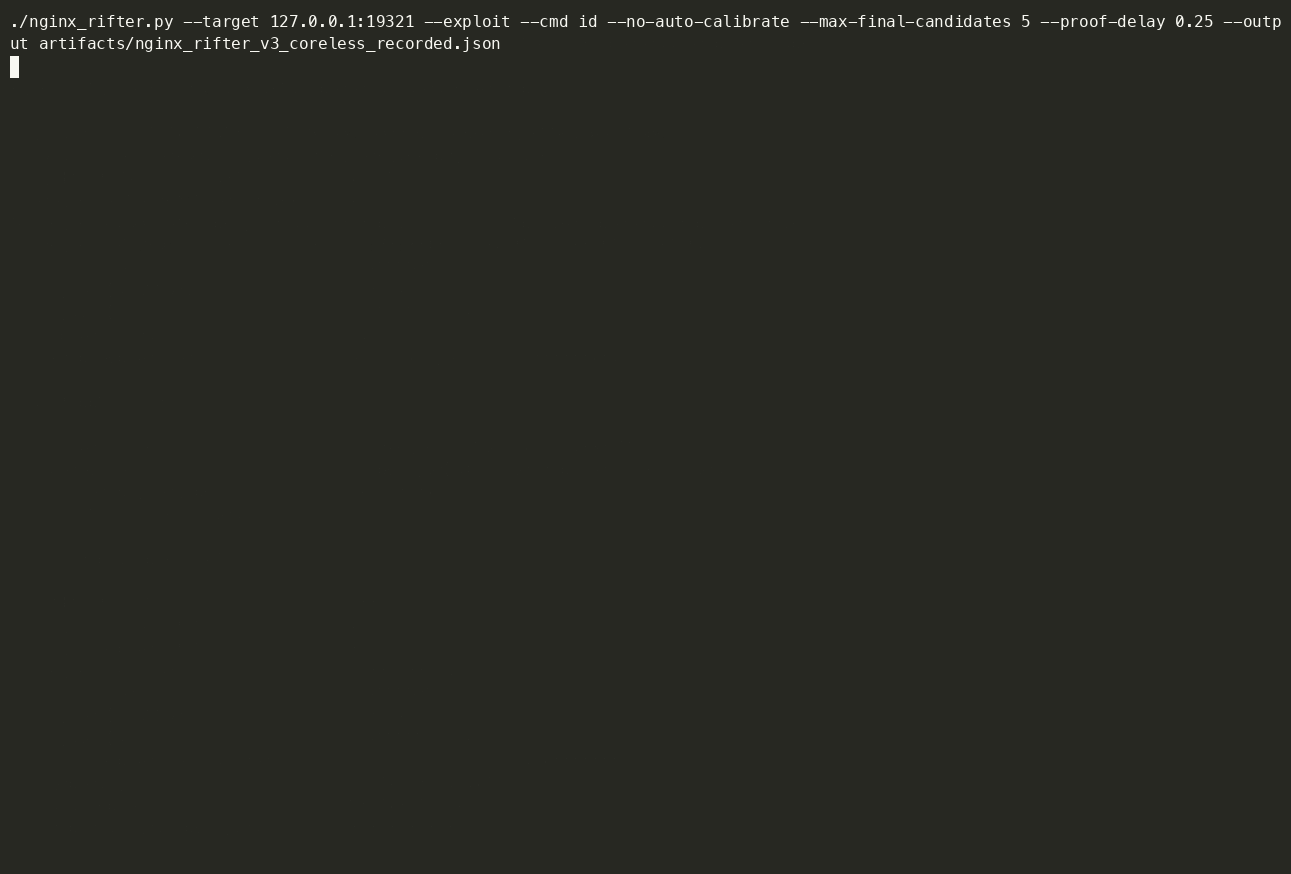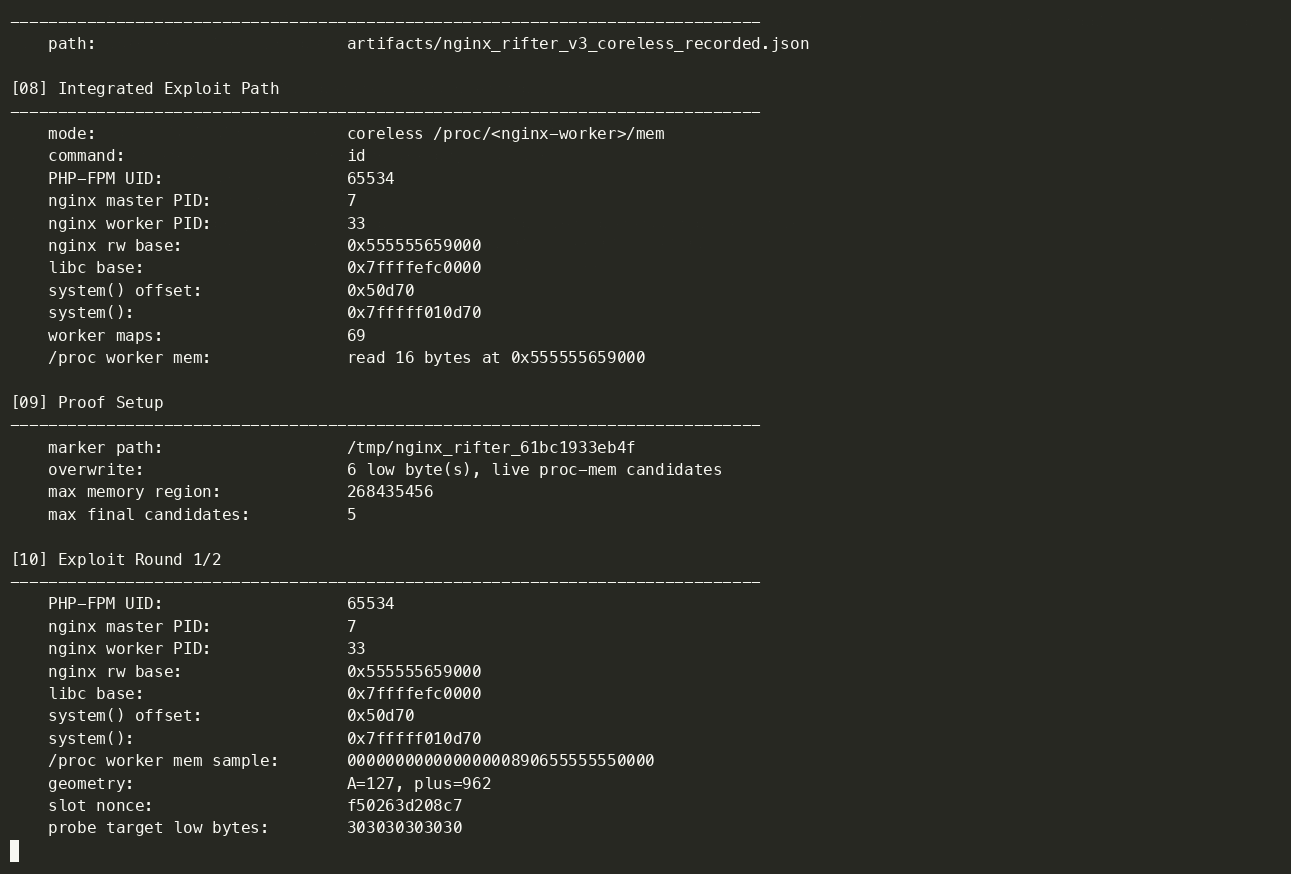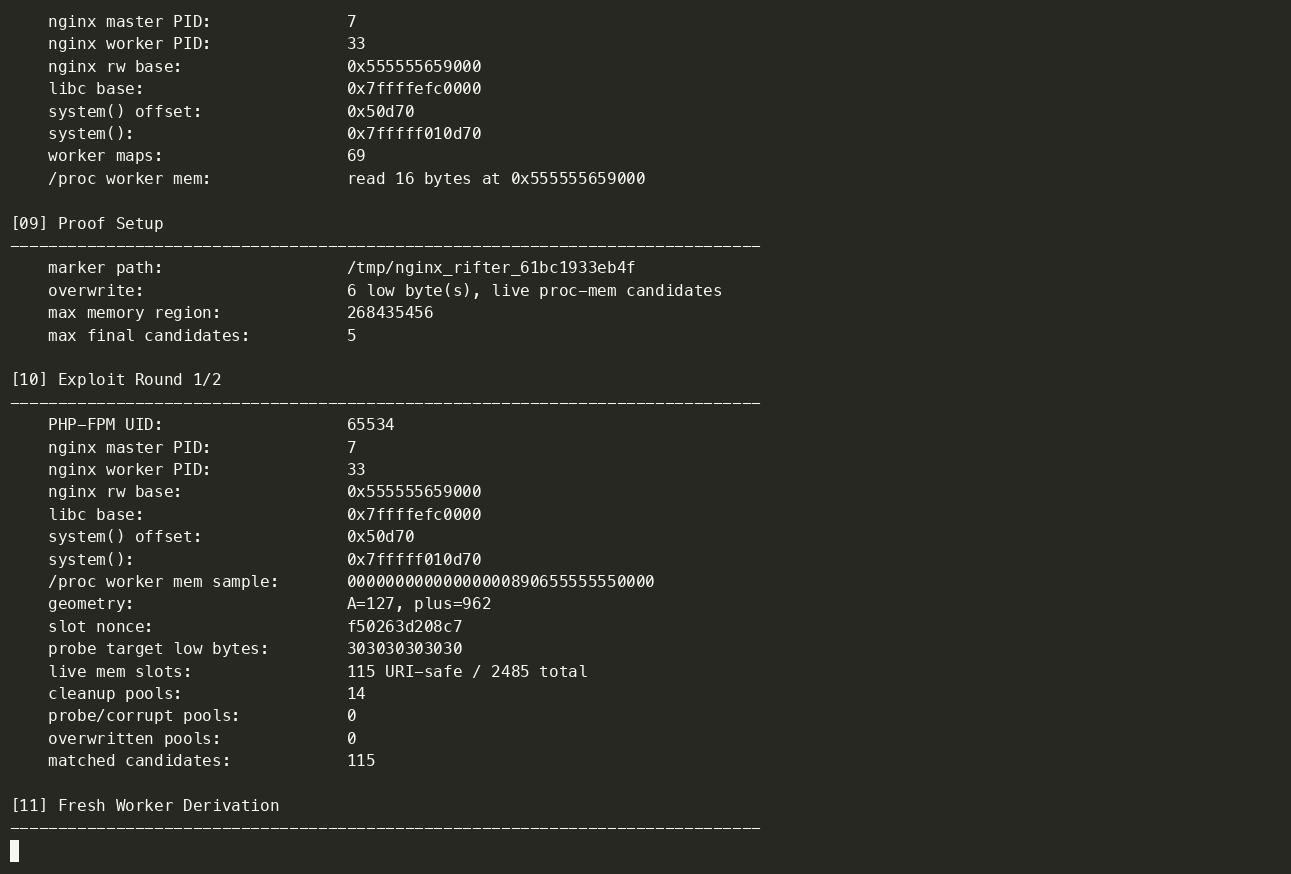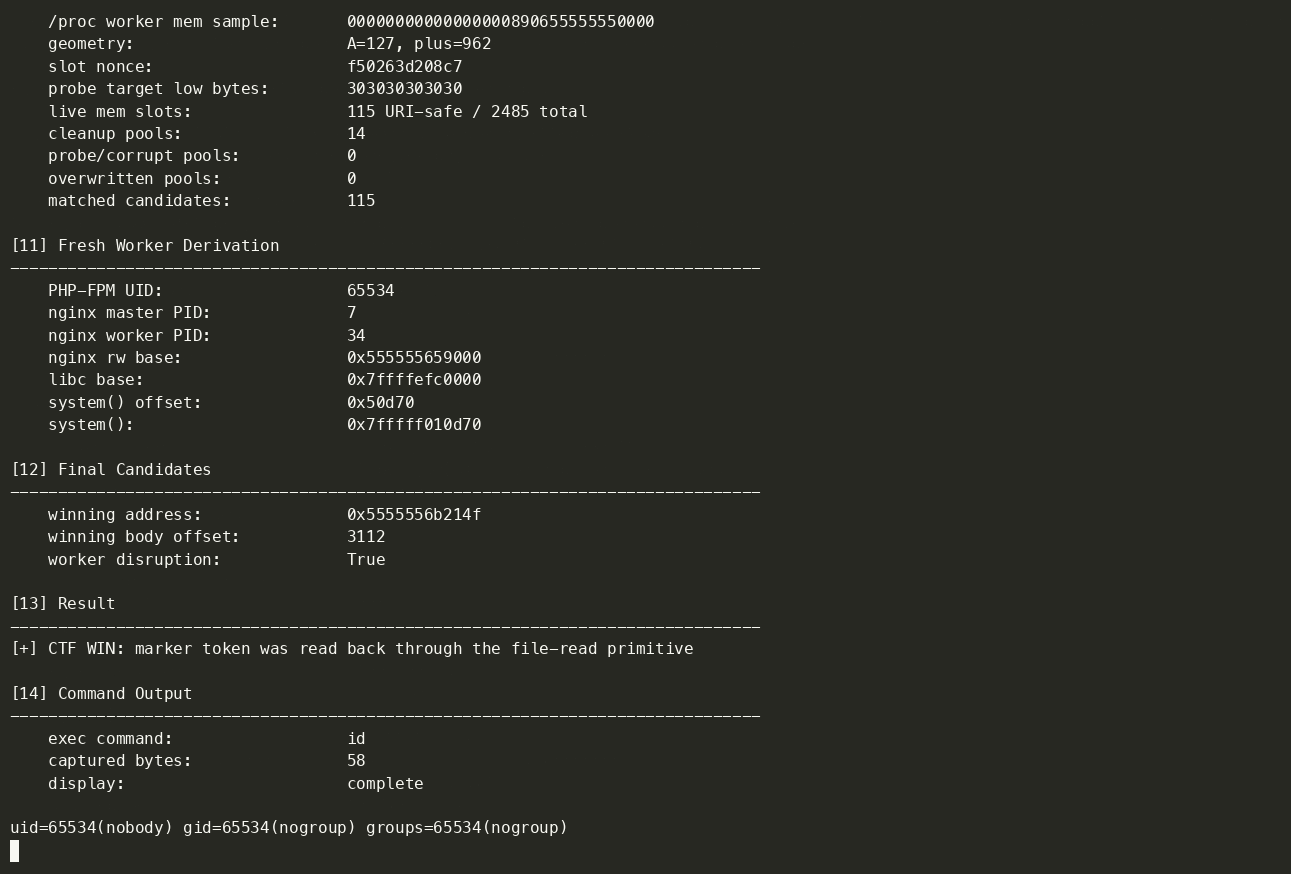 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 math-x-io/cve-2024-54152
PoC exploit for Angular Expressions sandbox escape (CVE-2024-54152) achieving RCE via malicious expression. Includes Docker environment and payload…
 0dayninja/cve-2021-24155.rb
WordPress Backup Guard Authenticated Remote Code Execution Exploit
 silentsignal/cve-2023-30990
CVE-2023-30990 exploits
 skynoxk/cve-2025-48703
Remote Code execution in CentOS web panel
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 x1o3/cve-2025-50286
Metasploit exploit for the CVE-2025-50286.
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 ready2disclose/cve-2022-31491
CVE-2022-31491
 estebanzarate/cve-2025-4517-python-tarfile-filter-data-bypass-poc
Proof-of-concept exploit for CVE-2025-4517, a path traversal vulnerability in Python's tarfile filter='data' sandbox, enabling arbitrary file writes…
 kov404/cve-2025-52385
Studio 3T v.2025.1.0