
CVE-2012-5106
 war4uthor/cve-2012-5106
CVE-2012-5106 - Freefloat FTP Server Buffer Overflow Vulnerability. Tested on Windows XP Professional SP3.
binary-exploitationexploitationpayload-development+2
war4uthor/cve-2012-5106CVE-2012-5106 - Freefloat FTP Server Buffer Overflow Vulnerability. Tested on Windows XP Professional SP3.
 war4uthor/cve-2003-0264
CVE-2003-0264 - SLMail 5.5 POP3 'PASS' Remote Buffer Overflow Vulnerability. Tested on Windows XP Professional SP3.
 0xsalle/cve-2018-15133
Proof-of-concept exploit for CVE-2018-15133 that achieves remote command execution on Laravel applications by abusing insecure deserialization with…
 blackninja23/cve-2024-32002
Proof-of-concept exploit for CVE-2024-32002, a Git RCE via crafted submodules on case-insensitive filesystems, demonstrating malicious hook execution…
 manojcode/cloudme-sync-1.10.9---buffer-overflow-seh-dep-bypass
My version - CloudMe-Sync-1.10.9---Buffer-Overflow-SEH-DEP-Bypass on Win7 x64 CVE-2018-6892
 aus-mate/cve-2021-4034-poc
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec. Compiles and runs a C payload to…
 ashutosh0408/cve-2024-32002-poc
This repository contains a PoC for exploiting CVE-2024-32002, a vulnerability in Git that allows RCE during a git clone operation. By crafting…
 harshit-mashru/cve-2023-6553
Exploit Development for CVE-2023-6553 on Backup Plugin in Wordpress
 ashutosh0408/cve-2024-32002
This repository contains a PoC for exploiting CVE-2024-32002, a vulnerability in Git that allows RCE during a git clone operation. By crafting…
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386
 jongmartinez/cve-2018-11235-poc
PoC exploit for CVE-2018-11235 allowing RCE on git clone --recurse-submodules
 jxerome/log4shell
Educational demonstration of the Log4Shell vulnerability (CVE-2021-44228) with JNDI LDAP payloads for experimental testing on your own systems.
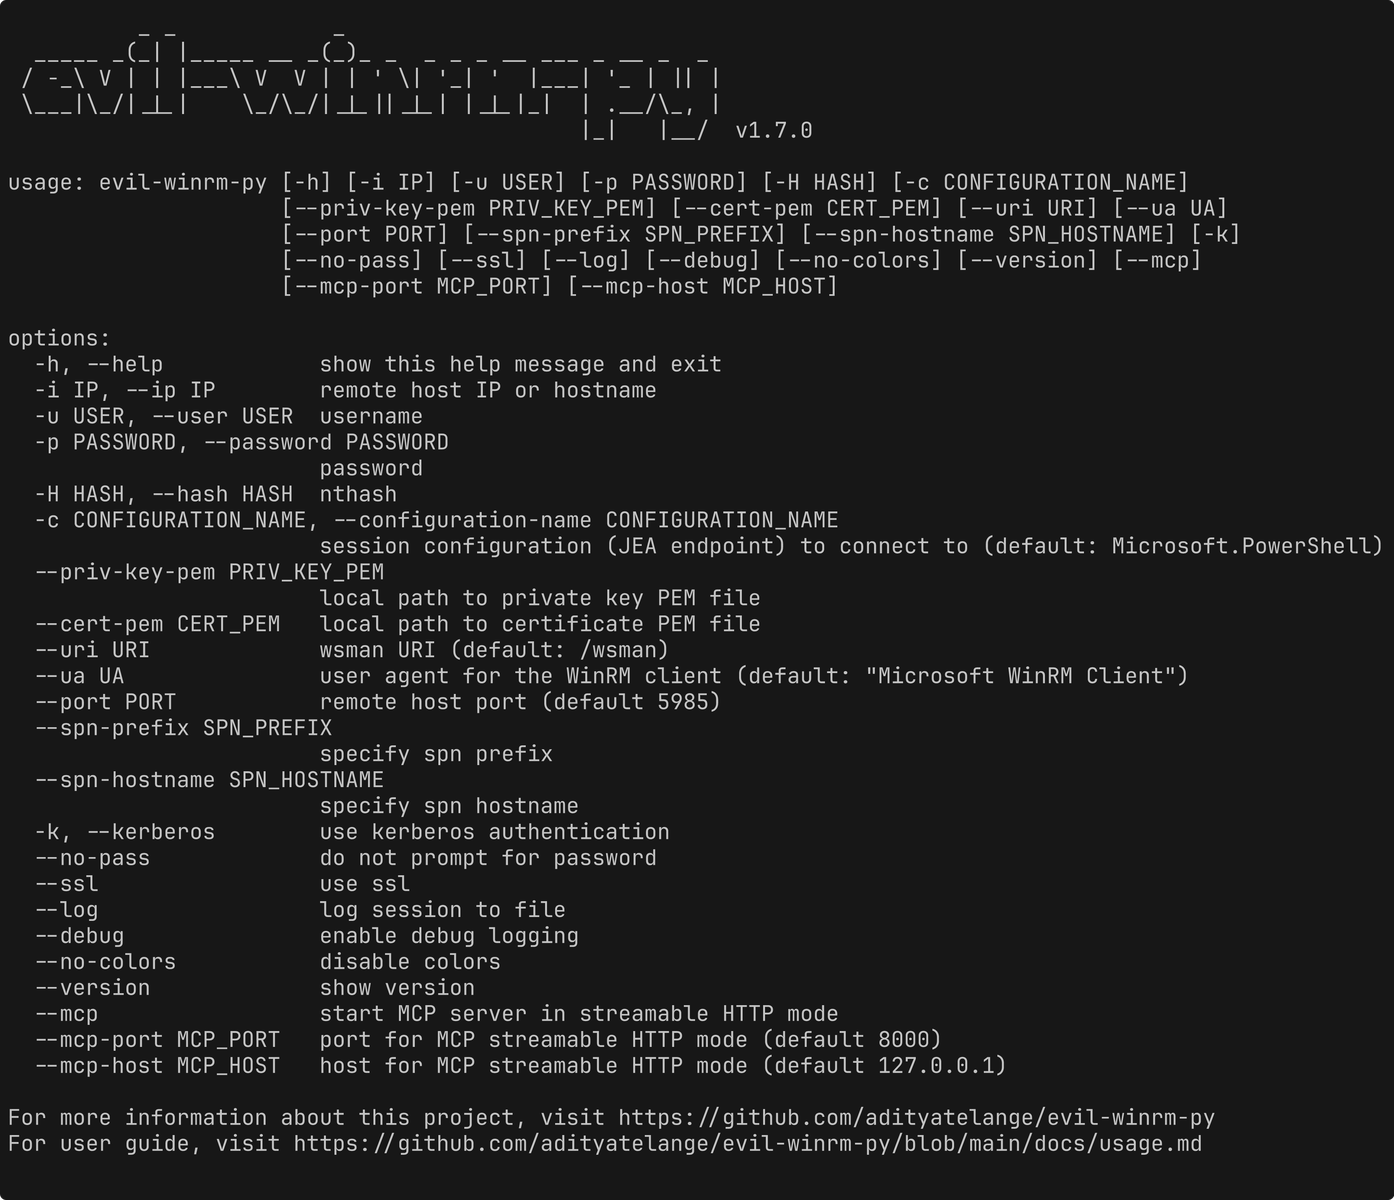 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 flex36ty/ps5-pihost
PS5 Exploit Web Server on a Raspberry Pi Powered by the PS5's USB Port
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.