Flowise-CVE-2026-58057-exploit

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…

AI修复生成的CVE-2025-32432的poc

收集网上CVE-2018-0708的poc和exp(目前没有找到exp)

A testing tool for CobaltStrike-RCE:CVE-2022-39197; Weblogic-RCE:CVE-2023-21839; MinIO:CVE-2023-28432

Unauthenticated RCE PoC for CVE-2026-48908 SP Page Builder (Joomla) arbitrary file upload and remote code execution exploit with mass scaning…

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

CVE-2026-42945 Nginx Rift

Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) to check remote overflow vulnerability in SMBv3.

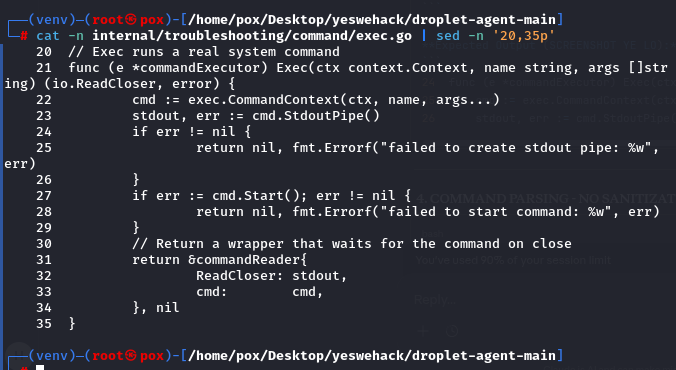
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

CVE-2024-23897: Jenkins Arbitrary File Read Lead to RCE

Disclosure and PoCs for CVE-2025-68413 and CVE-2025-68414

Advanced RCE exploitation toolkit for React Server Components vulnerabilities. Features multiple pre-built payloads, Shodan integration for target…

CVE-2026-3584

Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…

Suite for reverse shell handling geared toward working within the native shell