

CVE-2024-53677
 ctfsec/cve-2024-53677
Proof-of-concept exploit for Apache Struts file upload path traversal vulnerability (CVE-2024-53677) enabling remote code execution. Useful for…
exploitationpayload-developmentpenetration-testing+3
ctfsec/cve-2024-53677Proof-of-concept exploit for Apache Struts file upload path traversal vulnerability (CVE-2024-53677) enabling remote code execution. Useful for…
 foregenix/cve-2025-54309
Python-based exploitation scripts targeting CrushFTP CVE-2025-54309 for vulnerability verification and penetration testing.
 drkim-dev/cve-2025-62429
Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 diamorphine666/cve-2025-10162-exploit
Exploit for CVE-2025-10162, a remote code execution vulnerability. Delivers targeted payload for penetration testing and vulnerability validation.
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
 darrynb89/cve-2004-1561
Python port of a Metasploit exploit targeting CVE-2004-1561 for remote code execution. Designed for penetration testing and vulnerability validation…
 timeshu/weblogic_cve-2023-21931_poc-exp
Proof-of-concept and exploit for CVE-2023-21931, a WebLogic vulnerability, with JNDI injection techniques for penetration testing and security…
 dotpy-hax/copyfail
Python implementation of the CopyFail CVE-2026-31431 exploit with support for custom payloads. Designed for vulnerability verification and…
 novitahk/exploit-cve-2026-24061
Bash-based exploit for CVE-2026-24061 targeting telnet service, providing payload execution for penetration testing and vulnerability verification.
 machevalia/cve-2024-0692-solarwinds-sem-rce
Proof-of-concept exploit for CVE-2024-0692 targeting SolarWinds SEM, developed from penetration testing research to demonstrate remote code execution.
 kinghacker353/cve-2025-14847_expolit
Exploit for CVE-2025-14847, providing targeted vulnerability exploitation for penetration testing and security assessment of affected systems.
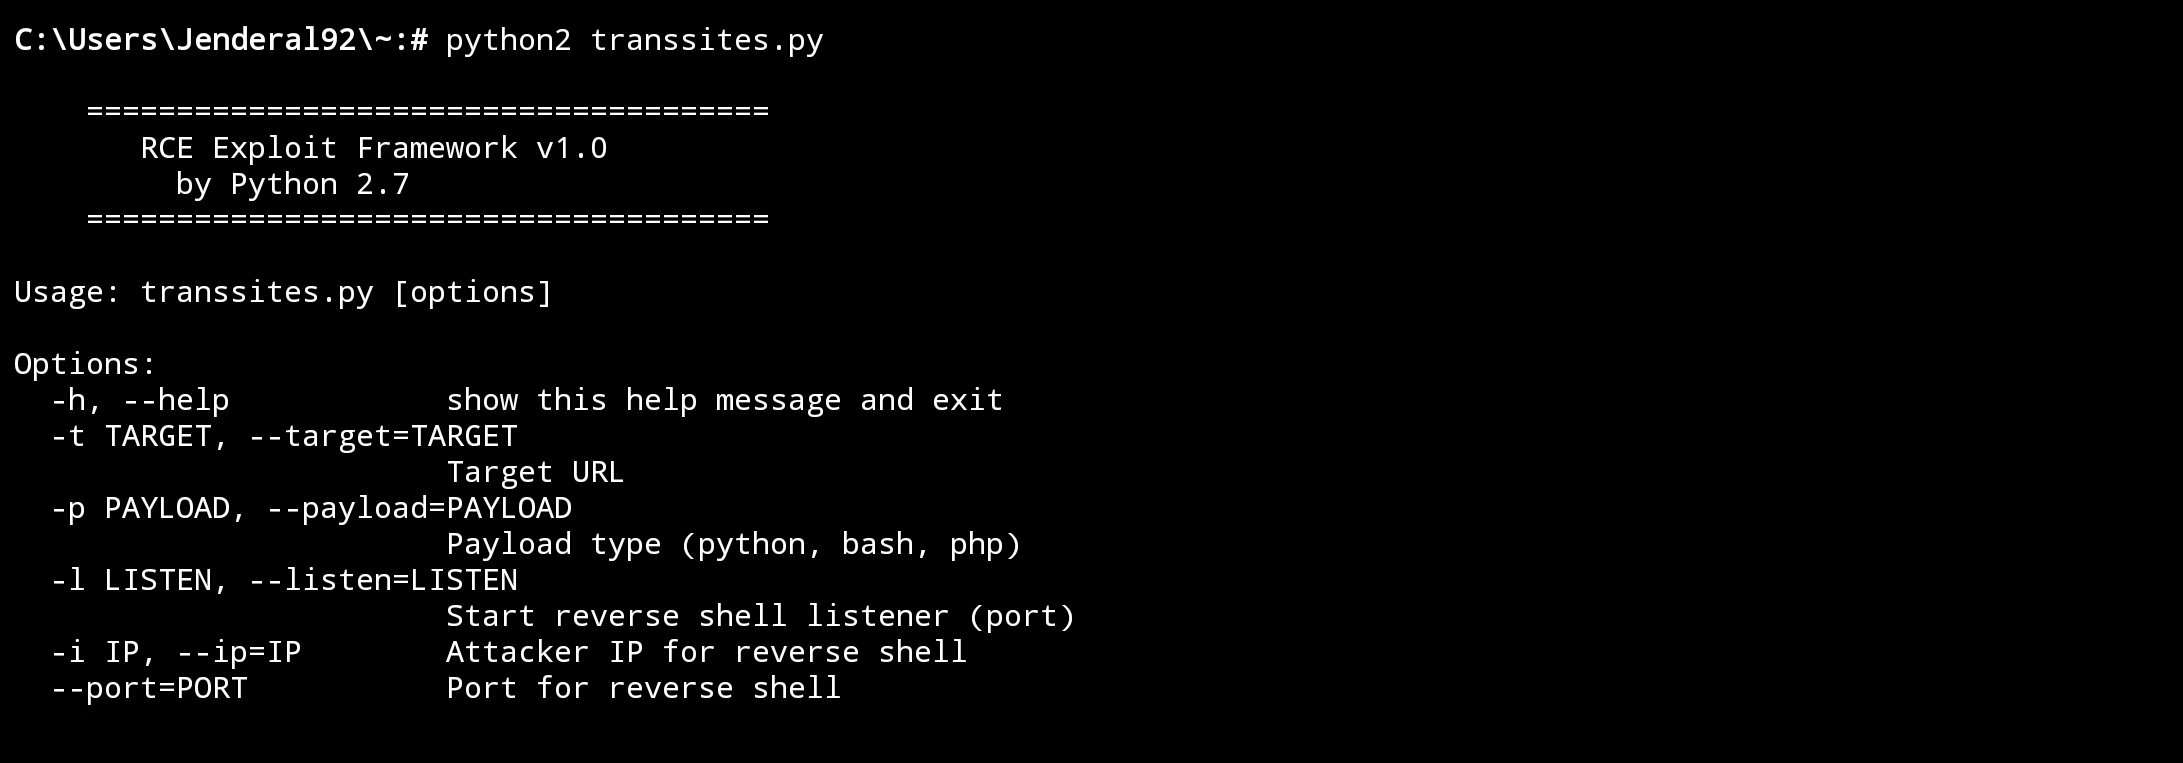 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 cuijiung/xstream-cve-2021-29505
Java-based exploit for CVE-2021-29505 targeting XStream deserialization vulnerability, enabling remote code execution via crafted XML payloads for…
 gy741/cve-2023-30258-setup
Shell-based exploit setup for CVE-2023-30258, providing a ready-to-use proof-of-concept for vulnerability verification and penetration testing.
 brunopincho/cve-2018-16763-rust
Rust implementation of an exploit for CVE-2018-16763, targeting a remote code execution vulnerability in Fuel CMS for penetration testing and…