

CVE-2026-42945
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
binary-exploitationcommand-and-controleducation+6
1
aratane/cve-2026-42945A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 0xhaggis/cve-2021-3064
Exploit for CVE-2021-3036, HTTP Smuggling + buffer overflow in PanOS 8.x
 kuri119/cve-2022-22965-spring4shell
Exploit for CVE-2022-22965 (Spring4Shell) enabling remote code execution on unpatched Spring Framework applications via crafted HTTP requests.
 tau-hub/firefox-cve-2016-9079
Manual exploit for Firefox RCE CVE-2016-9079 with customizable shellcode, served via HTTP for remote code execution on vulnerable Windows systems.
 huyennhat-dev/cve-2023-34040
Proof-of-concept exploit for Spring Kafka deserialization RCE (CVE-2023-34040) with a crafted HTTP POST payload targeting vulnerable message brokers.
 gmh5225/cve-2025-48799-
Proof-of-concept exploit for CVE-2025-48799, an Apache Tomcat remote code execution vulnerability. Demonstrates integer overflow exploitation via…
 eserror/cve-2025-31161
Go-based exploit for CVE-2025-31161 targeting crushFTP, enabling remote admin account creation via crafted HTTP requests.
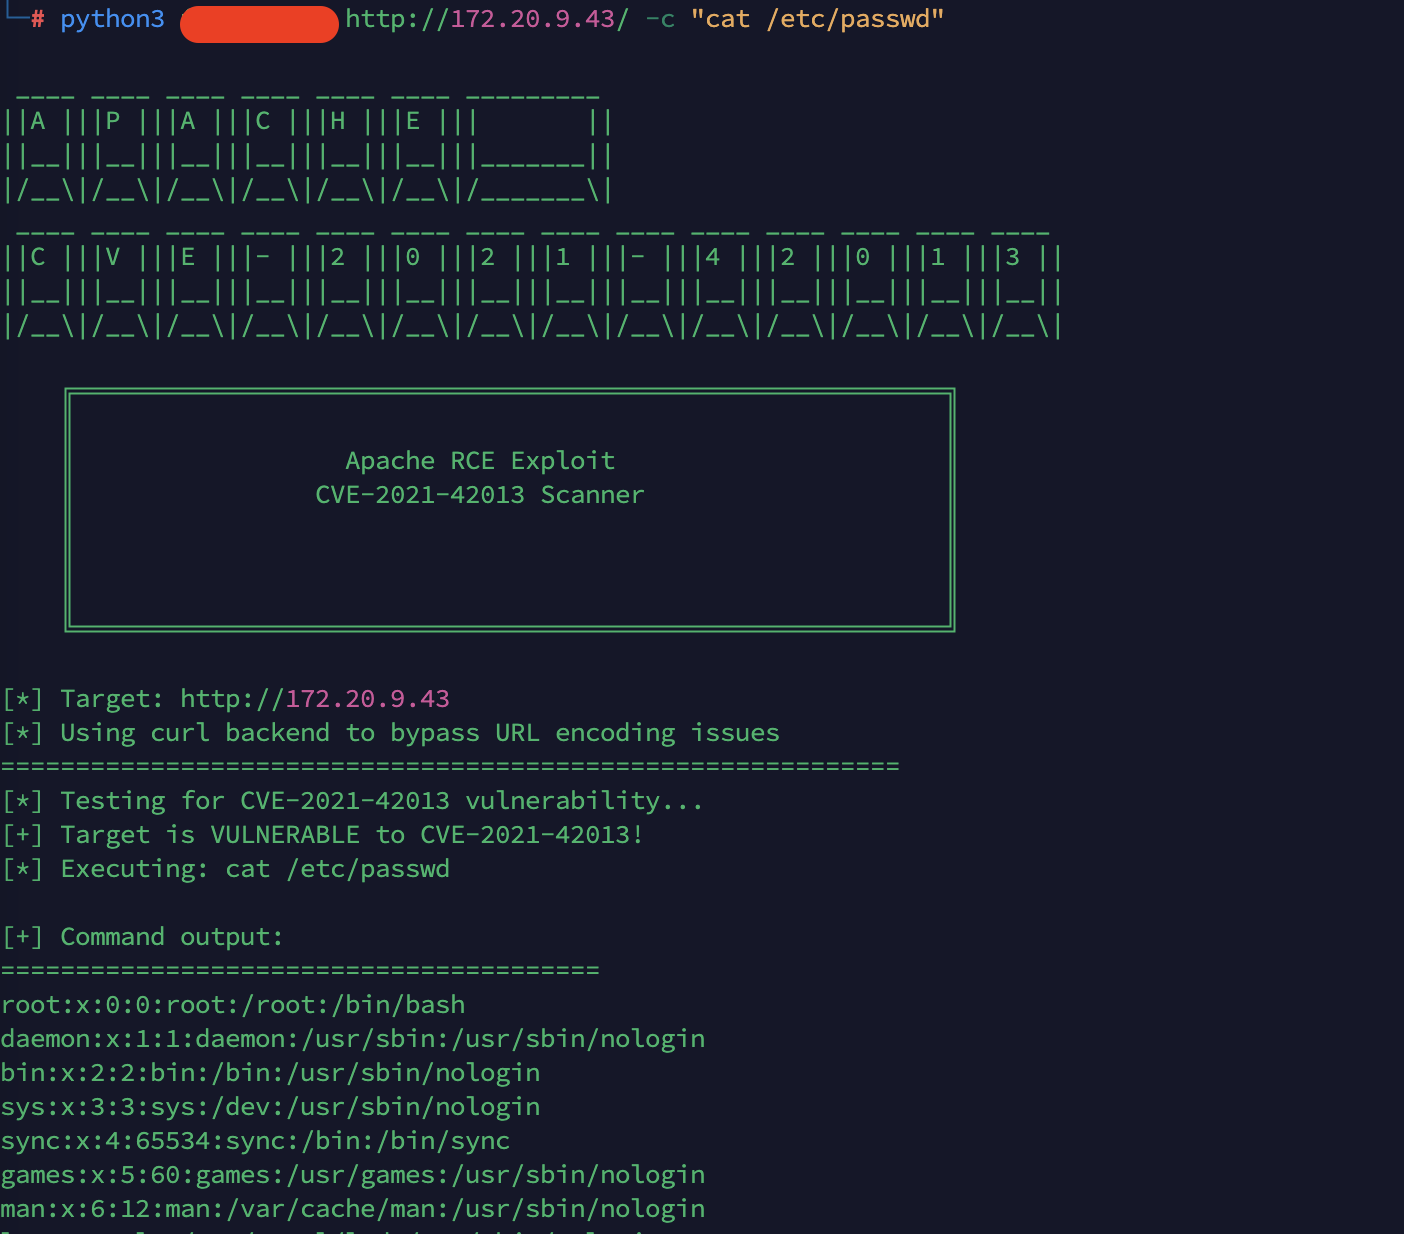 fakhricrd/apache-cve-2021-42013-rce-exploit
A powerful and reliable exploit tool for Apache HTTP Server vulnerabilities CVE-2021-41773 and CVE-2021-42013. This tool provides remote code…
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 kh4sh3i/cve-2023-22527
Proof-of-concept exploit for CVE-2023-22527, a Server-Side Template Injection (SSTI) vulnerability in Atlassian Confluence enabling remote code…
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 sentilaso1/cve-2025-24813-apache-tomcat-rce-poc
Proof of Concept for CVE-2025-24813, a Remote Code Execution vulnerability in Apache Tomcat. This PoC exploits unsafe deserialization via crafted…
 aruthw/cve-2014-6271
Exploit for CVE-2014-6271 (Shellshock) targeting vulnerable Bash environments, enabling remote code execution via crafted HTTP requests.
 yunus-a1i/cve-2021-3007-docker-poc
Reproducible Proof-of-Concept for CVE-2021-3007 (Laminas/Zend HTTP deserialization RCE) with a standalone exploit script, Nuclei template, and…
 frivolous-scholar/cve-2017-5941-nodejs-rce
Proof-of-concept exploit for CVE-2017-5941, a remote code execution vulnerability in Node.js. Demonstrates exploitation via crafted HTTP requests.
 shreesh1/cve-2014-0226-poc
Proof-of-concept exploit for CVE-2014-0226, targeting a man-in-the-middle vulnerability in Apache HTTP Server's mod_ssl to demonstrate SSL/TLS…
 davidblakecoe/axios-cve-2025-27152-poc
Proof-of-concept exploit for CVE-2025-27152 in Axios, demonstrating a server-side request forgery vulnerability in the popular HTTP client library.