CVE-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

CVE-2026-64824 — Home Assistant backup-restore symlink path traversal → root RCE. First working PoC, verified on real HA 2026.5.4 (sitecustomize.py…

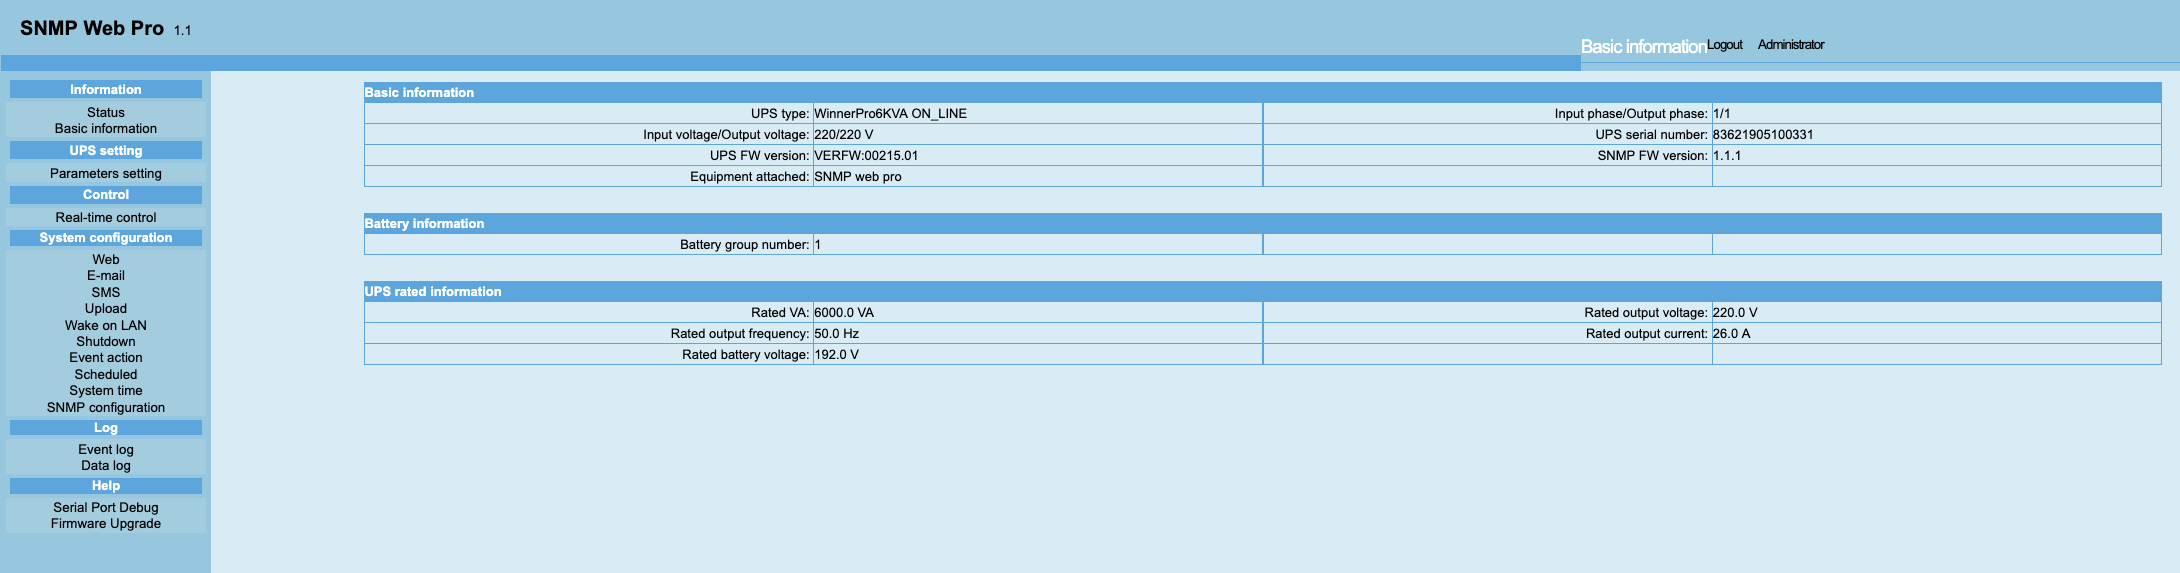
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1

Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…

CVE-2026-8836 — lwIP SNMPv3 stack-based buffer overflow PoC (CVSS 9.8)

Remote code execution for Grandstream GXV3175 VOIP phone.

An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.

Proof-of-Concept for CVE-2025-2082, demonstrating function pointer overwrite via signed-to-unsigned integer conversion bug in Tesla VCSEC, leading to…

Proof-of-concept exploit for a remote buffer overflow vulnerability in KNX ETS4 management software, demonstrating ROP-based code execution via…

Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

Example project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.

Homebrew enabler for PS Vita

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)

RISC-V Virtual Machine

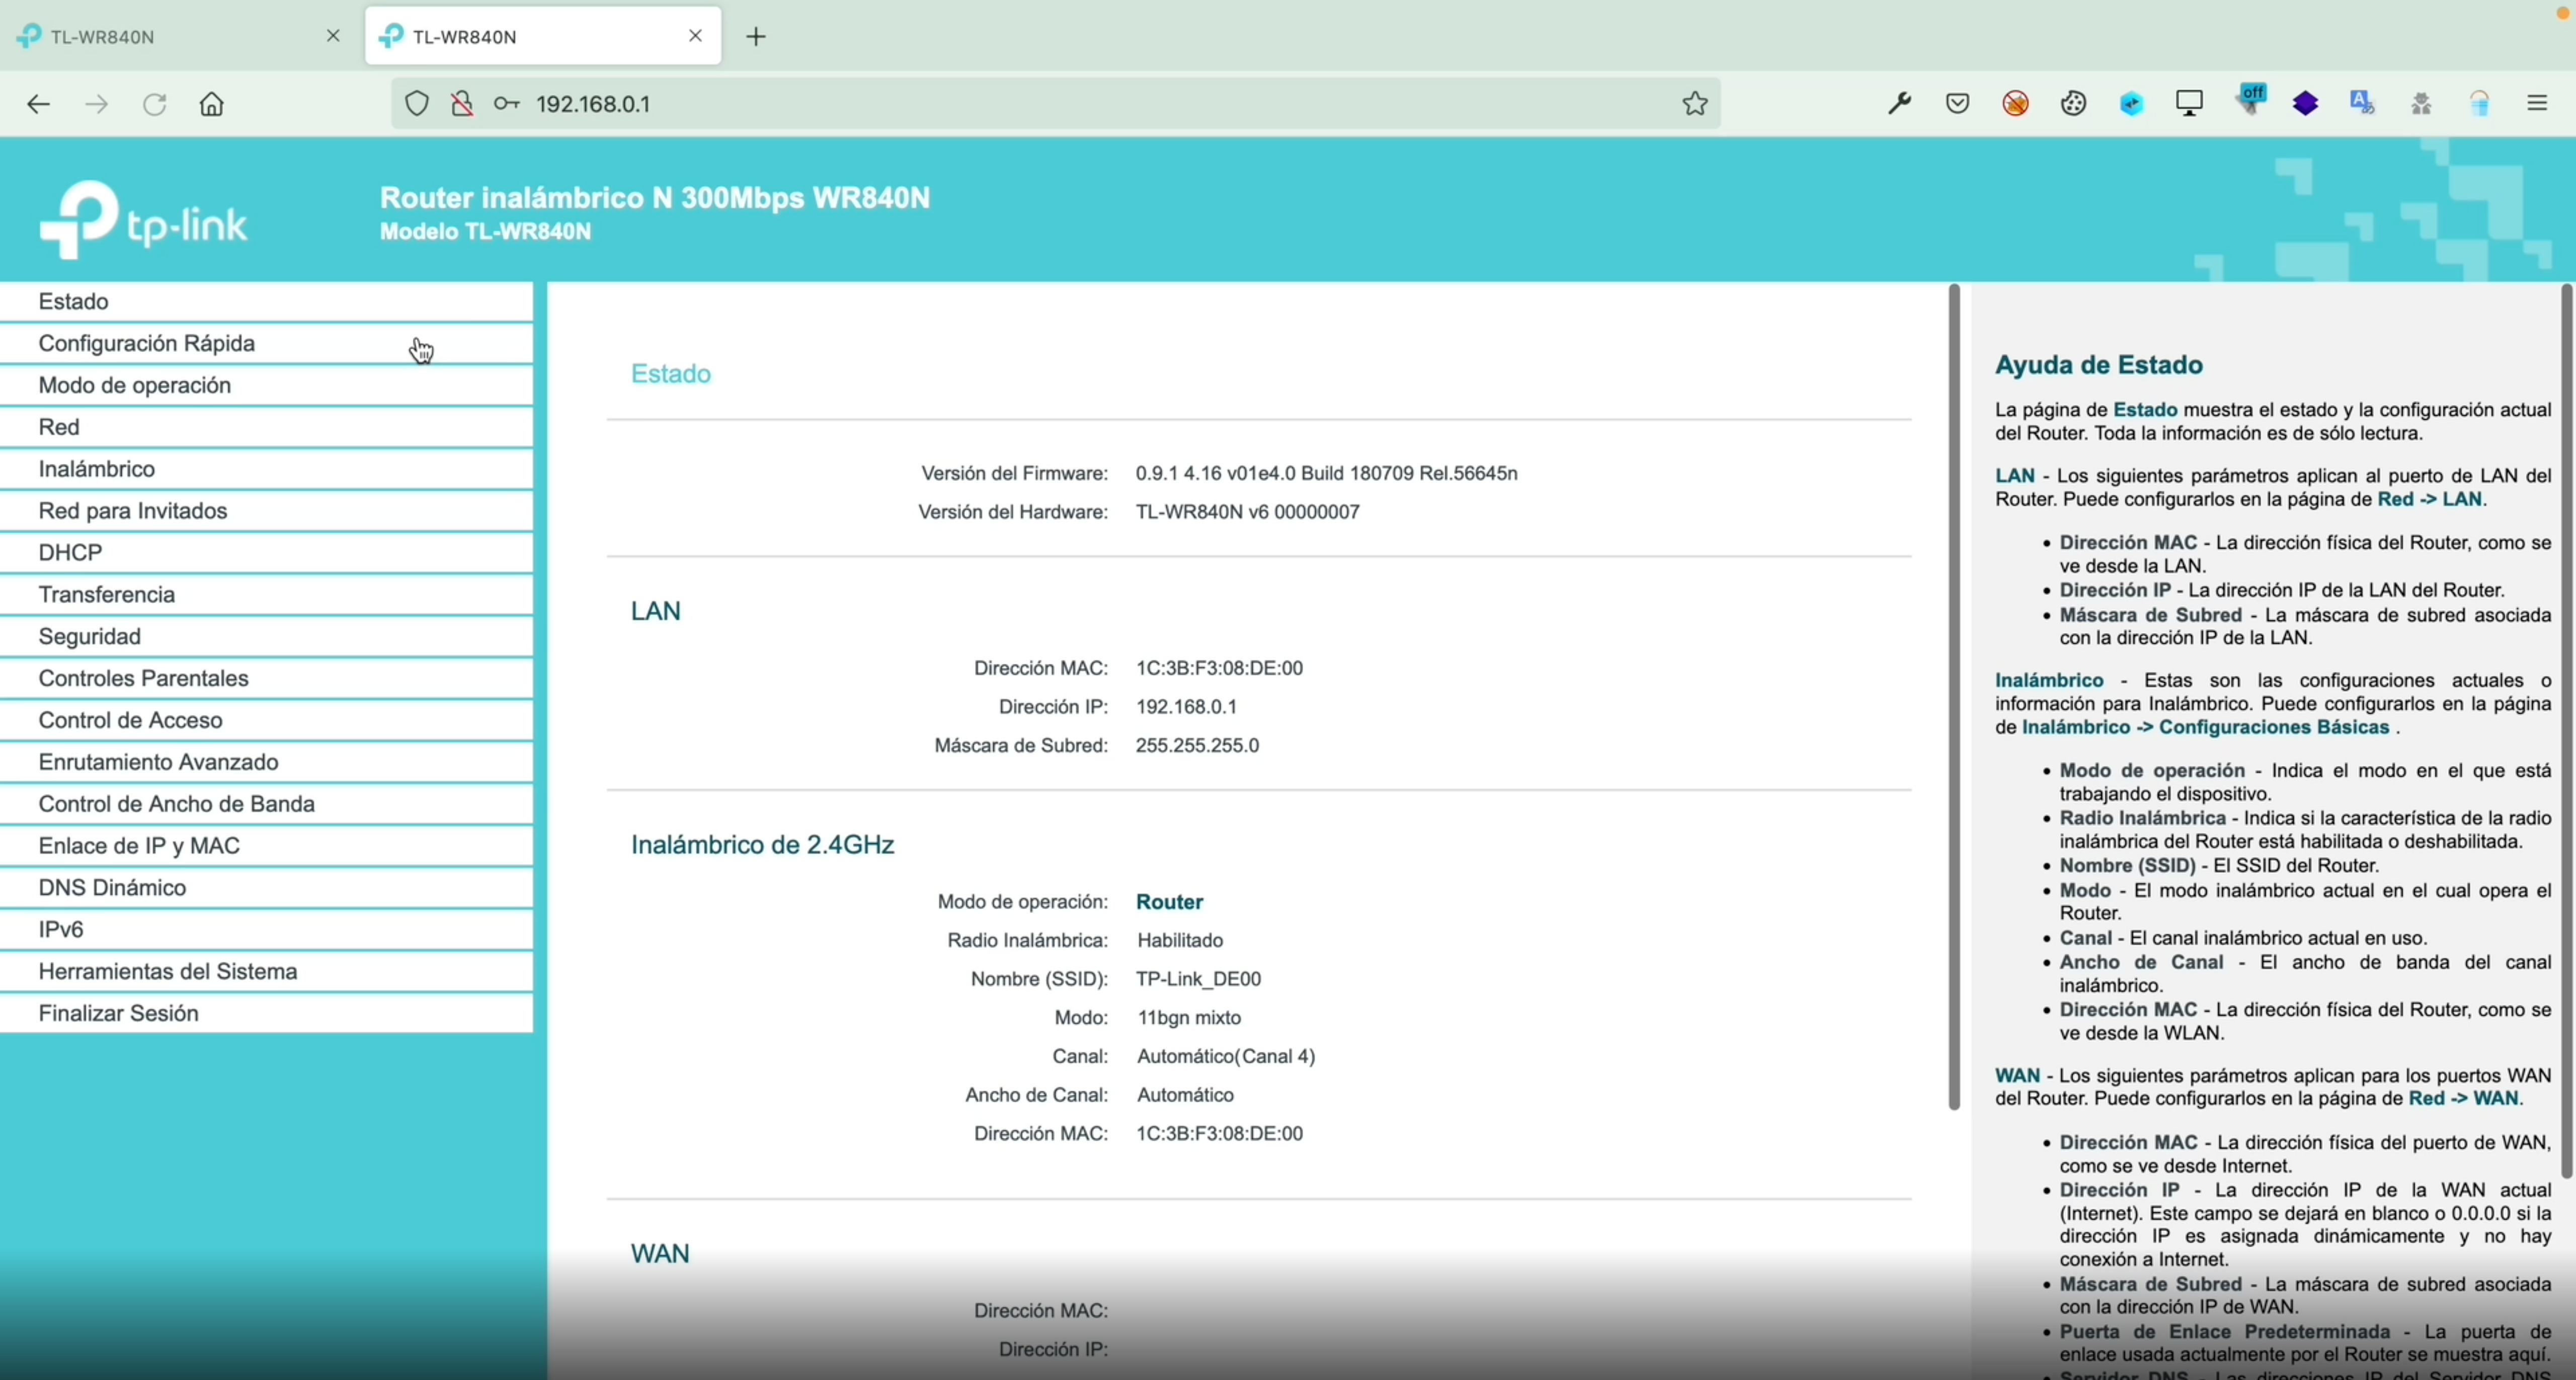
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…