
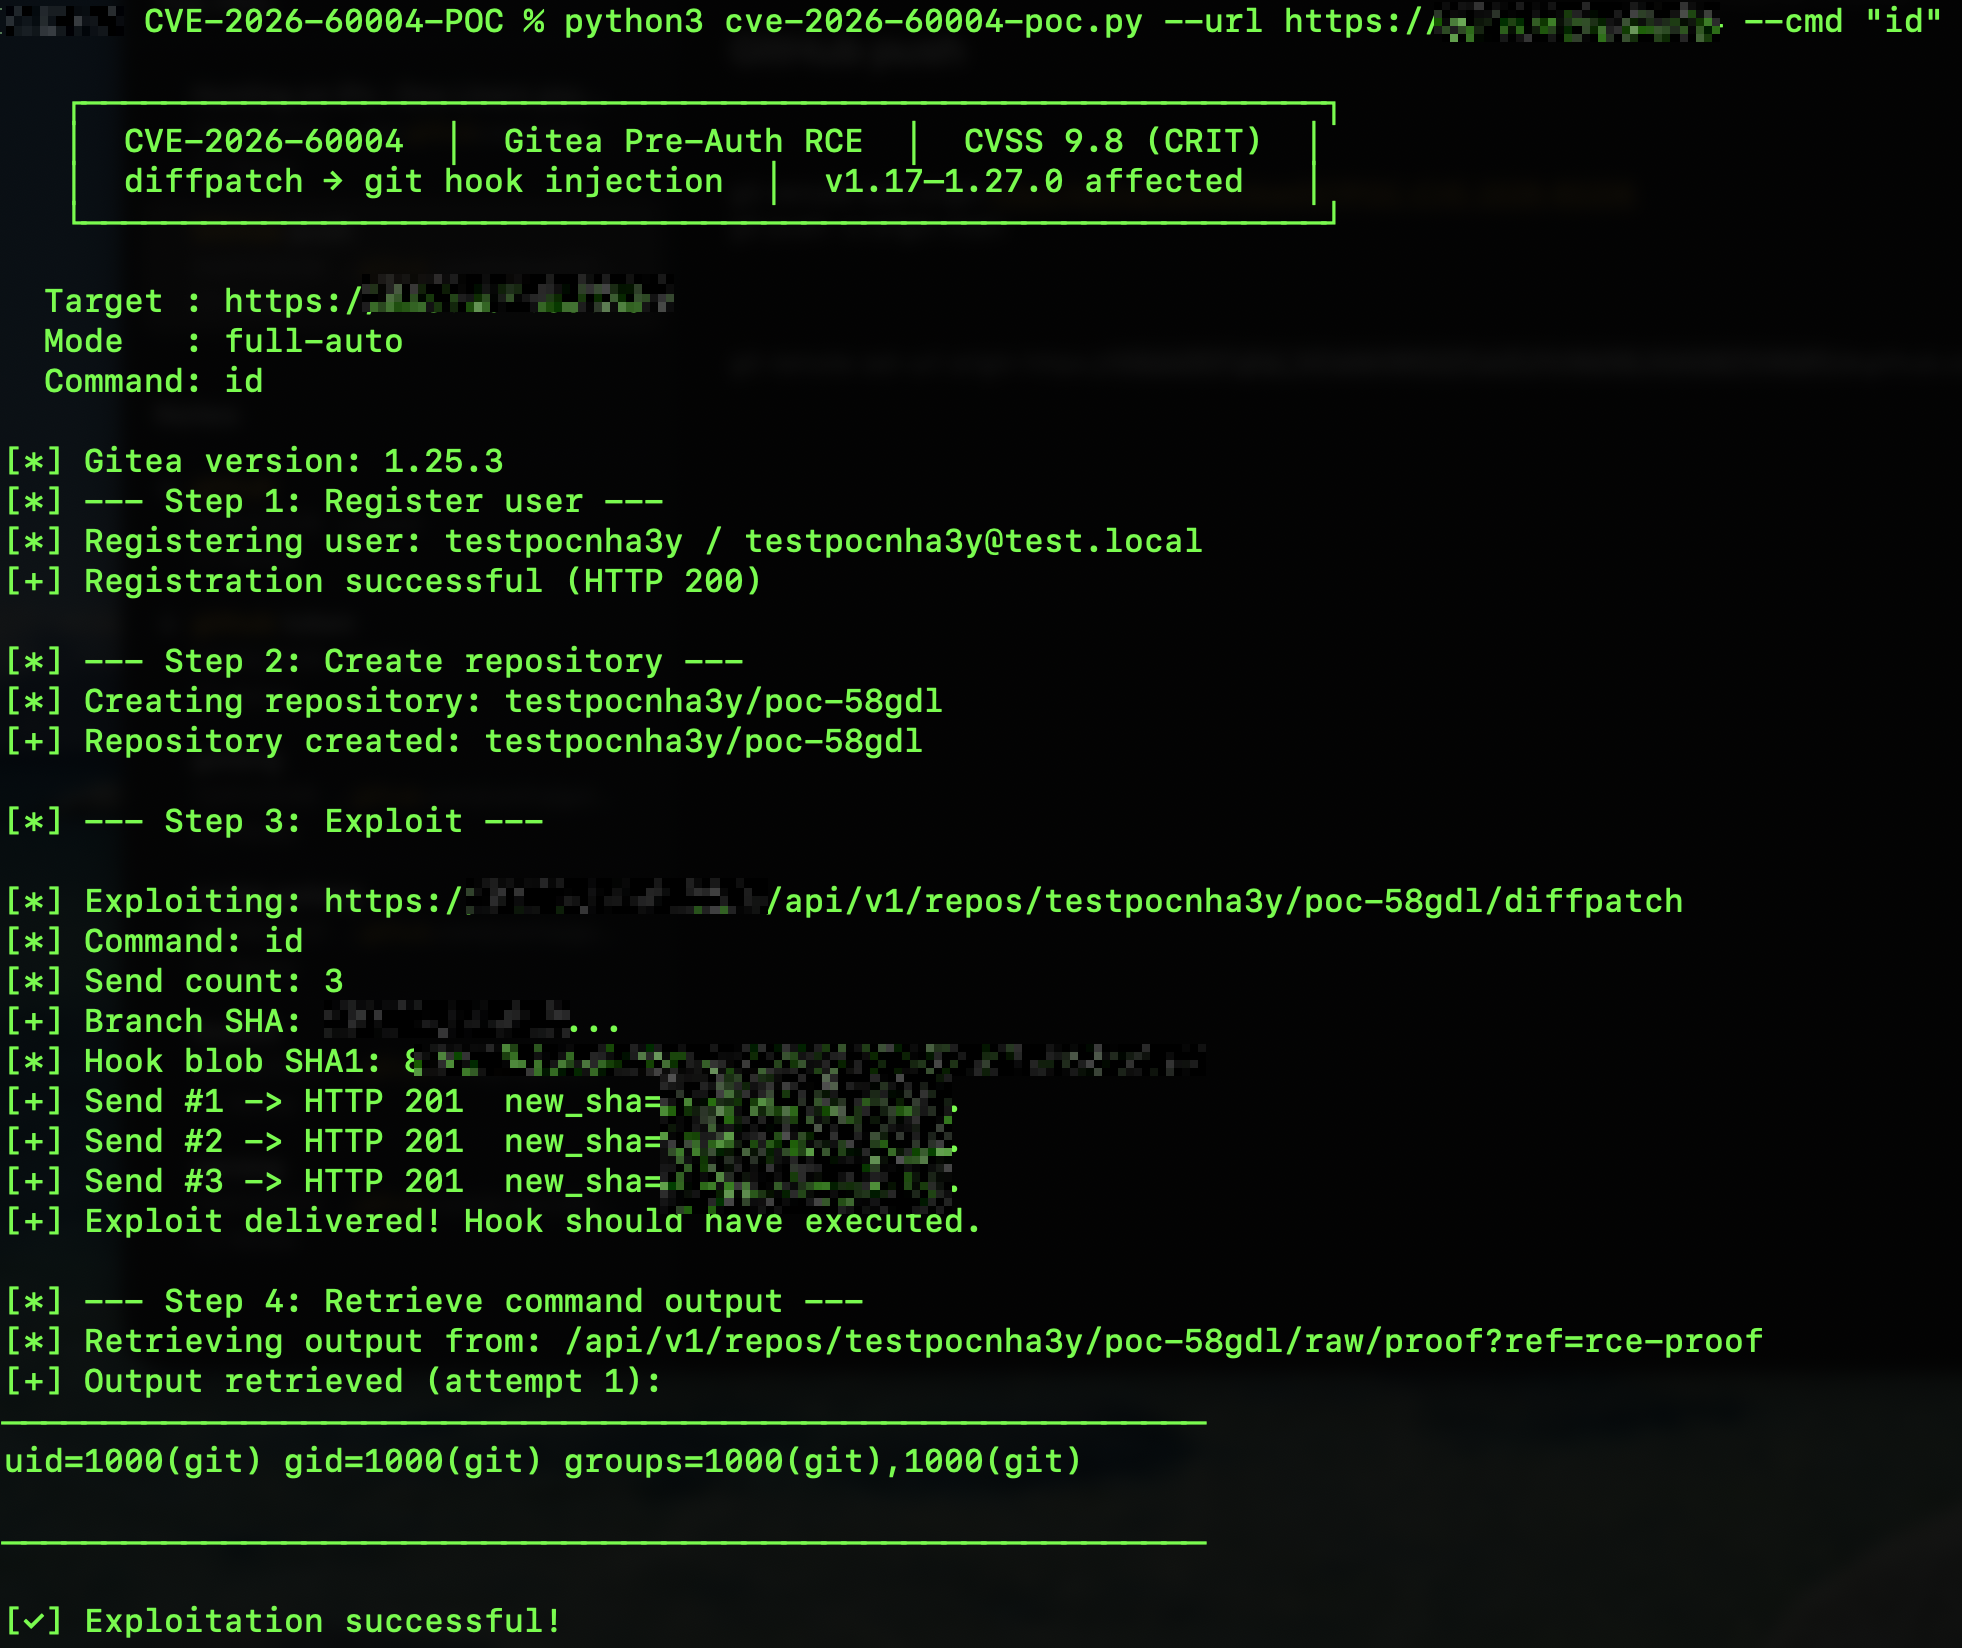
CVE-2026-60004-POC
 imbas007/cve-2026-60004-poc
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)
exploitationpayload-developmentpenetration-testing+4
16
imbas007/cve-2026-60004-pocCVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)
 momika233/cve-2024-21006
Proof-of-concept exploit for CVE-2024-21006 targeting Oracle WebLogic Server via T3/IIOP, enabling unauthenticated remote access to critical data.
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 xxconi/cve-2026-12415-or-cve-2026-12416.py
CVE-2026-12415-or-CVE-2026-12416.py
 abbarhissarh/cve-exploit
CVE-2020-2551 Exploiter
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
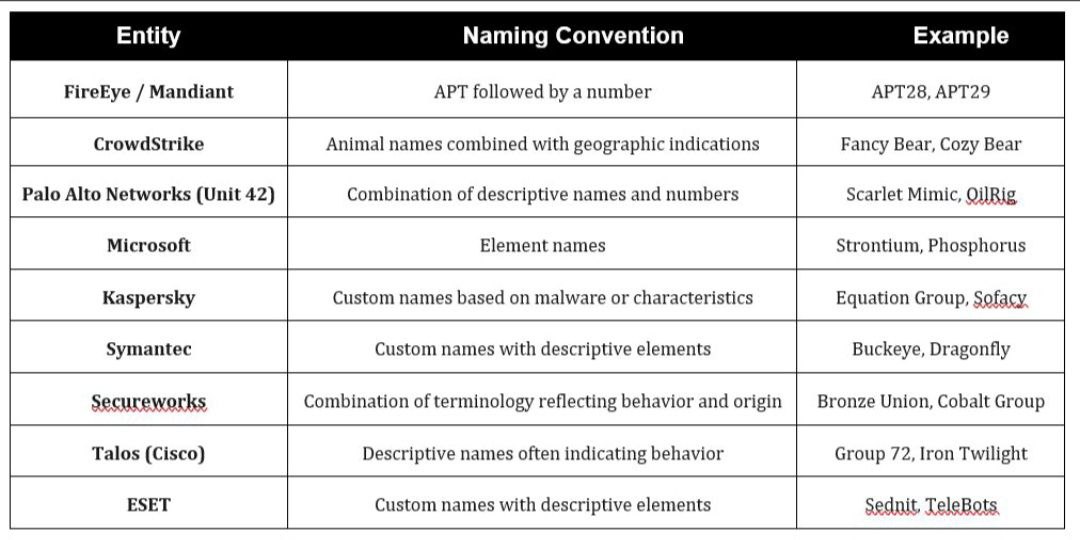 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
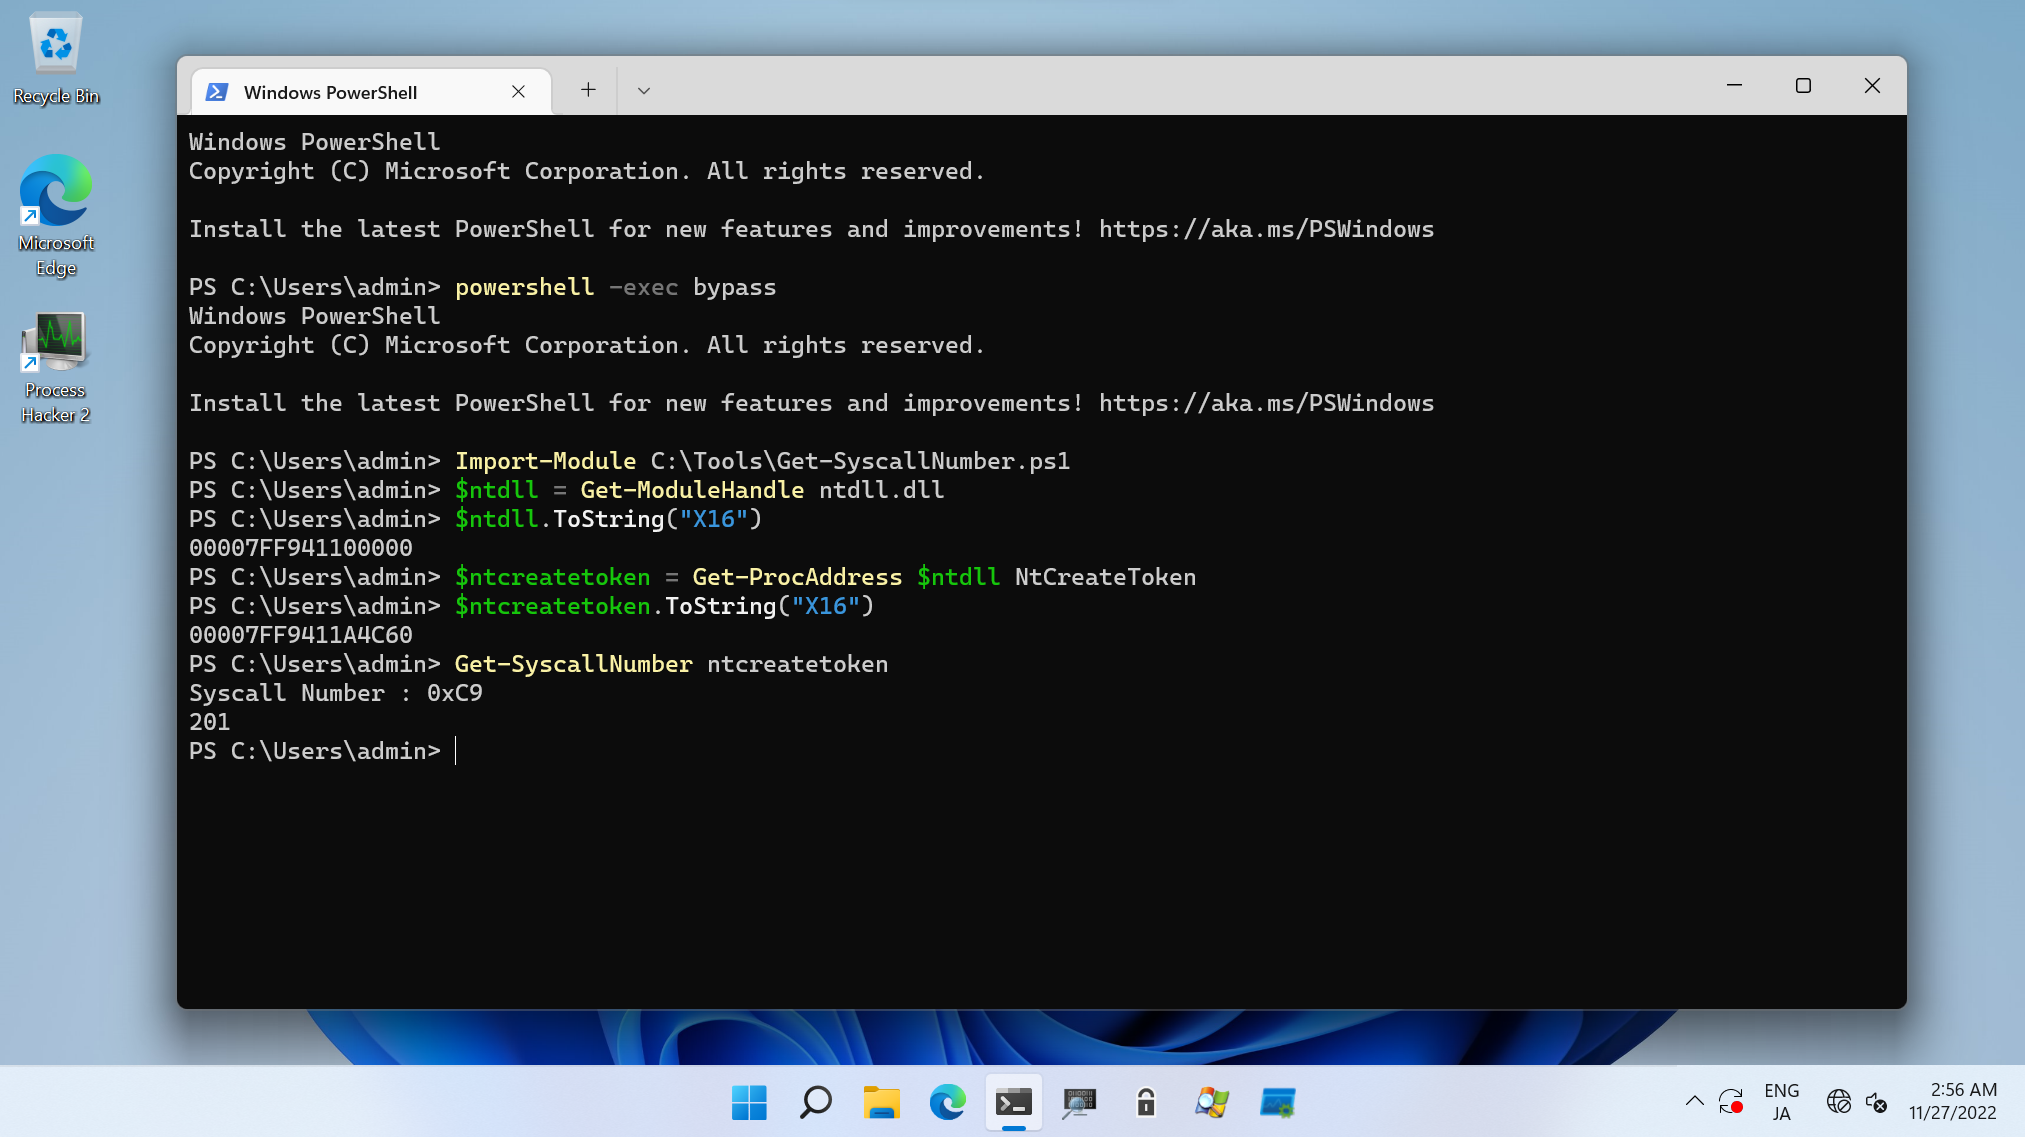 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
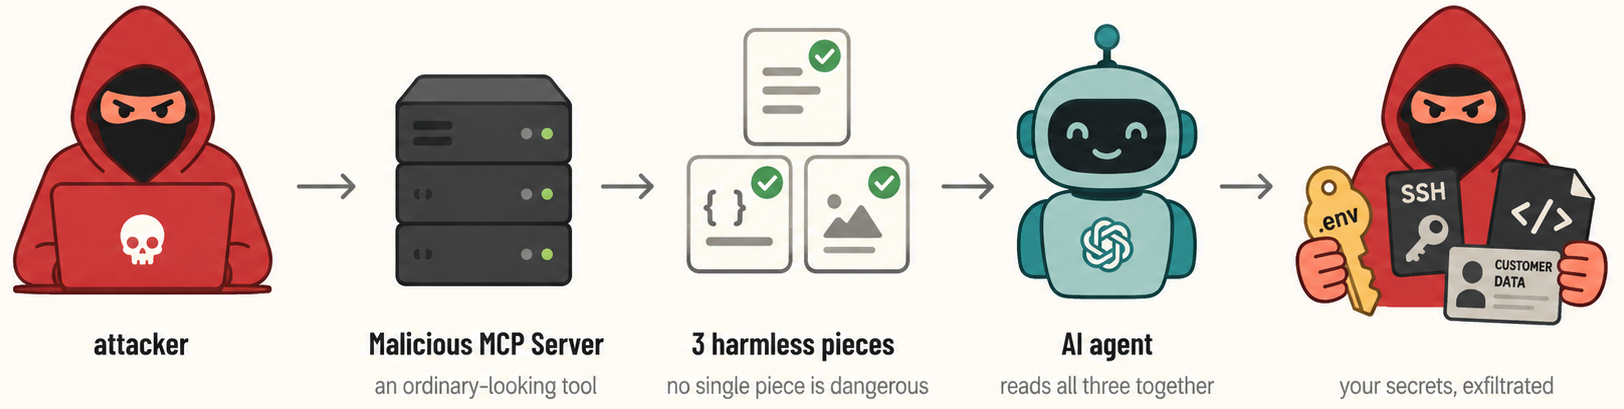 asset-group/ghostsplice
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
 bishopfox/sliver
Adversary Emulation Framework
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.