-CVE-2024-21683-RCE-in-Confluence-Data-Center-and-Server

This vulnerability could allow an attacker to take complete control of a vulnerable Confluence server. This could allow the attacker to steal data,…

This vulnerability could allow an attacker to take complete control of a vulnerable Confluence server. This could allow the attacker to steal data,…

PoC for CVE-2026-32475: Elementor Pro <=4.2.1 unauthenticated file upload to RCE. Stdlib-only Python.

Standalone Python 3 exploit for CVE-2017-17562 targeting GoAhead web server 2.5–3.6.5 with automated CGI endpoint discovery and reverse shell payload…

Use CVE-2026-43074 to disable SELinux on Android (Linux 6.6/6.12)

Remote Code Execution on Confluence Servers : CVE-2021-26084

GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)

Proof-of-concept exploit for CVE-2014-7911 targeting Android 4.4.4 on Nexus5, using a custom ROP chain to escalate privileges and write files as the…

CVE-2024-53691

exploit for cve-2014-7911; android; java deserialization ;system privilege;ace;

One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.

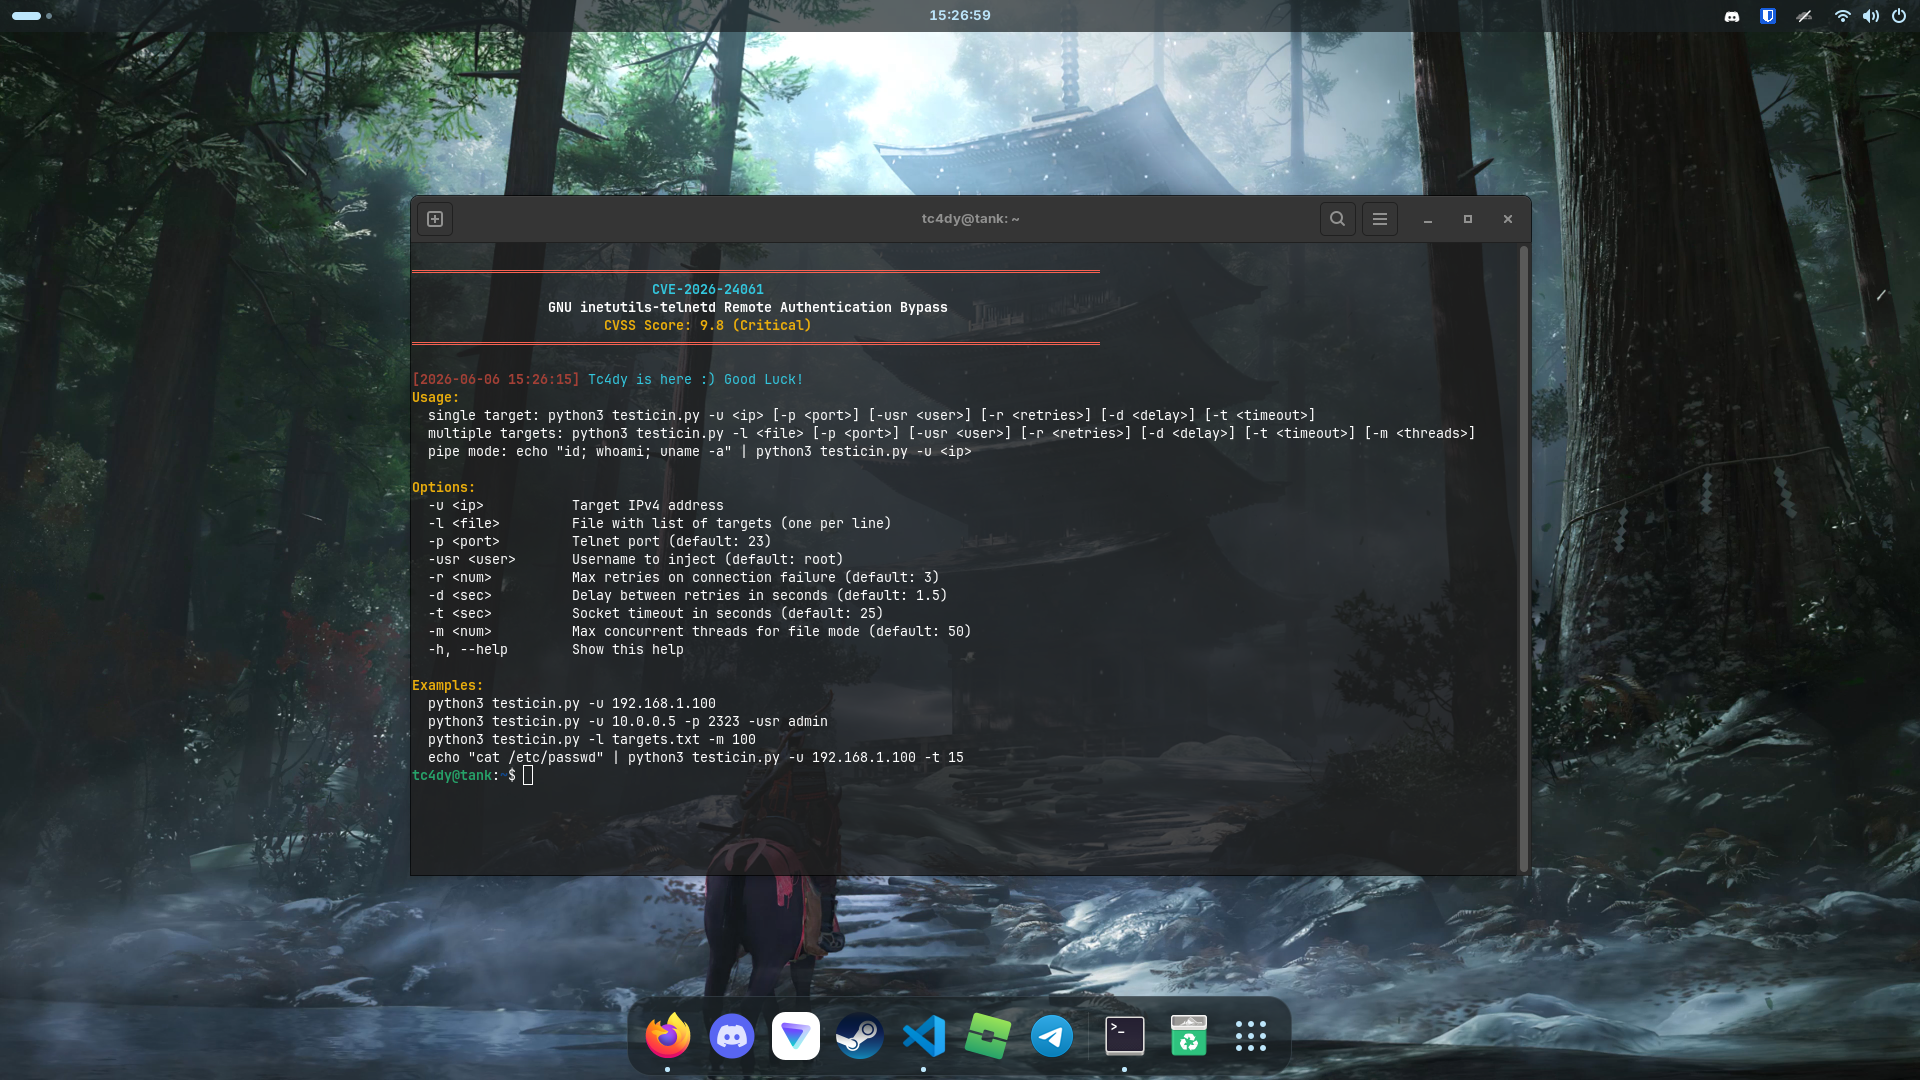
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…

Proof of concept for CVE-2018-4150 by @cmwdotme

The PoC demonstrates the potential for remote code execution by exploiting the identified security flaw.

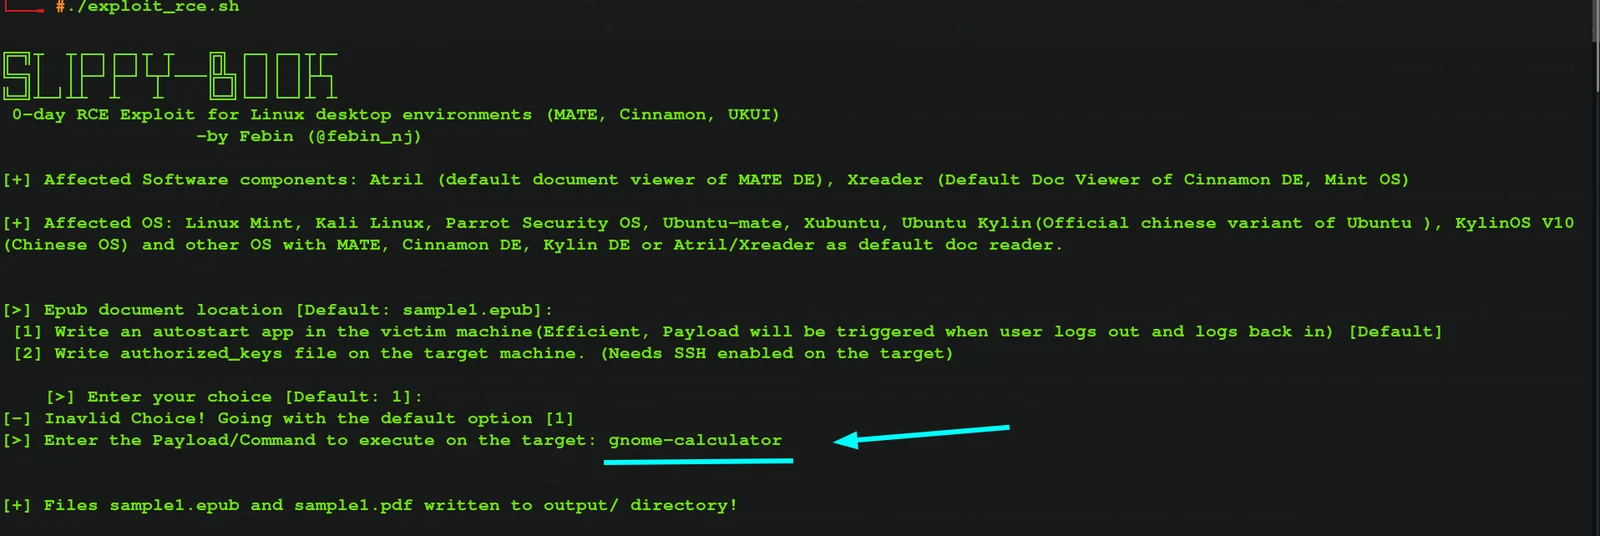
CVE-2023-44451, CVE-2023-52076: RCE Vulnerability affected popular Linux Distros including Mint, Kali, Parrot, Manjaro etc. EPUB File Parsing…

CVE-2020-1938 / CNVD-2020-1048 Detection Tools

Python reimplementation of the CVE-2025-27840 exploit code presented at RootedCON, providing a ready-to-use proof-of-concept for security testing.

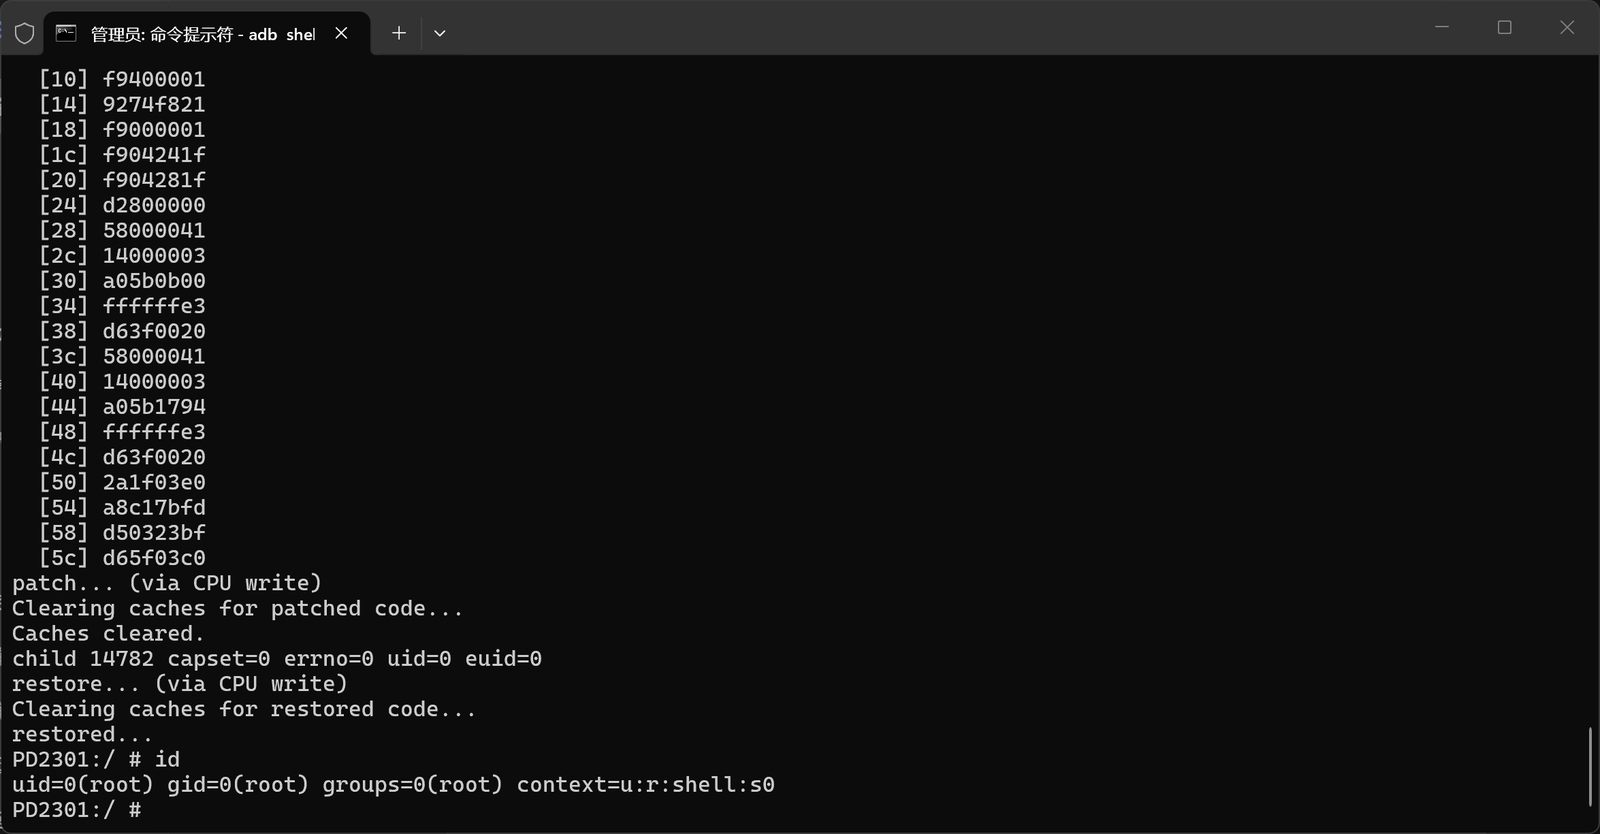
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell