
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
716 results
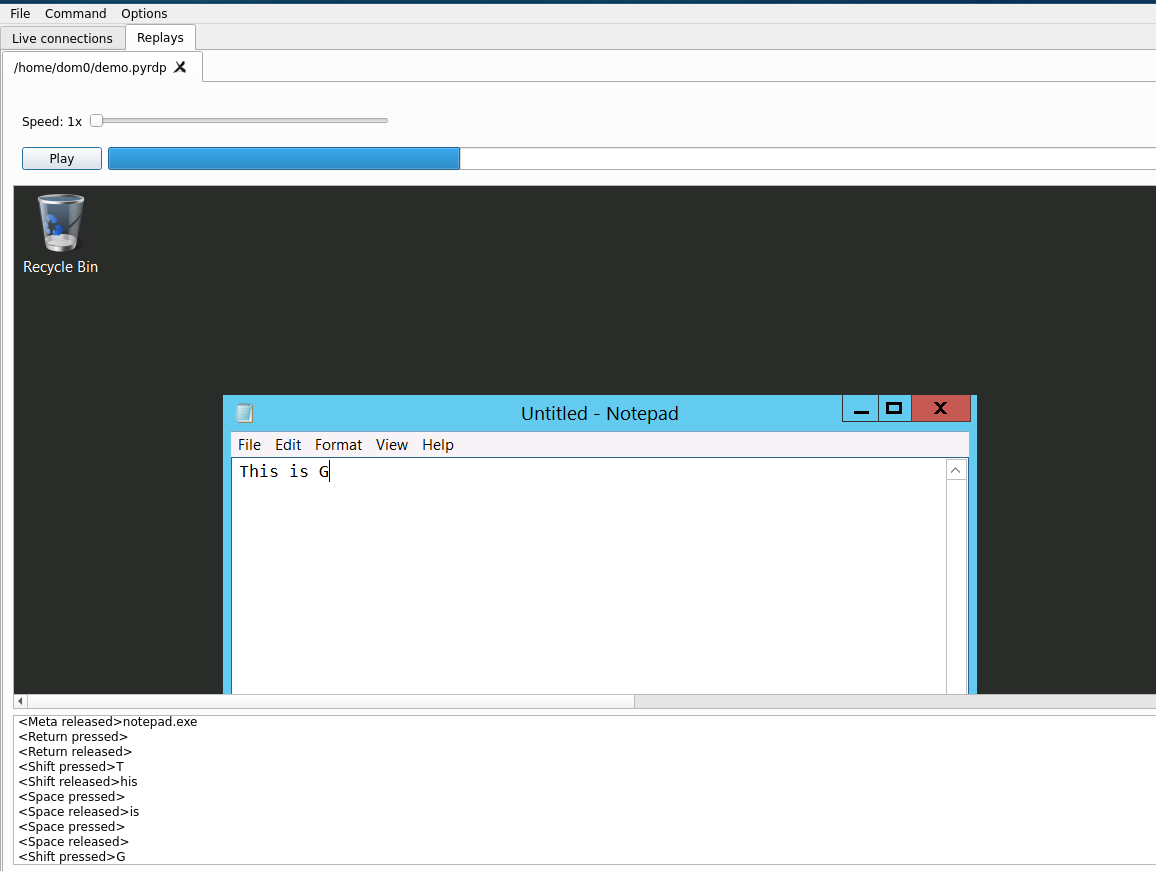
pyrdp preview

pyrdp

GitHubgosecure/pyrdp

RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
ctfeducationexploitation+9
1.8k5 months ago
meterssh preview

meterssh

GitHubtrustedsec/meterssh

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
command-and-controlexploitationpayload-development+4
5289 years ago
PlasmaRAT preview

PlasmaRAT

GitHubmwsrc/plasmarat

Remote Access Trojan(RAT), Miner, DDoS
command-and-controldata-exfiltrationmalware-analysis+3
4019 years ago
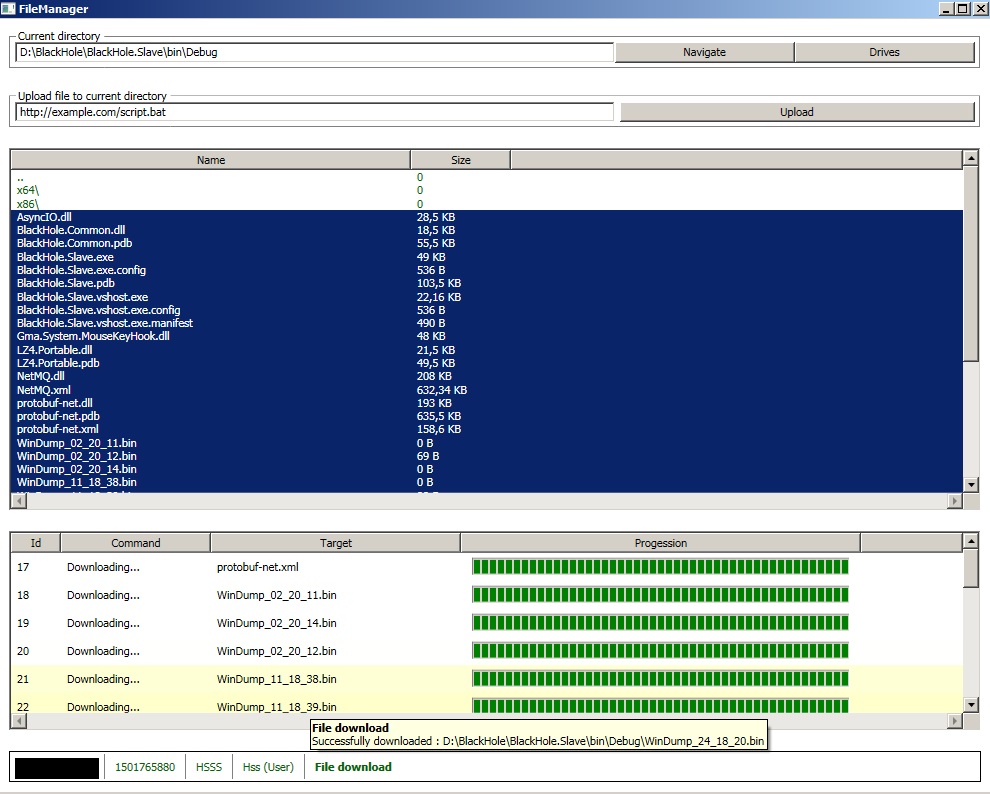
BlackHole preview

BlackHole

GitHubhussein-aitlahcen/blackhole

C# RAT (Remote Administration Tool)
command-and-controleducationpayload-development+5
3039 years ago
sagemcom-fast-3890-exploit preview

sagemcom-fast-3890-exploit

GitHublyrebirds/sagemcom-fast-3890-exploit

Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
binary-exploitationembedded-systems-securityexploitation+4
2236 years ago
Umbra preview

Umbra

GitHubh3xduck/umbra

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
command-and-controleducationencryption-decryption-tools+6
1365 years ago
python-hacklib preview

python-hacklib

GitHublazorfuzz/python-hacklib

hacklib - pentesting, port scanning, and logging in anywhere with Python
exploitationinformation-gatheringpassword-attacks+4
1017 years ago
rvbbit-arsenal preview

rvbbit-arsenal

GitHubbuter-chkalova/rvbbit-arsenal

Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
command-and-controldefensive-toolseducation+5
161 month ago
CVE-2010-2075 preview

CVE-2010-2075

GitHubrushikesh-a-bhujbal/cve-2010-2075

UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
educationexploitationlabs-practice+7
1 month ago
Blackash-CVE-2025-48593 preview

Blackash-CVE-2025-48593

GitHubc0d331ng/blackash-cve-2025-48593

CVE-2025-48593
android-securitybinary-exploitationeducation+5
20 years ago
CVE-2017-16524 preview

CVE-2017-16524

GitHubrealistic-security/cve-2017-16524

Unrestricted file upload vulnerability - Web Viewer 1.0.0.193 on Samsung SRN-1670D
exploit-frameworkspayload-developmentpenetration-testing+3
48 years ago
parquet-rce-poc-CVE-2025-30065 preview

parquet-rce-poc-CVE-2025-30065

GitHubmouadk/parquet-rce-poc-cve-2025-30065

Proof-of-concept exploit for CVE-2025-30065 demonstrating remote class instantiation and SSRF via malicious Parquet files in Java applications.
educationexploitationpayload-development+3
31 year ago
CVE-2026-63720-datamodel-code-generator preview

CVE-2026-63720-datamodel-code-generator

GitHubrahulreddykarne/cve-2026-63720-datamodel-code-generator

Code injection (RCE) in datamodel-code-generator via unvalidated customBasePath (CVE-2026-63720)
educationexploitationpayload-development+2
3 months ago
CVE-2026-23744 preview

CVE-2026-23744

GitHuboryk0/cve-2026-23744

CVE-2026-23744 Reverse shell
exploitationpayload-developmentpenetration-testing+3
4 months ago
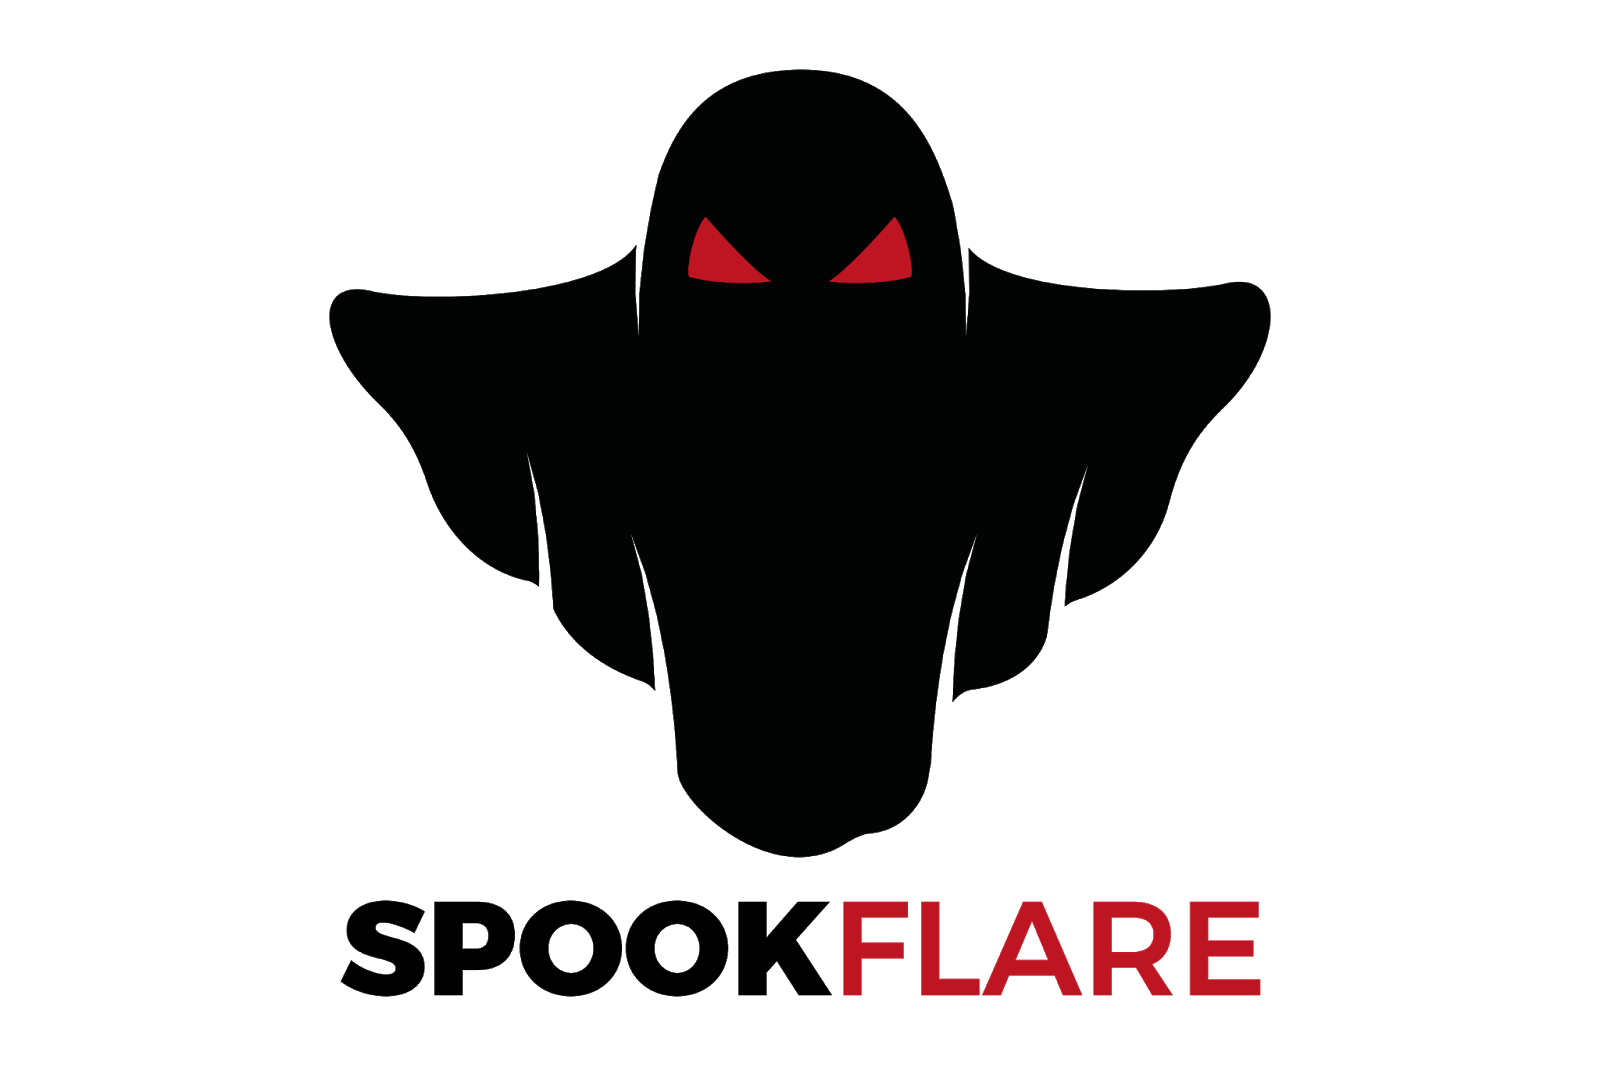
Harald preview

Harald

GitHubgmh5225/harald

An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
1 year ago
SpookFlare preview
Archived

SpookFlare

GitHubhlldz/spookflare

Loader, dropper generator with multiple features for bypassing client-side and network-side countermeasures.
exploit-frameworkspayload-developmentpayload-generation+1
9427 years ago
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

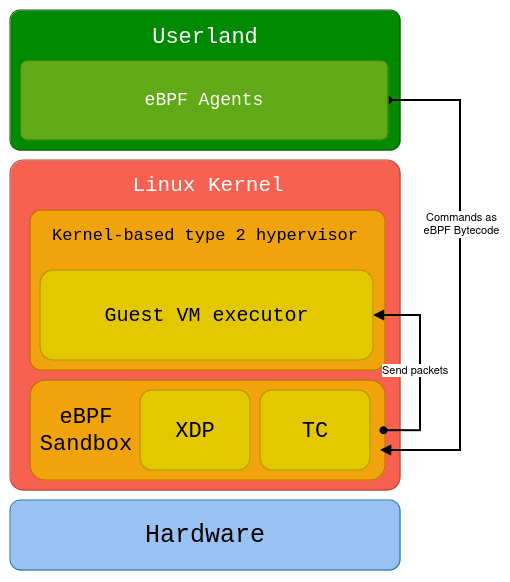
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

binary-exploitationcommand-and-controlids-ips-evasion+7
3408 months ago
M-Botnet preview
Archived

M-Botnet

GitHubm507/m-botnet

A C2 project that controls a self-propagating MS17-010 worm.

command-and-controleducationexploitation+4
785 years ago
Previous123…40Next