
ABL_ROP
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
android-securitybinary-exploitationembedded-systems-security+4
7
boredpentester/abl_ropExperimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…

 michaelroland/omapi-cve-2015-6606-exploit
Simple Exploit for Verification of CVE-2015-6606
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 reactivezero/cve-2026-20251
CVE-2026-20251 — Splunk Secure Gateway jsonpickle deserialization RCE (CVSS 8.8) | ReactiveZero Security Research
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
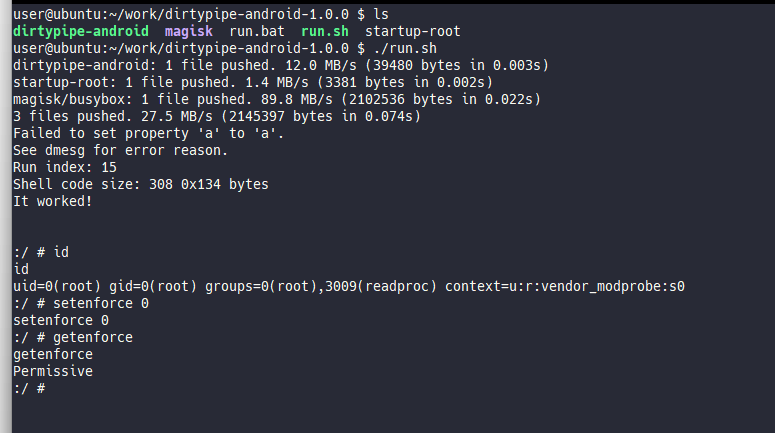 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 snothin/ghostlock-s26
GhostLock (CVE-2026-43499) for the Galaxy S26
 0x33c0unt/cve-2024-21633
MobSF Remote code execution (via CVE-2024-21633)
 shinyquagsire23/cve-2020-12753-poc
A proof-of-concept for CVE-2020-12753
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.
 martinmullins/cve-2016-8655_android
Android attempt at PoC CVE-2016-8655
