
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
305 results
edrEvasionWorkshop preview

edrEvasionWorkshop

GitHubtyeurada/edrevasionworkshop

Workshop materials for “Step-by-Step Malware Development: Evading EDR from Loaders to the Kernel” presented at DEF CON 34 and BSidesLV 2026. Covers…
defensive-toolseducationexploitation+5
397
2 months ago
DInvoke preview

DInvoke

GitHubthewover/dinvoke

Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
adversarial-attackpayload-developmentpost-exploitation+1
7914 years ago
azureOutlookC2 preview

azureOutlookC2

GitHubboku7/azureoutlookc2

Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
api-securitycloud-securitycommand-and-control+2
5043 years ago
anamnesis-release preview

anamnesis-release

GitHubseanheelan/anamnesis-release

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

ai-securitybinary-exploitationeducation+9
6289 months ago
NXLoader preview

NXLoader

GitHubdavidbuchanan314/nxloader

My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)
android-securityexploitationhardware-iot-security+2
5628 years ago
Stracciatella preview

Stracciatella

GitHubmgeeky/stracciatella

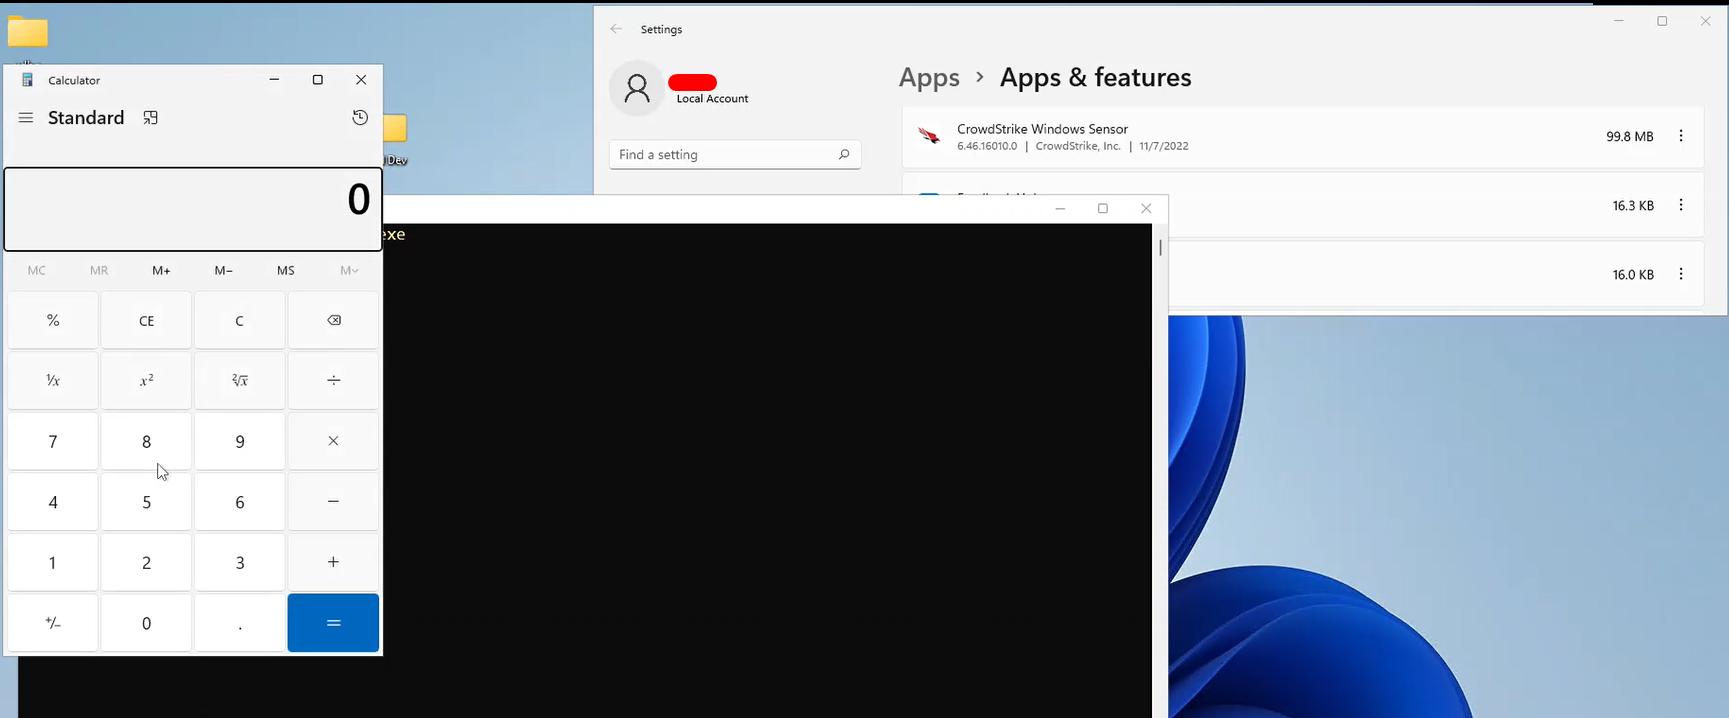
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
command-and-controlexploit-frameworksids-ips-evasion+7
5434 years ago
D1rkLdr preview

D1rkLdr

GitHubsaadahla/d1rkldr

Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…

ids-ips-evasionpayload-developmentred-teaming+1
3233 years ago
Burp2Malleable preview

Burp2Malleable

GitHubcodextf2/burp2malleable

Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
command-and-controlids-ips-evasionpayload-development+2
4183 years ago
xsser preview

xsser

GitHubvarbaek/xsser

From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
exploitationpayload-developmentpenetration-testing+3
4246 years ago
ad-autopwn preview

ad-autopwn

GitHubjonaslejon/ad-autopwn

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
371 month ago
MemoryModulePP preview

MemoryModulePP

GitHubstrivexjun/memorymodulepp

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

binary-analysisexploitationmalware-analysis+2
2256 years ago
FruityC2 preview

FruityC2

GitHubxtr4nge/fruityc2

FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
command-and-controlexploit-frameworkspayload-development+4
2068 years ago
ropium preview

ropium

GitHubboyan-milanov/ropium

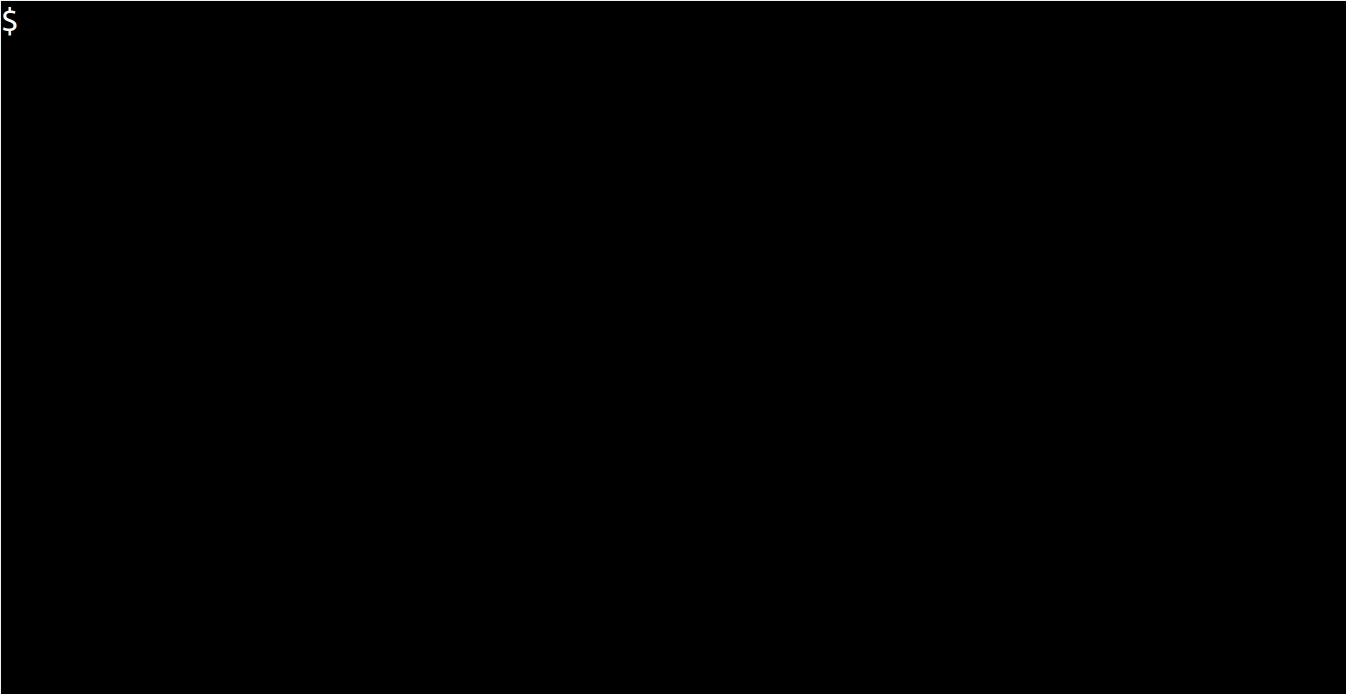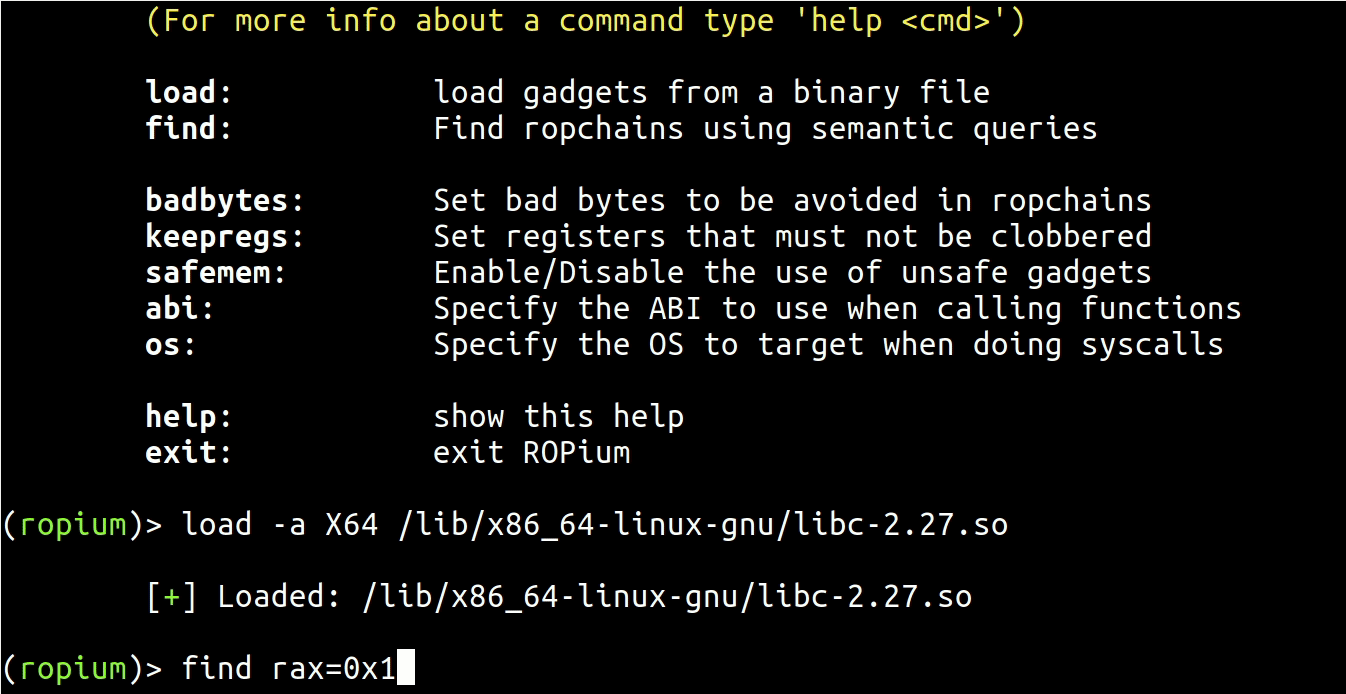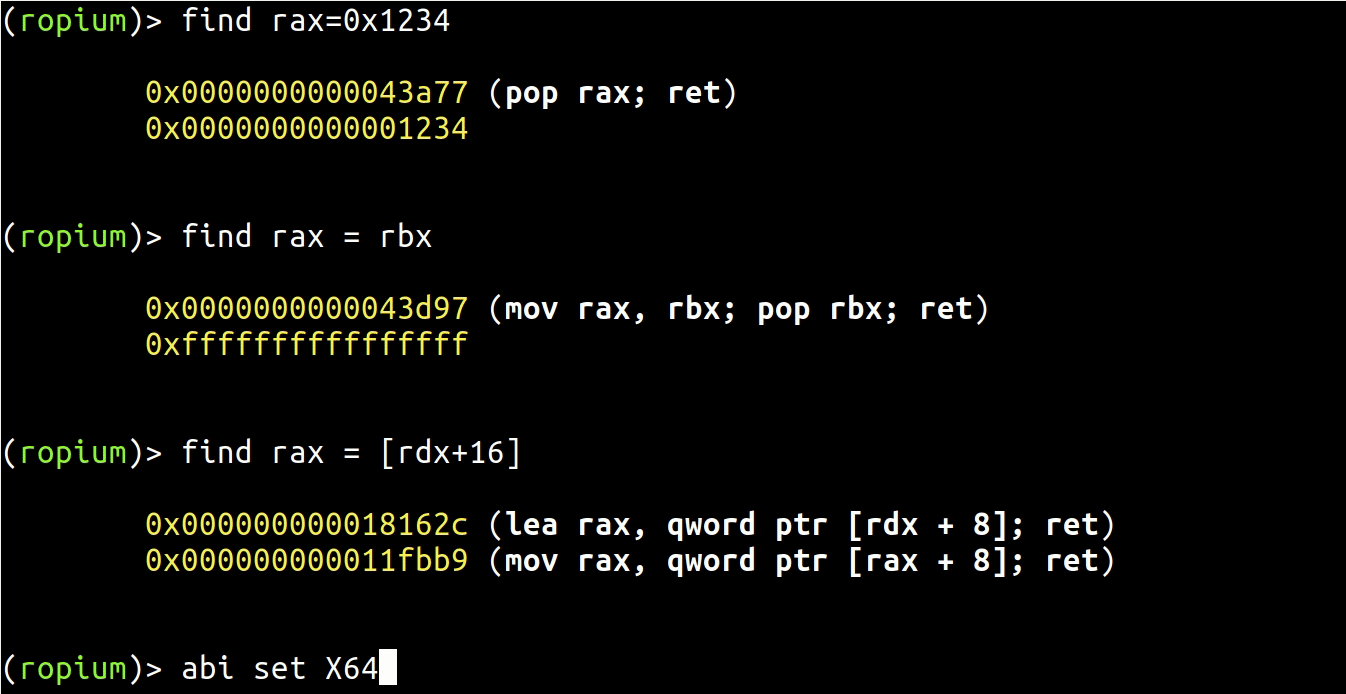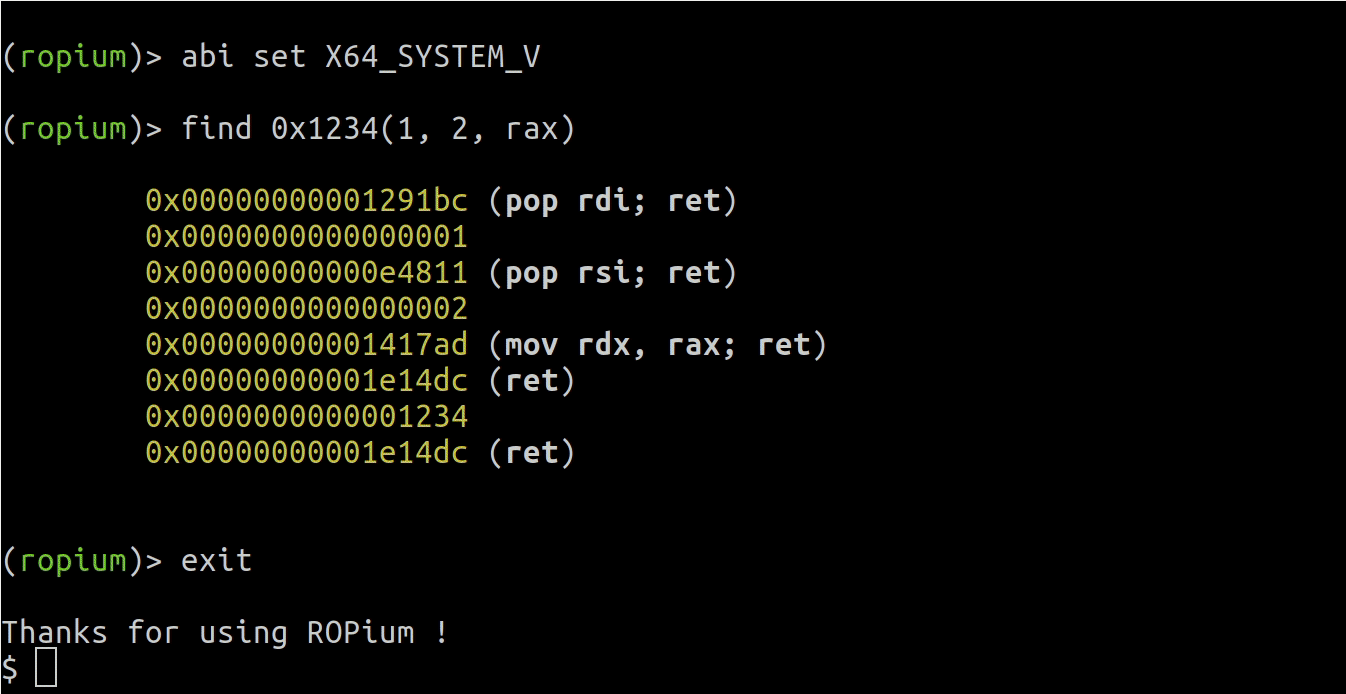
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
binary-exploitationexploit-frameworkspayload-development+2
4024 years ago
SharpZipRunner preview

SharpZipRunner

GitHubjfmaes/sharpziprunner

Executes position independent shellcode from an encrypted zip
exploitationpayload-developmentpayload-generation+3
3035 years ago
Nim-RunPE preview

Nim-RunPE

GitHubs3cur3th1ssh1t/nim-runpe

A Nim implementation of reflective PE-Loading from memory

binary-exploitationexploitationmalware-analysis+3
2952 years ago
UnhookMe preview

UnhookMe

GitHubmgeeky/unhookme

Dynamic Windows API resolver and unhooker that detects and restores hooked functions (IAT, EAT, inline patches) to invoke unmonitored system calls…

defensive-toolspayload-developmentred-teaming
3484 years ago
cve-2017-7494 preview

cve-2017-7494

GitHubbetab0t/cve-2017-7494

Proof-of-Concept exploit for CVE-2017-7494(Samba RCE from a writable share)
exploitationpayload-developmentpenetration-testing+2
1819 years ago
CoercedPotatoRDLL preview

CoercedPotatoRDLL

GitHubsokarepo/coercedpotatordll

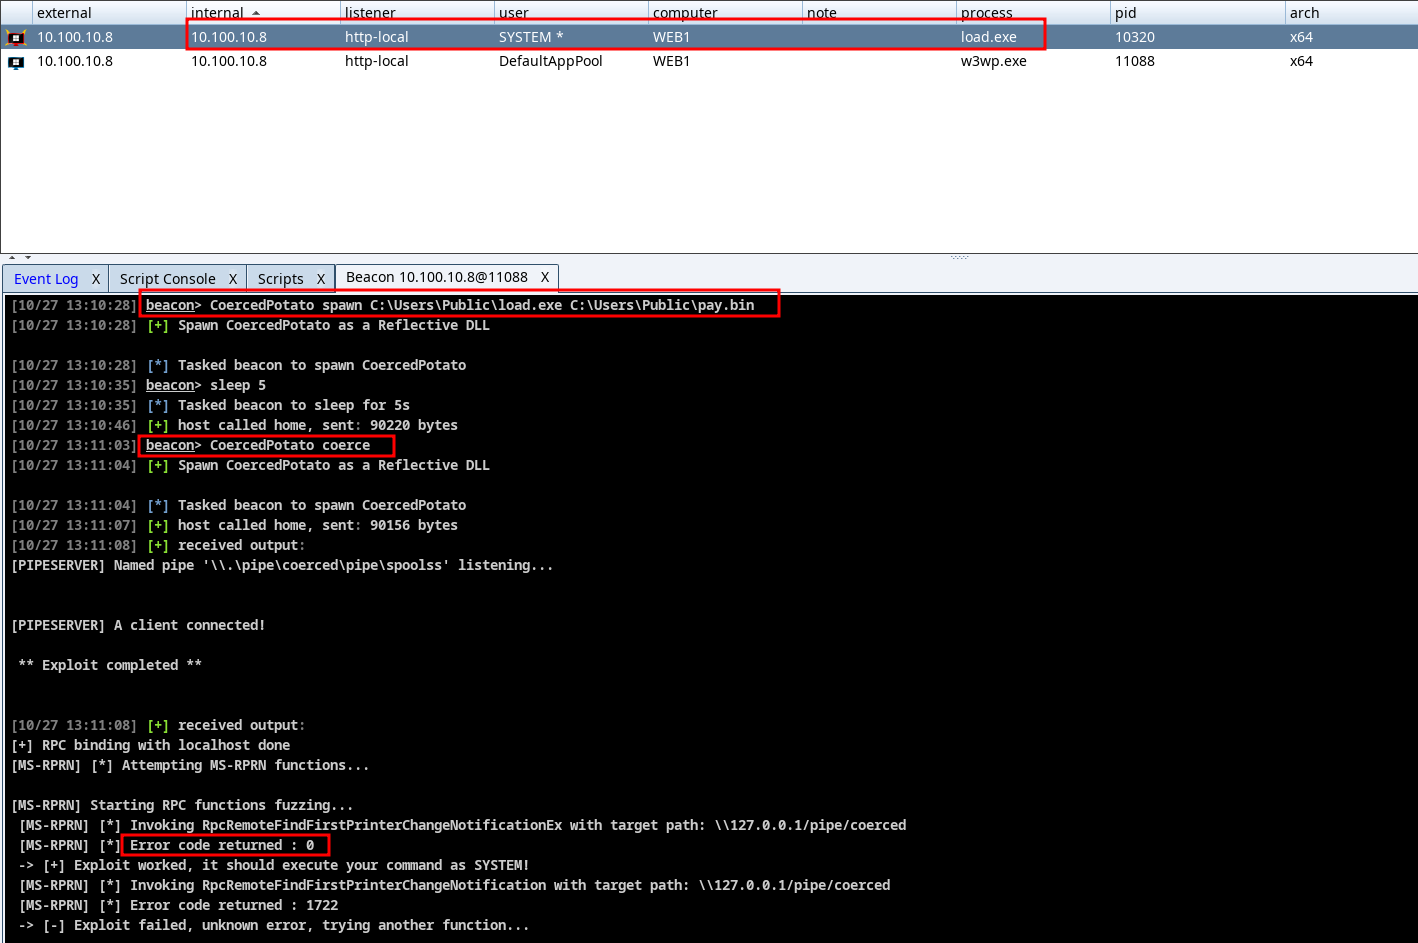
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege

exploitationpayload-developmentpenetration-testing+4
2272 years ago
Previous123…17Next