

Dirty-Vanity
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
adversarial-attackexploitationpayload-development+4
674
deepinstinct/dirty-vanityA POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
 0xb11a1/yetanotherobfuscator
C# obfuscator that bypass windows defender
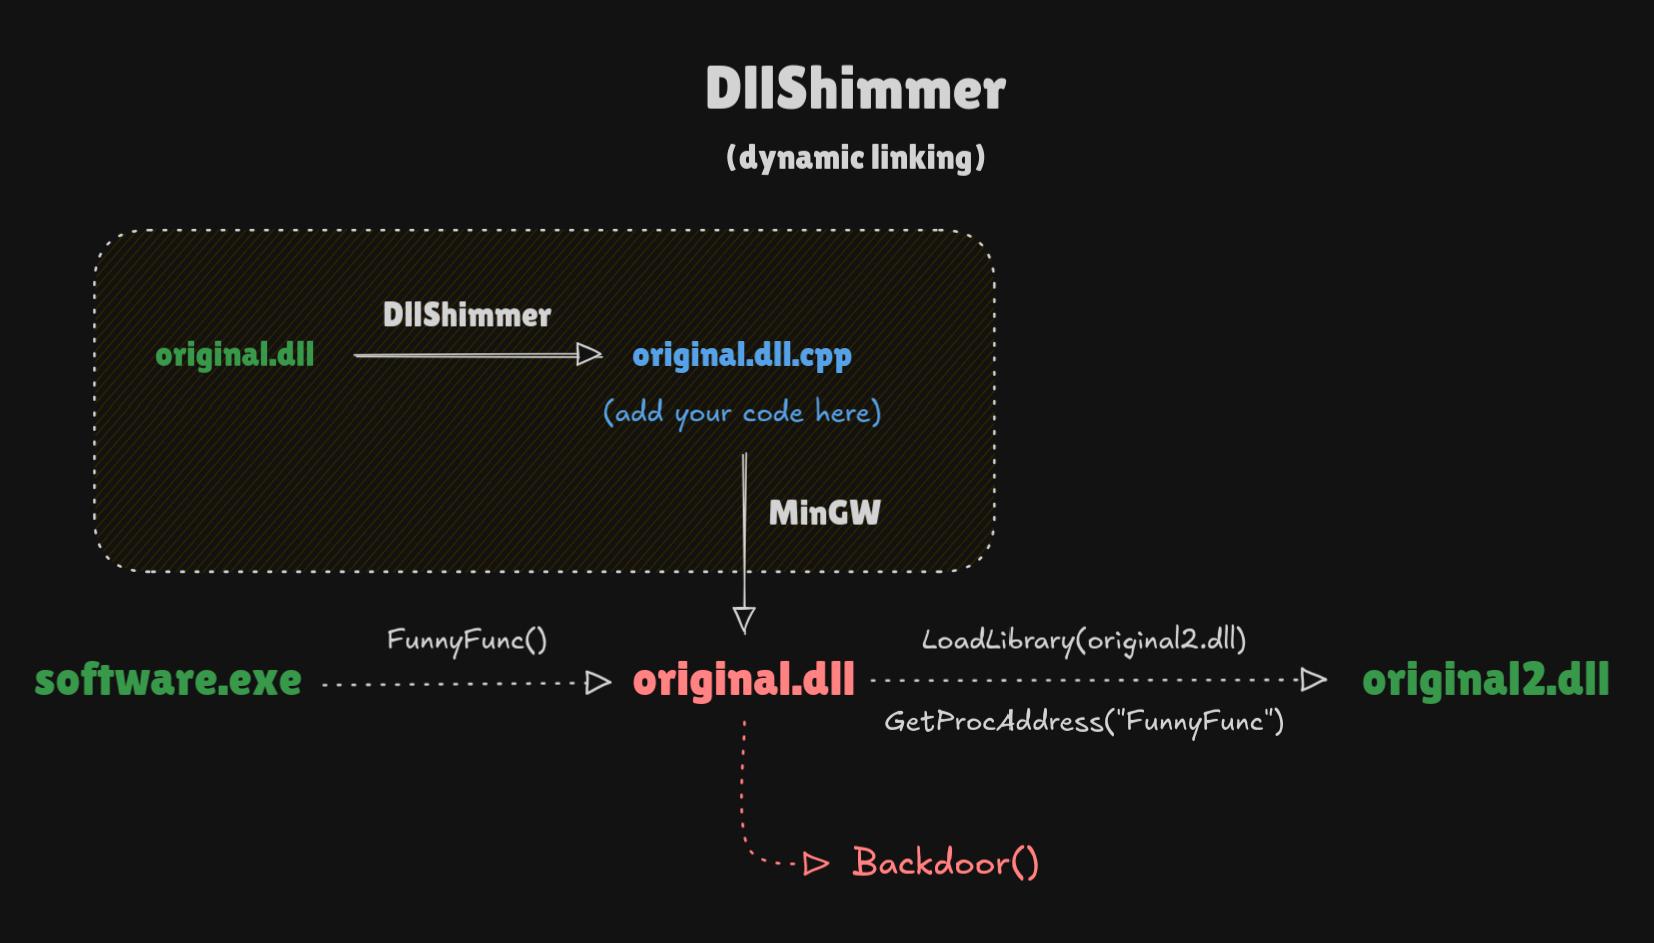 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
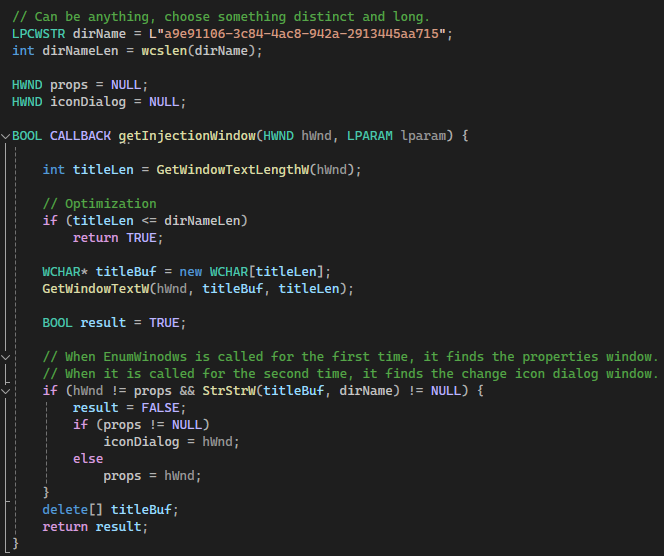 d419h/iconjector
Inject DLLs into the explorer process using icons
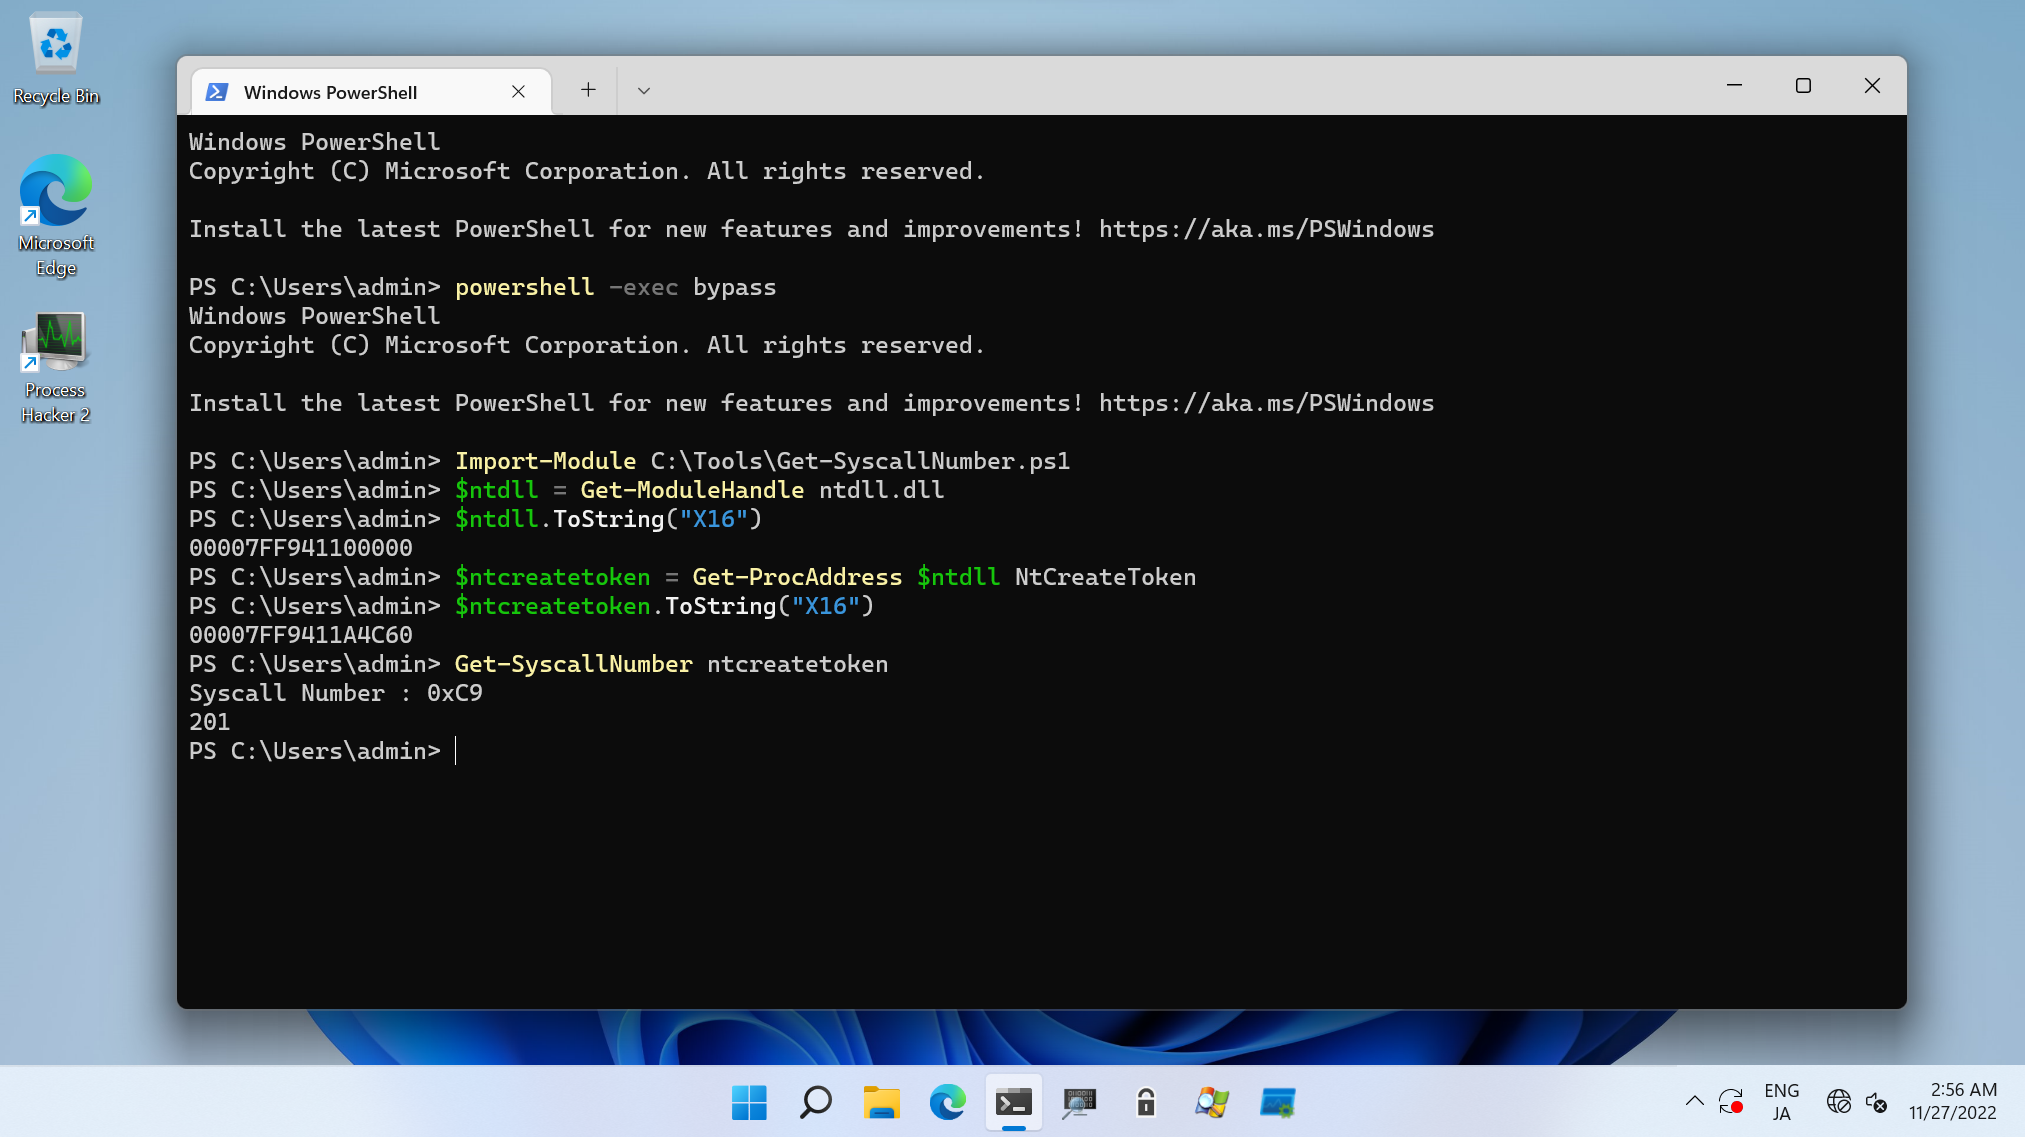 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
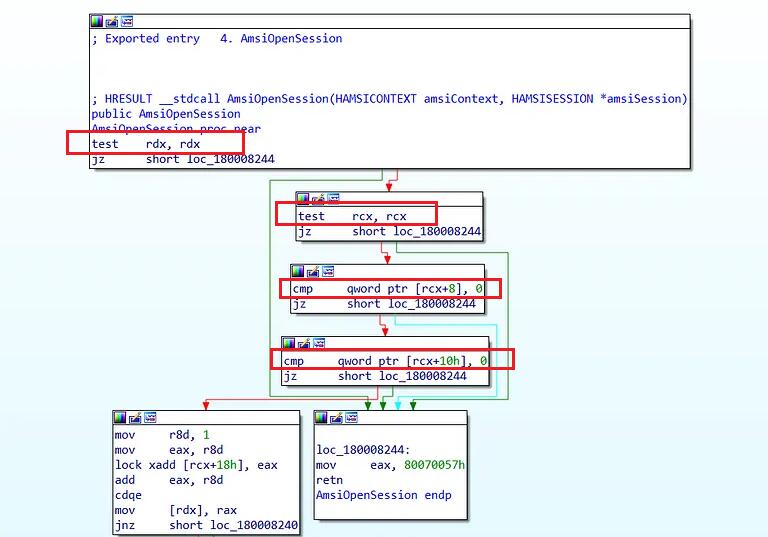 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 d00mfist/mystikal
macOS Initial Access Payload Generator
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
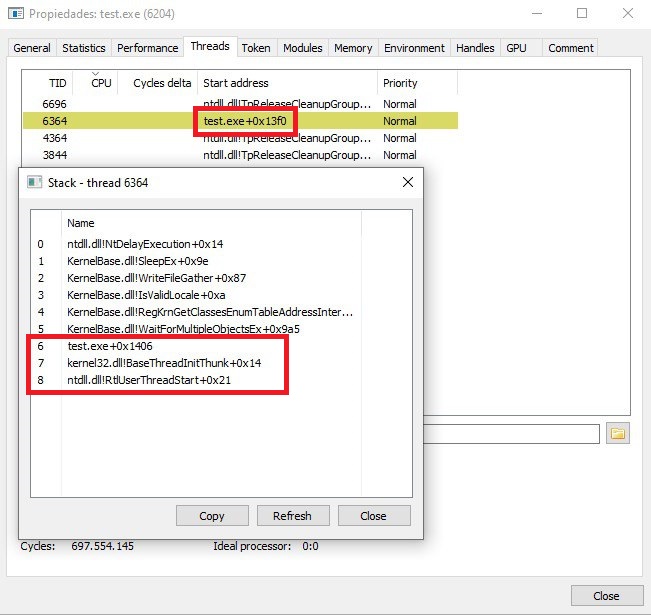 kudaes/unwinder
Call stack spoofing for Rust
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 xforcered/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 saadahla/heapcrypt
Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.