
ImgBackdoor
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
command-and-controlexploitationpayload-development+3
393
tsuyoken/imgbackdoorHide your payload into .jpg file
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 tennc/webshell
This is a webshell open source project
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 xiphosresearch/exploits
Miscellaneous exploit code
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
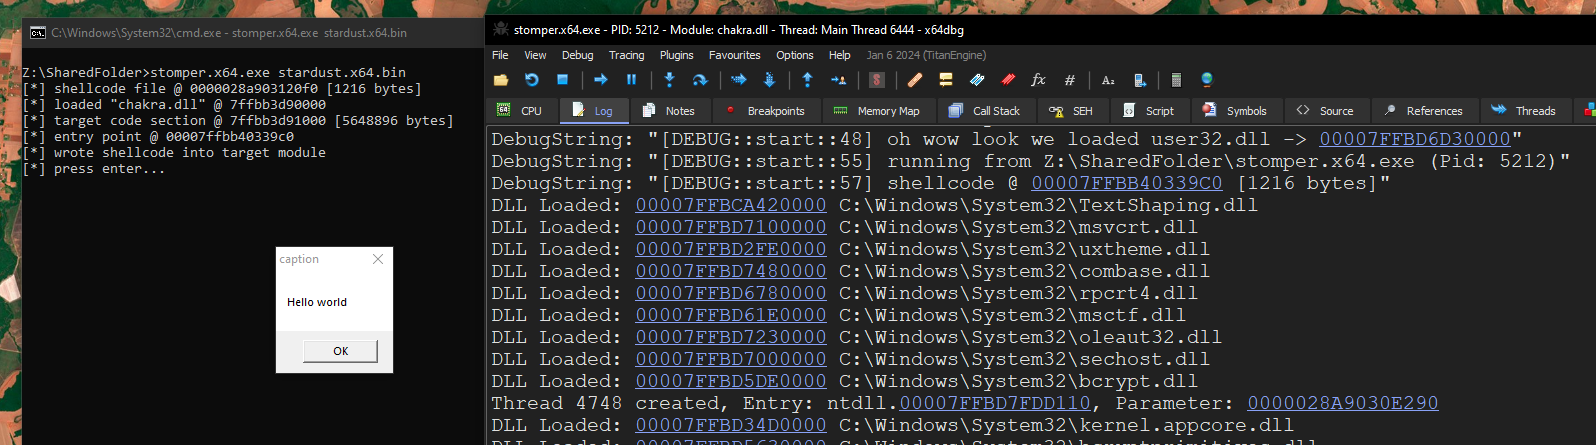 cracked5pider/stardust
A modern 32/64-bit position independent implant template
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 tylous/zipexec
A unique technique to execute binaries from a password protected zip
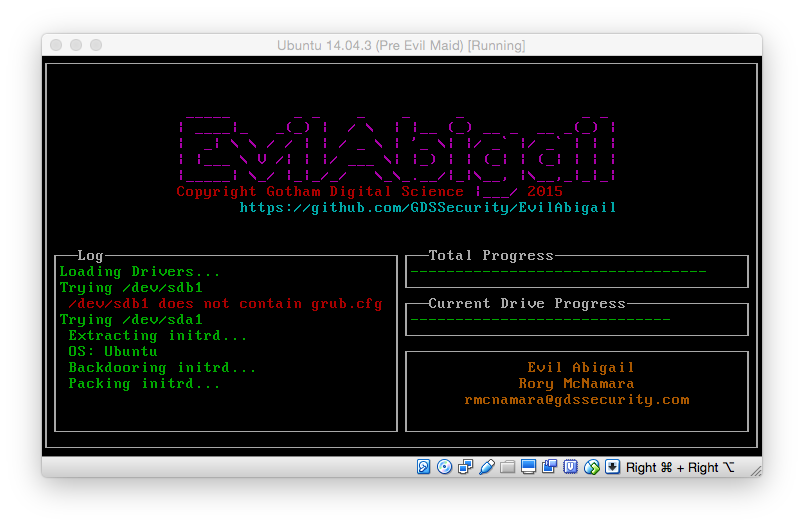 strozfriedberg/evilabigail
Automated Linux evil maid attack