
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
105 results
SysWhispers3 preview

SysWhispers3

GitHubklezvirus/syswhispers3

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

defensive-toolsexploitationids-ips-evasion+5
1.7k2 years ago
Invisi-Shell preview

Invisi-Shell

GitHubomerya/invisi-shell

Hide your Powershell script in plain sight. Bypass all Powershell security features
defensive-toolsexploitationids-ips-evasion+9
1.3k7 years ago
charlotte preview

charlotte

GitHub9emin1/charlotte

c++ fully undetected shellcode launcher ;)

anti-botexploitationids-ips-evasion+6
9755 years ago
FilelessPELoader preview

FilelessPELoader

GitHubsaadahla/filelesspeloader

Loading Remote AES Encrypted PE in memory , Decrypted it and run it
adversarial-attackids-ips-evasionpayload-development+3
1.0k3 years ago
Loki preview

Loki

GitHubboku7/loki

🧙‍♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
command-and-controlexploitationids-ips-evasion+5
1.4k6 months ago
HellHall preview

HellHall

GitHubmaldev-academy/hellhall

Performing Indirect Clean Syscalls
adversarial-attackids-ips-evasionpayload-development+1
6284 months ago
No-Consolation preview

No-Consolation

GitHubfortra/no-consolation

A BOF that runs unmanaged PEs inline
ids-ips-evasionpayload-developmentpenetration-testing-frameworks+2
7021 year ago
HWSyscalls preview

HWSyscalls

GitHubdec0ne/hwsyscalls

HWSyscalls is a new method to execute indirect syscalls using HWBP, HalosGate and a synthetic trampoline on kernel32 with HWBP.
ids-ips-evasionpayload-developmentpenetration-testing+2
7373 years ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
5985 years ago
Crystal-Kit preview

Crystal-Kit

GitHubrasta-mouse/crystal-kit

Evasion kit for Cobalt Strike
adversarial-attackcommand-and-controlids-ips-evasion+3
5074 months ago
Cronos preview

Cronos

GitHubidov31/cronos

PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.

cryptographyids-ips-evasionpayload-development+2
6283 years ago
DInvoke_rs preview

DInvoke_rs

GitHubkudaes/dinvoke_rs

Dynamically invoke arbitrary unmanaged code
binary-analysisids-ips-evasionpayload-development+3
3672 months ago
TamperingSyscalls preview

TamperingSyscalls

GitHubrad9800/tamperingsyscalls

C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
ids-ips-evasionpayload-developmentpost-exploitation+1
5074 years ago
CallstackSpoofingPOC preview

CallstackSpoofingPOC

GitHubpard0p/callstackspoofingpoc

C++ self-Injecting dropper based on various EDR evasion techniques.
adversarial-attackids-ips-evasionpayload-development+1
4452 years ago
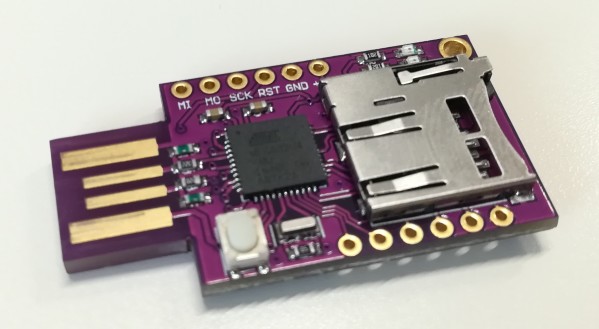
bad_ducky preview

bad_ducky

GitHubmharjac/bad_ducky

Rubber Ducky compatible clone based on CJMCU BadUSB HW.
hardware-hackingids-ips-evasionimpersonation-tools+5
3018 years ago
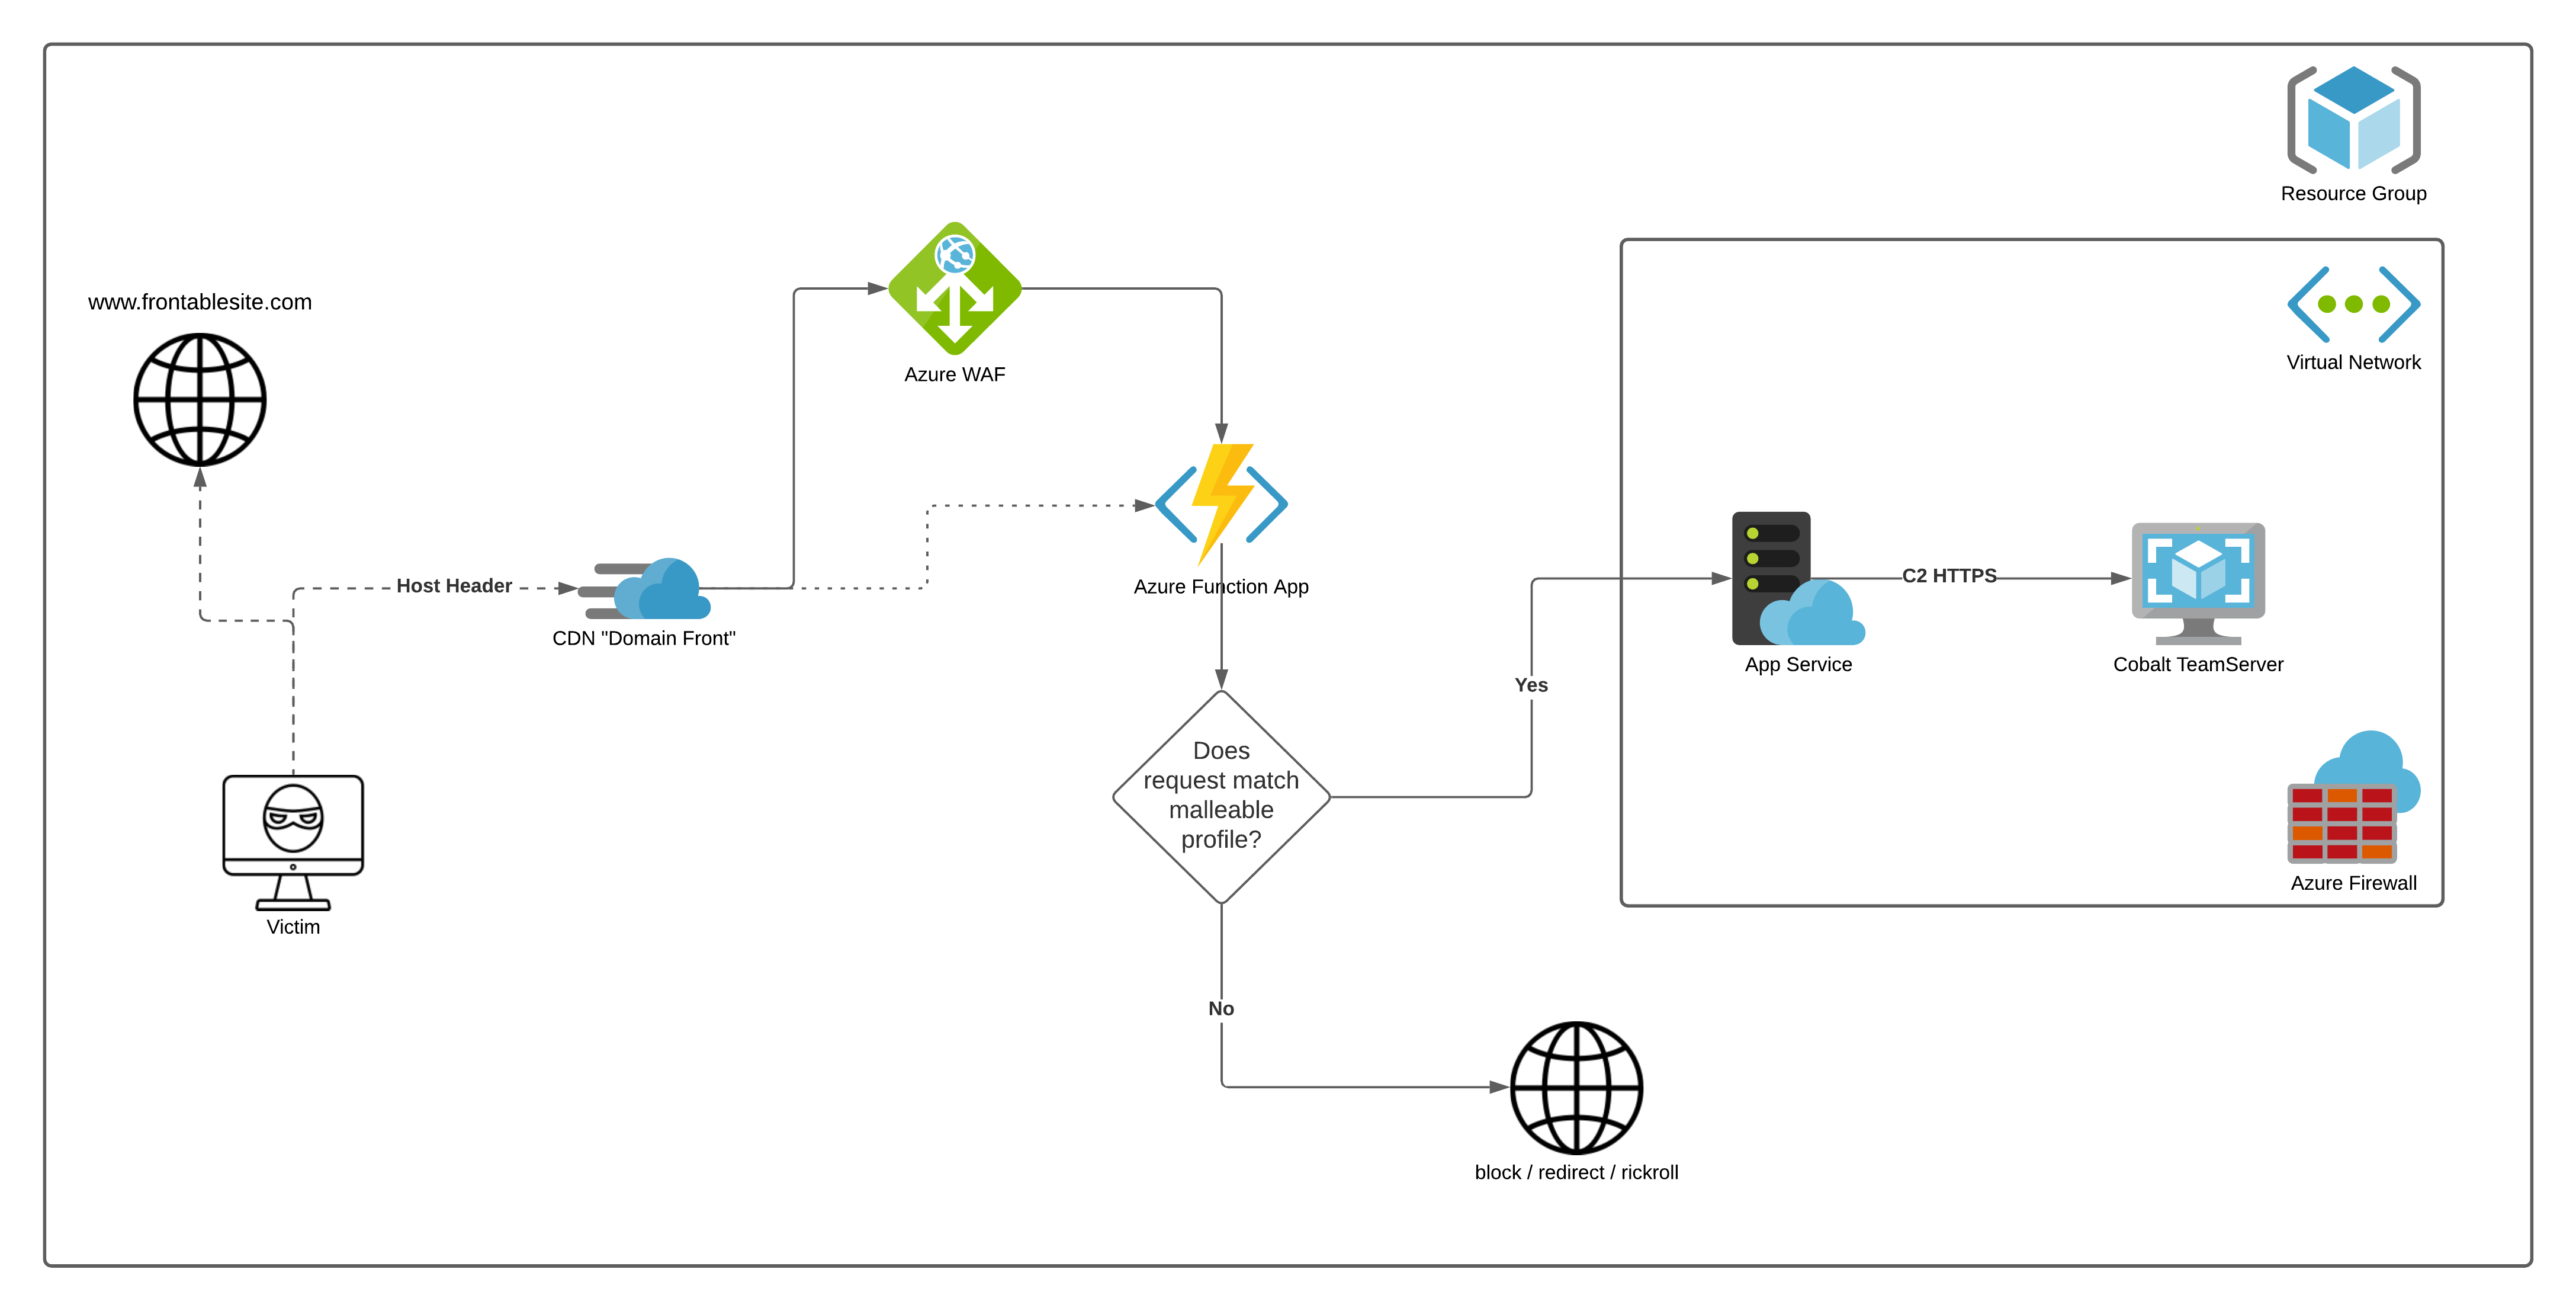
AzureC2Relay preview

AzureC2Relay

GitHubflangvik/azurec2relay

Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…

cloud-securitycommand-and-controlids-ips-evasion+2
2335 years ago
AtlasLdr preview

AtlasLdr

GitHubkrypteria/atlasldr

Reflective x64 PE/DLL Loader implemented using Dynamic Indirect Syscalls

ids-ips-evasionpayload-developmentpenetration-testing+2
3951 year ago
trojanizer preview

trojanizer

GitHubr00t-3xp10it/trojanizer

Trojanize your payload - WinRAR (SFX) automatization - under Linux distros

command-and-controlexploitationids-ips-evasion+6
2948 years ago
Previous123456Next