JavaUnserializeExploits

Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.

Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.

Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)

Python backdoor that uses http post/get requests to communicate

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…

Quicky serve files over http or https using flask.

Educational lab for understanding Java deserialization vulnerabilities with PoC exploits for JBoss CVEs, gadget chain analysis, and a vulnerable HTTP…

Python exploit for Oracle WebLogic CVE-2019-2725, enabling unauthenticated remote code execution via crafted HTTP requests to vulnerable servers.

Proof-of-concept exploit for CVE-2020-8515 targeting DrayTek routers with remote code execution via unauthenticated HTTP request.

Proof-of-concept exploit for CVE-2025-69219, demonstrating remote code execution in Apache Airflow Providers HTTP via unsafe pickle deserialization.…

Exploits unauthenticated RCE in Apache Gravitino < 1.2.1 via H2 JDBC INIT; hosts SQL/Java payloads, executes commands, and exfiltrates output over…

Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…

Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.

CVE-2026-44789 — n8n <1.123.43 HTTP Request pagination prototype pollution to RCE (NODE_OPTIONS runner-spawn gadget). Lab + automated PoC, verified…

Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…

Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)

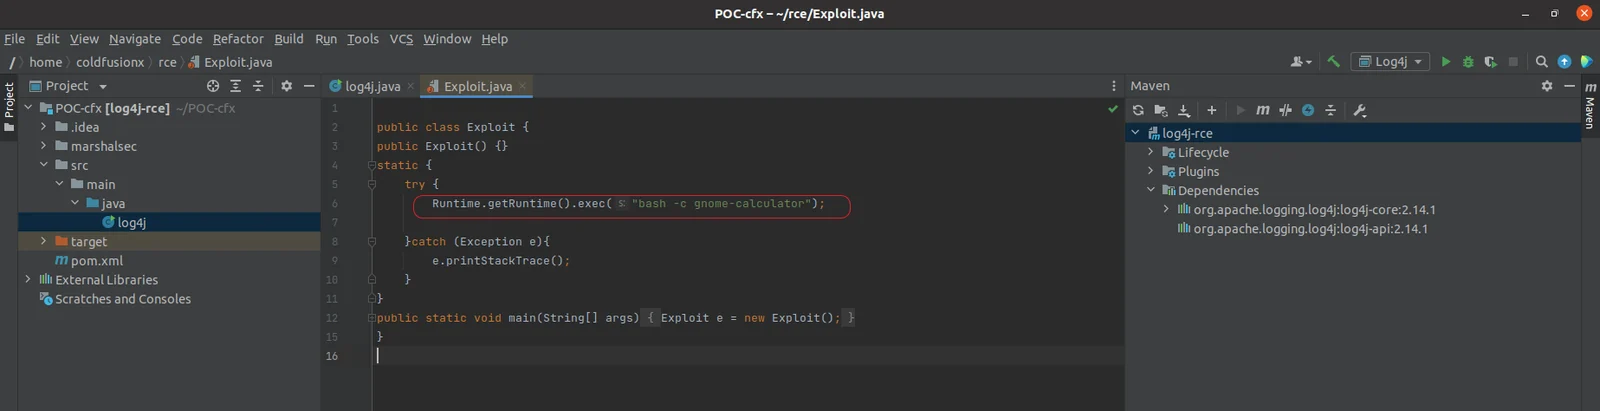
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating JNDI-based remote code execution via LDAP and HTTP servers.

Exploit for CVE-2022-22965 (Spring4Shell) enabling remote code execution on unpatched Spring Framework applications via crafted HTTP requests.

A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…