
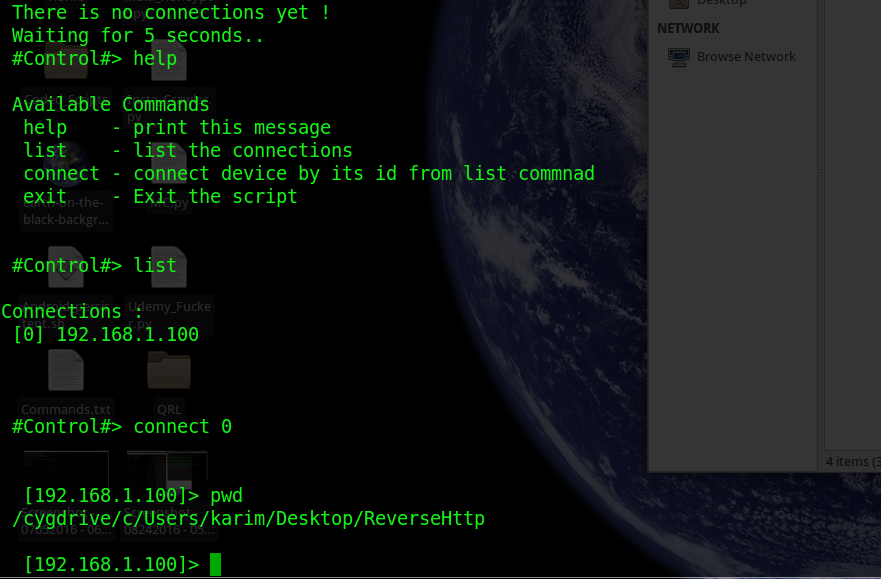
ReverseHttp
 d4vinci/reversehttp
Python backdoor that uses http post/get requests to communicate
command-and-controlpayload-developmentpenetration-testing+3
4210 years ago
d4vinci/reversehttpPython backdoor that uses http post/get requests to communicate
 byinarie/qu1ckdr0p2
Quicky serve files over http or https using flask.
 ianxtianxt/cve-2015-7501
Educational lab for understanding Java deserialization vulnerabilities with PoC exploits for JBoss CVEs, gadget chain analysis, and a vulnerable HTTP…
 lasensio/cve-2019-2725
Python exploit for Oracle WebLogic CVE-2019-2725, enabling unauthenticated remote code execution via crafted HTTP requests to vulnerable servers.
 imjdl/cve-2020-8515-poc
Proof-of-concept exploit for CVE-2020-8515 targeting DrayTek routers with remote code execution via unauthenticated HTTP request.
 boroeurnprach/ashwesker-cve-2026-21962
Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…
 sak110/cve-2025-69219
Proof-of-concept exploit for CVE-2025-69219, demonstrating remote code execution in Apache Airflow Providers HTTP via unsafe pickle deserialization.…
 ibonok/cve-2026-33439-poc
Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 lulztigre/cve-2026-41042
Exploits unauthenticated RCE in Apache Gravitino < 1.2.1 via H2 JDBC INIT; hosts SQL/Java payloads, executes commands, and exfiltrates output over…
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 mahajian/cve-2024-10793
Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…
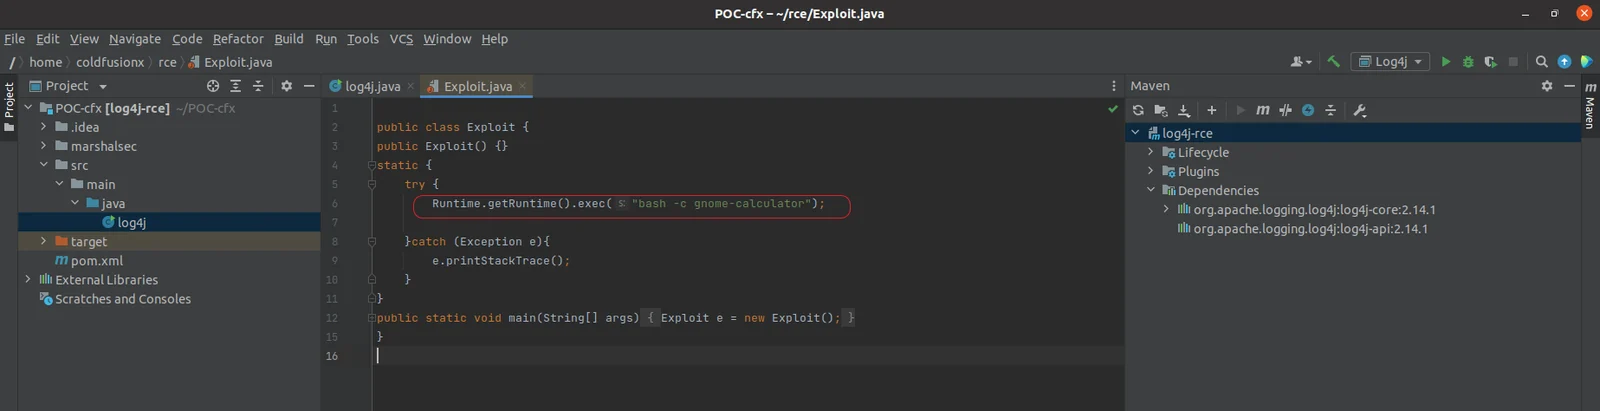 coldfusionx/cve-2021-44228-log4shell-poc
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating JNDI-based remote code execution via LDAP and HTTP servers.
 george1-adel/cve-2026-41940_exploit
Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…
 iveresk/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager. Injects SSH keys via…
 biitts/cve-2026-44789-n8n-prototypepollution-rce
CVE-2026-44789 — n8n <1.123.43 HTTP Request pagination prototype pollution to RCE (NODE_OPTIONS runner-spawn gadget). Lab + automated PoC, verified…
 jeanback1/cve-2019-0211-exploit
Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…