
CrossC2Kit
 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
command-and-controlexploit-frameworksinformation-gathering+7
229
crossc2/crossc2kitCrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations
 hosch3n/proxyvulns
[ProxyLogon] CVE-2021-26855 & CVE-2021-27065 Fixed RawIdentity Bug Exploit. [ProxyOracle] CVE-2021-31195 & CVE-2021-31196 Exploit Chains.…
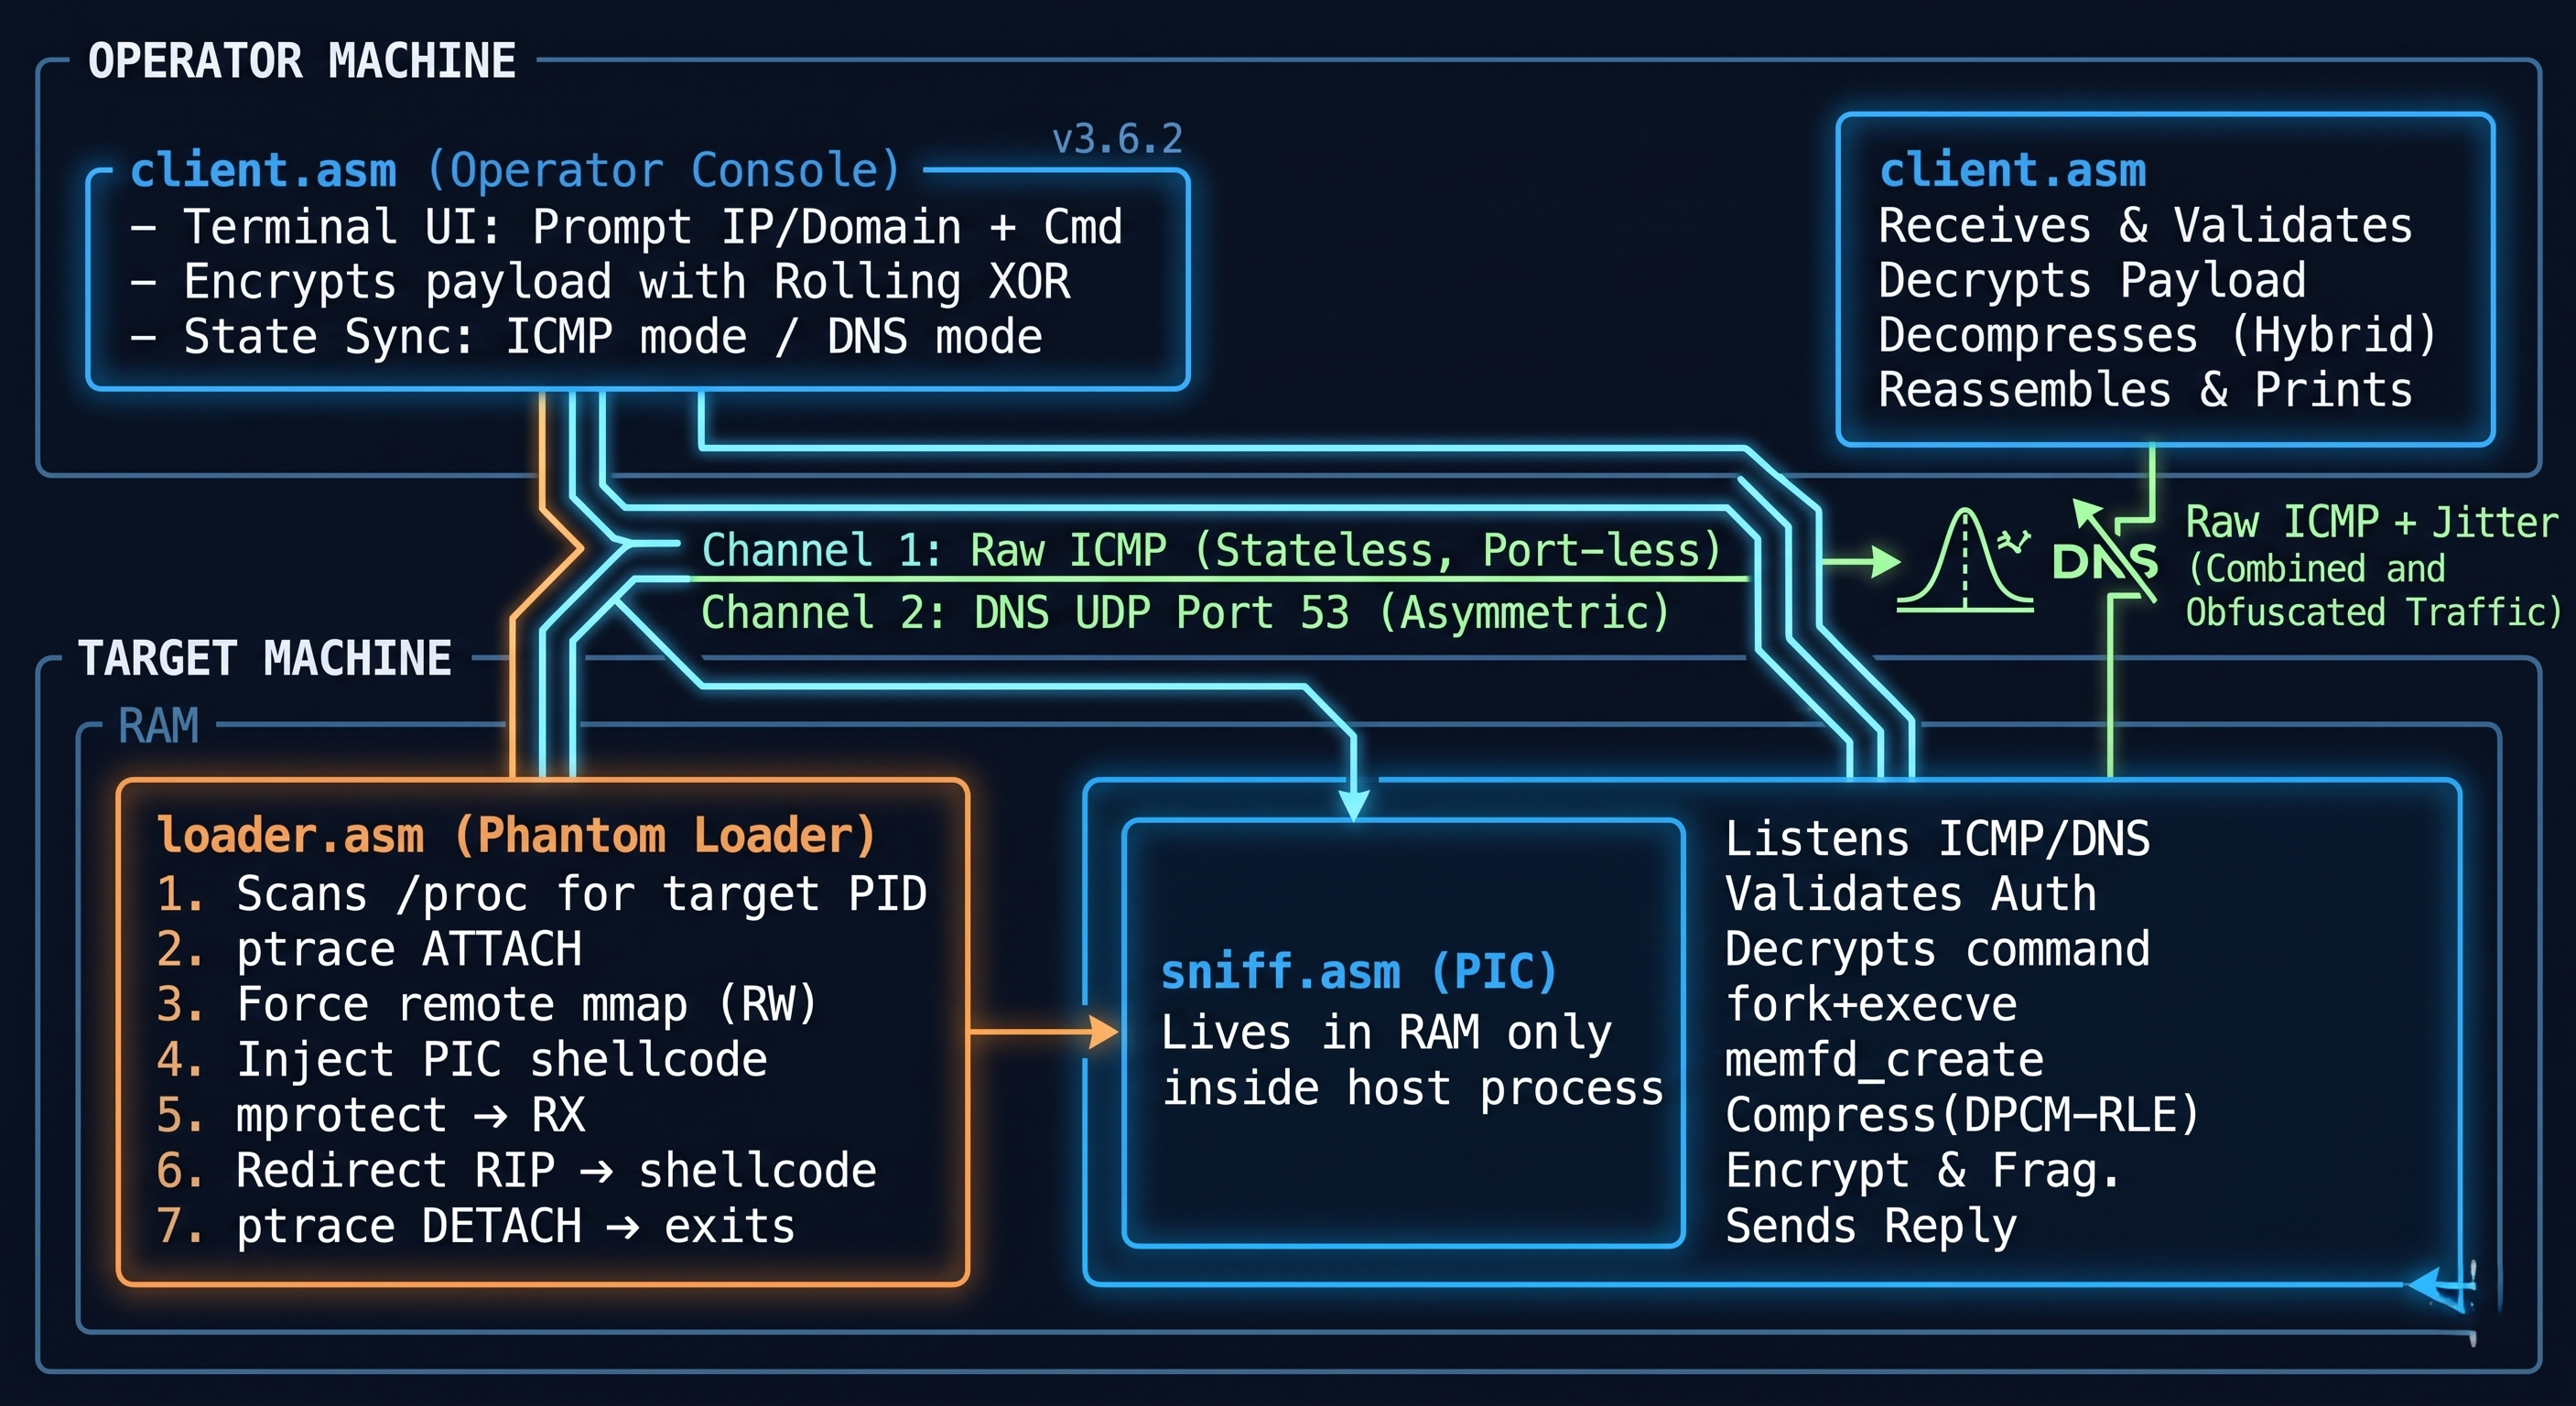 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 hktalent/cve_2020_2546
CVE-2020-2546,CVE-2020-2915 CVE-2020-2801 CVE-2020-2798 CVE-2020-2883 CVE-2020-2884 CVE-2020-2950 WebLogic T3 payload exploit poc python3,
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)

 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 taroballzchen/cve-2021-21972
CVE-2021-21972 Unauthorized RCE in VMware vCenter metasploit exploit script
 wqsemc/cve-2019-0708
initial exploit for CVE-2019-0708, BlueKeep CVE-2019-0708 BlueKeep RDP Remote Windows Kernel Use After Free The RDP termdd.sys driver improperly…
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
 0dayninja/cve-2021-24155.rb
WordPress Backup Guard Authenticated Remote Code Execution Exploit
 securifera/cve-2015-2900-exploit
Proof-of-concept exploit and Metasploit module for CVE-2015-2900 targeting the MEDCIN Engine (medcinserv.exe) versions prior to 2.22.20142.166.
 taroballzchen/proxylogon-cve-2021-26855-metasploit
CVE-2021-26855 proxyLogon metasploit exploit script