
CVE-2026-41940
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
authenticationcommand-and-controlexploitation+6
5
jenderal92/cve-2026-41940Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 speatx/react2shell-cve-2025-55182
CVE-2025-55182 — Unauthenticated RCE in React Server Components (React2Shell). CVSS 10.0 exploit tool for authorized penetration testing.
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
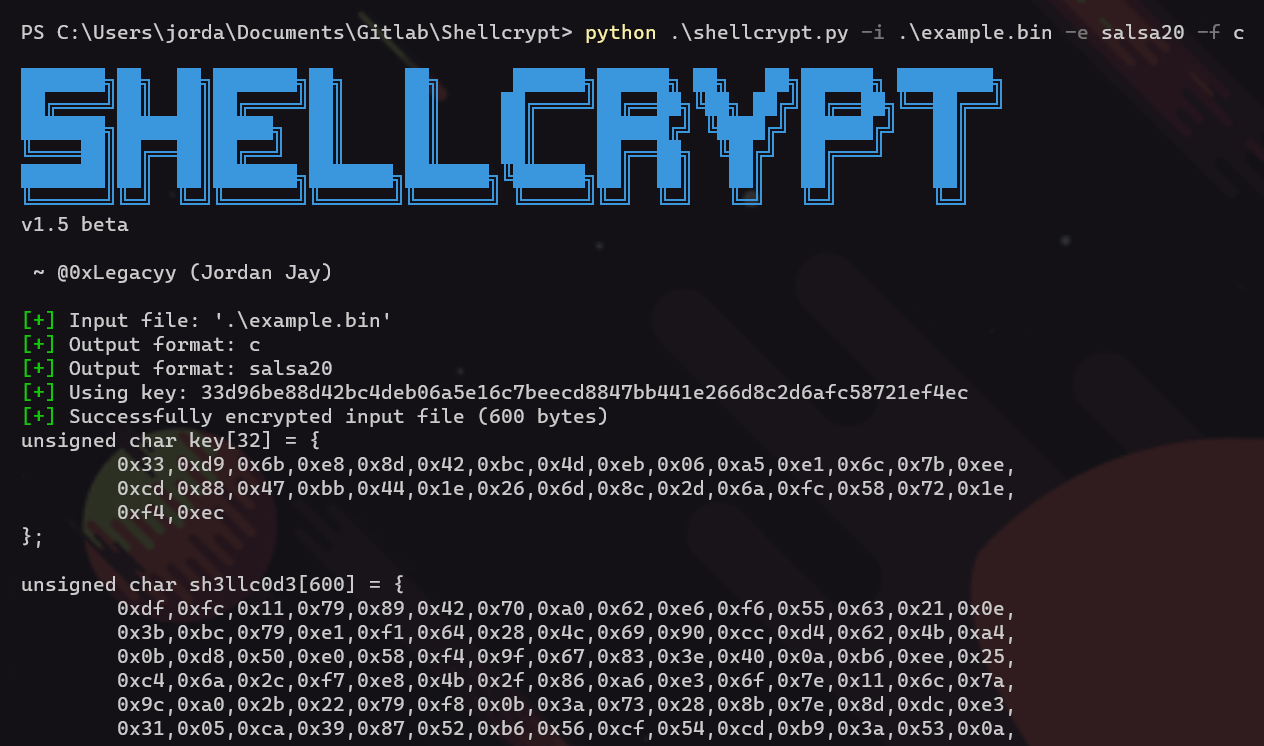 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 m4sc3r4n0/avoidz
Avoidz tool to bypass most A.V softwares
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template
 tw1sm/badger-builder
badger-builder is an AI-assisted tool for generating dynamic Brute Ratel C4 profiles
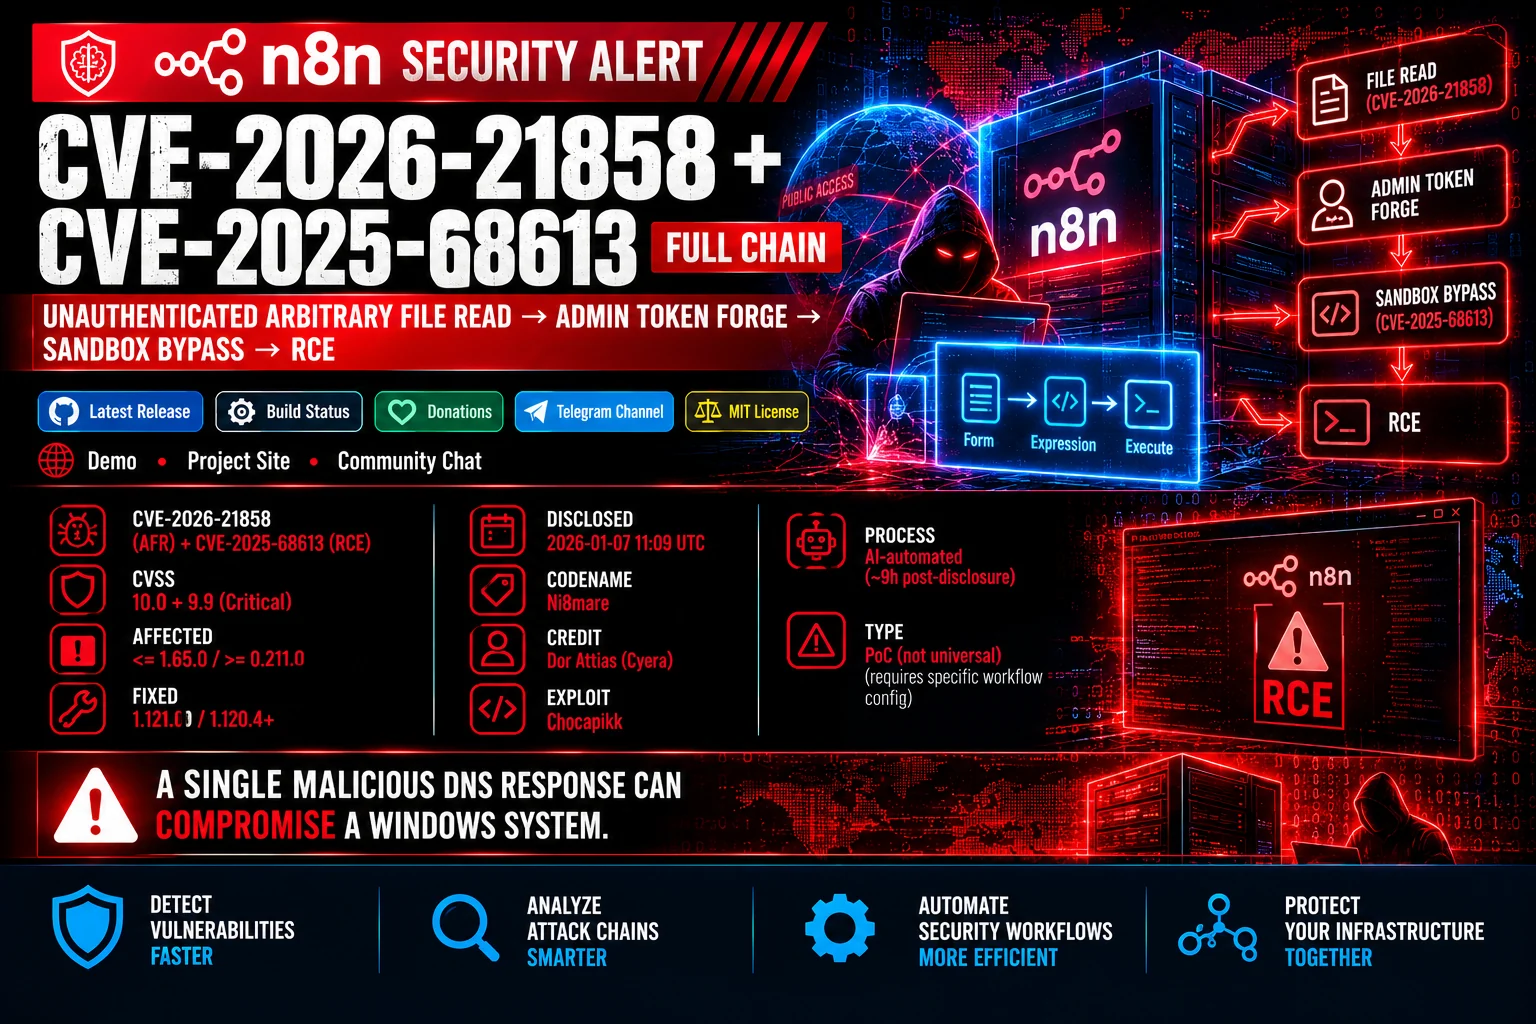 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 lasensio/cve-2019-2725
Python exploit for Oracle WebLogic CVE-2019-2725, enabling unauthenticated remote code execution via crafted HTTP requests to vulnerable servers.
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 ivanitlearning/cve-2017-17562
Standalone Python 3 exploit for CVE-2017-17562 targeting GoAhead web server 2.5–3.6.5 with automated CGI endpoint discovery and reverse shell payload…
 cerberusmrxi/cve-2026-23744-mcpjam-exploit
A proof-of-concept exploit for CVE-2026-23744 - MCPJam Inspector Remote Code Execution (RCE) vulnerability. This tool demonstrates the security flaw…
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 george1-adel/cve-2026-41940_exploit
Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…