
CVE-2024-2667-Poc
 nxploited/cve-2024-2667-poc
PoC exploit for CVE-2024-2667: automated arbitrary file upload and shell access via insufficient file validation in InstaWP Connect WordPress plugin…
exploitationpayload-developmentpenetration-testing+3
nxploited/cve-2024-2667-pocPoC exploit for CVE-2024-2667: automated arbitrary file upload and shell access via insufficient file validation in InstaWP Connect WordPress plugin…
 mesudmammad1/cve-2023-26326_buddyform_exploit
Python exploit for CVE-2023-26326 (WordPress BuddyForms) chained with CVE-2024-2961 to achieve unauthenticated remote code execution via php://filter…
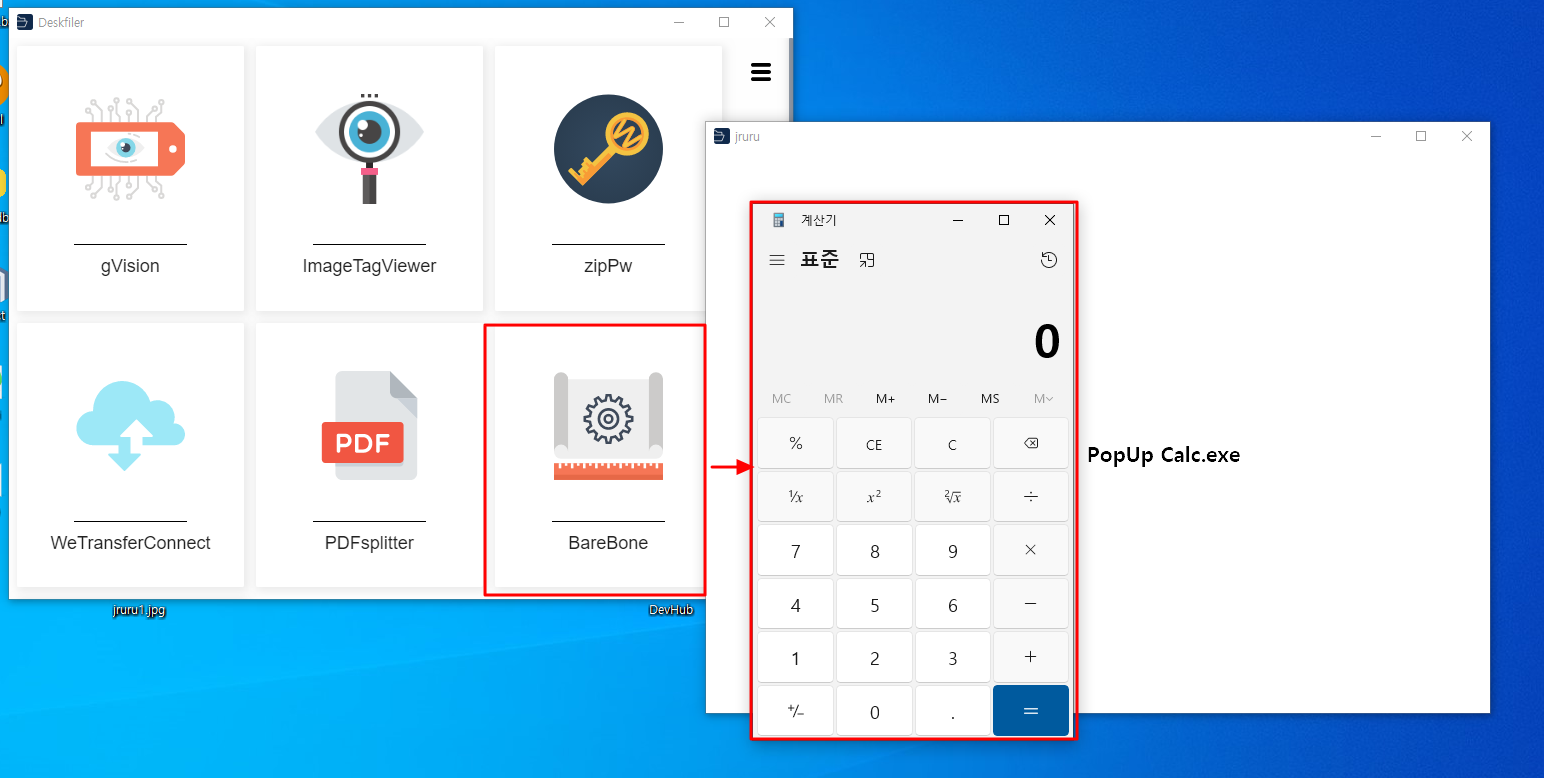 eqstlab/cve-2024-25291
deskfiler 1.2.3 Open Redirect exploit
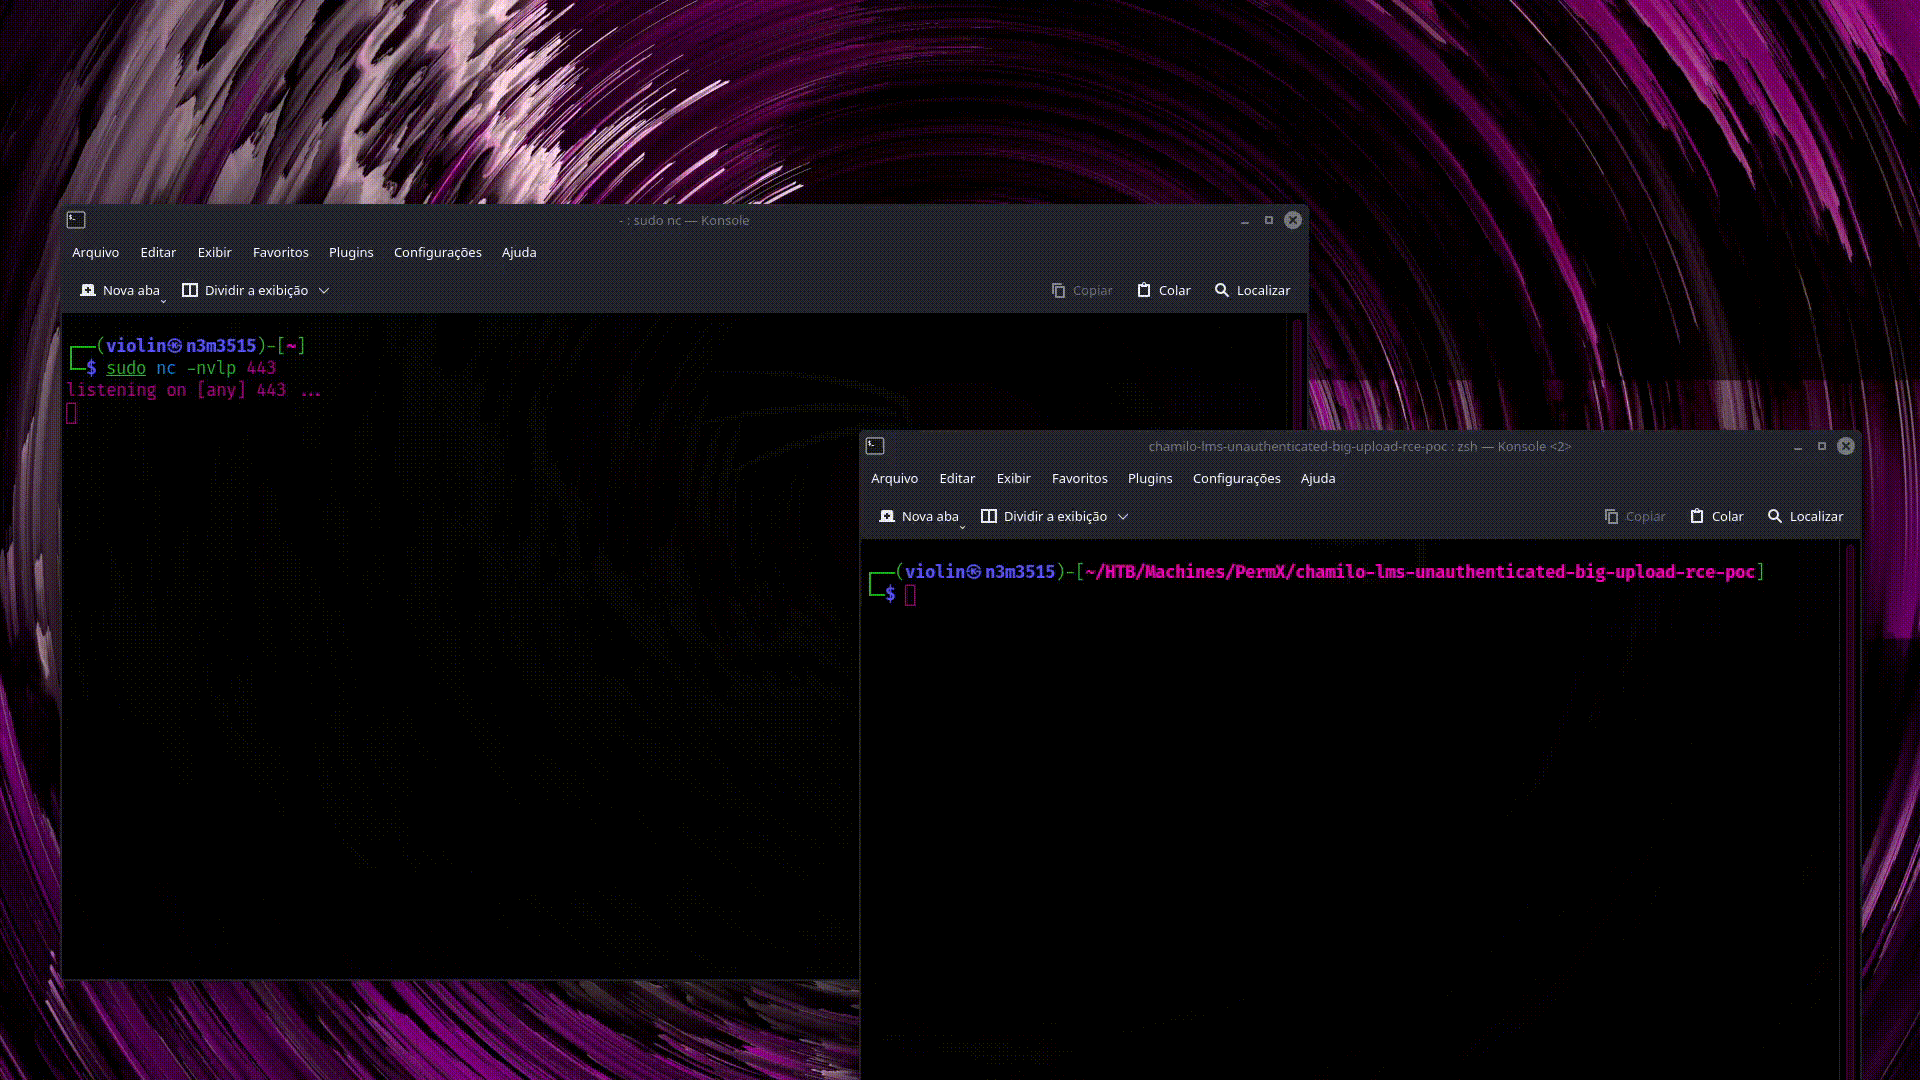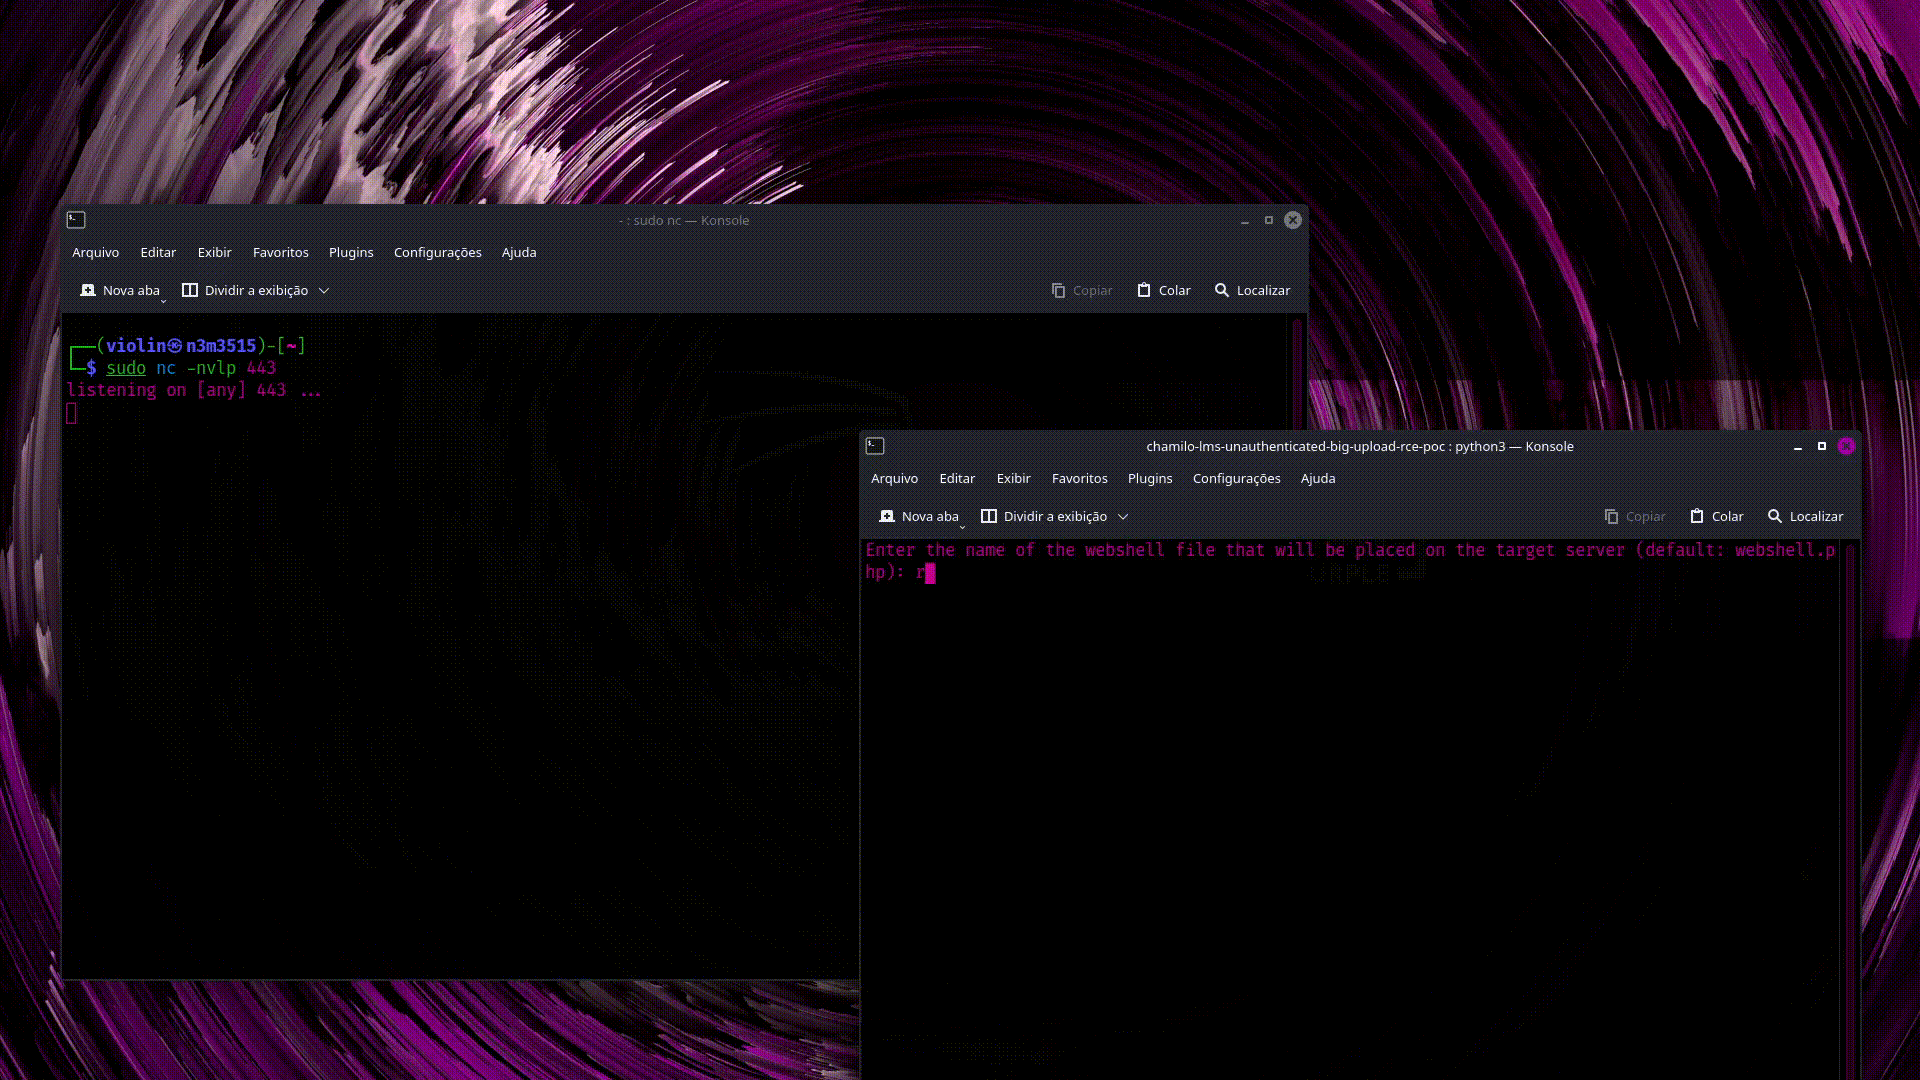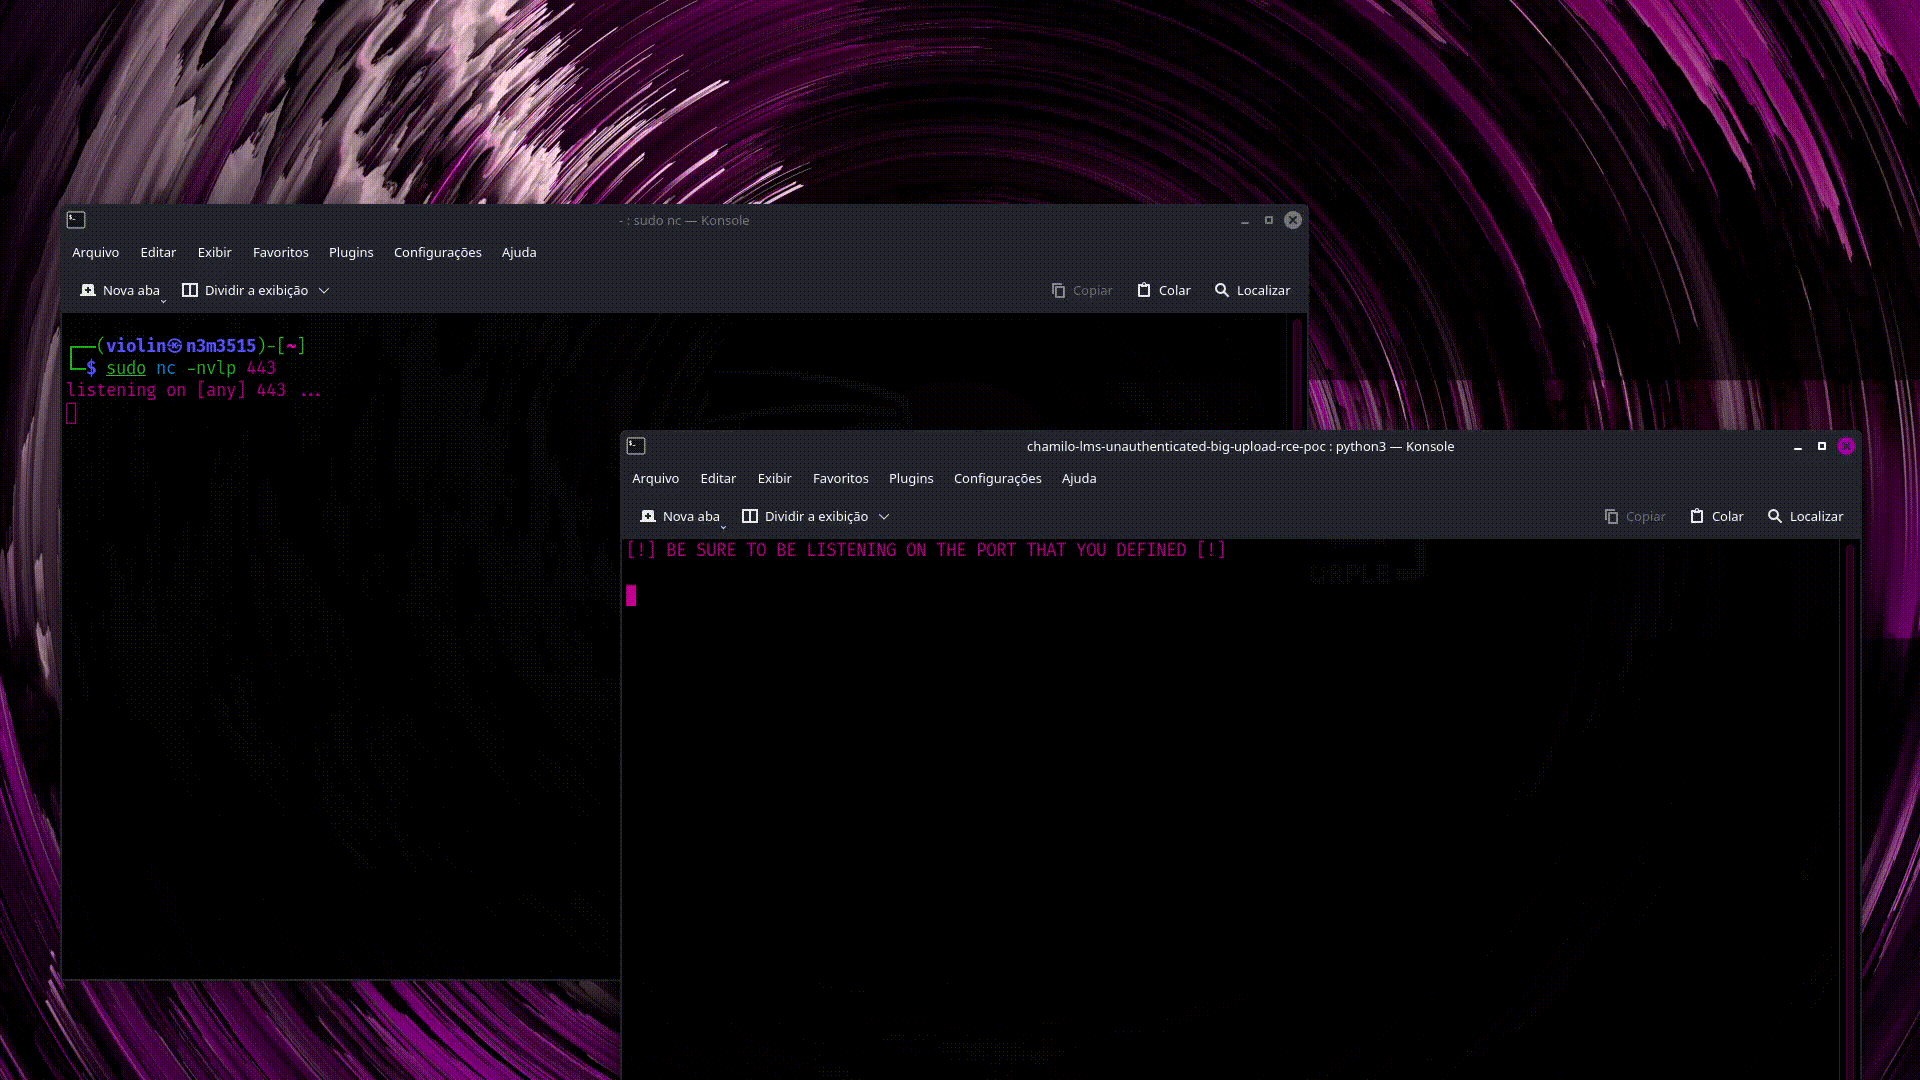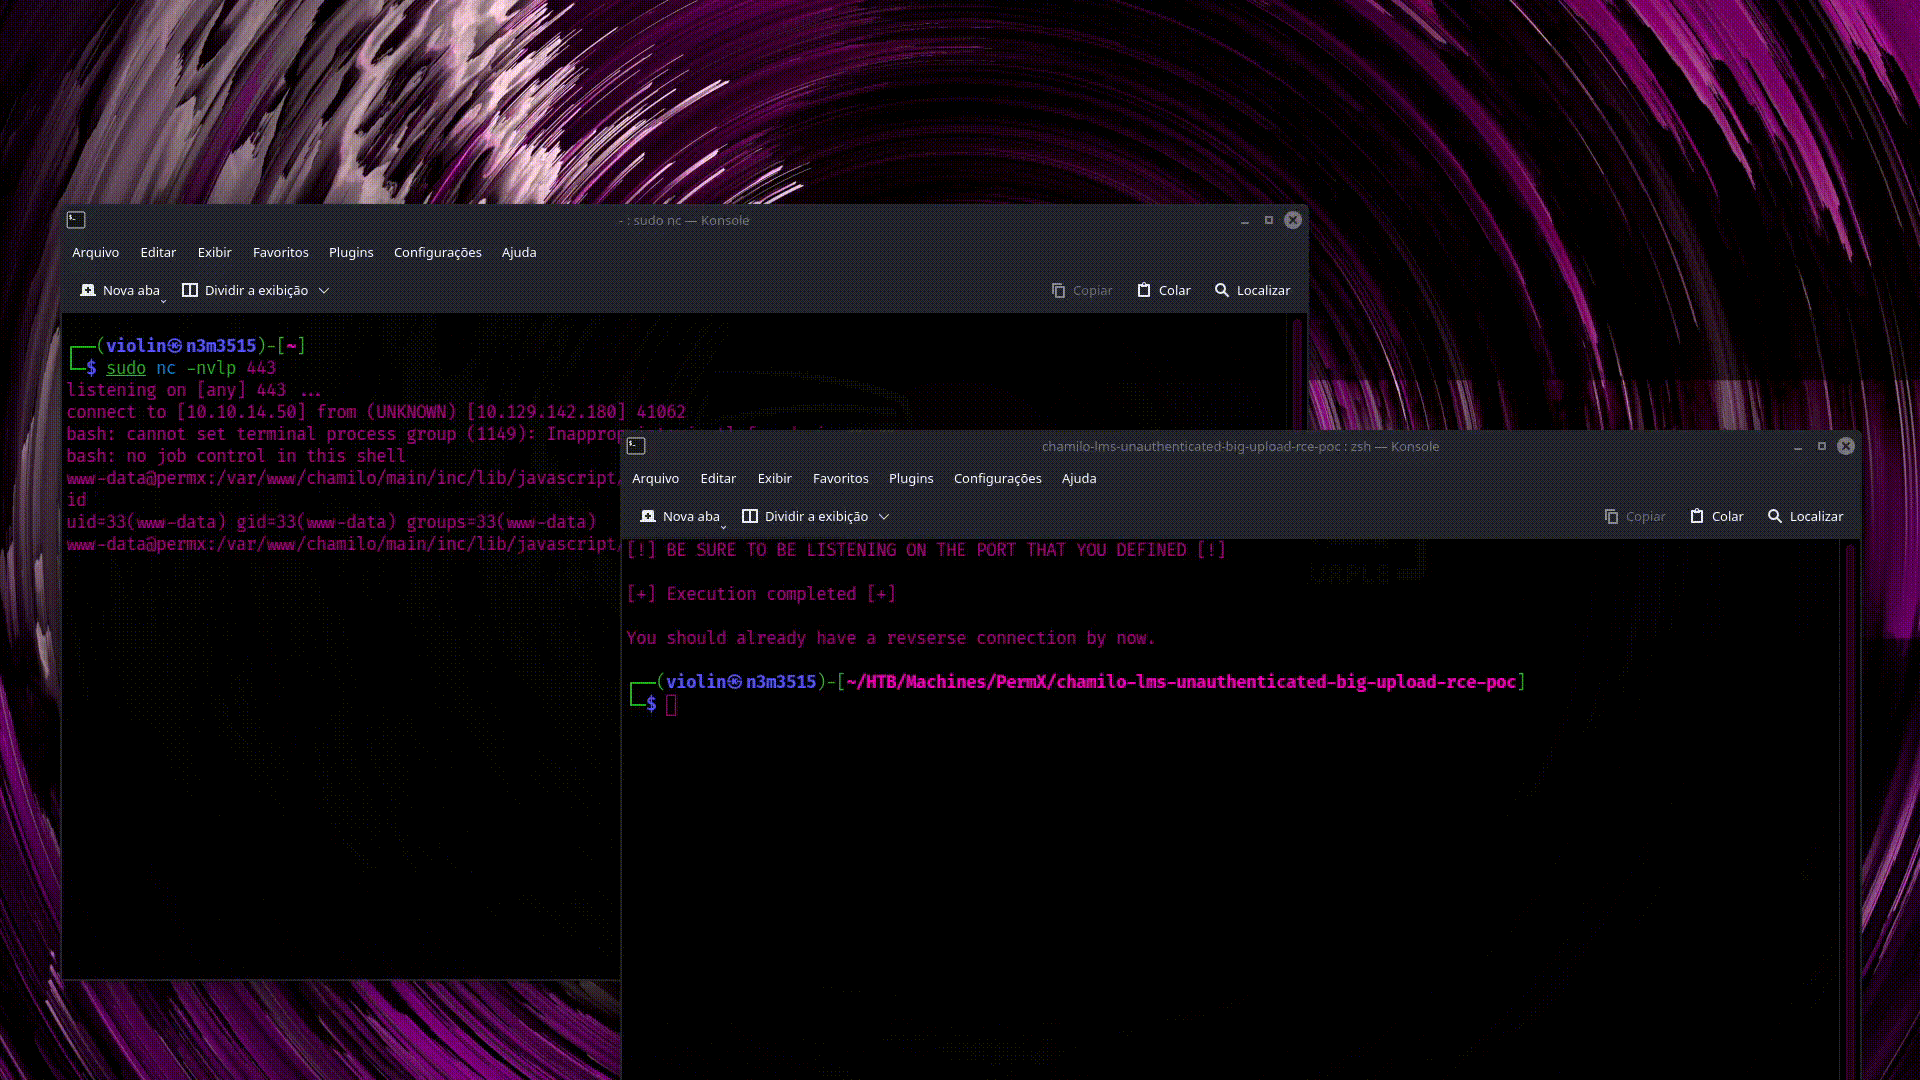 m3m0o/chamilo-lms-unauthenticated-big-upload-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 lolameroo/codiad-cve-2018-14009
Codiad through 2.8.4 allows Remote Code Execution, a different vulnerability than CVE-2017-11366 and CVE-2017-15689
 symbolexe/cve-2023-23397
CVE-2023-23397: Remote Code Execution Vulnerability in Microsoft Outlook
 improvecybersecurityjaro/2022_poc-msdt-follina-cve-2022-30190
Proof of Concept zu MSDT-Follina - CVE-2022-30190. ÜBERPRÜFUNG DER WIRKSAMKEIT VON MICROSOFT DEFNEDER IN DER JEWEILS AKTUELLSTEN WINDOWS 10 VERSION.
 nitzanoligo/cve-2023-46604-demo
 paradox0909/cve-2022-30333_online_rar_extracor
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…
 hhesenjan/cve-2023-27163-and-mailtrail-v0.53
Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.
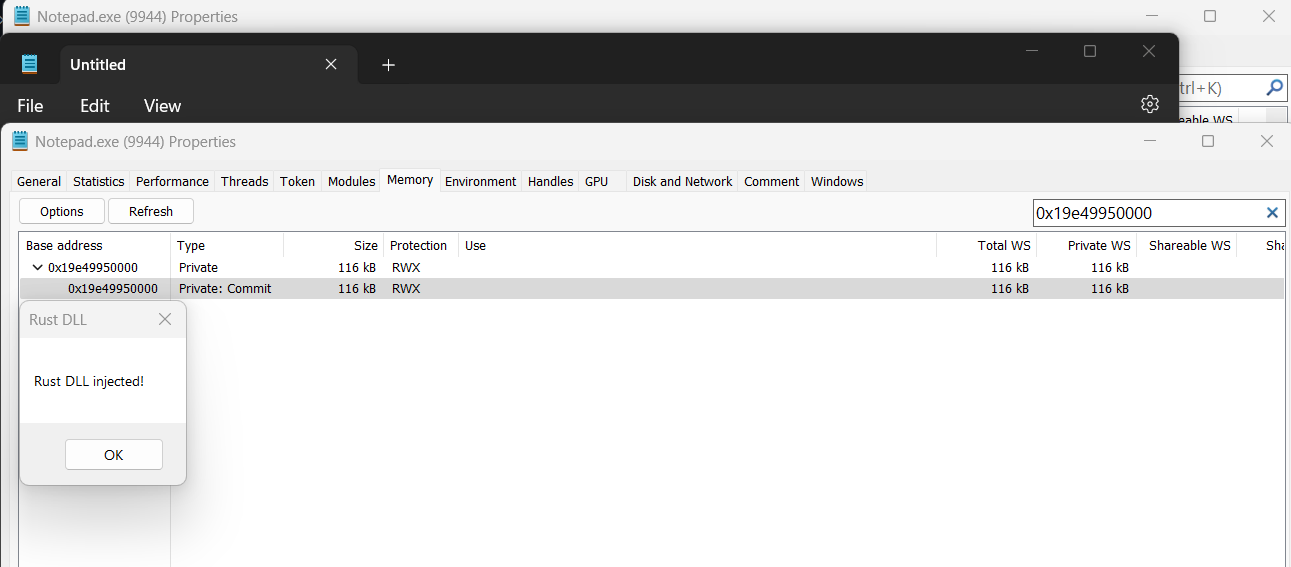 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
 tazmidev/cve-2026-36239
CVE-2026-36239 | Authenticated RCE in PbootCMS ≤3.2.12
