
CVE-2021-1675-PrintNightmare
 oppressionbreedsresistance/cve-2021-1675-printnightmare
Working PowerShell POC
exploitationpayload-developmentpenetration-testing+2
1
oppressionbreedsresistance/cve-2021-1675-printnightmareWorking PowerShell POC
 aljazceru/cve-2017-5638-apache-struts2
Tweaking original PoC (https://github.com/rapid7/metasploit-framework/issues/8064) to work on self-signed certificates
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…
 ly1g3/mailcow-cve-2022-31138
Proof-of-concept exploit for Mailcow CVE-2022-31138 enabling RCE via perl code injection in Sync Job regex fields, with privilege escalation to…
 nxploited/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 cyb3rfr0g/cve-2024-48990-poc
My take on the needrestart Python CVE-2024-48990
 whoami-chmod777/zerologon-attack-cve-2020-1472-poc
Python exploit for CVE-2020-1472 (Zerologon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…
 joeymeech/cve-2022-0847-exploit-implementation
Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.
 trailer2/corsair---dll-planting-cve-2023-38822
DLL Planting in the Corsair iCUE v.5.3.102 CVE-2023-38822
 mbadanoiu/jvmtiagentload-exploit
Tools and code for generating a malicious JAR to exploit jvmtiAgentLoad
 oledouxet/cve-2023-29324_patch_deploy
 kaanaryoverflow/ipfire-2-25-auth-rce
ipfire 2.25 authenticated remote code execution
 morton-li/copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation, with x86_64, AArch64, and C payloads to obtain root on affected…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 boompig/cve-2016-6662
Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.
 al1ex/powershell-c2
Powershell-C2
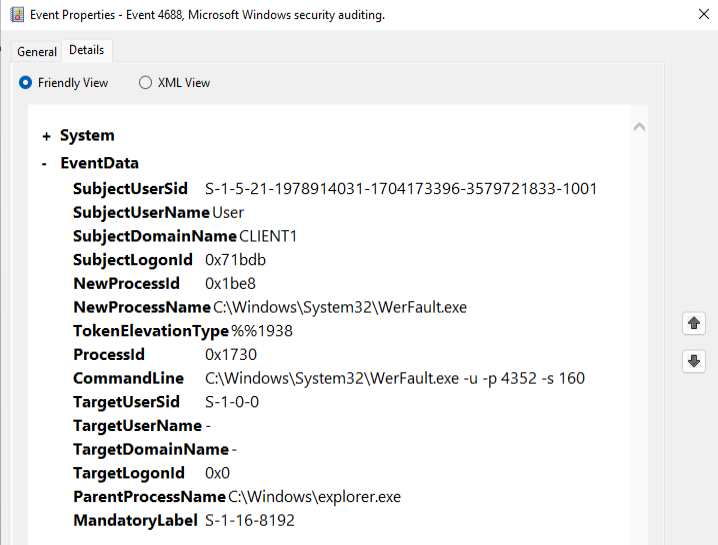 gmh5225/cs-dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 homjxi0e/cve-2017-8625_bypass_umci
Proof-of-concept exploit demonstrating UMCI bypass in Internet Explorer using JScript and ActiveX to execute arbitrary binaries, targeting Windows…