
dicerosbicornis
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
16
maldevel/dicerosbicornisA fully featured Windows backdoor that uses email as a C&C server
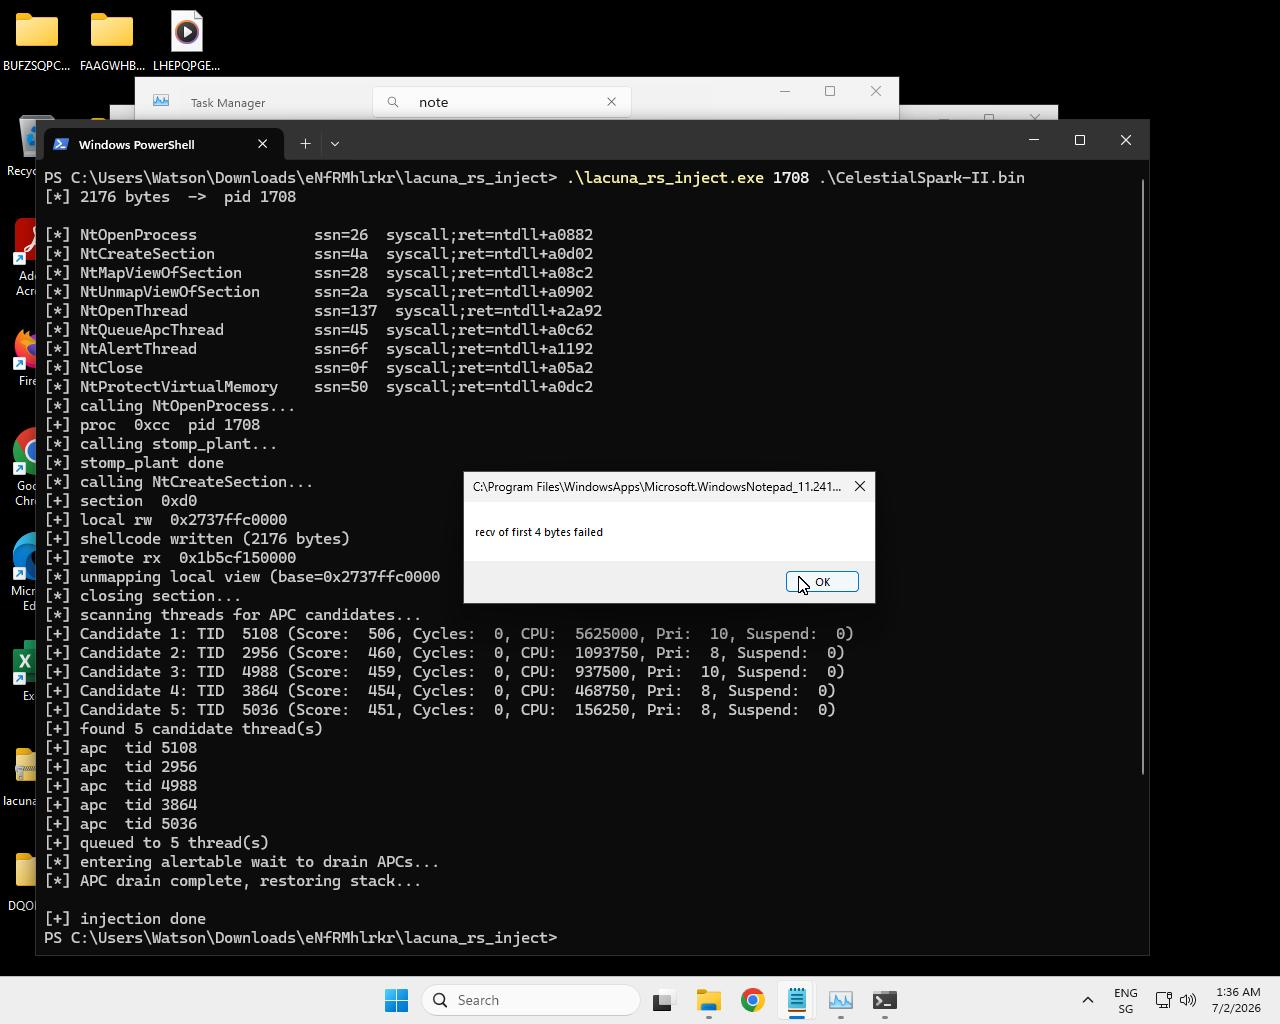 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 ntkernel0/cve-2019-0708
收集网上CVE-2018-0708的poc和exp(目前没有找到exp)
 flyinbedxyz/cve-2021-1732
Local privilege escalation exploit for CVE-2021-1732 targeting Windows 10 and Server versions, with PoC code and affected system enumeration.
 nweks/bluekeep-metasploit-lab-project
Exploiting Bluekeep (CVE-2019-0708) on windows 7 using metasploit (Esucational lab)
 emmadej1234/bluekeep-metasploit-lab-project
Exploiting BlueKeep (CVE-2019-0708) on Windows 7 using Metasploit
 atici/imagemagick-cve-2022-44268-poc
A bash script for easyly exploiting ImageMagick Arbitrary File Read Vulnerability CVE-2022-44268
 bsec404/cve-2020-0796
Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) to check remote overflow vulnerability in SMBv3.
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 marshall-hallenbeck/cve_2025_68413-4
Disclosure and PoCs for CVE-2025-68413 and CVE-2025-68414
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 spiralbl0ck/sigint_through_brother_printers
Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.
 june-in-exile/cve-2021-26700
Educational RCE exploit for CVE-2021-26700 in VS Code npm extension, demonstrating DNS tunneling to a Caldera C2 server via malicious package.json…