
Pentest-tools
 al1ex/pentest-tools
Intranet penetration tools
exploitationinformation-gatheringlateral-movement+8
al1ex/pentest-toolsIntranet penetration tools
 redcode-labs/coldfire
Golang malware development library
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository

 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
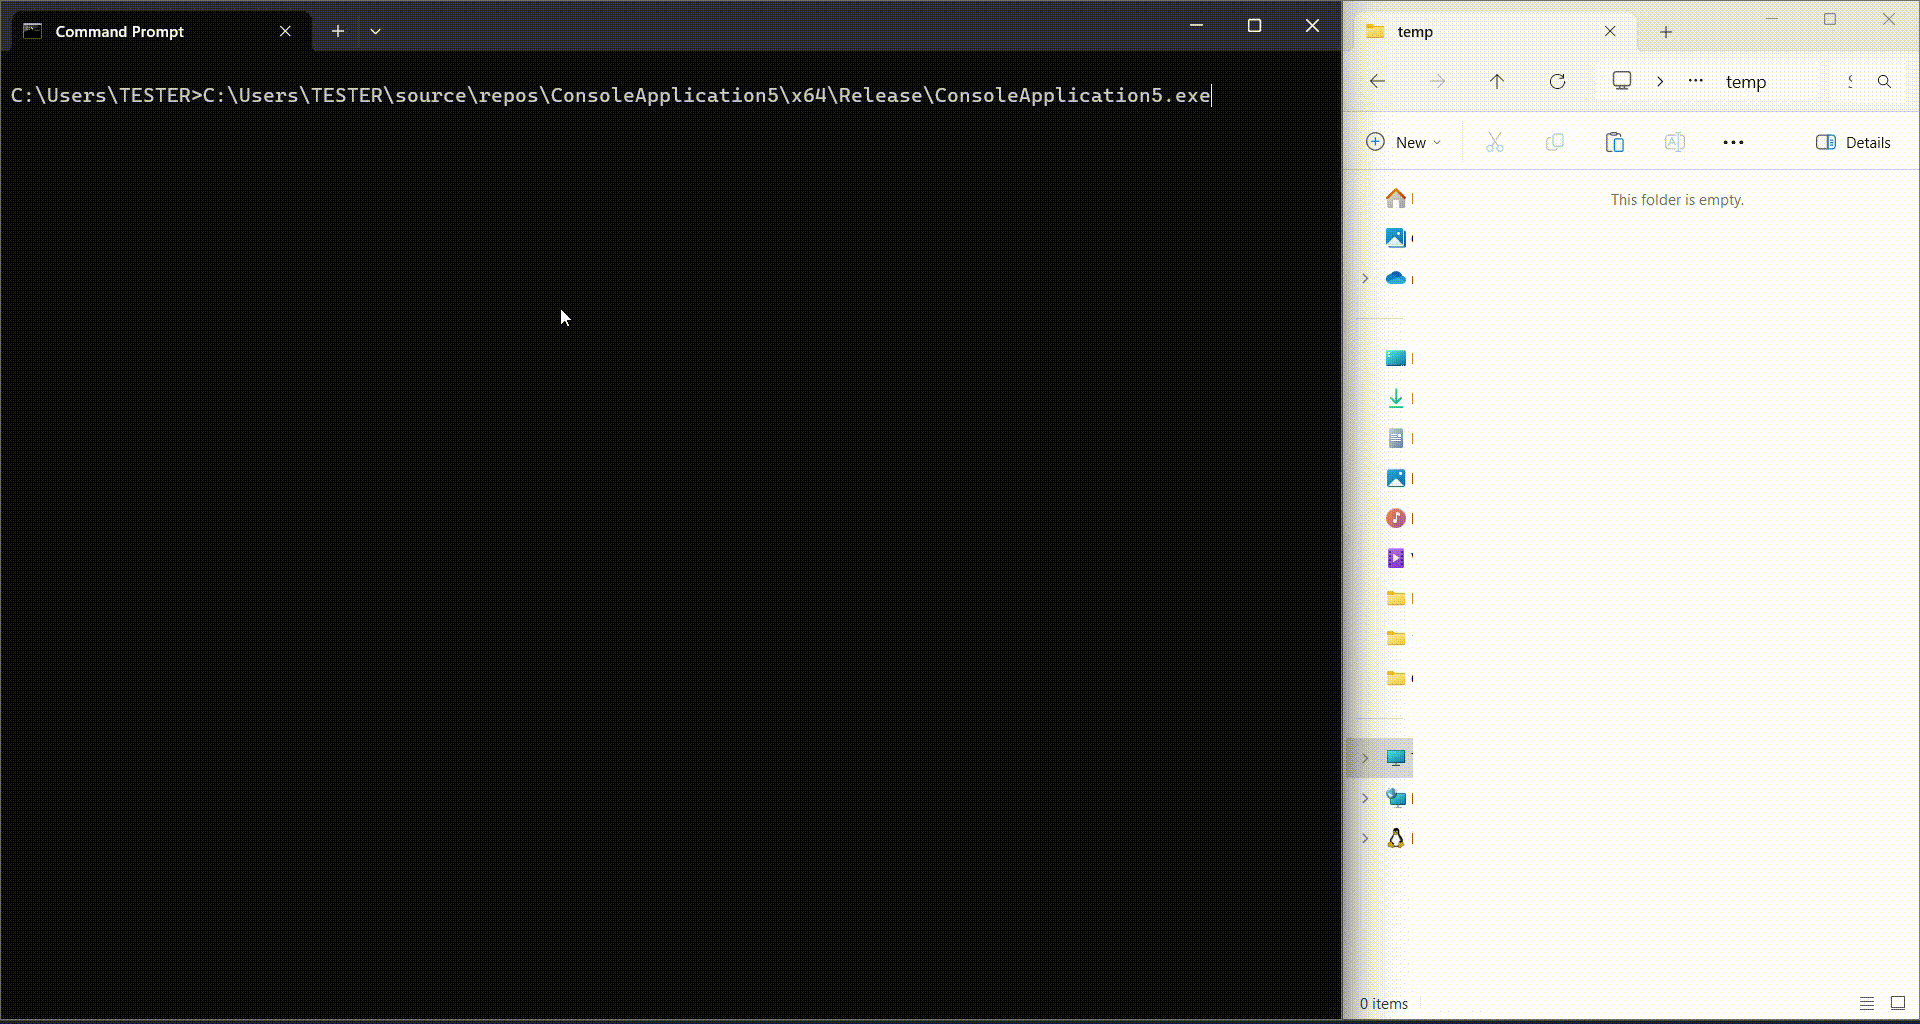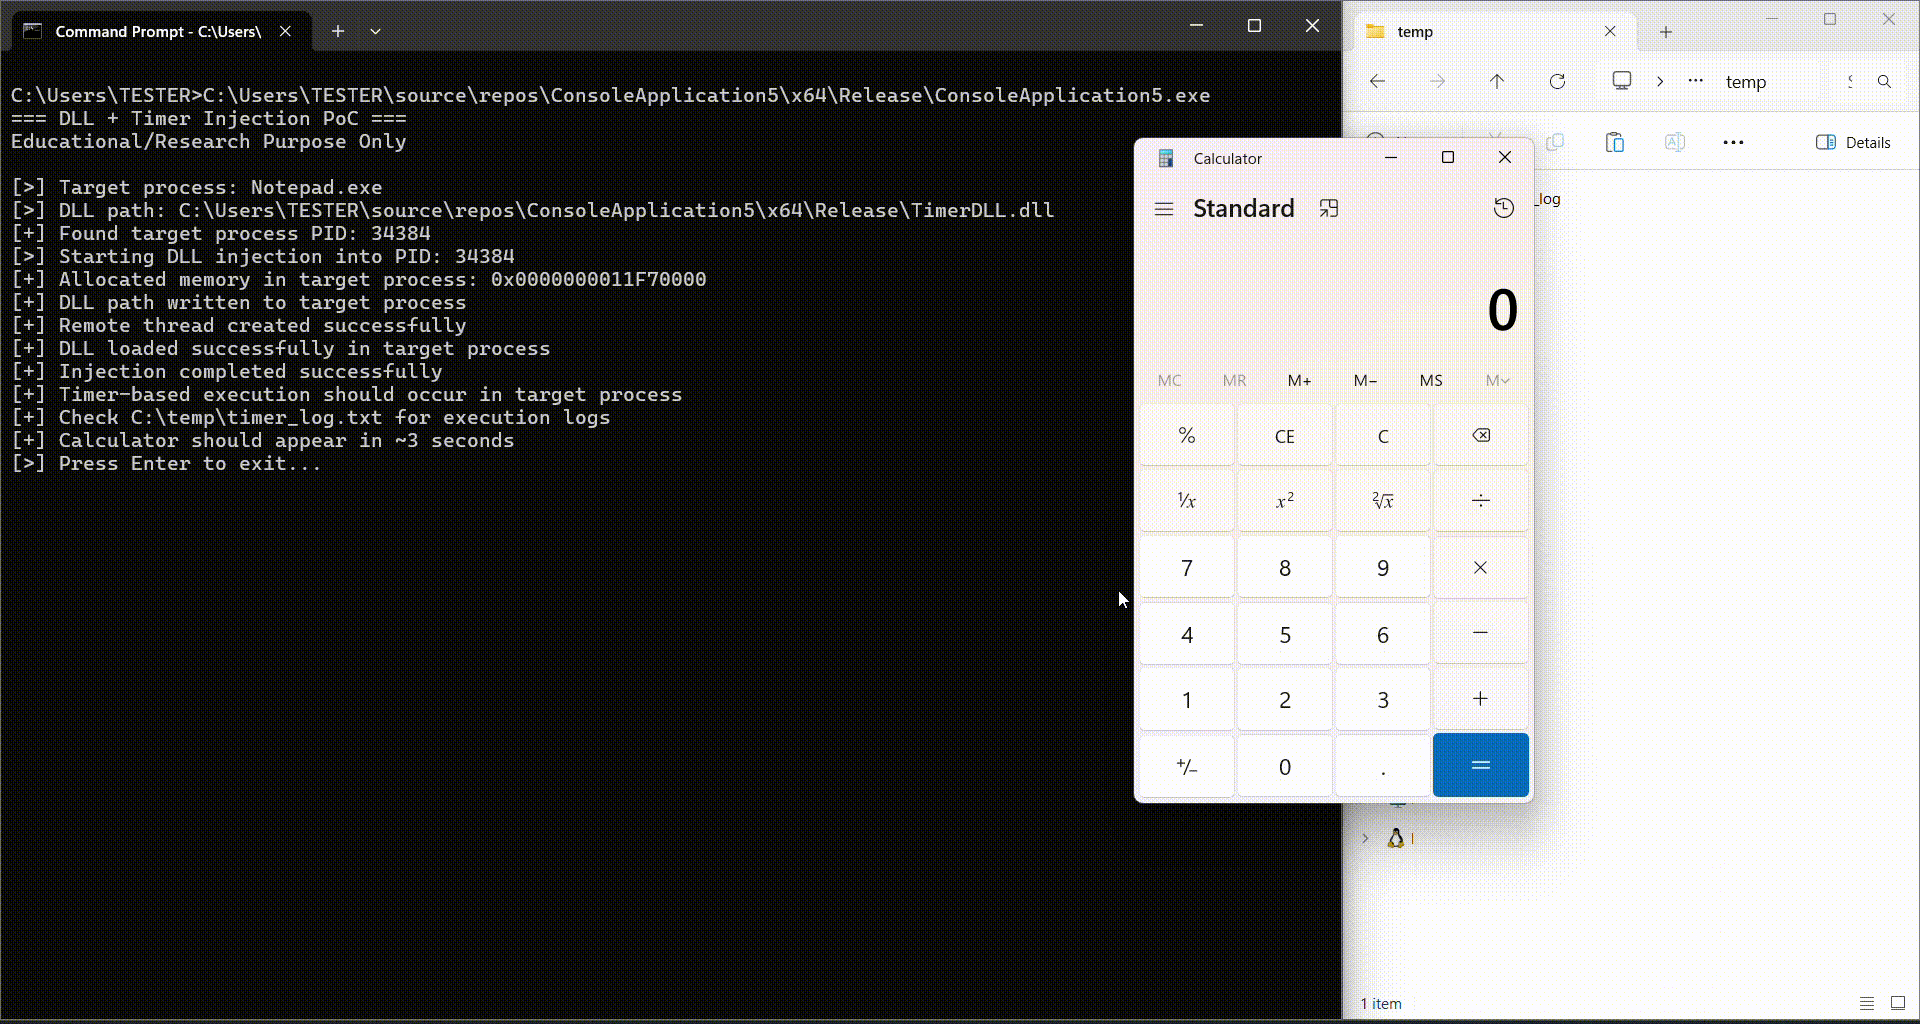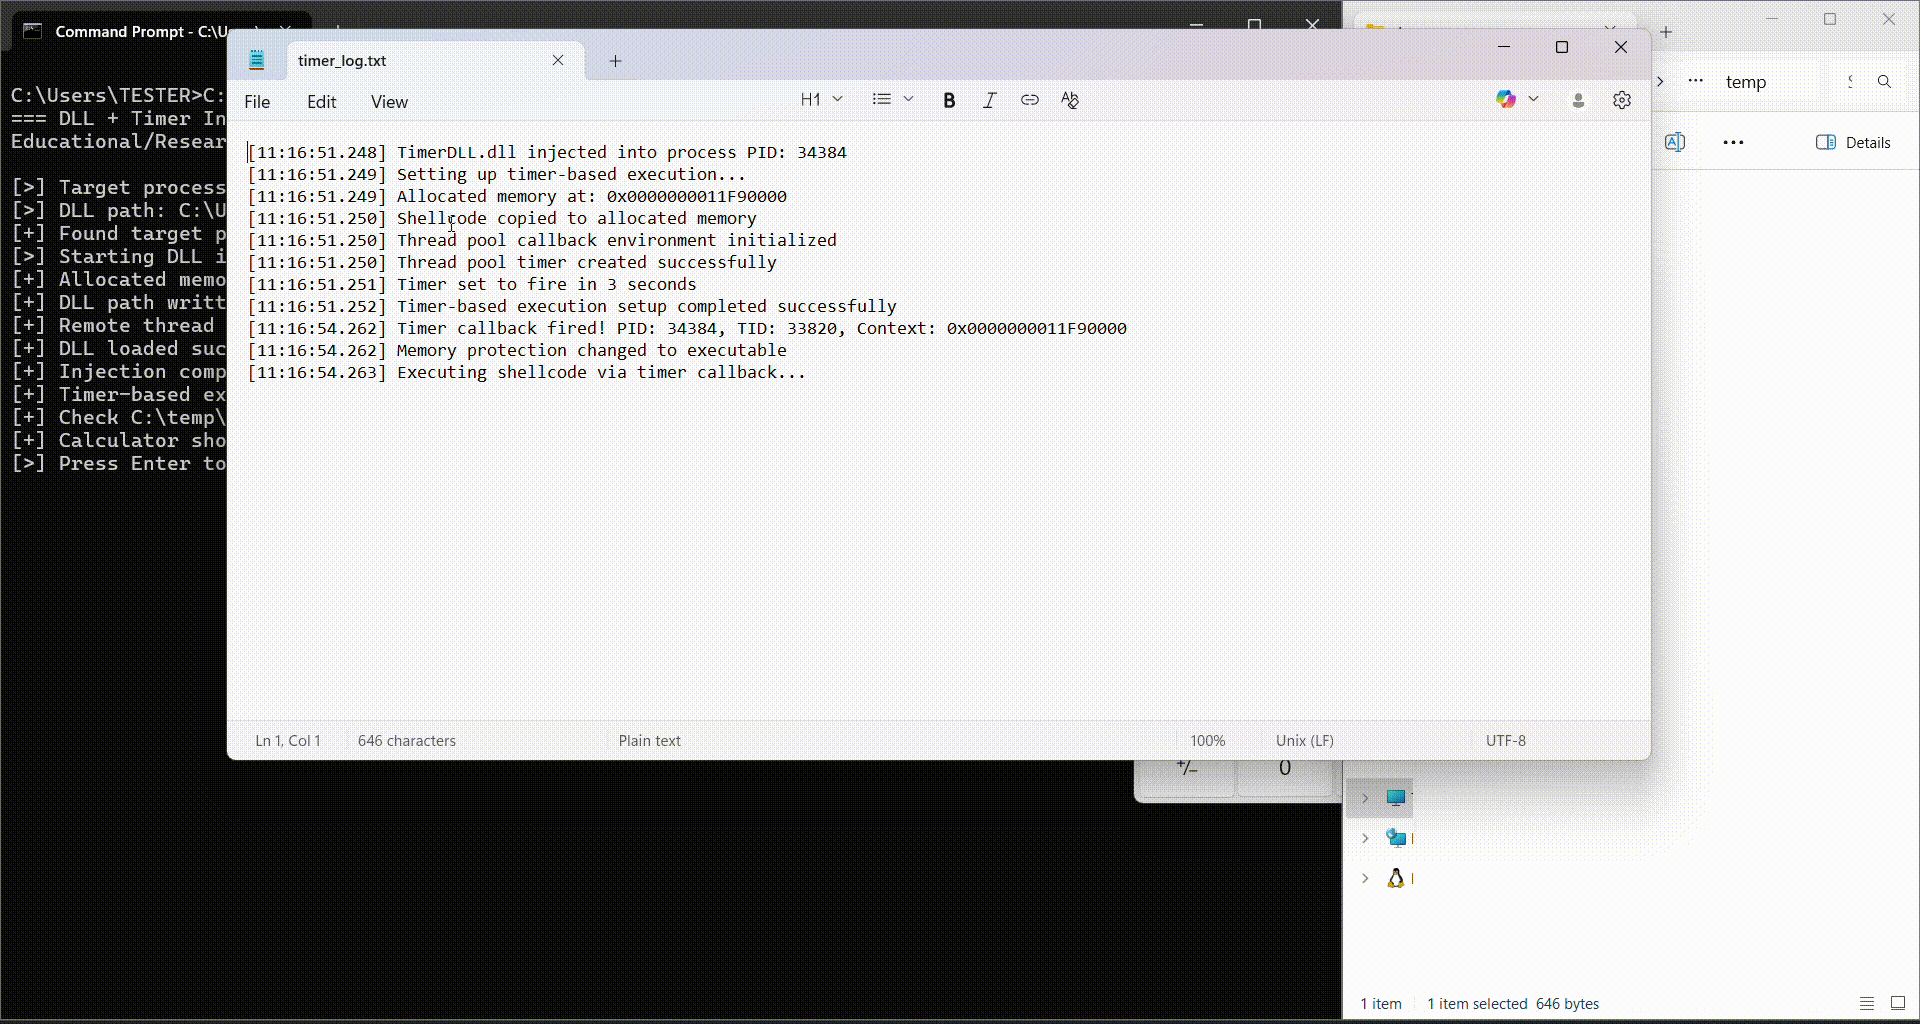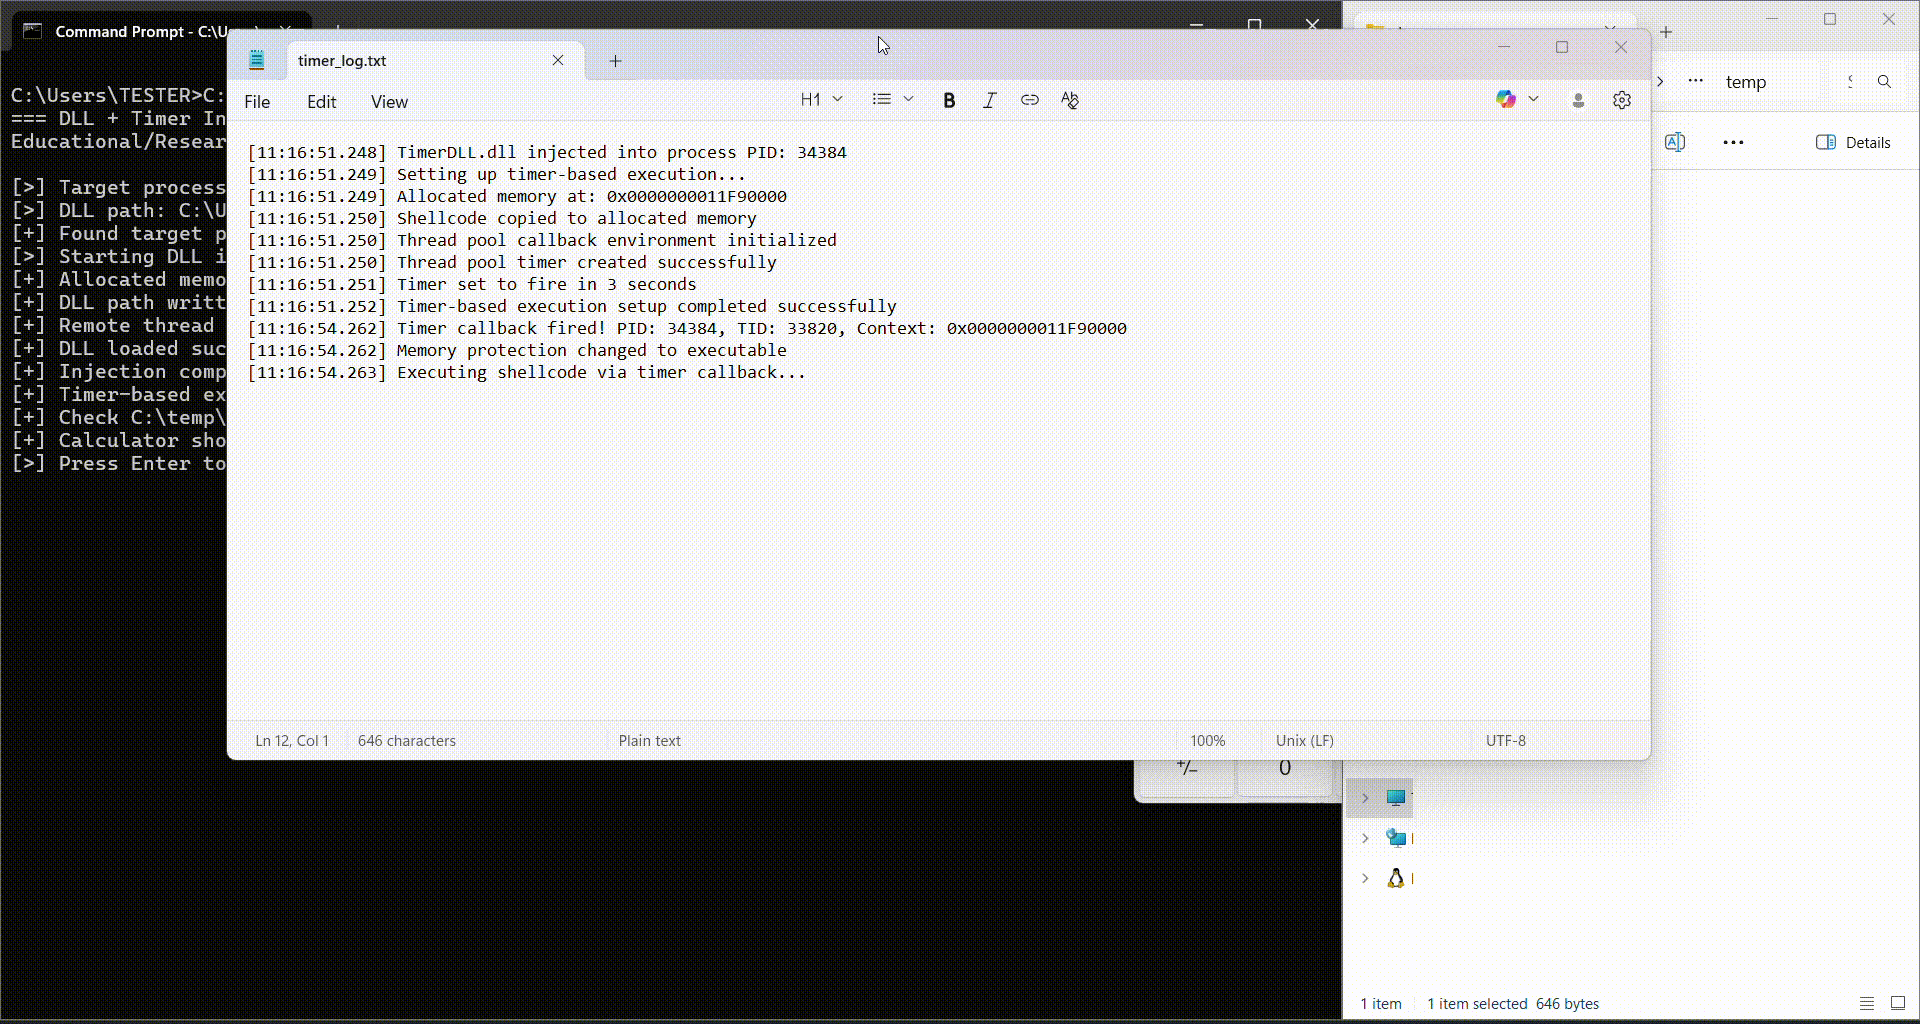 andreisss/remote-dll-injection-with-timer-based-shellcode-execution
Remote DLL Injection with Timer-based Shellcode Execution
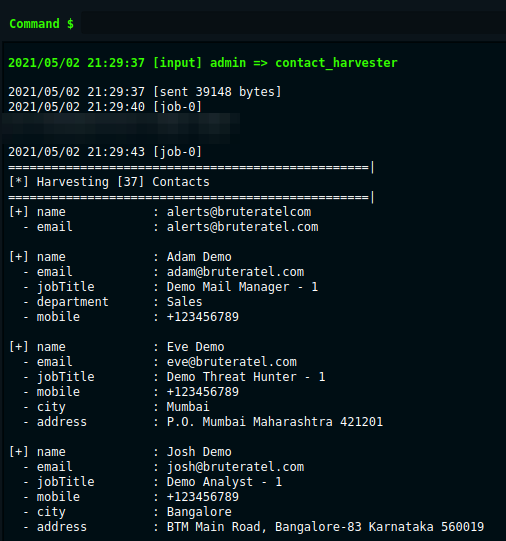 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 brmkit/toastnotify-bof
abusing windows toast notifications for fun and user manipulation
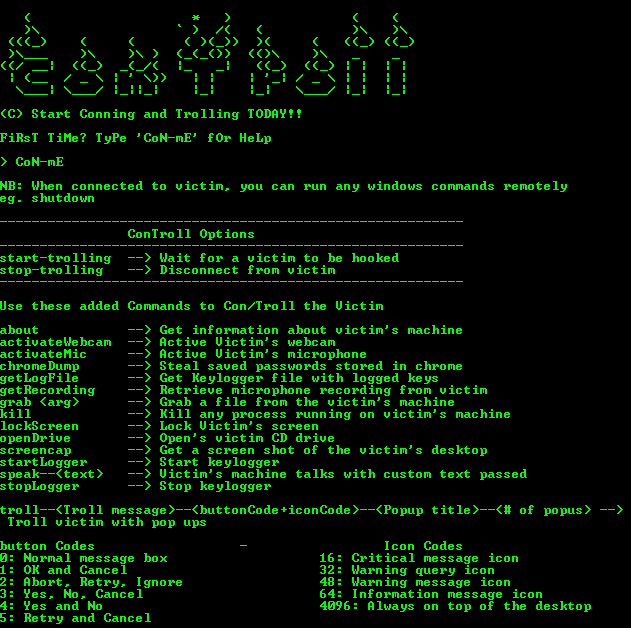 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
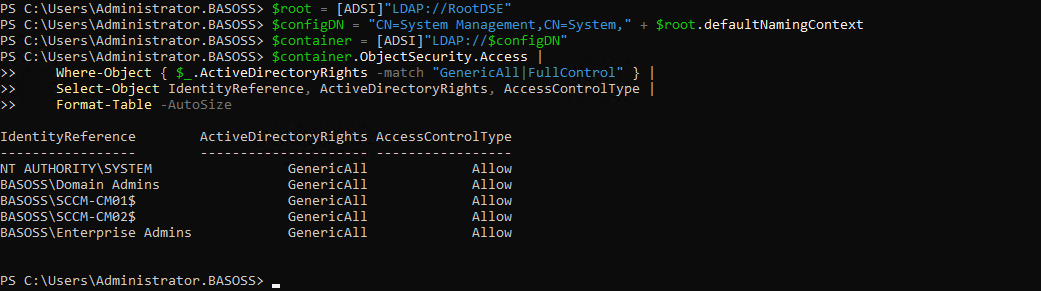 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 jvbotelho/skewrun
Active Directory time discovery protocols for red teams. Stealthy extraction via Kerberos, SMB, NTLM, and CLDAP.
 jsecu/bof-pack-1
A care package of useful bofs for red team engagments
 satchfunky/cve-2026-41096-poc
windows api bug
 preludeorg/cua-kit
Tools for attacking Computer Use Agents