
CVE-2026-38526
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
ctfexploitationpayload-development+5
1
mrdark-ops/cve-2026-38526Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
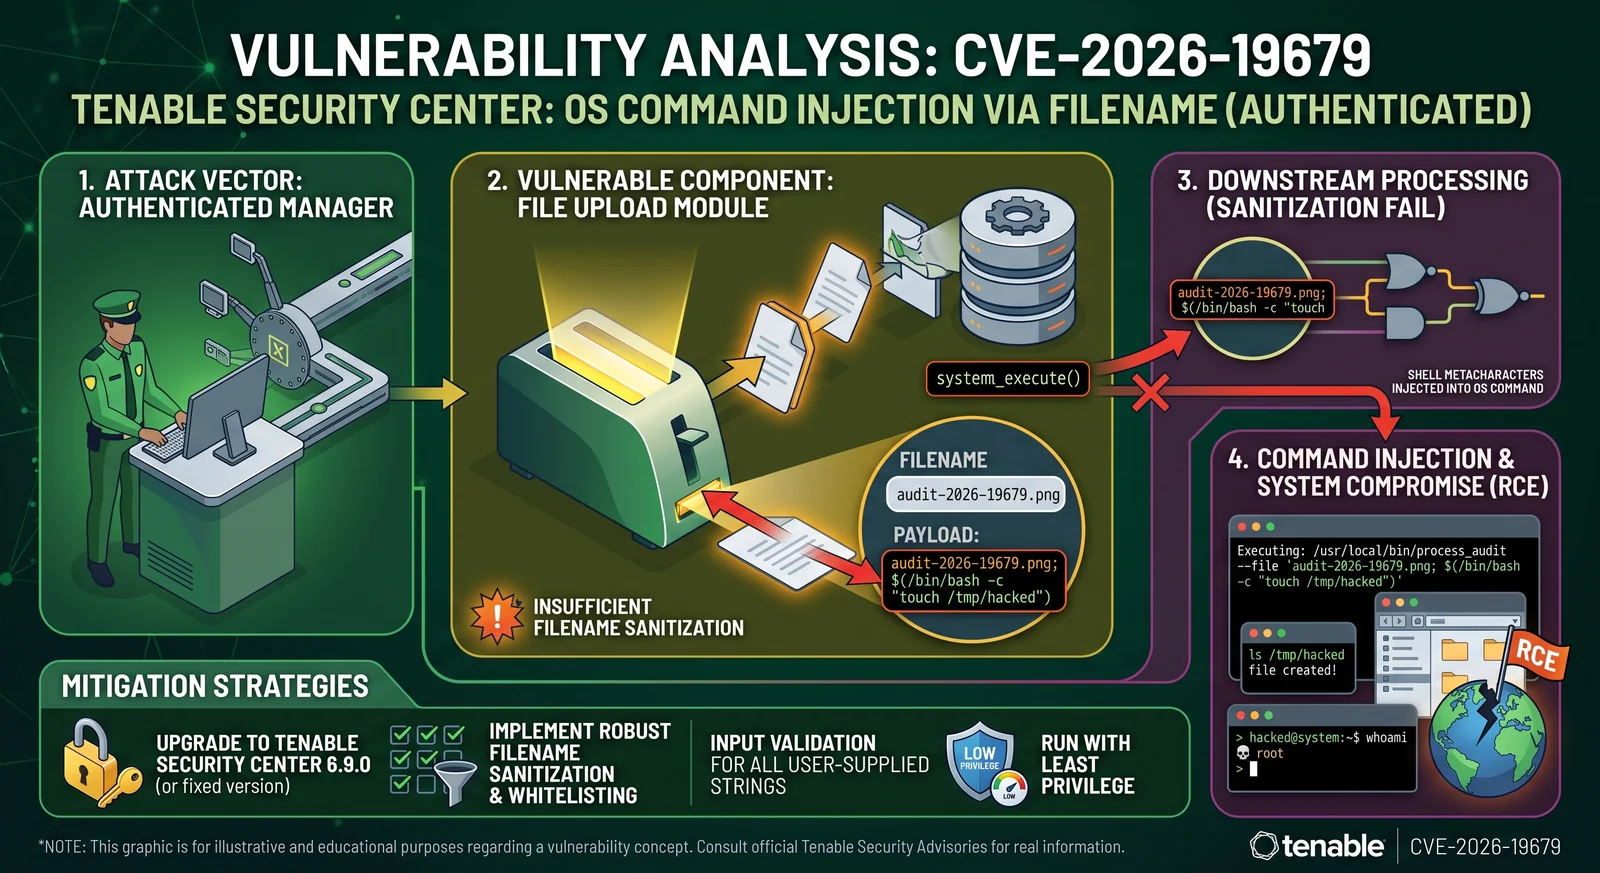 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
 ayiezola/cve-2026-48908
Unauthenticated RCE PoC for CVE-2026-48908 SP Page Builder (Joomla) arbitrary file upload and remote code execution exploit with mass scaning…
 mbanyamer/cve-2026-27574-oneuptime-rce
Proof-of-concept exploit for CVE-2026-27574, a critical code injection in OneUptime enabling remote code execution and environment variable leakage.
 shreyas-malhotra/cve-2025-27410
Updated PoC for CVE-2025-27410, since the one publicly available in the security advisory is prone to failing.
 secforce/wptimecapsulepoc
An authentication bypass was recently discovered (https://www.webarxsecurity.com/vulnerability-infinitewp-client-wp-time-capsule/) on WP Time Capsule…