
CVE-2026-90847
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
shlln/cve-2026-90847Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
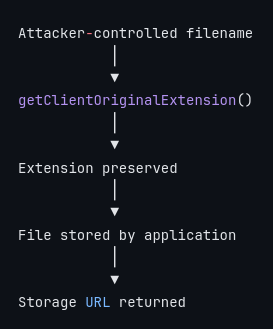 ish3ng0m4/cve-2026-38526-krayincrm
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
 d1n3sh-0x3/cve-2026-92247
Python PoC for CVE-2026-92247, an authenticated RCE in SynaptikCMS file manager via PHP upload and rename validation bypass.
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 chiefyoru/exploit-cve-2026-18351
Drag and Drop File Upload for Elementor Forms - Unauthenticated Arbitrary File Upload to RCE.🔥
 4minx/cve-2026-32475
Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 boreas37/cve-2026-32475-poc
PoC for CVE-2026-32475: Elementor Pro <=4.2.1 unauthenticated file upload to RCE. Stdlib-only Python.
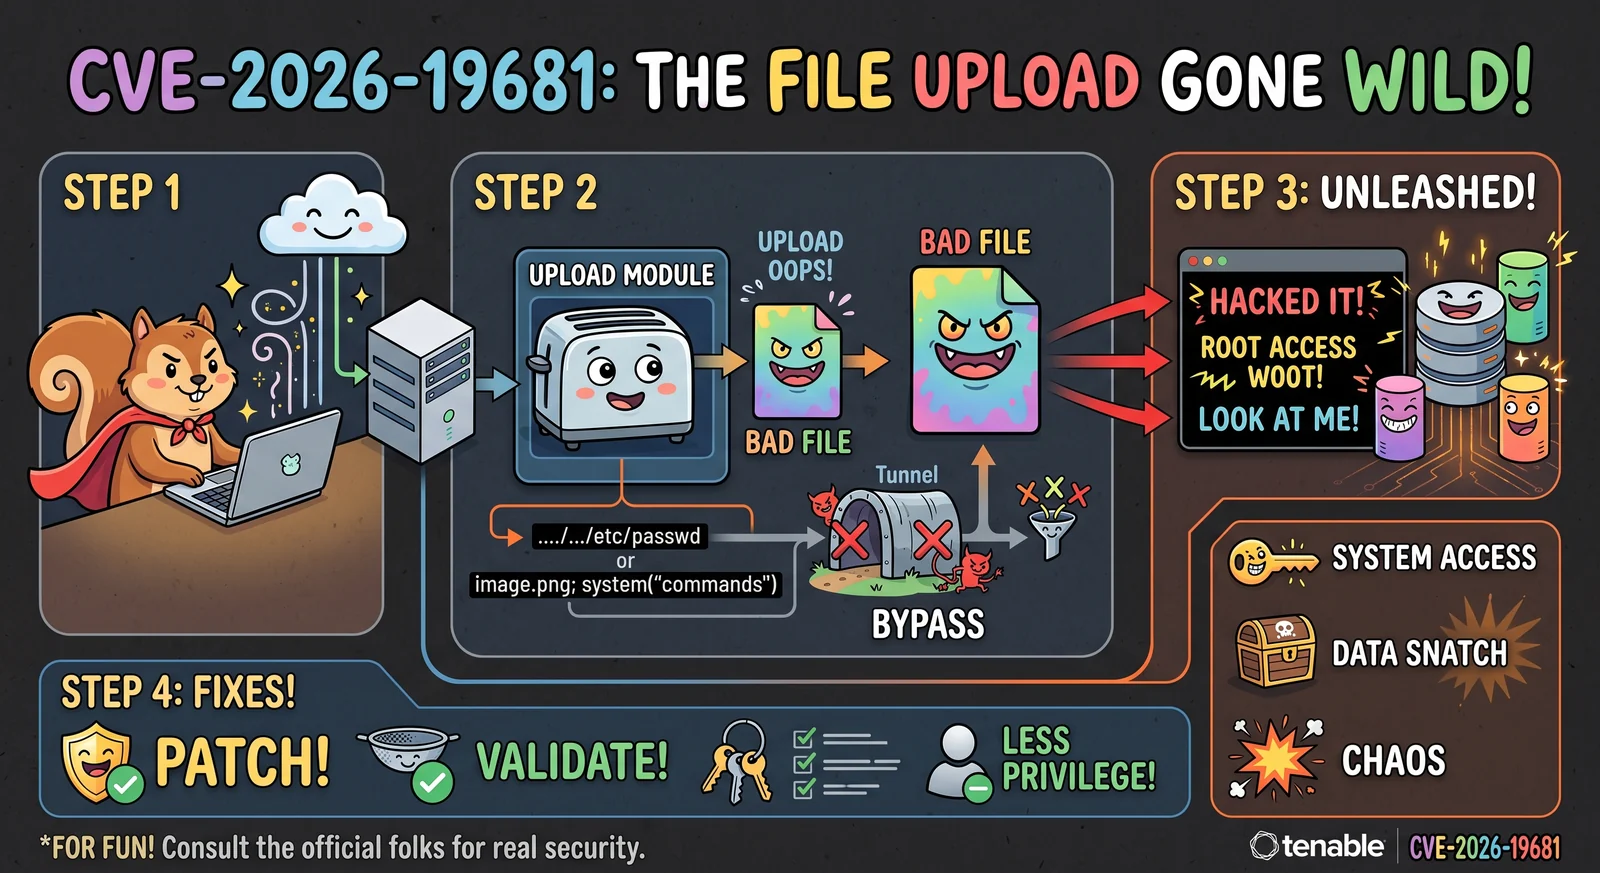 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
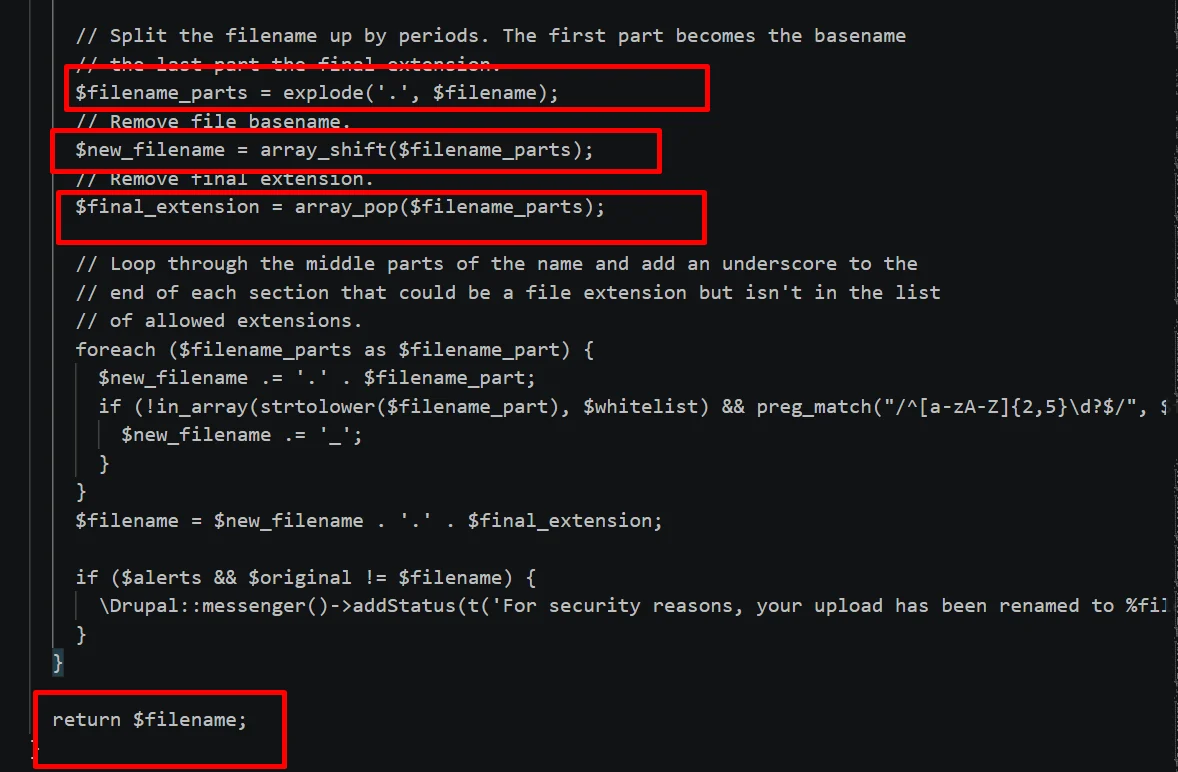 dungsocool/cve-2020-13671-old
CVE-2020-13671 - Drupal RCE via File Upload Vulnerability Analysis and PoC
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
 mohammad-008/rsfiles-cve-2026-57827
Unauthenticated File Upload → RCE PoC for CVE-2026-57827 (RSFiles! Joomla < 1.17.12). Authorized security research use only.
 minhhk68/cve-2026-13158
Proof-of-concept exploit and technical advisory for an Admin+ arbitrary file upload to remote code execution vulnerability in Everest Toolkit…
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12