
cve-2026-41940-PoC
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
authenticationcommand-and-controlexploitation+7
189
yasouxken/cve-2026-41940-pocPython PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 hypnguyen1209/cve-2026-63520
Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 hunt-benito/siyuan-mcp-admin-takeover-cve-2026-66012-missing-authorization
Unauthenticated administrator takeover exploit for CVE-2026-66012 using MCP missing authorization to exfiltrate credentials and achieve remote code…
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
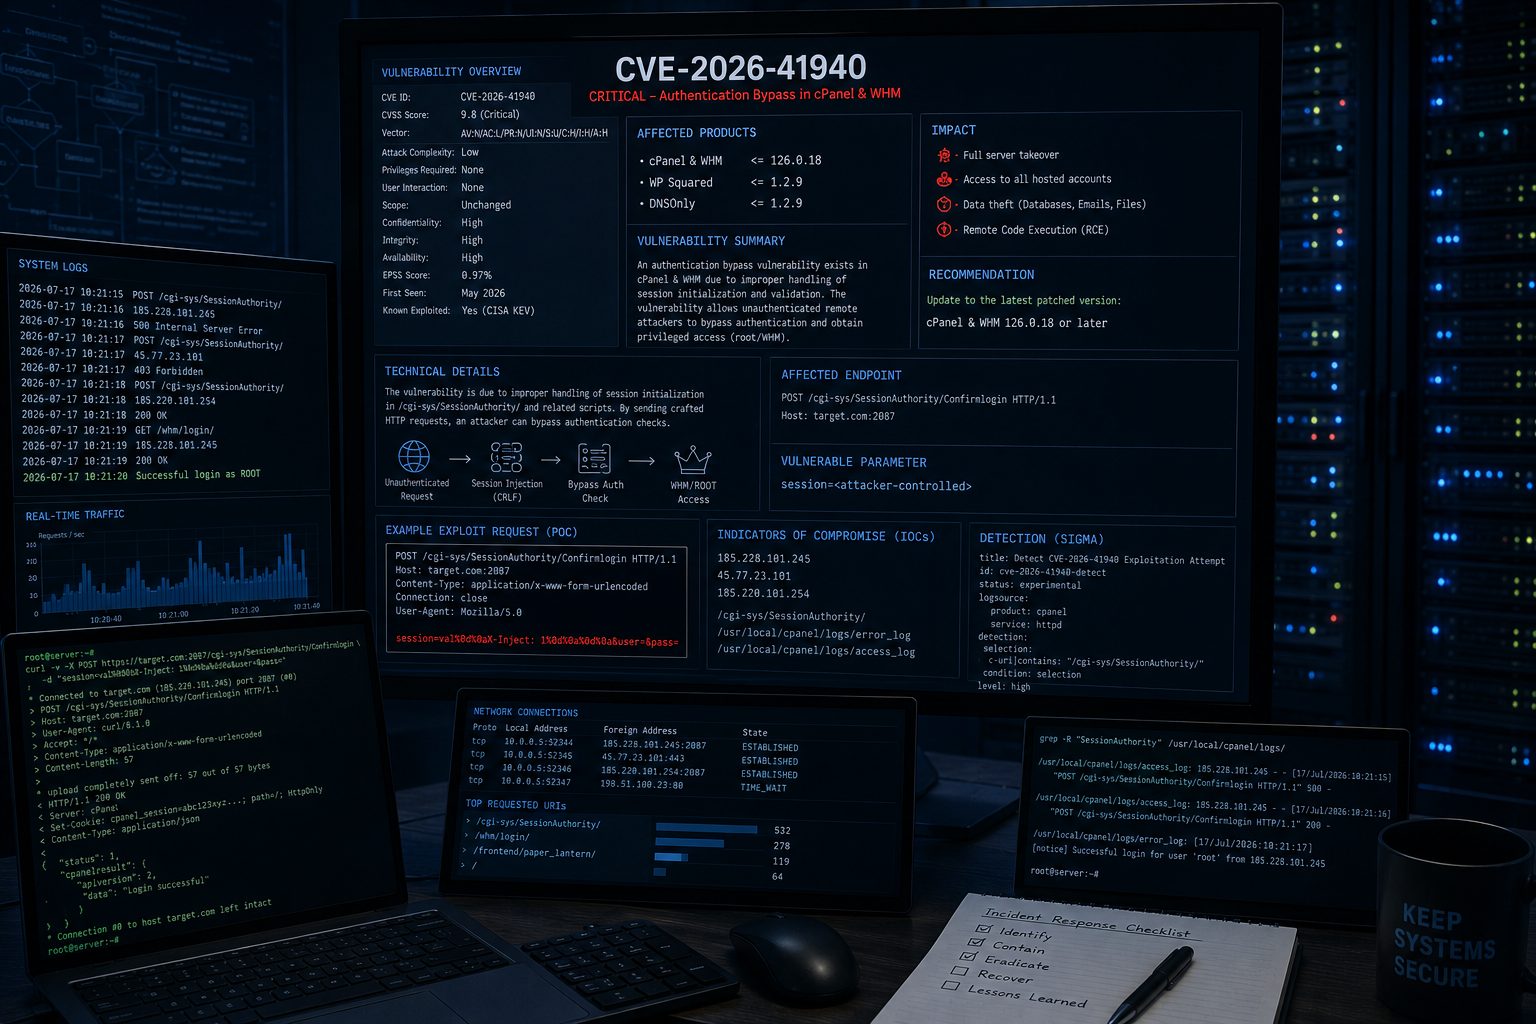 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 lutfifakee-project/cve-2026-41940
cPanel/WHM CVE-2026-41940 - Mass Scanner & Exploiter
 gentilkiwi/mimikatz
A little tool to play with Windows security
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 imjdl/cve-2026-31816-rshell
Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 iveresk/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager. Injects SSH keys via…
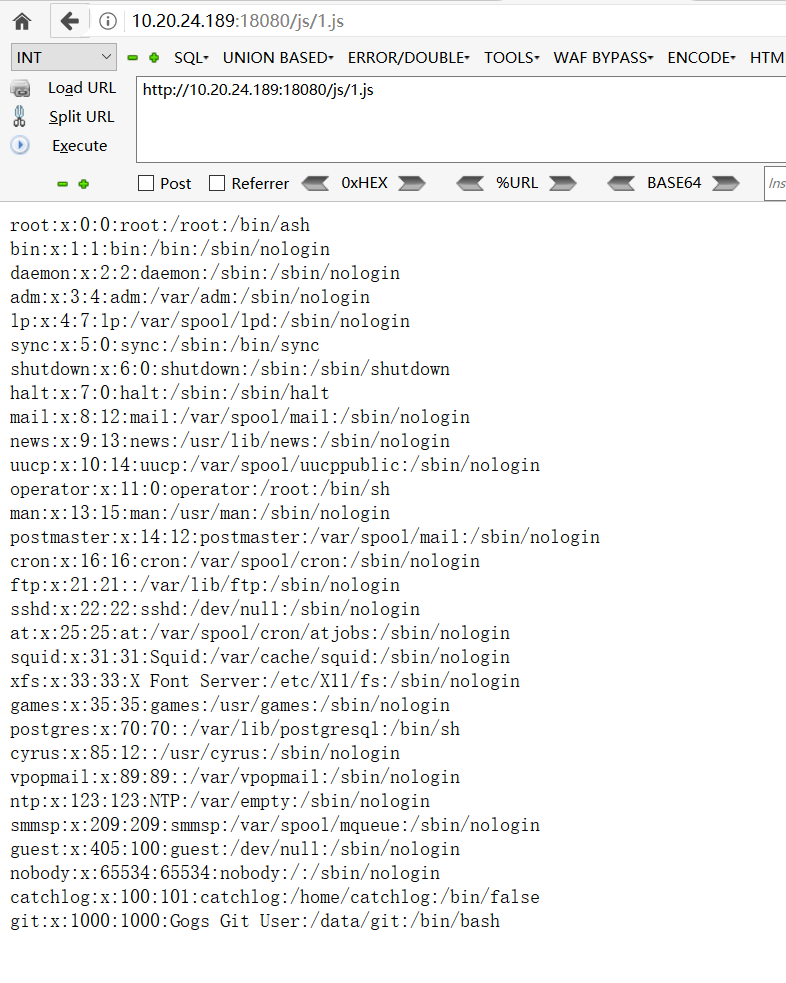 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.